miniDumpReader
 gmh5225/minidumpreader
Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
binary-analysisdigital-forensicsforensics+3
gmh5225/minidumpreaderParses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
 withsecurelabs/memory-carving-scripts
Scripts for extracting useful information from infected memory dumps
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
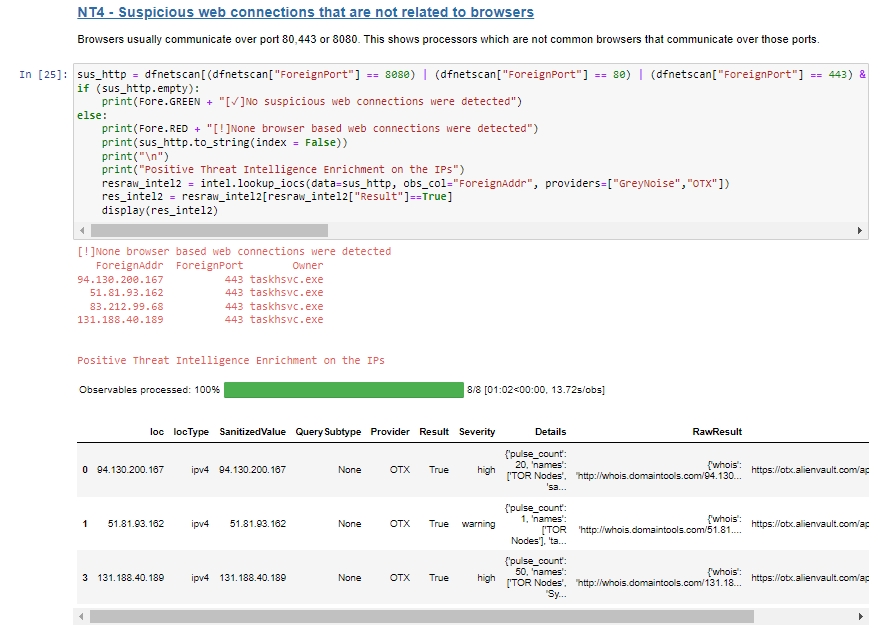 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
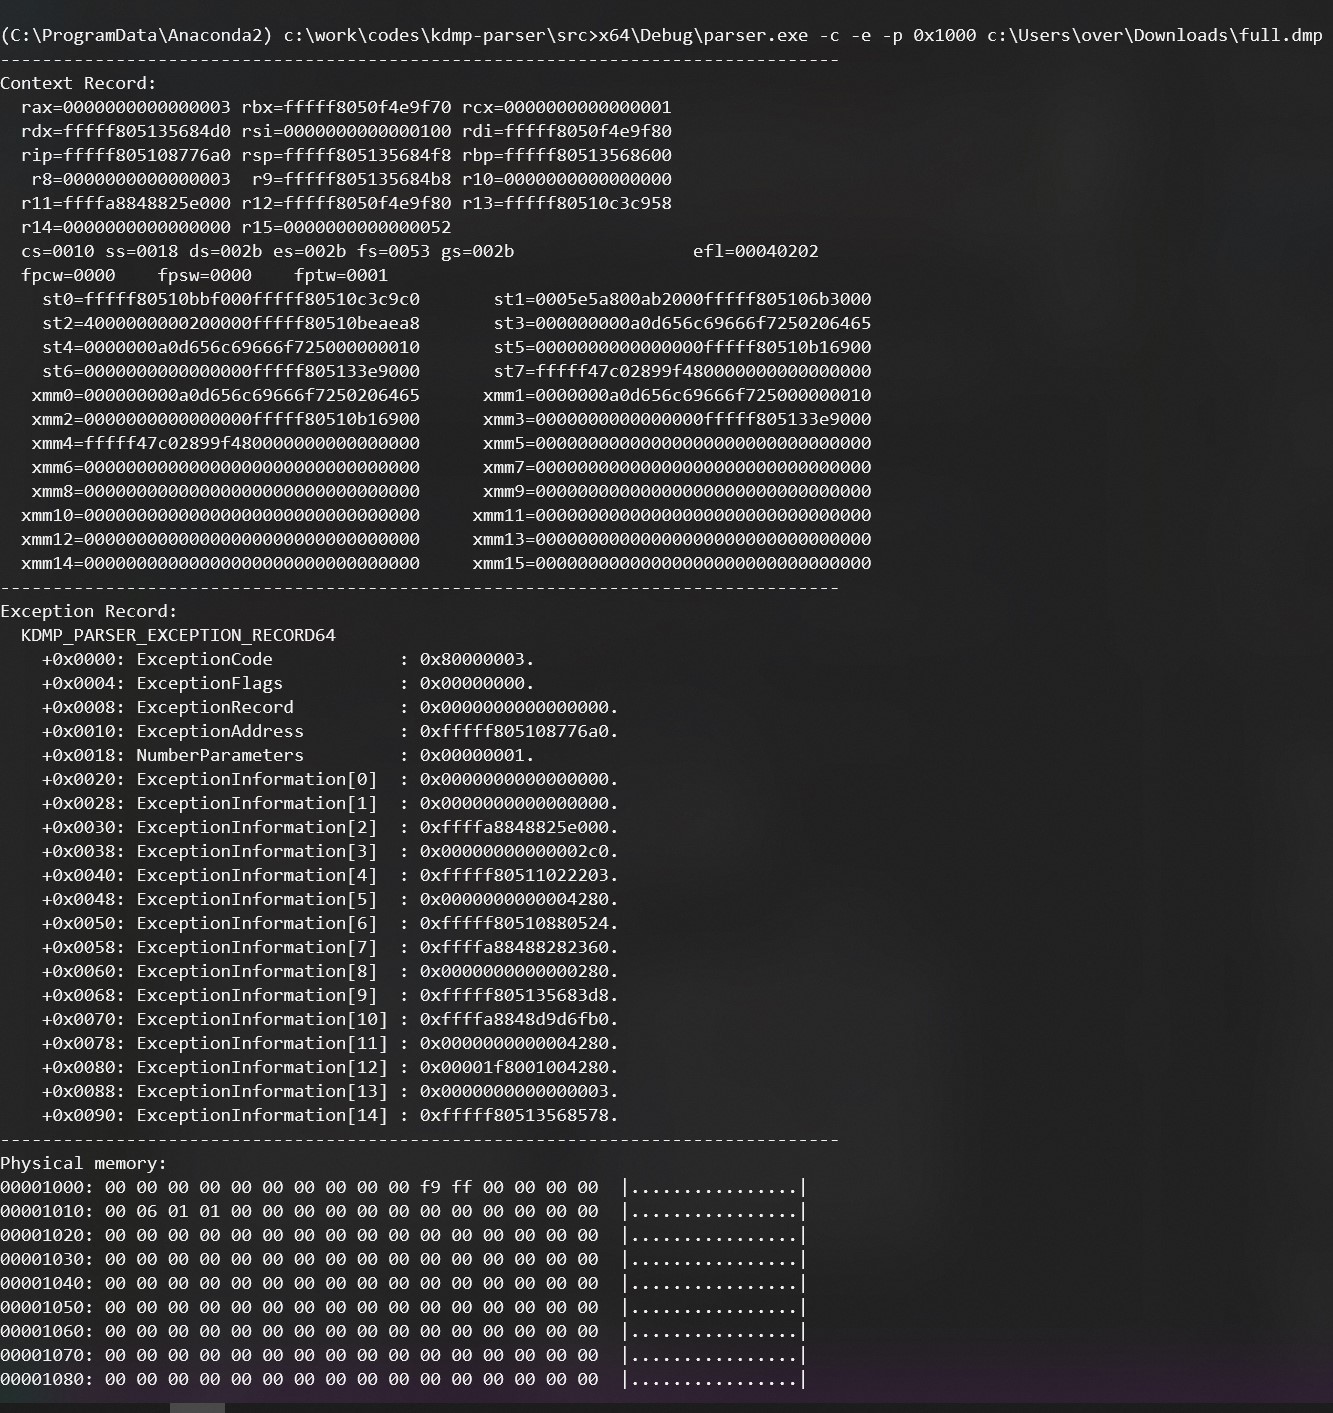 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
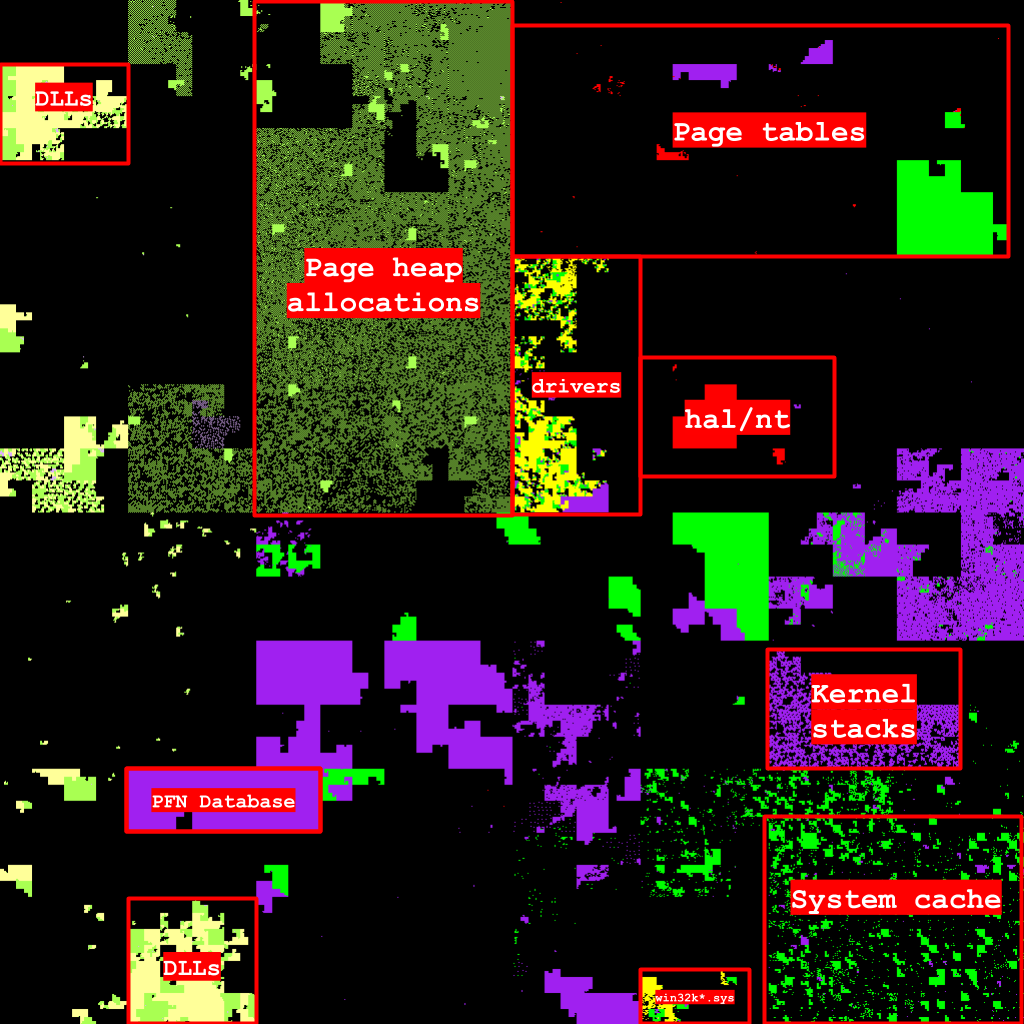 0vercl0k/clairvoyance
Visualize the virtual address space of a Windows process on a Hilbert curve.