
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
XenoboxX preview

XenoboxX

GitHubcecio/xenoboxx

Hardware Sandbox Toolkit

dynamic-analysis-sandboxingforensicshardware-security+4
62 years ago
ShellGhost preview

ShellGhost

GitHublem0nsec/shellghost

A memory-based evasion technique which makes shellcode invisible from process start to end.
binary-analysisencryption-decryption-toolsexploitation+4
1.2k2 years ago
CVE-2021-45067 preview

CVE-2021-45067

GitHubhacksysteam/cve-2021-45067

Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
binary-exploitationdata-exfiltrationexploitation+3
233 years ago
ReflectiveDLLInjection preview

ReflectiveDLLInjection

GitHubstephenfewer/reflectivedllinjection

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…

exploitationmemory-forensicspayload-development+2
3.4k4 years ago
dnSpy preview

dnSpy

GitHubdnspyex/dnspy

Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.2k1 month ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
digital-forensicsdisk-forensicsforensics+3
5165 years ago
pypykatz preview

pypykatz

GitHubskelsec/pypykatz

Mimikatz implementation in pure Python
authenticationdigital-forensicsencryption-decryption-tools+4
3.4k6 months ago
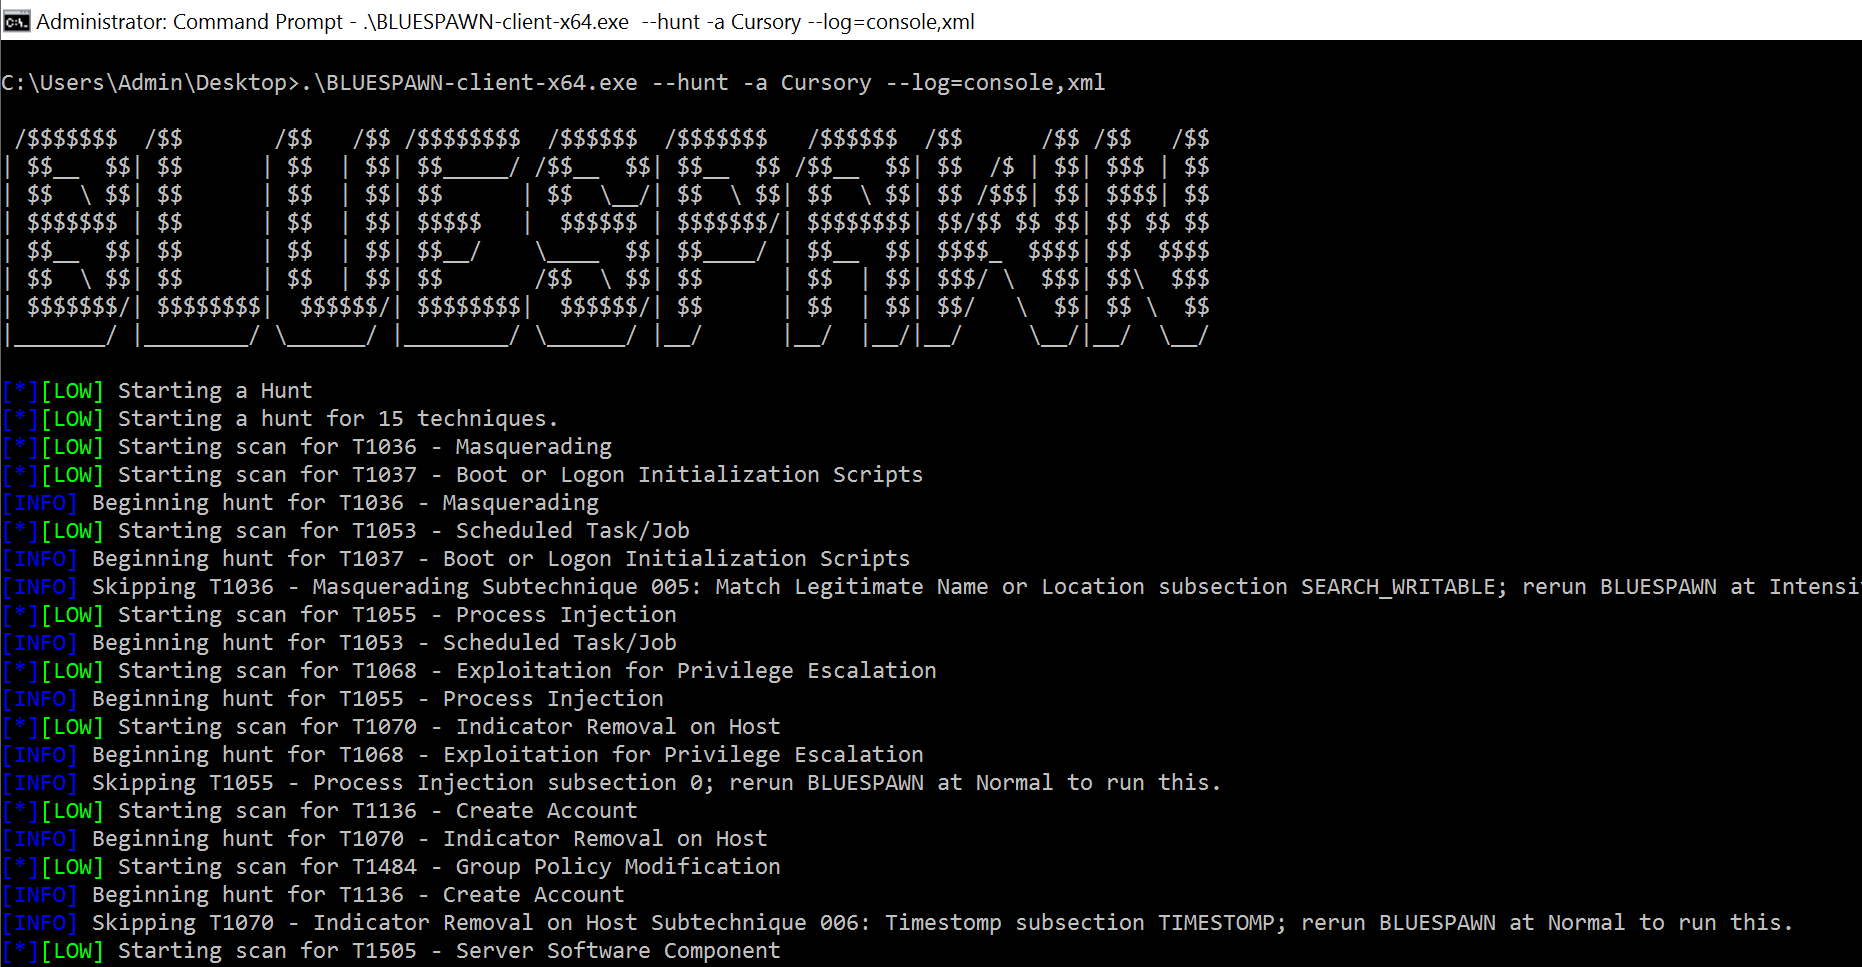
BLUESPAWN preview

BLUESPAWN

GitHubion28/bluespawn

An Active Defense and EDR software to empower Blue Teams
configuration-auditingdefensive-toolsincident-response+3
1.3k6 months ago
ATMMalScan preview

ATMMalScan

GitHubfboldewin/atmmalscan

Command-line DFIR tool for scanning Windows ATM systems to detect malware traces in process memory and disk, with automated memory dump creation for…
digital-forensicsdisk-forensicsincident-response+2
575 years ago
CVE-2025-27363 preview

CVE-2025-27363

GitHubtin-z/cve-2025-27363

Integer overflow in FreeType software, which also affects Chrome
binary-exploitationeducationexploitation+3
312 months ago
gsscred-move-uaf preview

gsscred-move-uaf

GitHubbazad/gsscred-move-uaf

CVE-2018-4343: Proof-of-concept for a use-after-free in the GSSCred daemon on macOS and iOS.
binary-exploitationexploitationios-security+2
78 years ago
java-stager preview

java-stager

GitHubcornerpirate/java-stager

A PoC Java Stager which can download, compile, and execute a Java file in memory.
command-and-controldynamic-code-analysiseducation+7
1078 years ago
NotEnough preview

NotEnough

GitHubcaoweiquan322/notenough

This tool calculates tricky canonical huffman histogram for CVE-2023-4863.
binary-exploitationexploitationfuzzing+3
252 years ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
binary-analysisdefensive-toolsforensics+3
6838 months ago
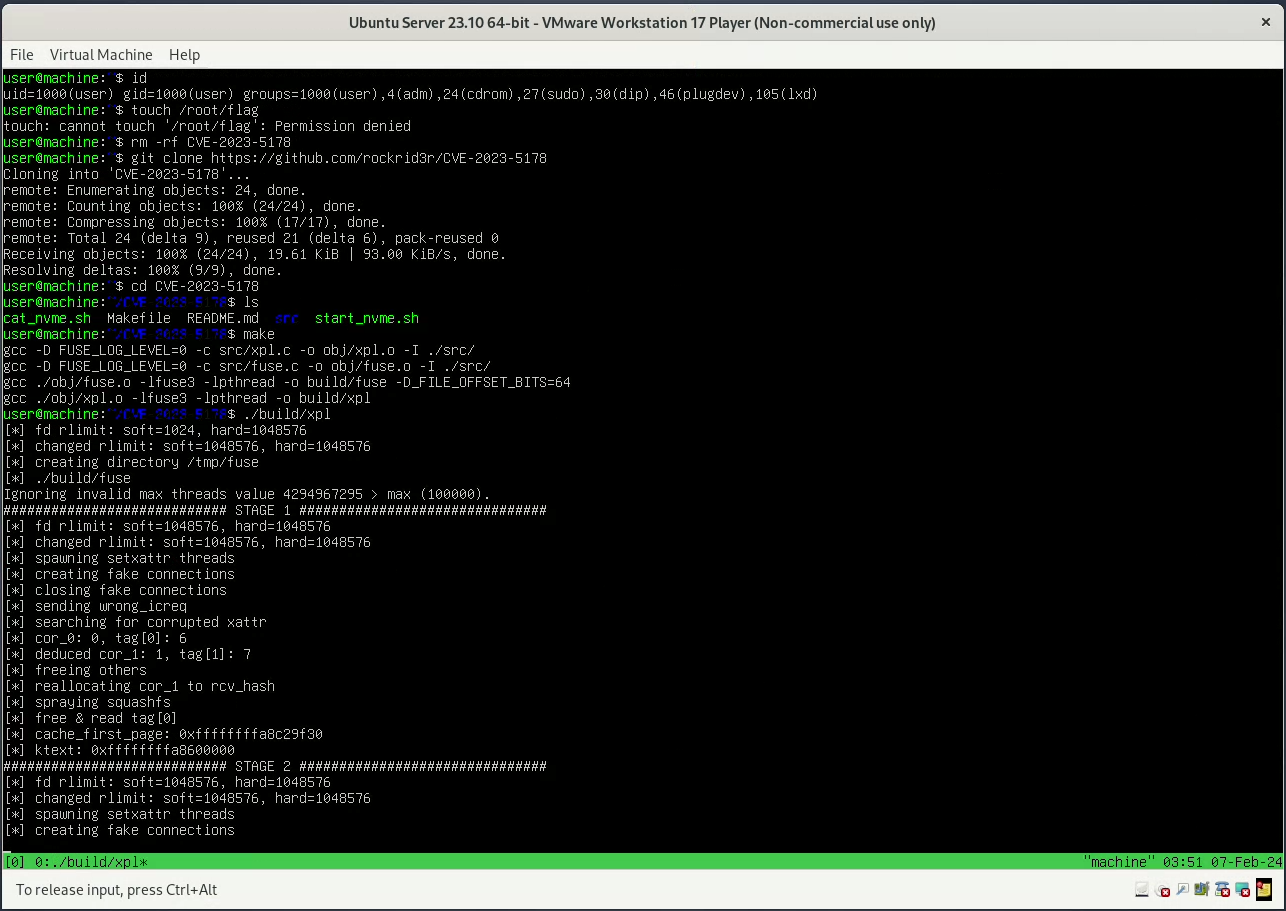
CVE-2023-5178 preview

CVE-2023-5178

GitHubrockrid3r/cve-2023-5178

Exploit for CVE-2023-5178
binary-exploitationeducationexploitation+3
72 years ago
CVE-2019-19012 preview

CVE-2019-19012

GitHubmanhndd/cve-2019-19012

Integer overflow in Oniguruma
binary-analysisexploitationfuzzing+3
46 years ago
Pixel_GPU_Exploit preview

Pixel_GPU_Exploit

GitHub0x36/pixel_gpu_exploit

Android 14 kernel exploit for Pixel7/8 Pro
android-securitybinary-exploitationeducation+4
5632 years ago
CVE-2017-8641_chakra_Js_GlobalObject preview

CVE-2017-8641_chakra_Js_GlobalObject

GitHubhomjxi0e/cve-2017-8641_chakra_js_globalobject

There is a classic heap overflow when eval a string which large enough in Chakra! This issue can be reproduced steadly in uptodate Edge in Win10 WIP.…

binary-exploitationexploitationmemory-forensics+3
19 years ago
Previous12Next