

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.1k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
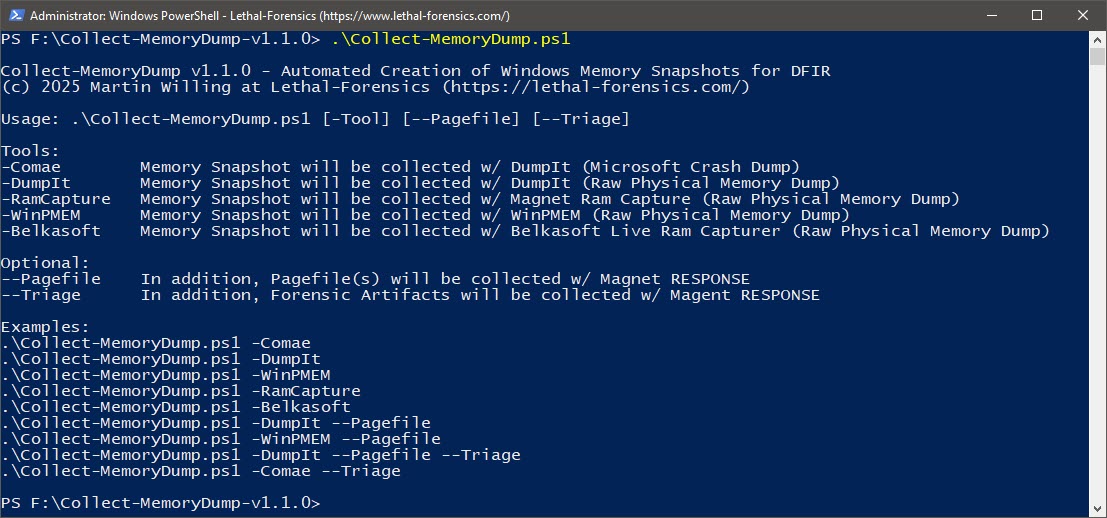 lethal-forensics/collect-memorydump
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…
 lsinus/cachemeifyoucan
SLUBStick exploitation of CVE-2022-2588. Converting a DF into a cross-cache arbitrary memory R/W primitive through PTE manipulation.