Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC

SALT - SLUB ALlocator Tracer for the Linux kernel

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.


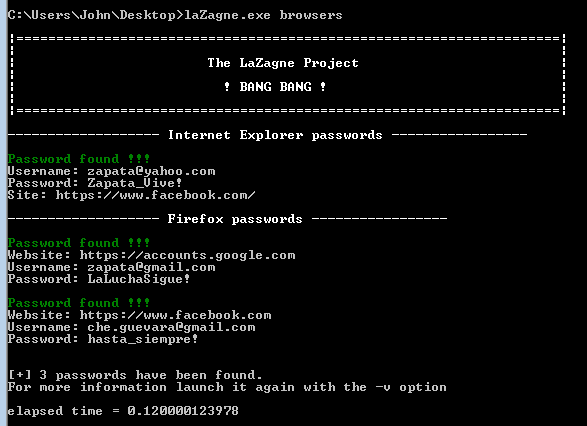
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

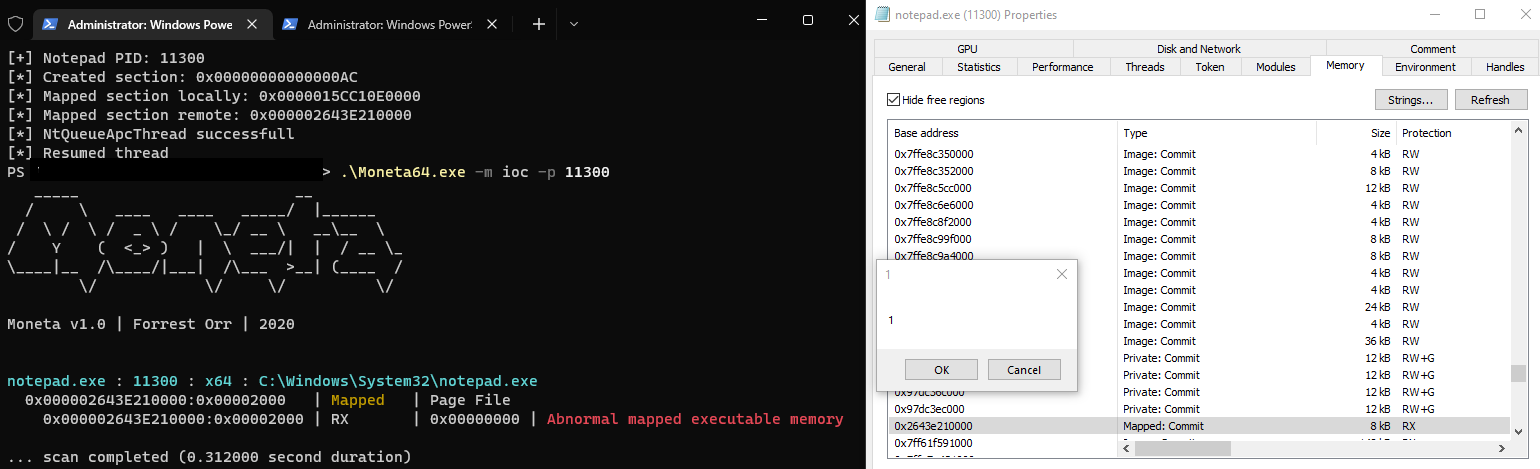
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

All reasonably stable tools

Windows memory hacking library

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.

Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…