

DeepSleep
 theflink/deepsleep
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
exploitationmemory-forensicspayload-development+1
3744 years ago
theflink/deepsleepA variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC

 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
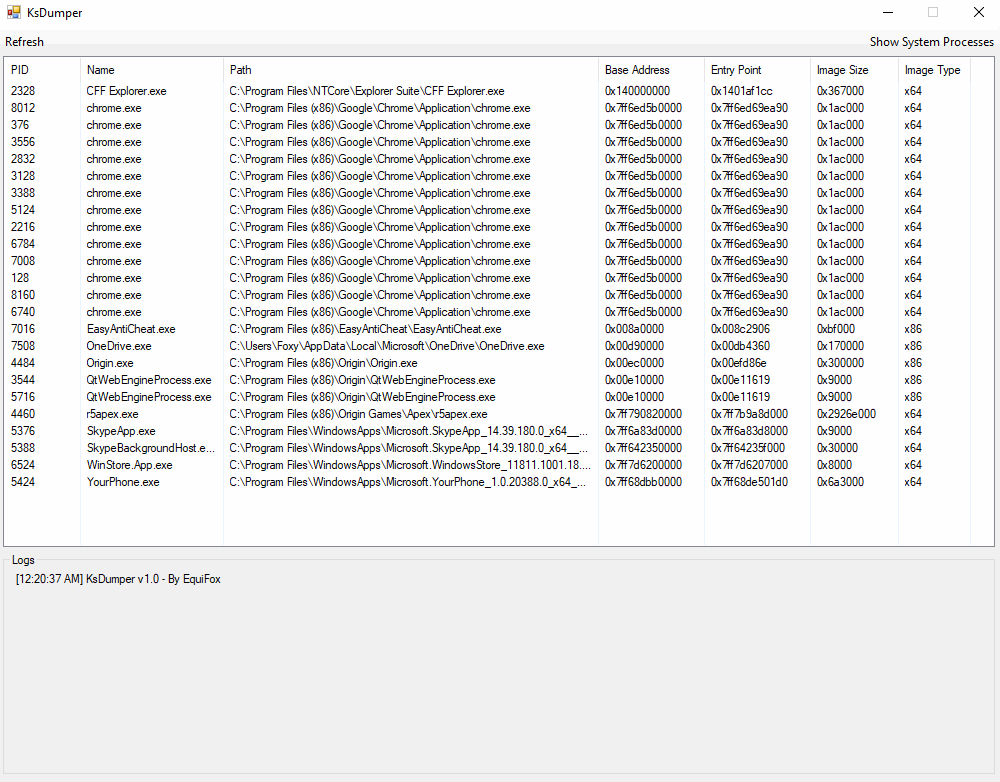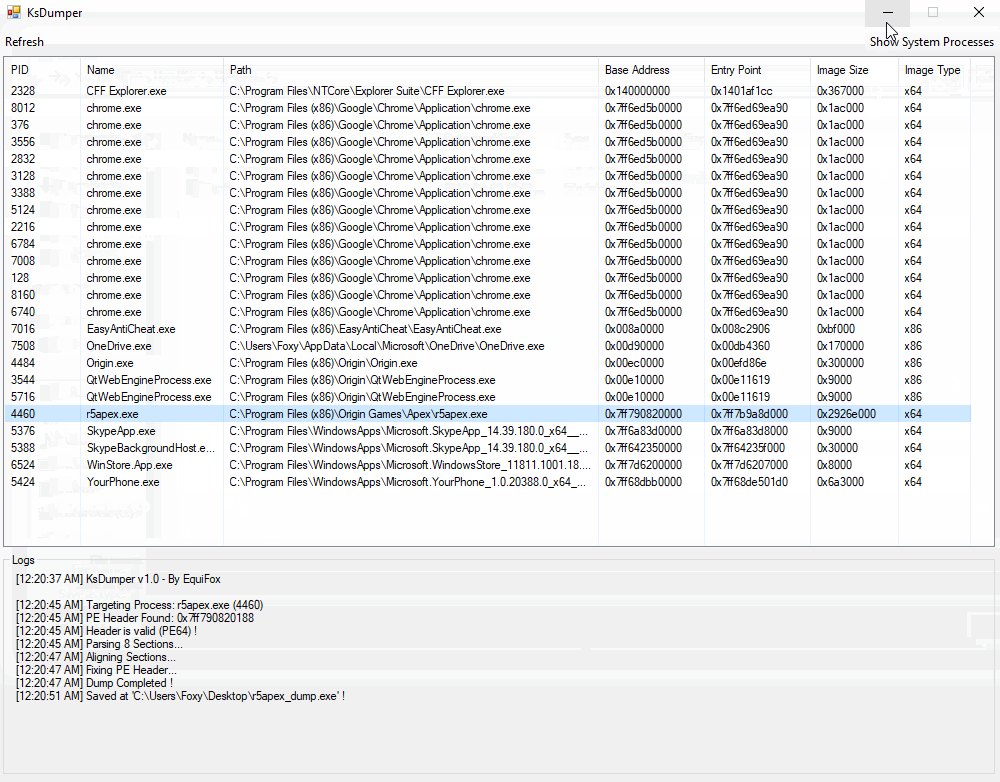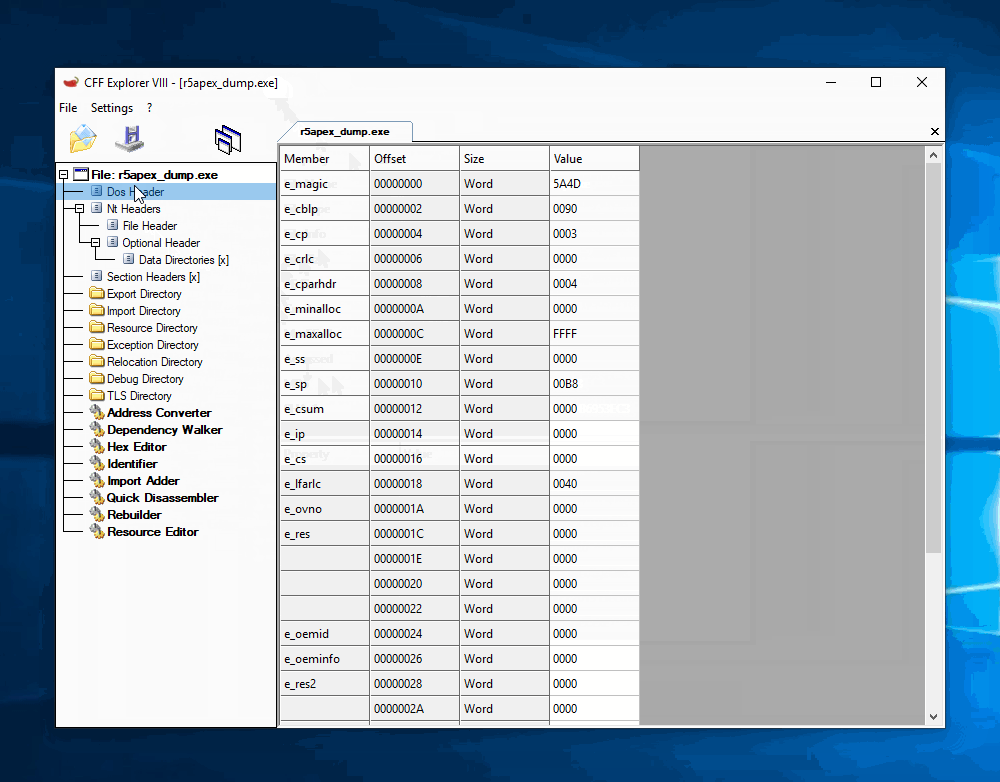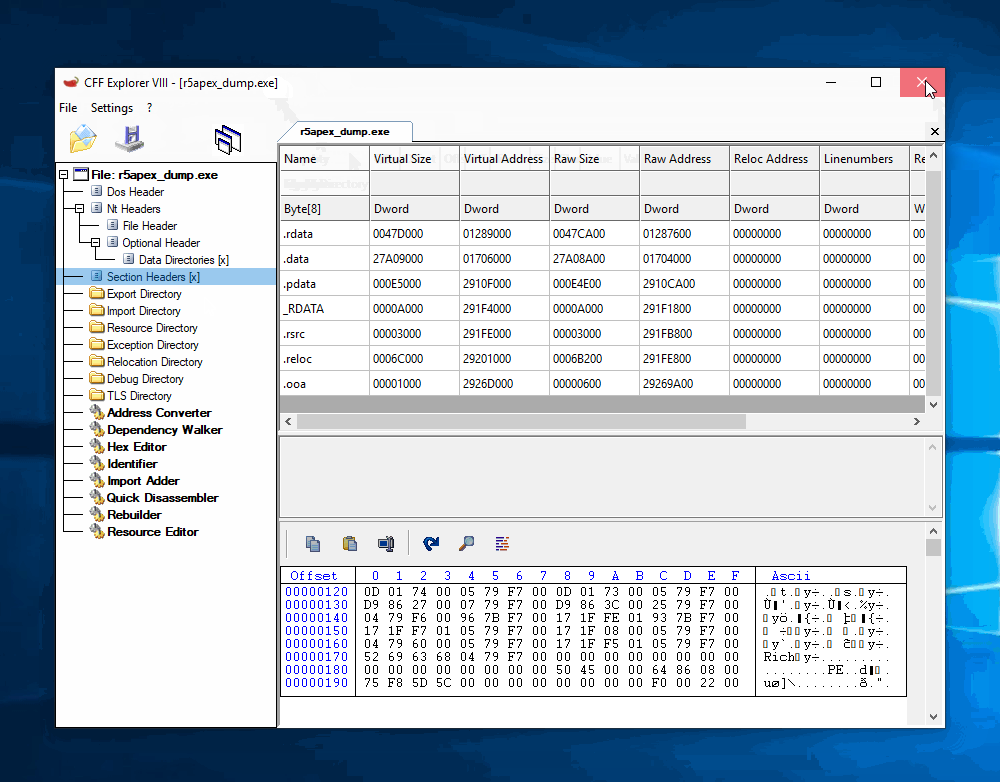 equifox/ksdumper
Dumping processes using the power of kernel space !
 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 0linear/cve-2026-62958
Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 amperclock/cve-2023-32784-kdbxpassdmp
Retrieves the master password from Keepass memory dump, using a hint of bruteforce.
 ricardojoserf/trickdump
Dump lsass using only NTAPI functions creating 3 JSON and 1 ZIP file... and generate the MiniDump file later!
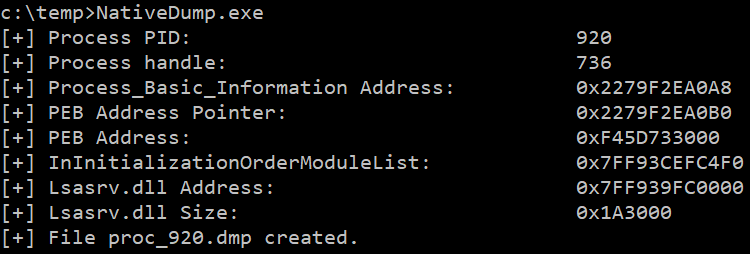 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 samueltulach/nullmap
Using CVE-2023-21768 to manual map kernel mode driver
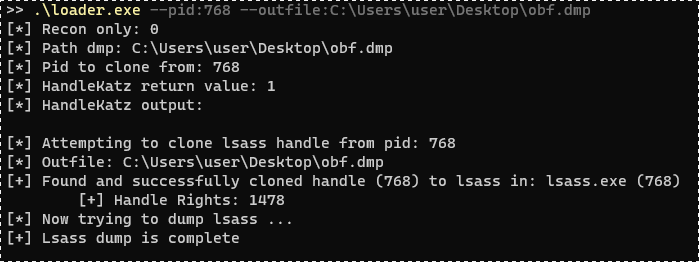 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…