
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
97 results
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
16.0k11h 2m ago
salt preview

salt

GitHubpaolomonti42/salt

SALT - SLUB ALlocator Tracer for the Linux kernel

binary-analysisdebuggerseducation+2
1578 years ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.2k1 day ago
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs

digital-forensicsforensicsioc-management+3
8492 years ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k7 days ago
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

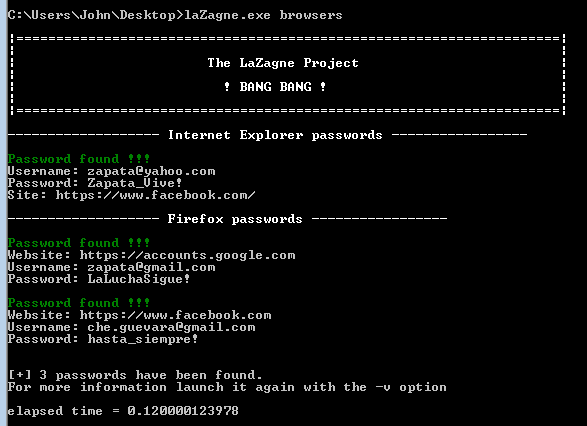
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
encryption-decryption-toolsforensicshash-analysis+8
11.0k0 years ago
AllTools preview

AllTools

GitHubzodiacon/alltools

All reasonably stable tools
binary-analysisdebuggersgeneral-purpose-utilities+1
1.4k3 months ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k3 months ago
LEAF preview

LEAF

GitHubalex-cart/leaf

Linux Evidence Acquisition Framework

digital-forensicsdisk-forensicsforensics+5
1211 year ago
WinPmem preview

WinPmem

GitHubvelocidex/winpmem

The multi-platform memory acquisition tool.
digital-forensicsforensicsincident-response+1
1.0k11 months ago
CVE-2025-5777 preview

CVE-2025-5777

GitHubbughuntar/cve-2025-5777

CVE-2025-5777 Citrix NetScaler Memory Leak Exploit (CitrixBleed 2)
exploitationinformation-gatheringmemory-forensics+3
301 year ago
ShellGhost preview

ShellGhost

GitHublem0nsec/shellghost

A memory-based evasion technique which makes shellcode invisible from process start to end.
binary-analysisencryption-decryption-toolsexploitation+4
1.2k2 years ago
bulk_extractor preview

bulk_extractor

GitHubsimsong/bulk_extractor

This is the development tree. Production downloads are at:
data-recoverydigital-forensicsdisk-forensics+9
1.4k15 days ago
XBadManners preview

XBadManners

GitHubttffdd/xbadmanners

Tool for CVE-2018-16323

data-exfiltrationexploitationmemory-forensics+2
837 years ago
silph preview

silph

GitHubalmounah/silph

Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall

authenticationmemory-forensicspassword-cracking+3
1509 months ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
digital-forensicsforensicsincident-response+4
2188 years ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k8 days ago
ProcDump-for-Linux preview

ProcDump-for-Linux

GitHubmicrosoft/procdump-for-linux

A Linux version of the ProcDump Sysinternals tool

debuggersdynamic-analysis-sandboxingincident-response+2
3.1k1 day ago
Previous123456Next