SHA-256-Backdoor-Discovery-Engine

Detects potential backdoors in SHA-256 hashes using cryptographic analysis and pattern recognition. Designed for malware analysis and security…

Detects potential backdoors in SHA-256 hashes using cryptographic analysis and pattern recognition. Designed for malware analysis and security…

Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…

Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.

Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…

An easy-to-use library for emulating memory dumps. Useful for malware analysis (config extraction, unpacking) and dynamic analysis in general…

Cross-platform Yara scanner written in Go

🦆 Malduck is your ducky companion in malware analysis journeys

wsb-detect enables you to detect if you are running in Windows Sandbox ("WSB")

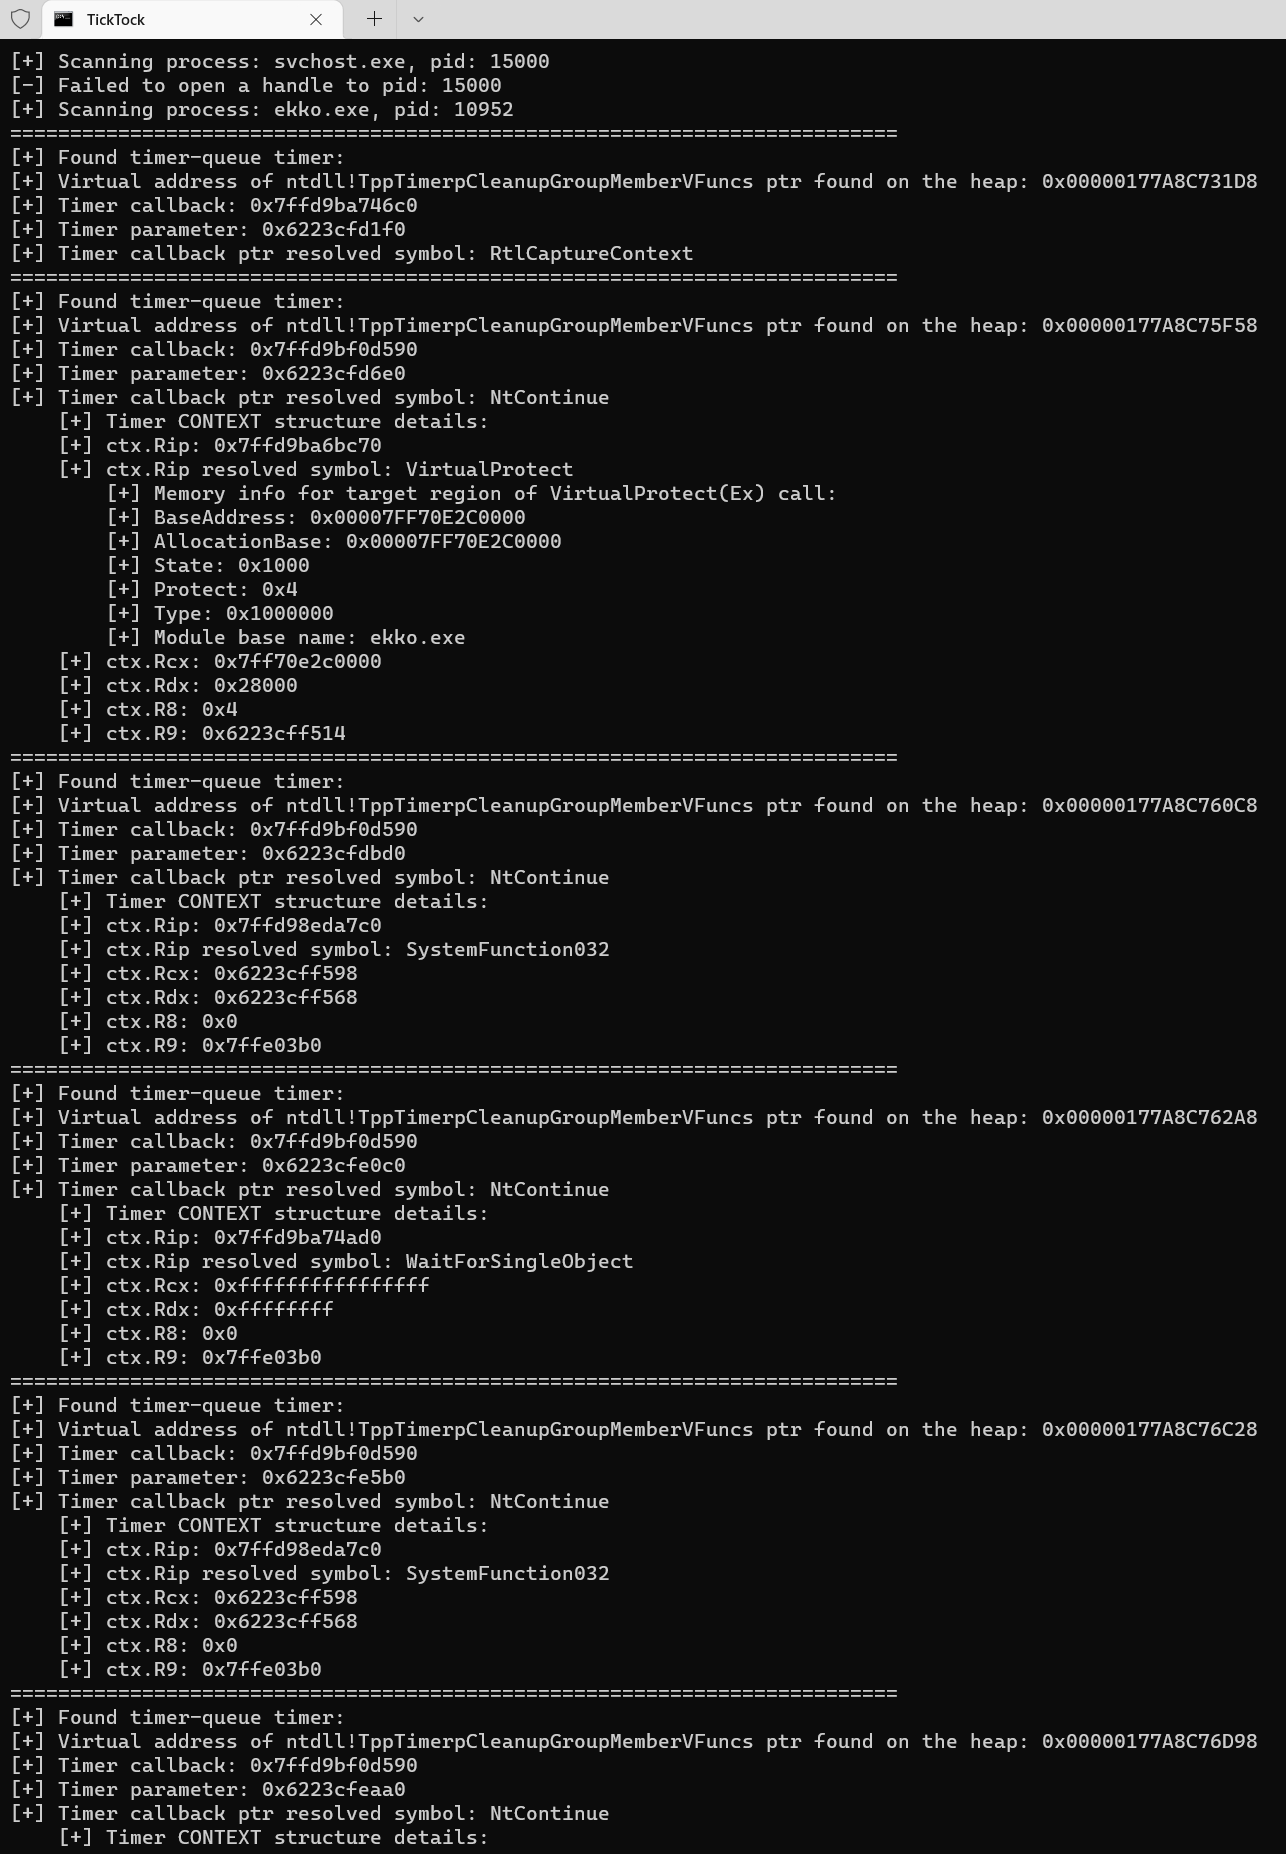
Enumerates Windows timer-queue timers to detect Ekko sleep obfuscation, aiding memory forensics and malware analysis in identifying evasive…

A scanner that files with compromised or untrusted code signing certificates written in python.

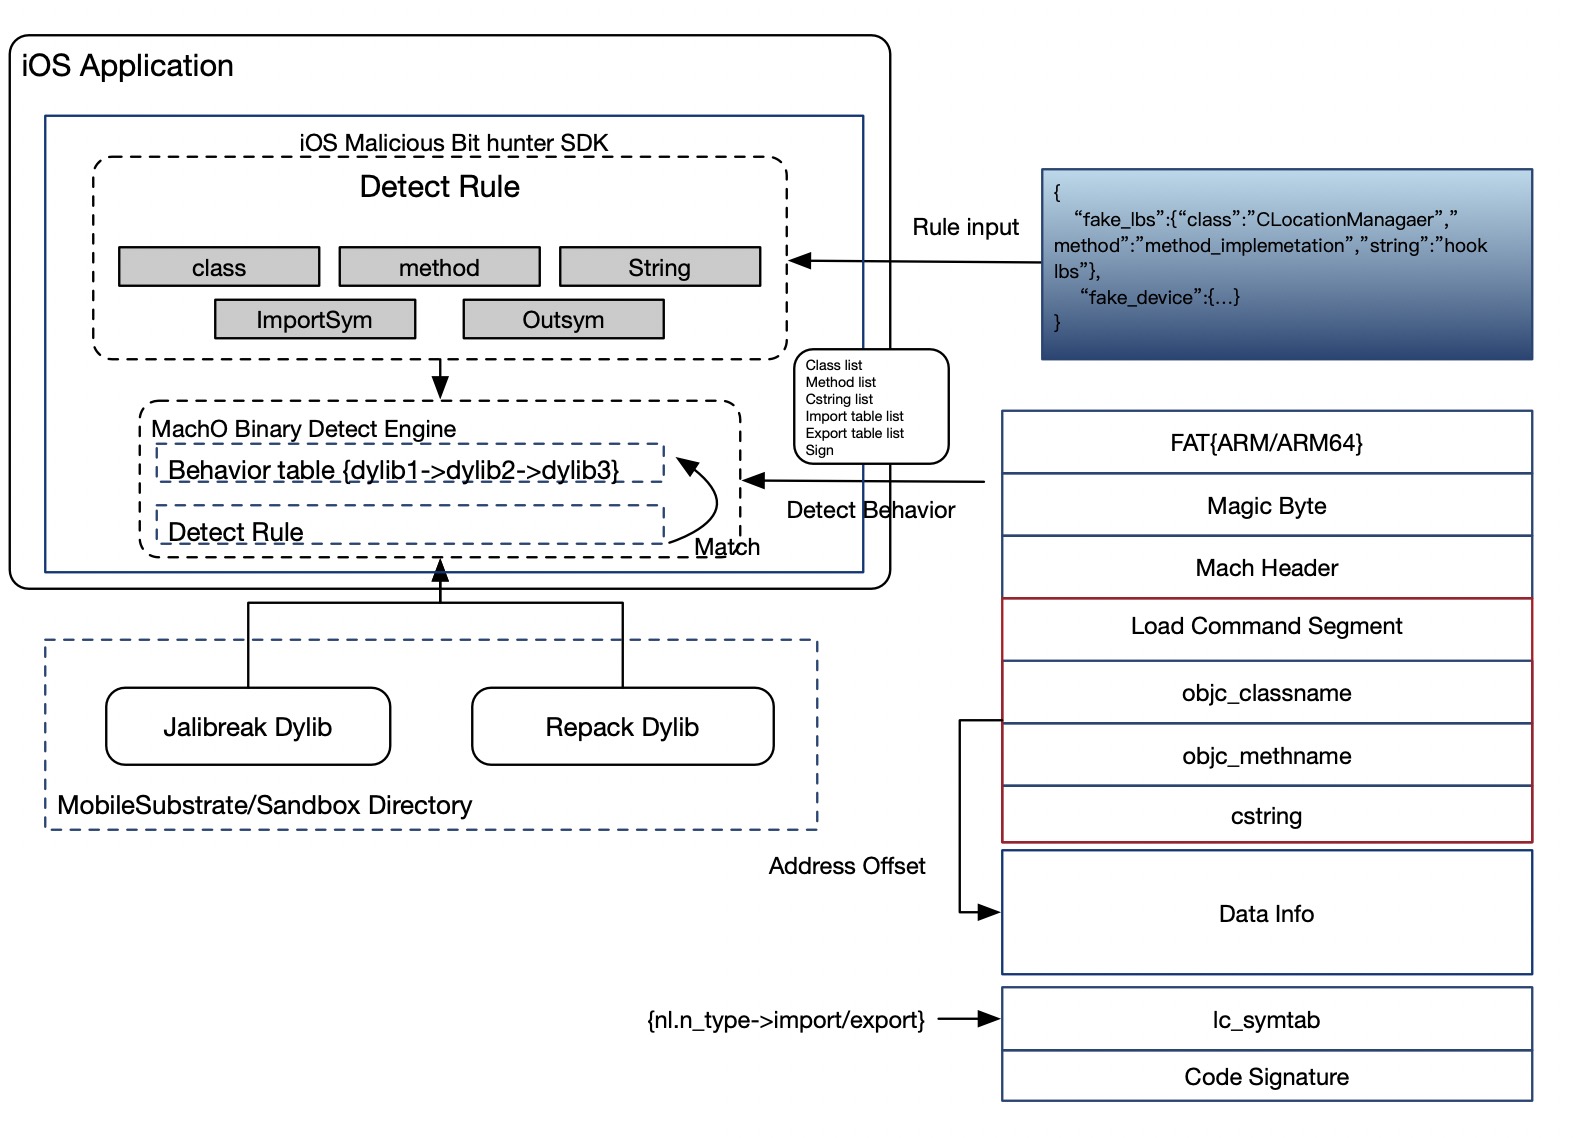
iOS Malicious Bit Hunter is a malicious plug-in detection engine for iOS applications. It can analyze the head of the macho file of the injected…

The Web Exploit Detector is a Node.js application used to detect possible infections, malicious code and suspicious files in web hosting environments

This Repository is created after my own research into malicious browser extensions, by brining the work of many others and news articles into one…

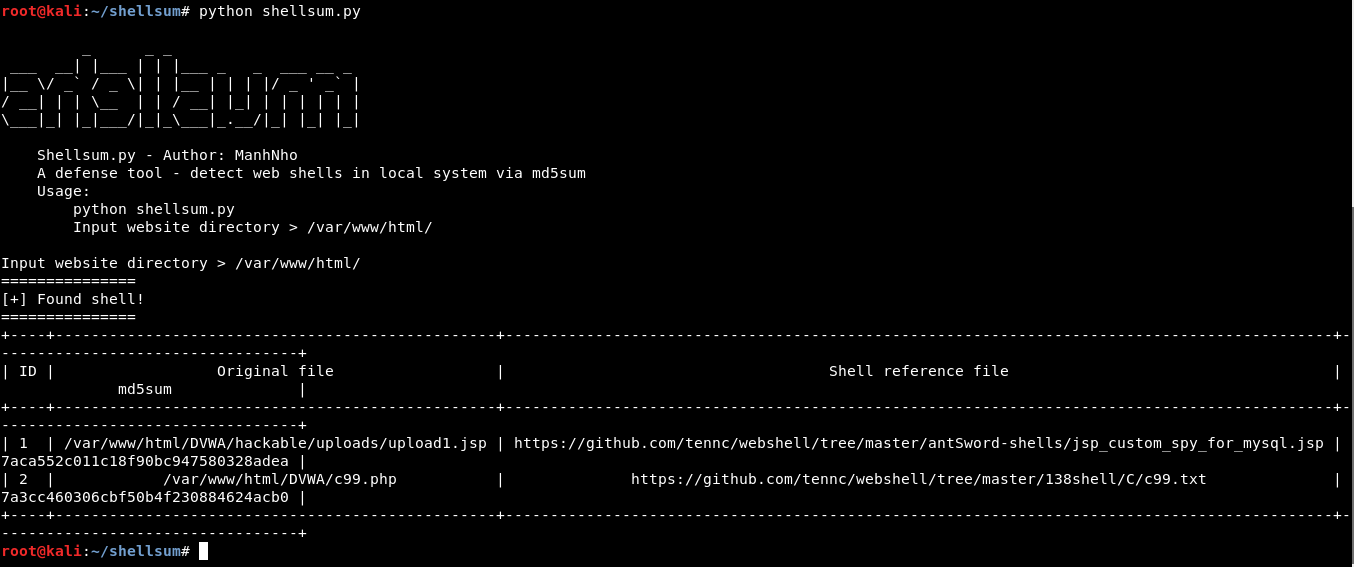
A defense tool - detect web shells in local directories via md5sum

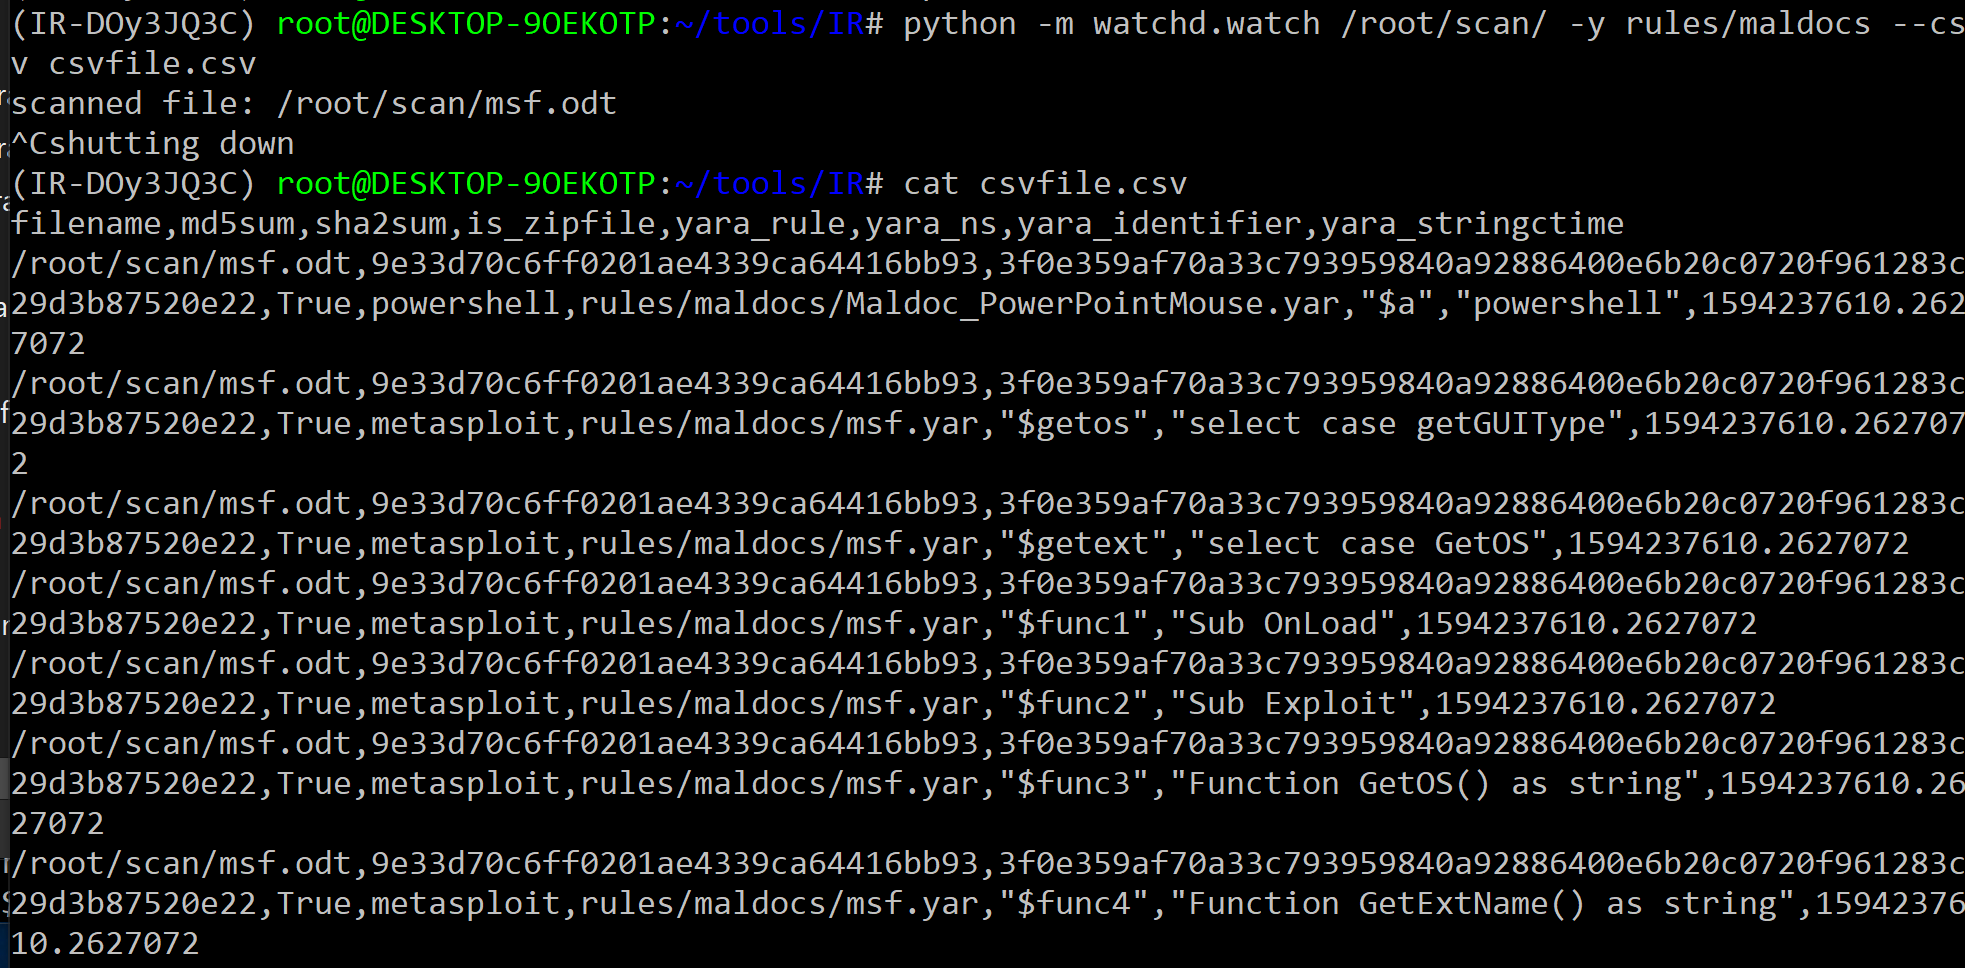
YARA-based file scanner that monitors directories, detects malware in document archives, and outputs CSV results for SIEM integration.