
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
21 results
dnschef preview

dnschef

GitHubiphelix/dnschef

DNSChef - DNS proxy for Penetration Testers and Malware Analysts
dns-analysisinformation-gatheringmalware-analysis+2
1.1k7 years ago
ReverseKit preview

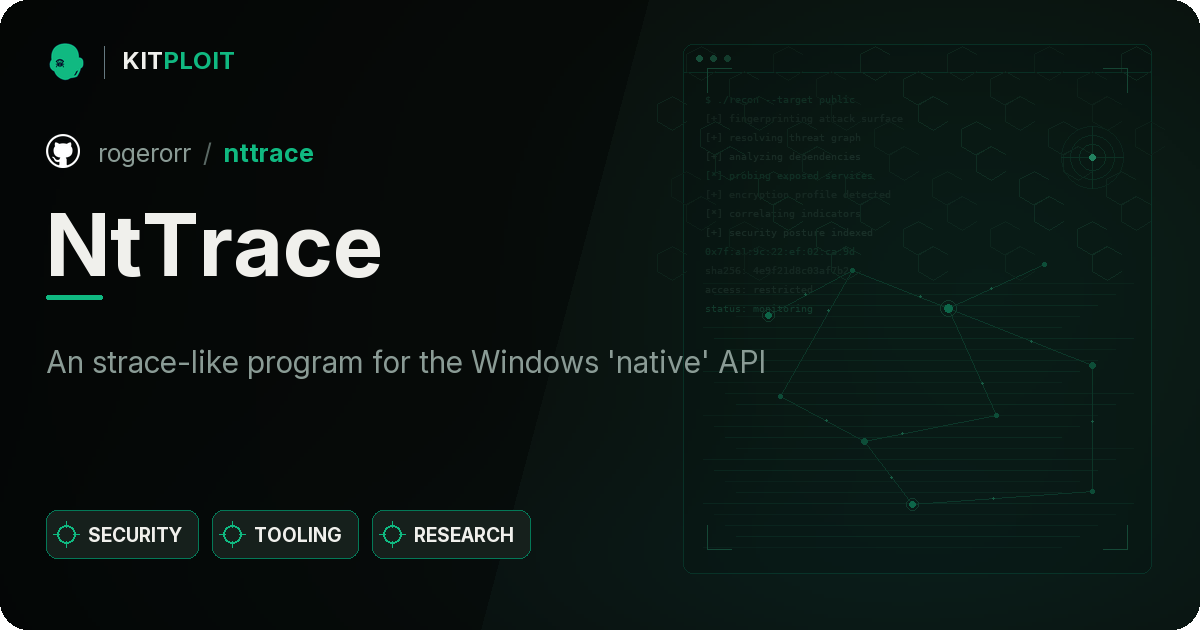
ReverseKit

GitHubzer0condition/reversekit

x64 Dynamic Reverse Engineering Toolkit
binary-analysisdynamic-code-analysismalware-analysis+1
7933 years ago
NtTrace preview

NtTrace

GitHubrogerorr/nttrace

An strace-like program for the Windows 'native' API
api-security-testingdebuggersdynamic-code-analysis+2
3911 month ago
VMUnprotect.Dumper preview

VMUnprotect.Dumper

GitHubvoid-stack/vmunprotect.dumper

VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.

binary-analysisdynamic-code-analysismalware-analysis+1
4634 years ago
fnprint preview

fnprint

GitHub1rhino2/fnprint

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
binary-analysisdynamic-code-analysisfirmware-analysis+3
5514 days ago
maps_scanner preview

maps_scanner

GitHubhackinglz/maps_scanner

MAPS cloud scanner and response parser for Microsoft Defender research.
api-security-testingdynamic-analysis-sandboxingfuzzing+6
968 months ago
NebulaPulsar preview

NebulaPulsar

GitHubiss4cf0ng/nebulapulsar

NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
dynamic-code-analysiseducationencryption-decryption-tools+7
473 months ago
ExportHider preview

ExportHider

GitHubfrkngksl/exporthider

ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
binary-analysisdynamic-code-analysisexploitation+4
366 months ago
ghidra_stack_strings preview

ghidra_stack_strings

GitHubzxgio/ghidra_stack_strings

A script to detect stack-strings by using emulation (leveraging Unicorn)
binary-analysisdynamic-code-analysismalware-analysis+1
3510 months ago
pesieve-go preview

pesieve-go

GitHubhasherezade/pesieve-go

Golang bindings for PE-sieve
binary-analysisdynamic-code-analysismalware-analysis+1
432 years ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications

api-security-testingbinary-analysisdebuggers+4
204 months ago
javascript-deobfuscator preview

javascript-deobfuscator

GitHublolcaken/javascript-deobfuscator

Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)

code-analysisdynamic-code-analysismalware-analysis+4
816 days ago
de4dot preview
Archived

de4dot

GitHubde4dot/de4dot

.NET deobfuscator and unpacker.

binary-analysisdynamic-code-analysismalware-analysis+2
7.4k6 years ago
malware-research preview

malware-research

GitHubeset/malware-research

Code written as part of our various malware investigations
digital-forensicsdynamic-code-analysismalware-analysis+4
41512 days ago
pmg preview

pmg

GitHubsafedep/pmg

PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
cloud-securitycontainer-securitydevsecops+6
5531 day ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

binary-analysiscommand-and-controleducation+6
53 months ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
75 months ago
dnschef-ng preview
Archived

dnschef-ng

GitHubbyt3bl33d3r/dnschef-ng

DNSChef (NG) - DNS proxy for Penetration Testers and Malware Analysts

data-exfiltrationdns-analysisinformation-gathering+4
1752 years ago
Previous12Next