
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
85 results
moneta preview

moneta

GitHubforrest-orr/moneta

Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
digital-forensicsforensicsioc-management+3
8492 years ago
fake-sandbox preview

fake-sandbox

GitHubnuclearphoenixx/fake-sandbox

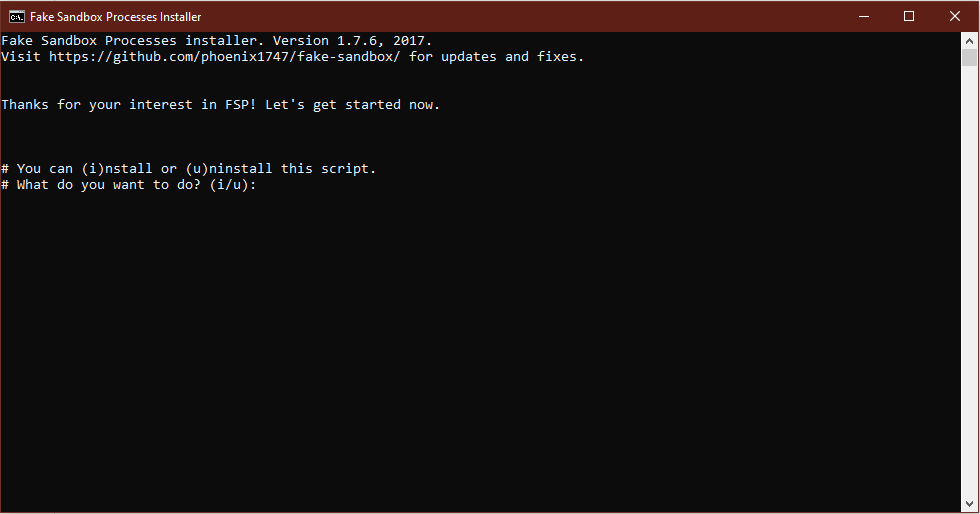
👁‍🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.

anti-botdefensive-toolsids-ips-evasion+1
1411 year ago
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.2k14h 32m ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.0k3 days ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k4 months ago
mac-monitor preview

mac-monitor

GitHubbrandon7cc/mac-monitor

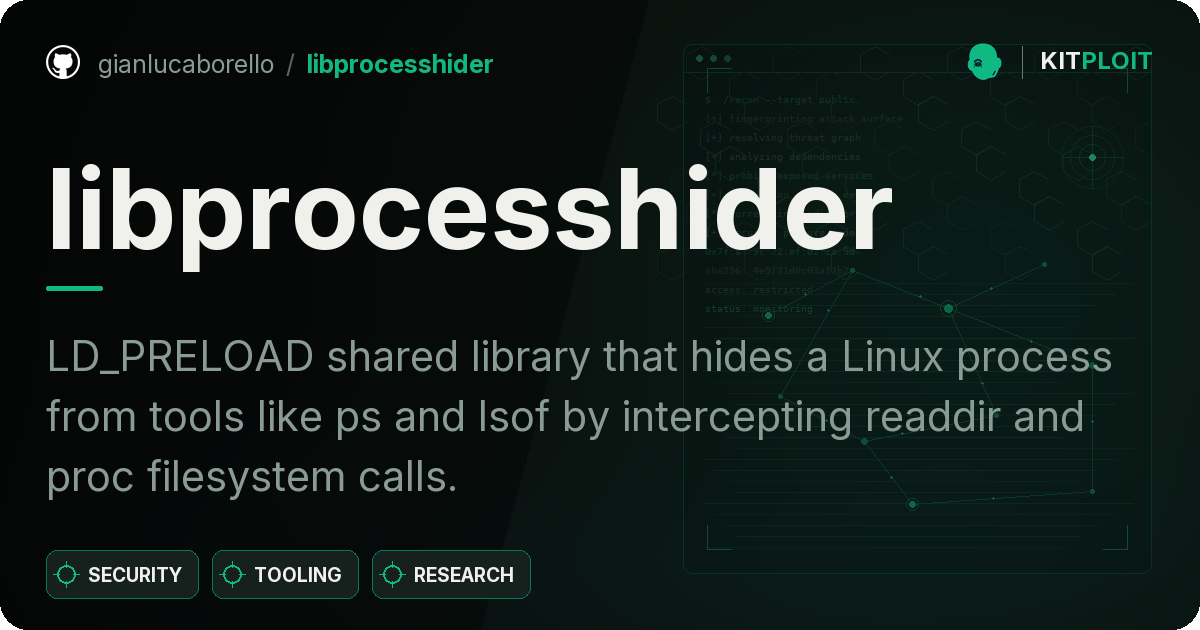
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
dynamic-analysis-sandboxingeducationforensics+2
1.4k16 days ago
libprocesshider preview

libprocesshider

GitHubgianlucaborello/libprocesshider

LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
defensive-toolsinformation-gatheringmalware-analysis+4
1.1k7 years ago
windows-api-function-cheatsheets preview

windows-api-function-cheatsheets

GitHub7etsuo/windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
binary-analysiscurated-resourcesmalware-analysis+3
1.5k2 years ago
BestEdrOfTheMarket preview

BestEdrOfTheMarket

GitHubxacone/bestedrofthemarket

Open-source Windows kernel-level EDR lab for understanding and testing detection methods against process injection, credential dumping, and other…

defensive-toolseducationlabs-practice+1
1.6k3 months ago
MaliciousMacroGenerator preview

MaliciousMacroGenerator

GitHubmr-un1k0d3r/maliciousmacrogenerator

Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.

malware-analysispayload-generationphishing-tools
8287 years ago
DarkWidow preview

DarkWidow

GitHubreveng007/darkwidow

Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…
binary-analysiseducationexploitation+6
8098 months ago
InjectProc preview

InjectProc

GitHubsecrary/injectproc

InjectProc - Process Injection Techniques [This project is not maintained anymore]

binary-exploitationeducationmalware-analysis+1
9927 years ago
MemProcFS-Analyzer preview

MemProcFS-Analyzer

GitHublethal-forensics/memprocfs-analyzer

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
anomaly-detectiondigital-forensicsincident-response+5
7381 month ago
community preview

community

GitHubvolatilityfoundation/community

Community-maintained Volatility plugin collection for memory forensics, extending memory dump analysis with modules for malware and process…

digital-forensicsmalware-analysismemory-forensics
3786 years ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
digital-forensicsdisk-forensicsforensics+7
37128 days ago
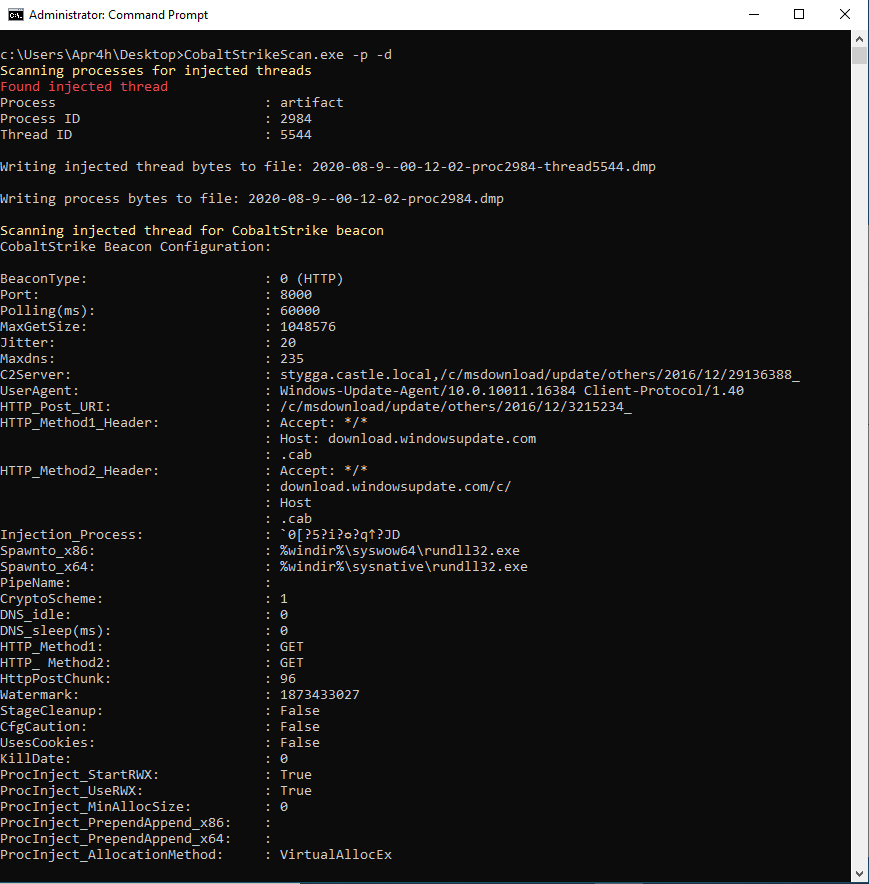
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
9165 years ago
PR0CESS preview

PR0CESS

GitHubaaaddress1/pr0cess

some gadgets about windows process and ready to use :)

exploitationmalware-analysispayload-development+3
6153 years ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

binary-analysisexploit-frameworksmalware-analysis+2
31612h 47m ago
Previous12345Next