
RansomLord
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
binary-exploitationdefensive-toolsexploitation+4
515
malvuln/ransomlordRansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 francisck/danderspritz_lab
A fully functional DanderSpritz lab in 2 commands
 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
 ir-huntguardians/cve-2023-38831-hunt
PowerShell-based tool to detect and analyze exploitation attempts targeting CVE-2023-38831, aiding incident response and forensic investigations.
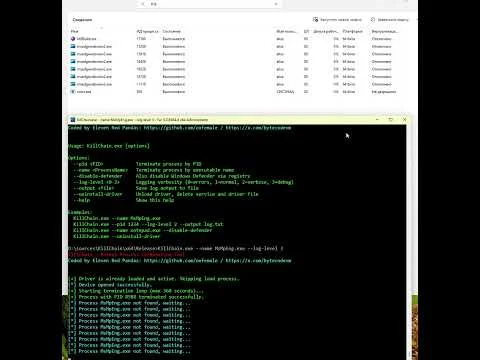 oxfemale/killchain
Kernel Process Termination Tool ( CVE-2026-0828 exploit)
 mansk1es/caboom
A malicious .cab creation tool for CVE-2021-40444
 gmh5225/dropper
Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.
 simoesctt/ctt-mailpit-rce-v1.0---temporal-resonance-mail-server-takeover
Exploit tool that transforms SMTP header injection into remote code execution with self-propagating worm capabilities, featuring persistence…
 ml-k-eng/cve-2023-38831-exploit-and-detection
This repository has both an attack detection tool and a Proof-of-Concept (PoC) Python script for the WinRAR CVE-2023-38831 vulnerability.
 shri142/zipscan
A tool written in Go that scans files & directories for the Follina exploit (CVE-2022-30190)
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 cyberforce/pesidious
Malware Mutation Using Reinforcement Learning and Generative Adversarial Networks
 machine1337/pyobfuscate
A simple and efficent script to obfuscate python payloads to make it completely FUD
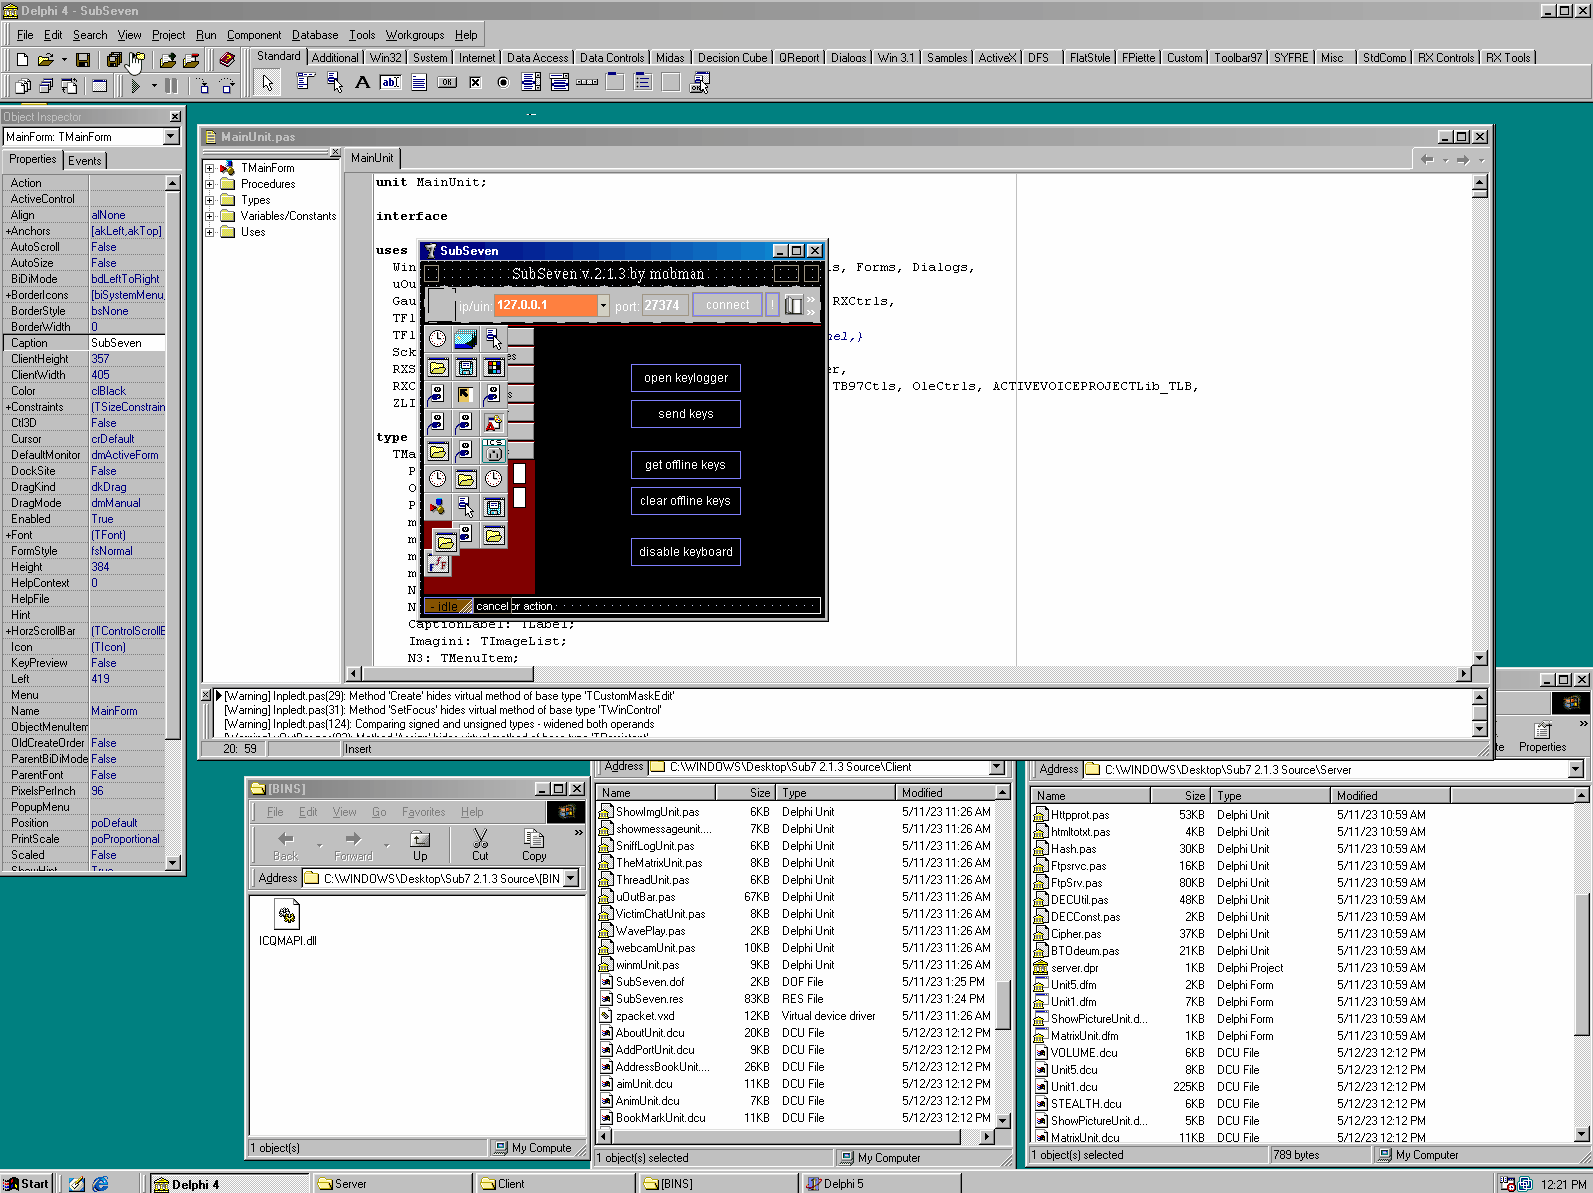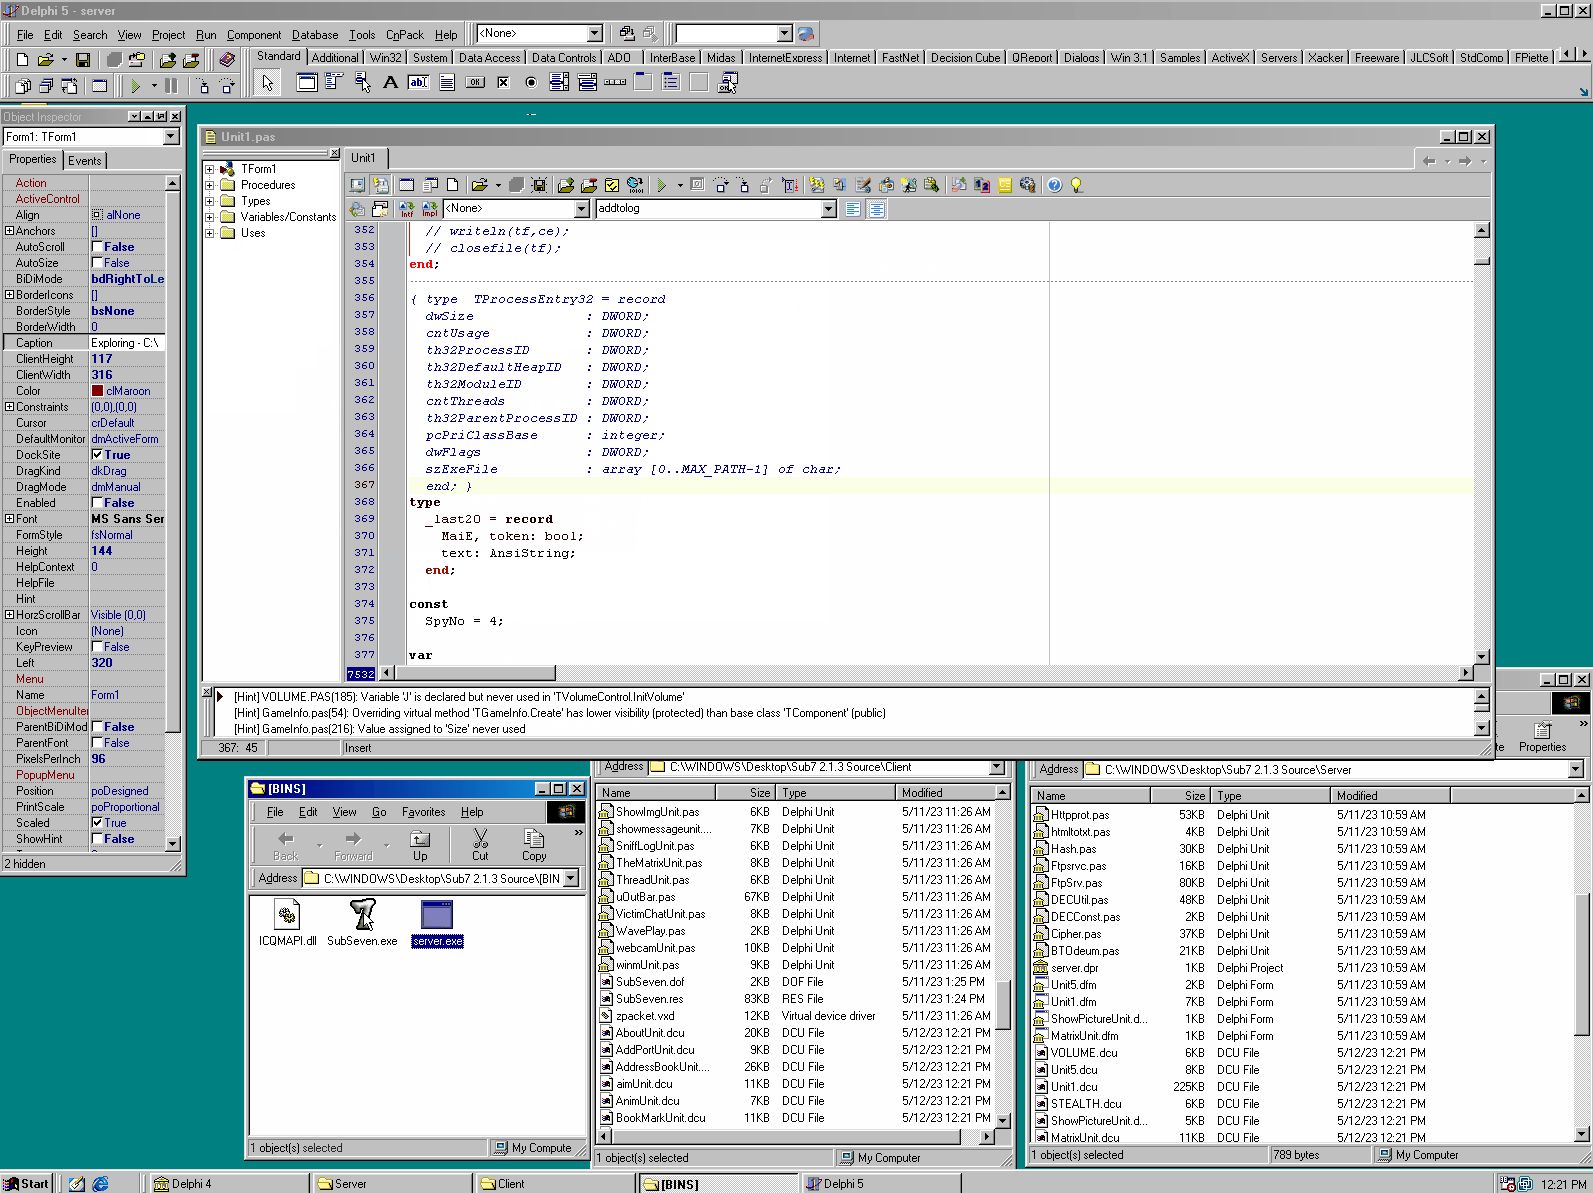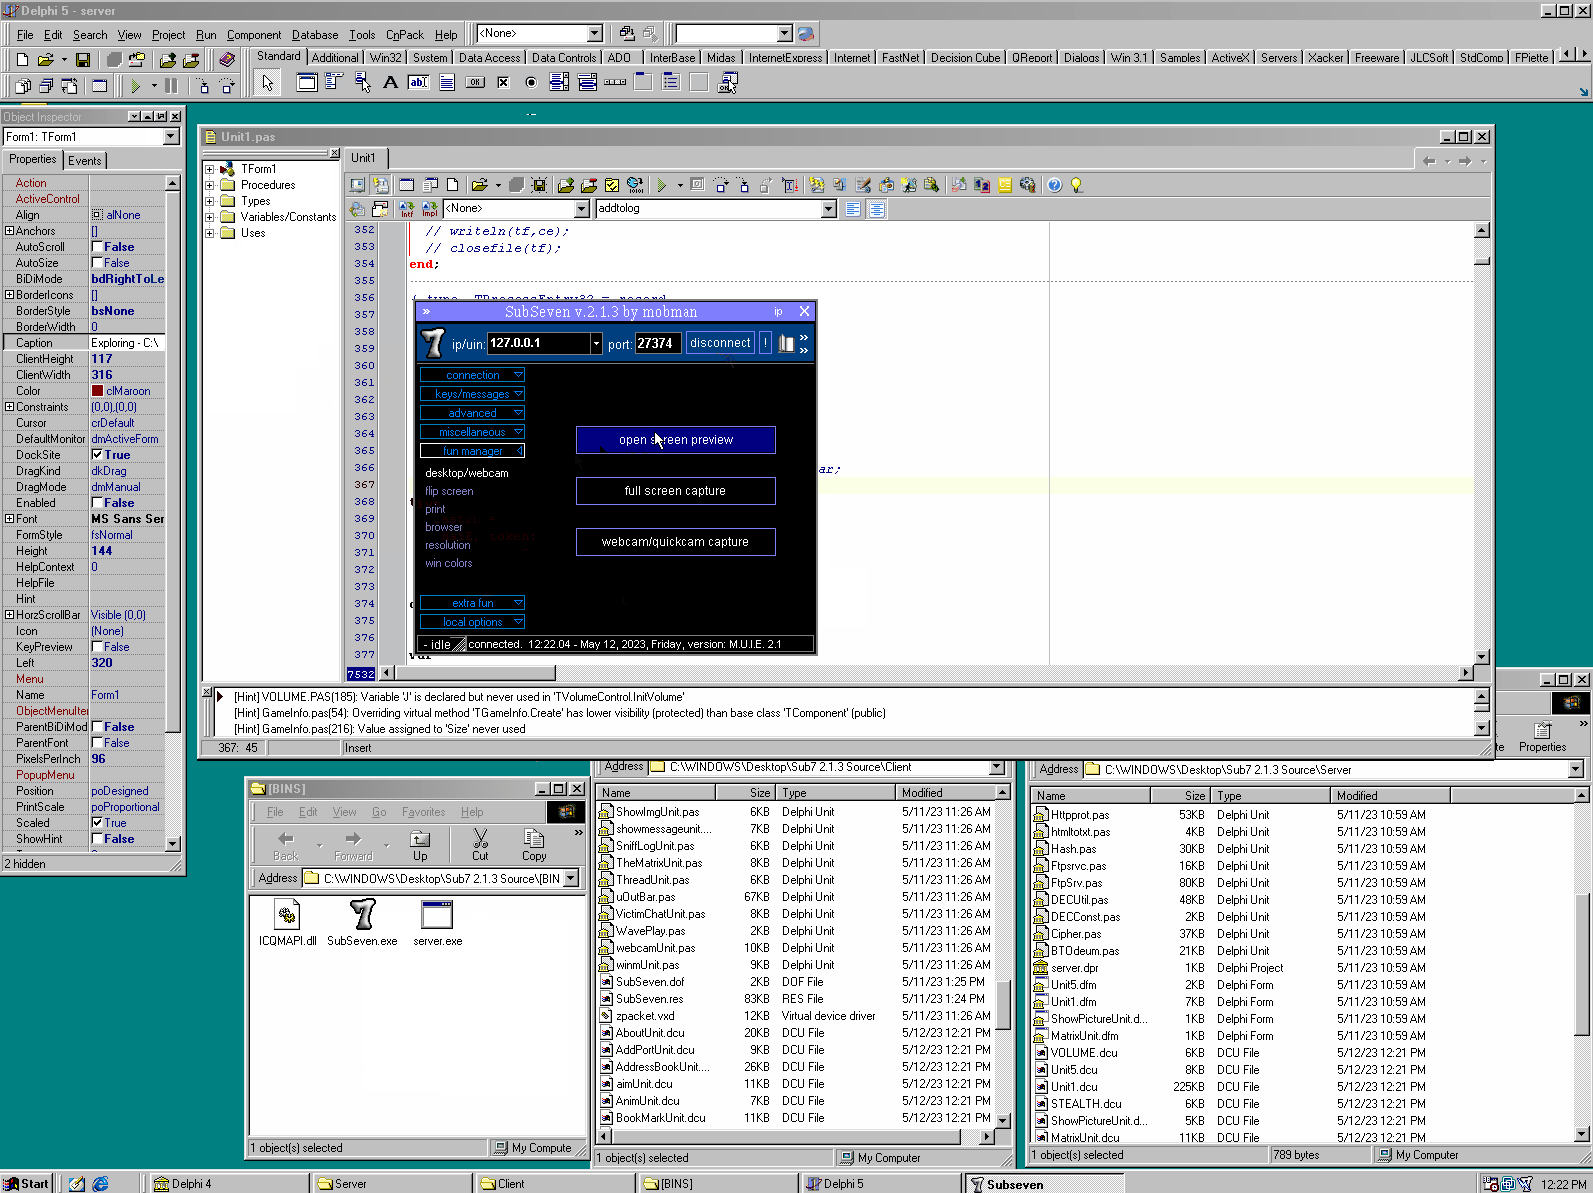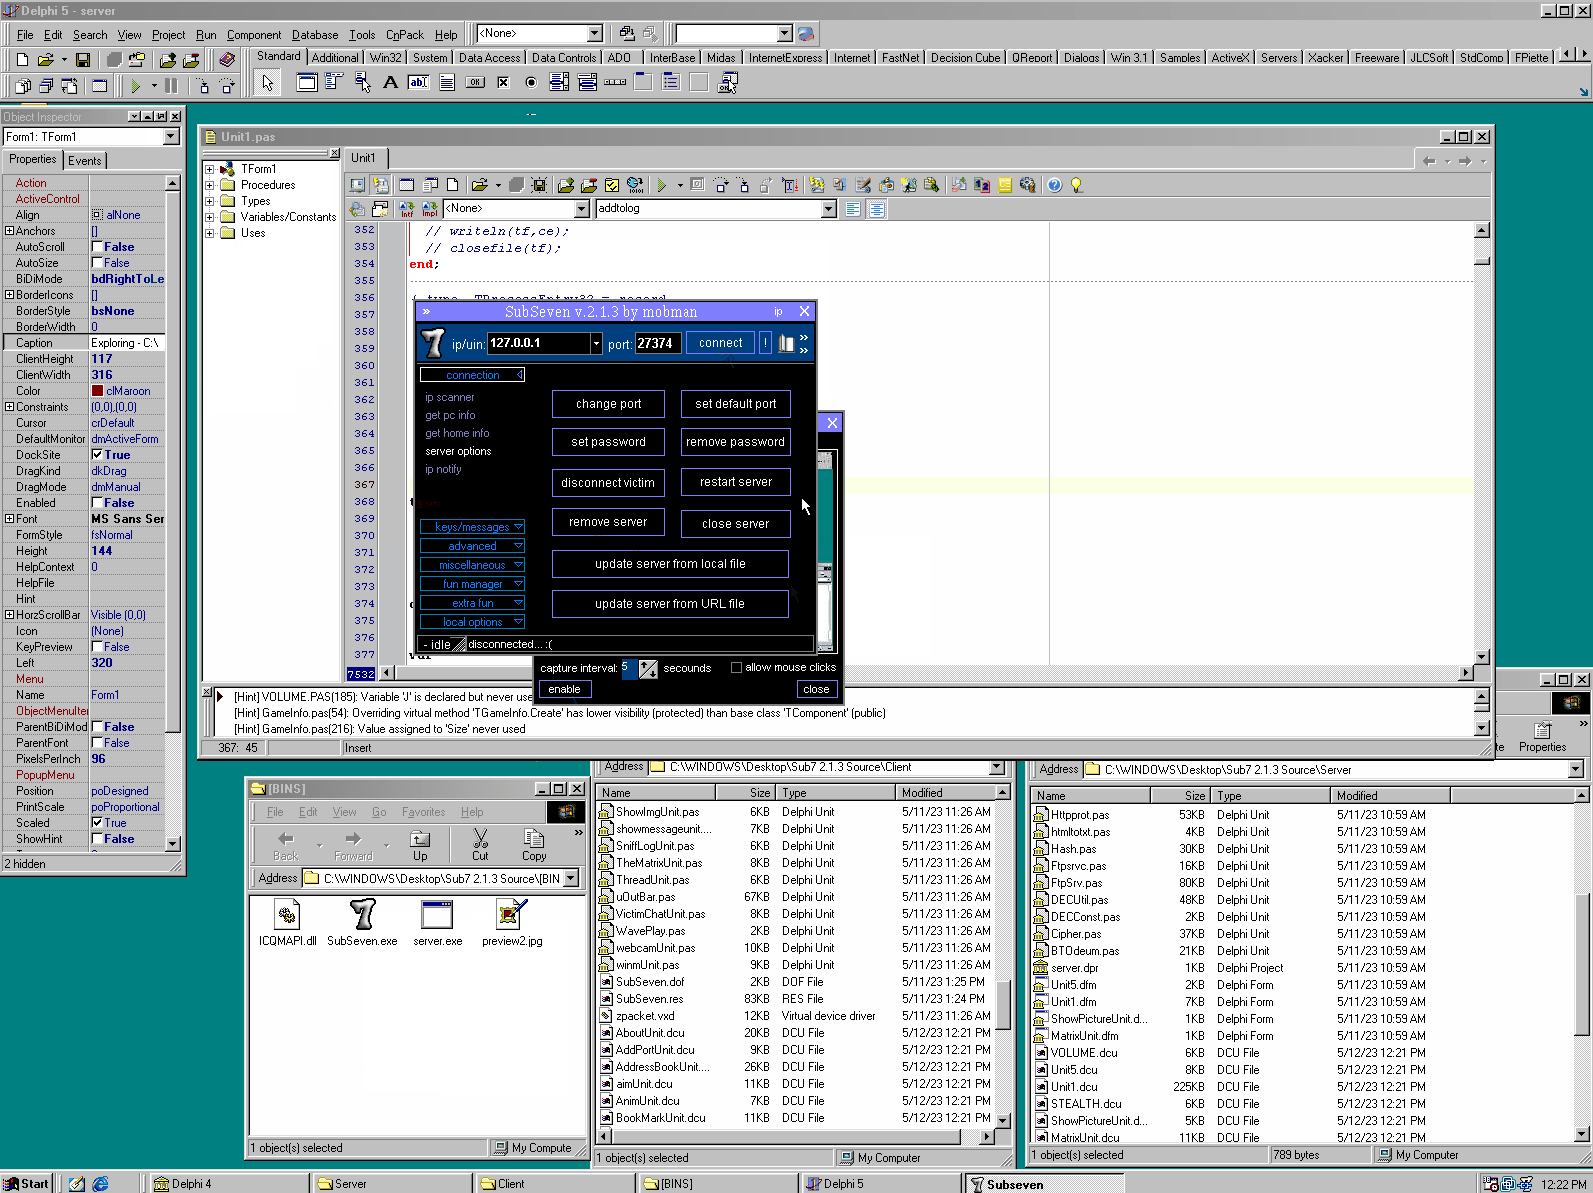
 illwill/sub7
Source code for SubSeven 2.1.3
 0xlane/xz-cve-2024-3094
XZ Backdoor Extract(Test on Ubuntu 23.10)
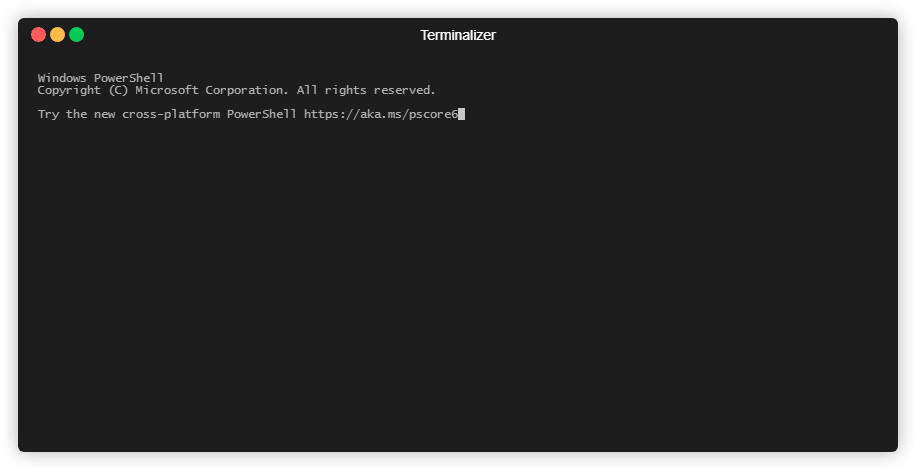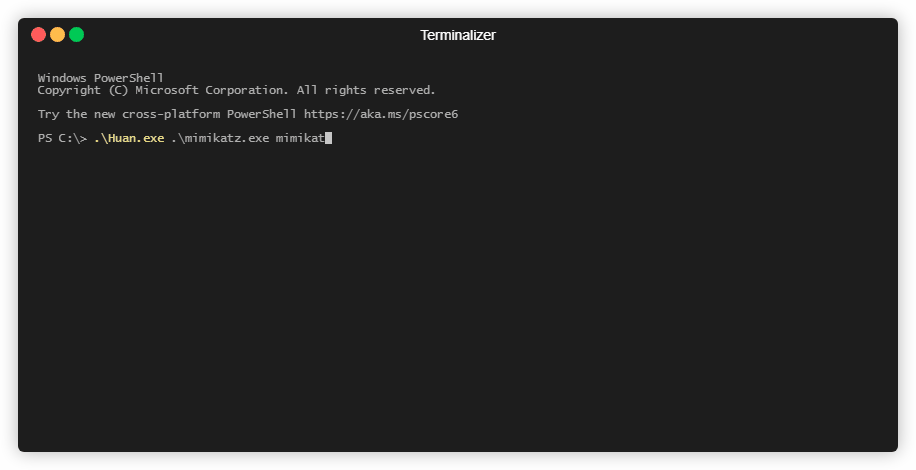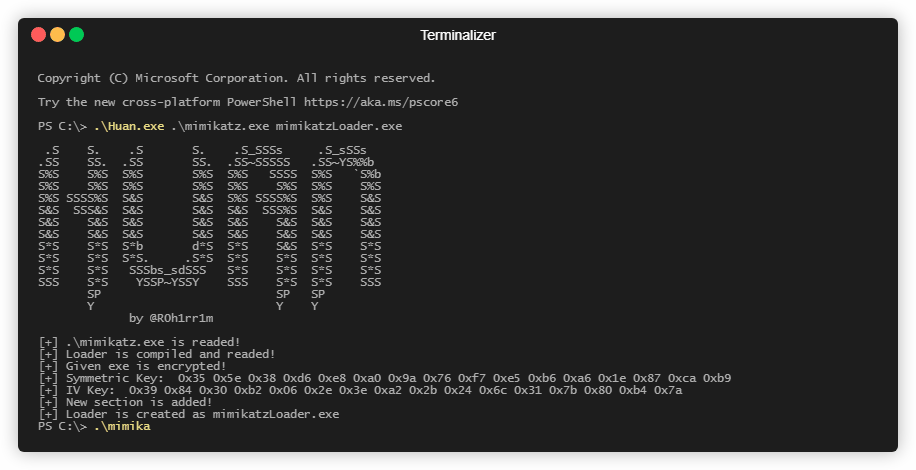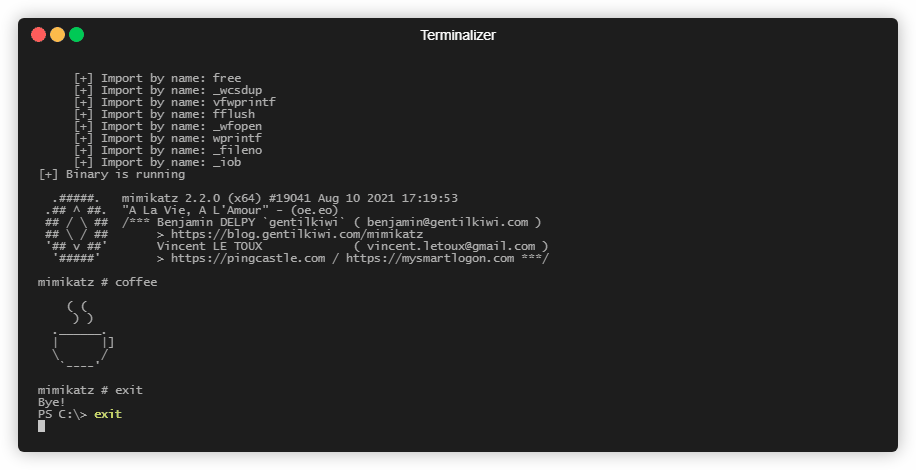 frkngksl/huan
Encrypted PE Loader Generator
 vortexcry-organization/vortexcry-ransomware-release
Advanced ransomware using process injection and kernel driver loading via CVE-2019-16098 to encrypt files, disable recovery, and demand ransom. For…