CVE-2021-40444-exp
 lisinan988/cve-2021-40444-exp
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
command-and-controlexploitationmalware-analysis+2
lisinan988/cve-2021-40444-expGenerates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…
 initconf/cve-2017-5638_struts
Bro/Zeek script for detecting Apache Struts CVE-2017-5638 reconnaissance, compromise, and malware download tracking with automated IP extraction.
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 omriher/captipper
Malicious HTTP traffic explorer
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
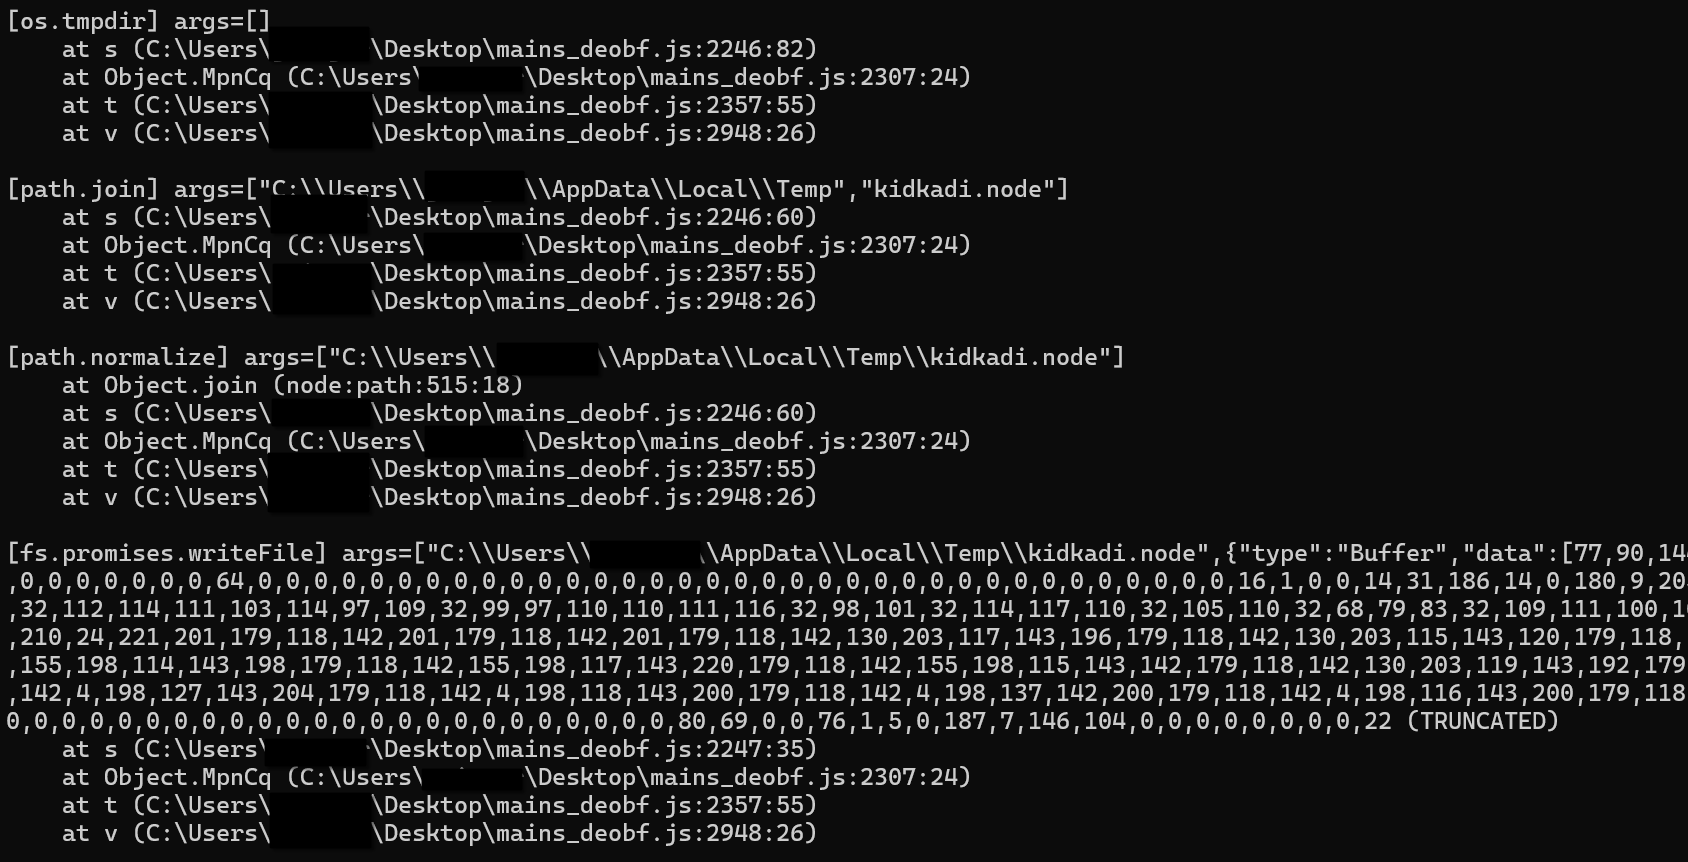 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
 al0ne/linuxcheck
Linux应急处置/信息搜集/漏洞检测工具,支持基础配置/网络流量/任务计划/环境变量/用户信息/Services/bash/恶意文件/内核Rootkit/SSH/Webshell/挖矿文件/挖矿进程/供应链/服务器风险等13类70+项检查