

androguard
 androguard/androguard
Reverse engineering and pentesting for Android applications
android-securitydynamic-analysis-sandboxingmalware-analysis+6
6.4k1 day ago
androguard/androguardReverse engineering and pentesting for Android applications
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 rednaga/apkid
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
 calebfenton/simplify
Android virtual machine and deobfuscator
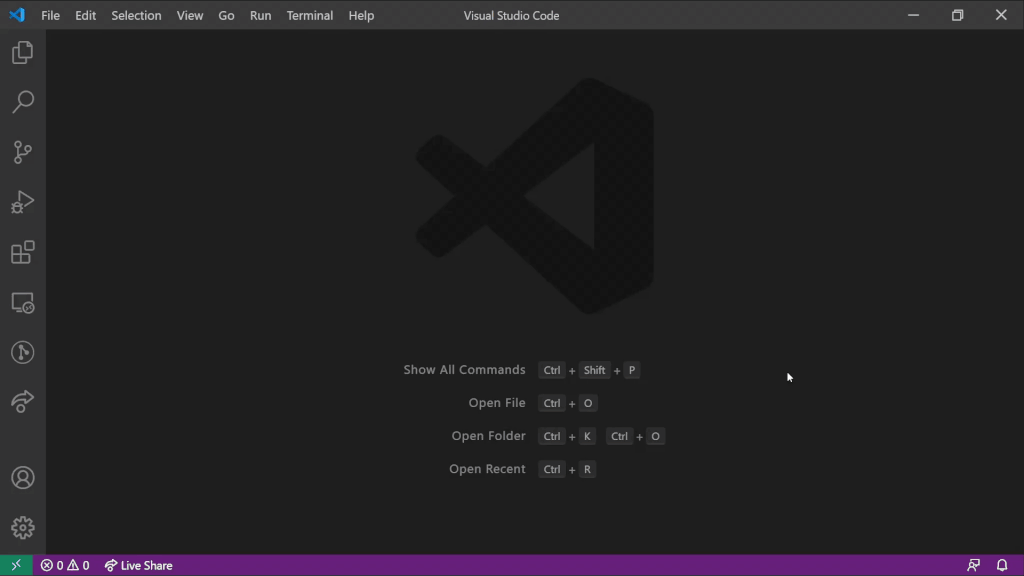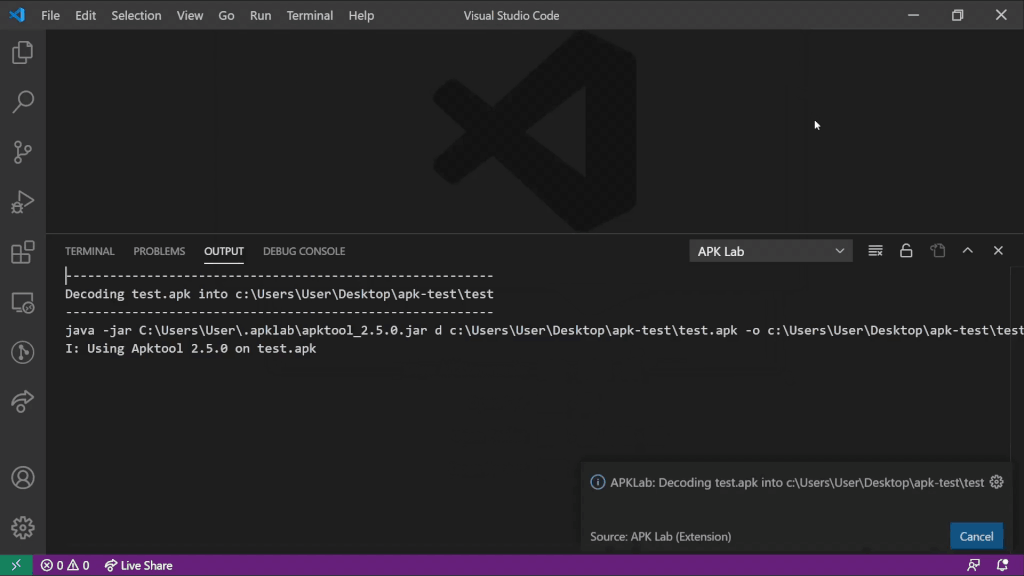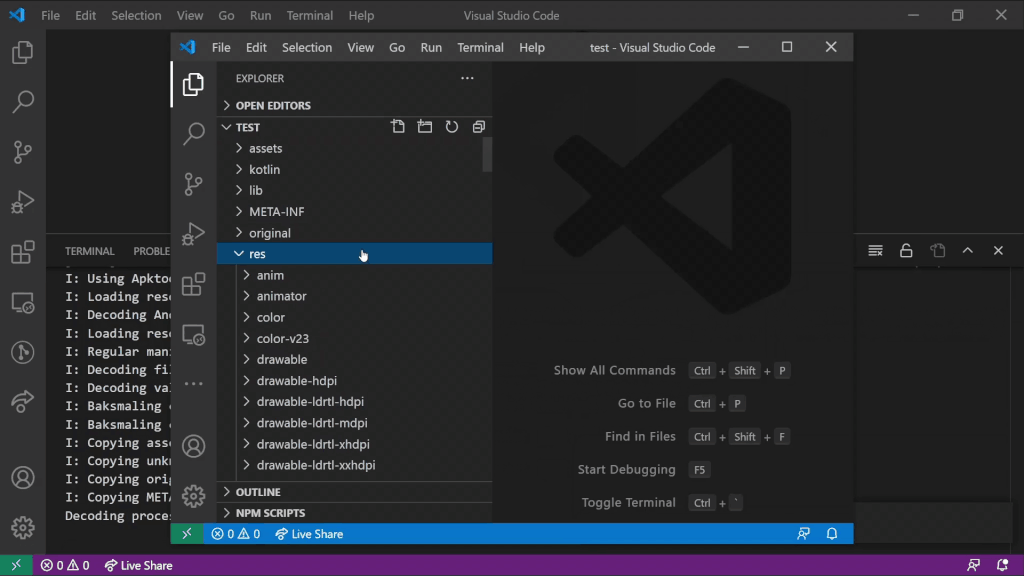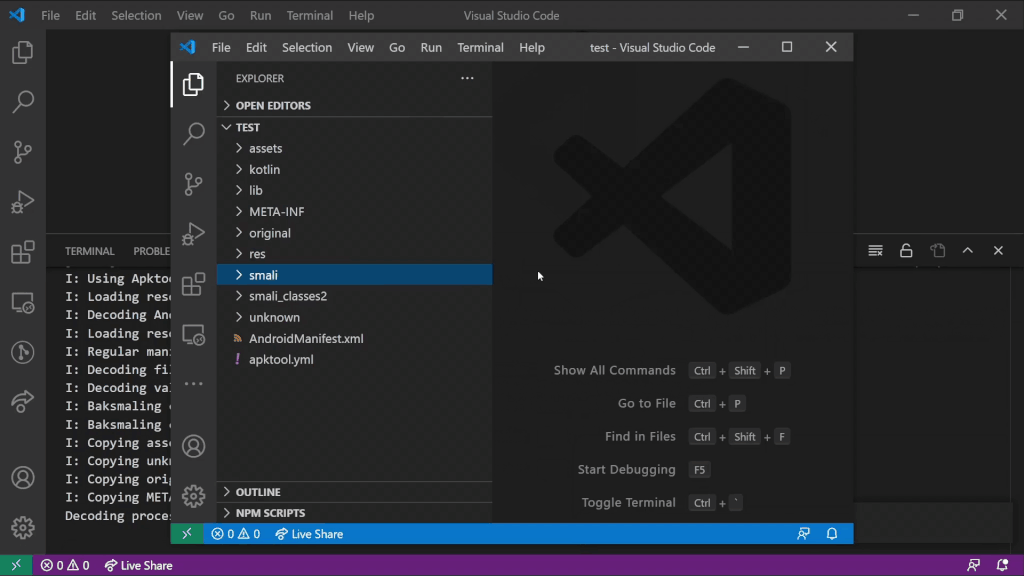 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
 sh4hin/androl4b
A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
 user1342/droiddetective
A machine learning malware analysis framework for Android apps.
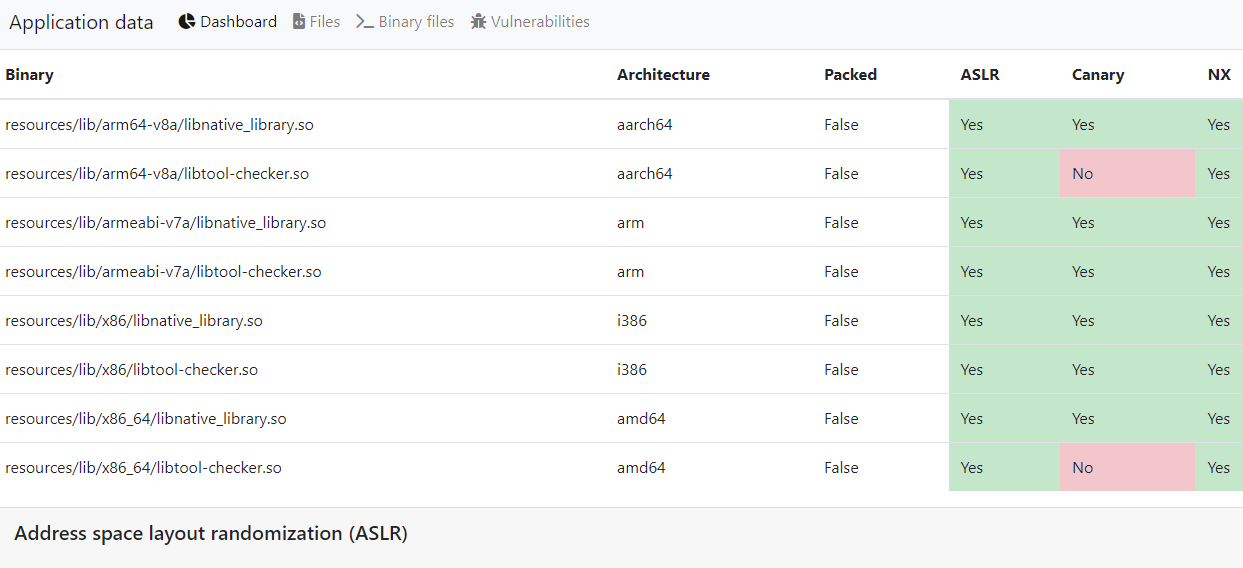 stefan2200/aparoid
Static and dynamic Android application security analysis
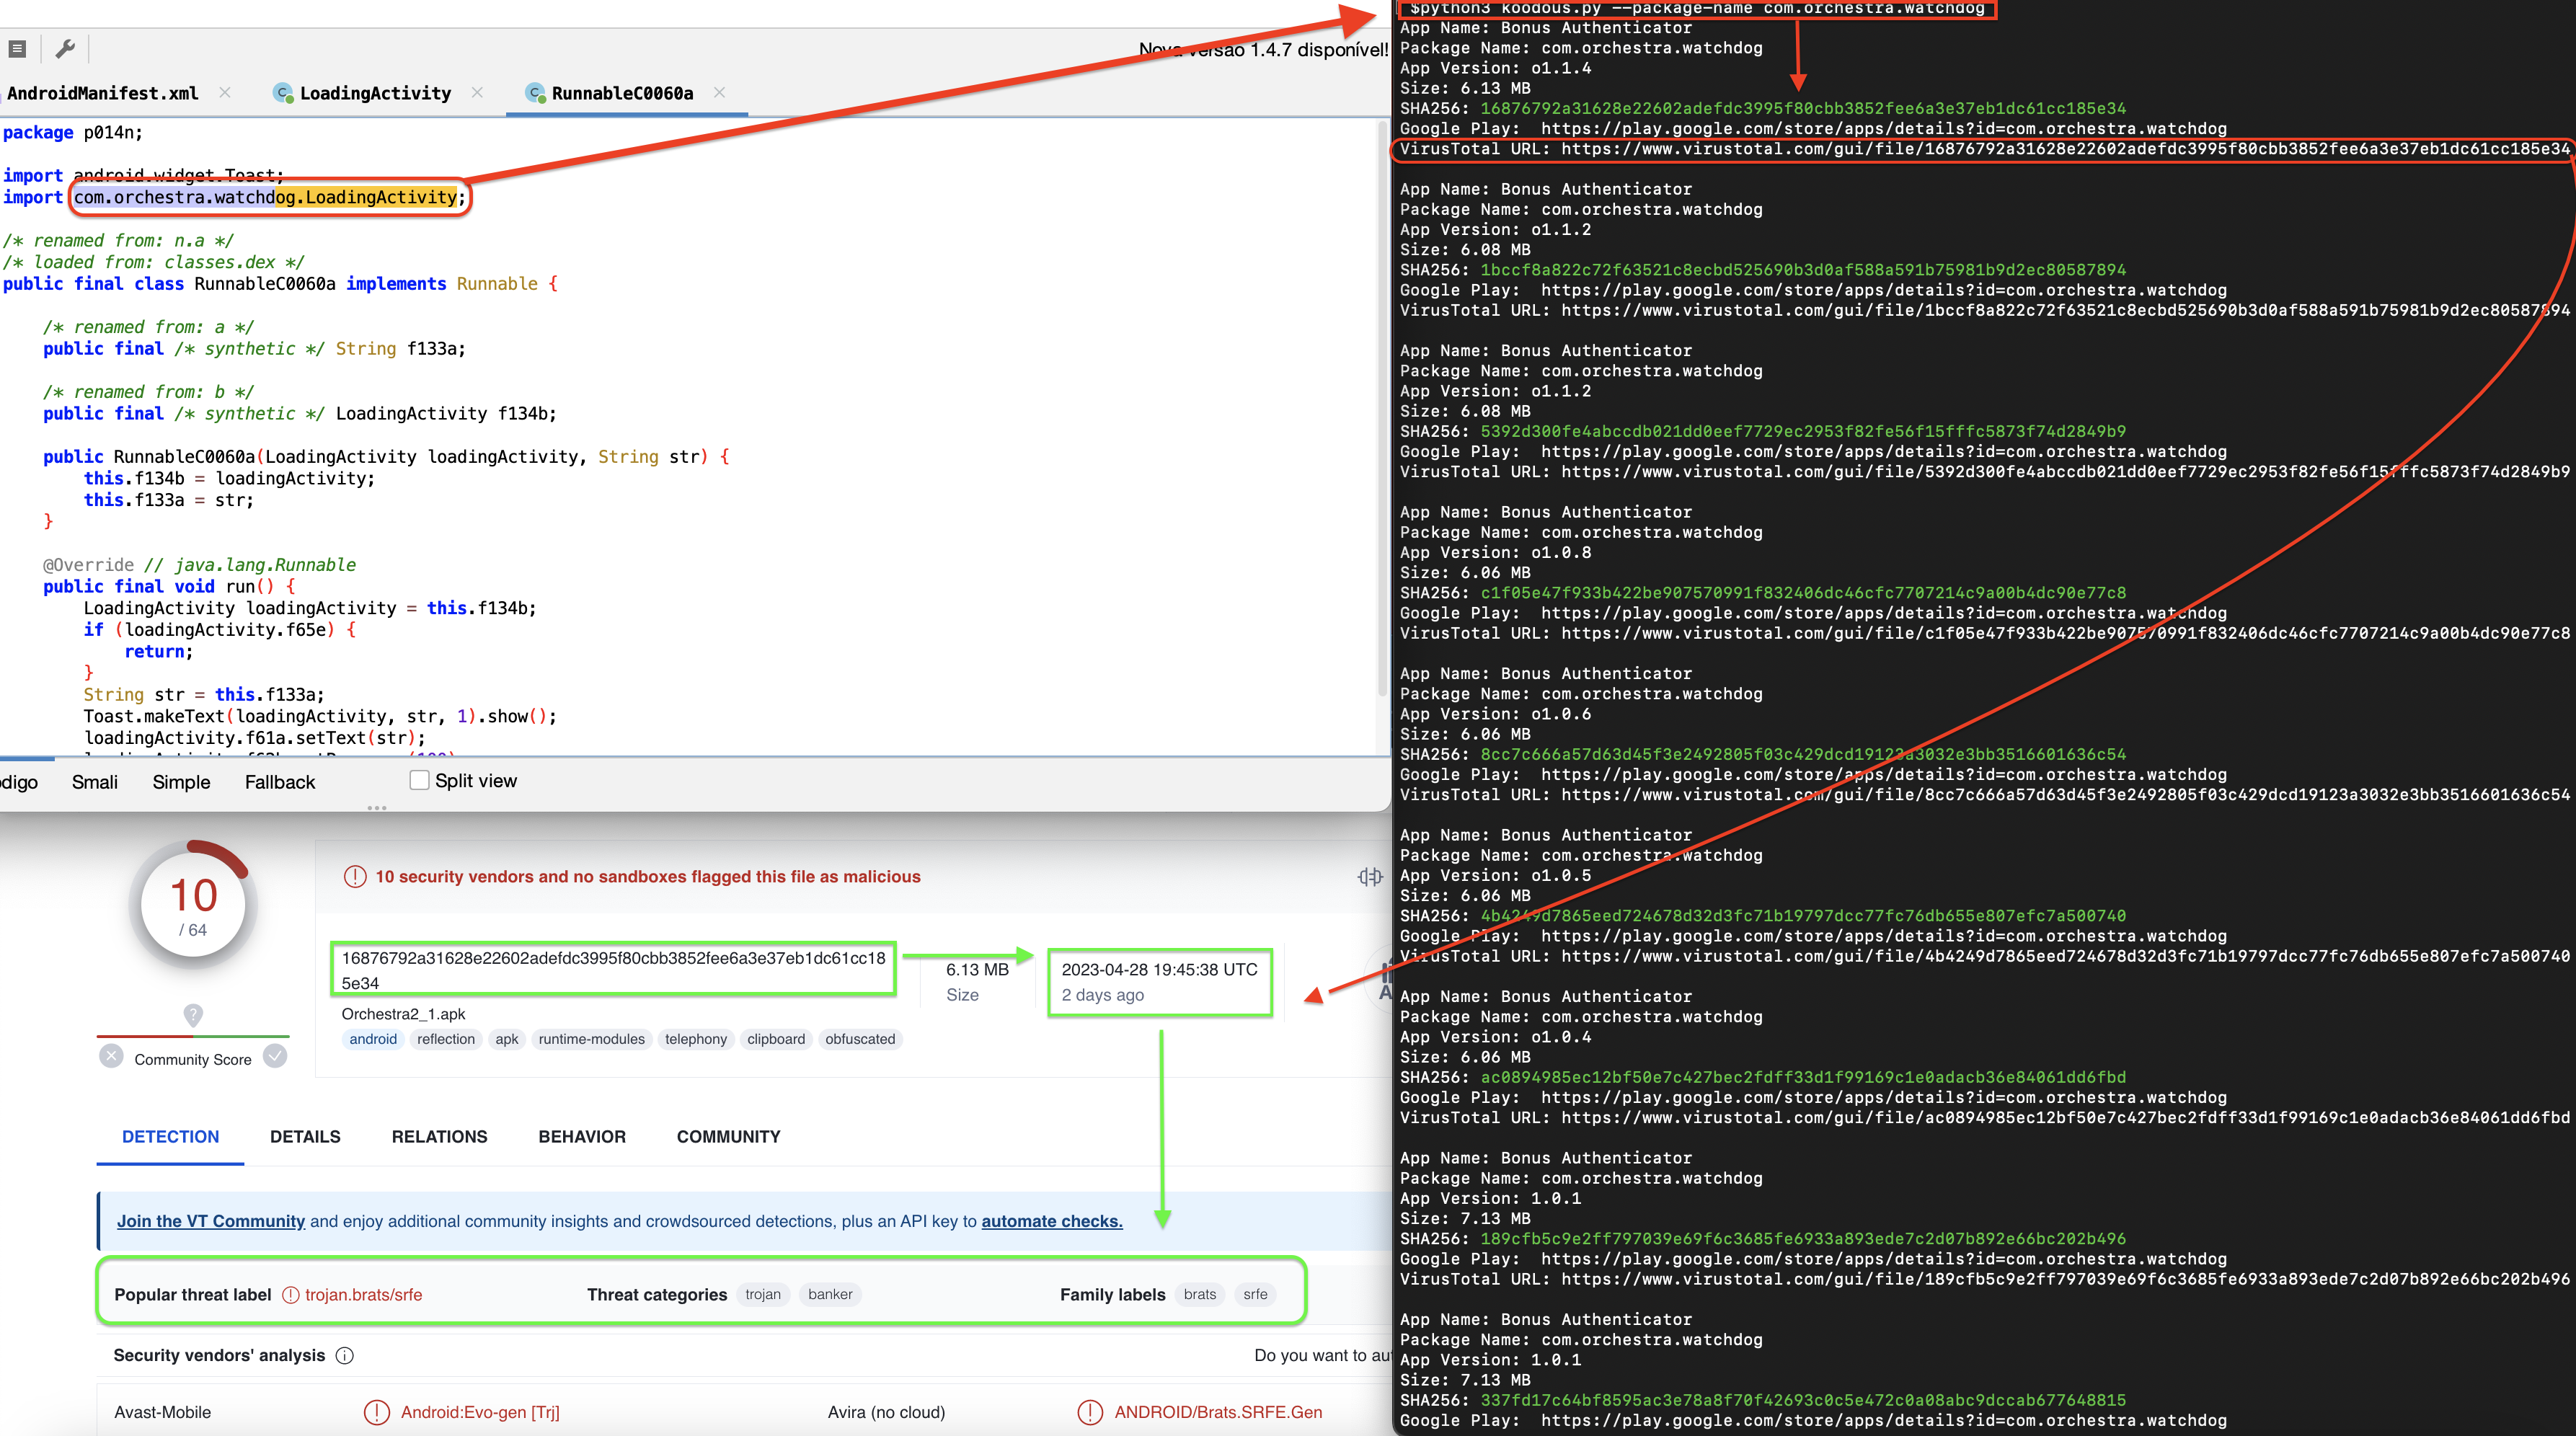 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
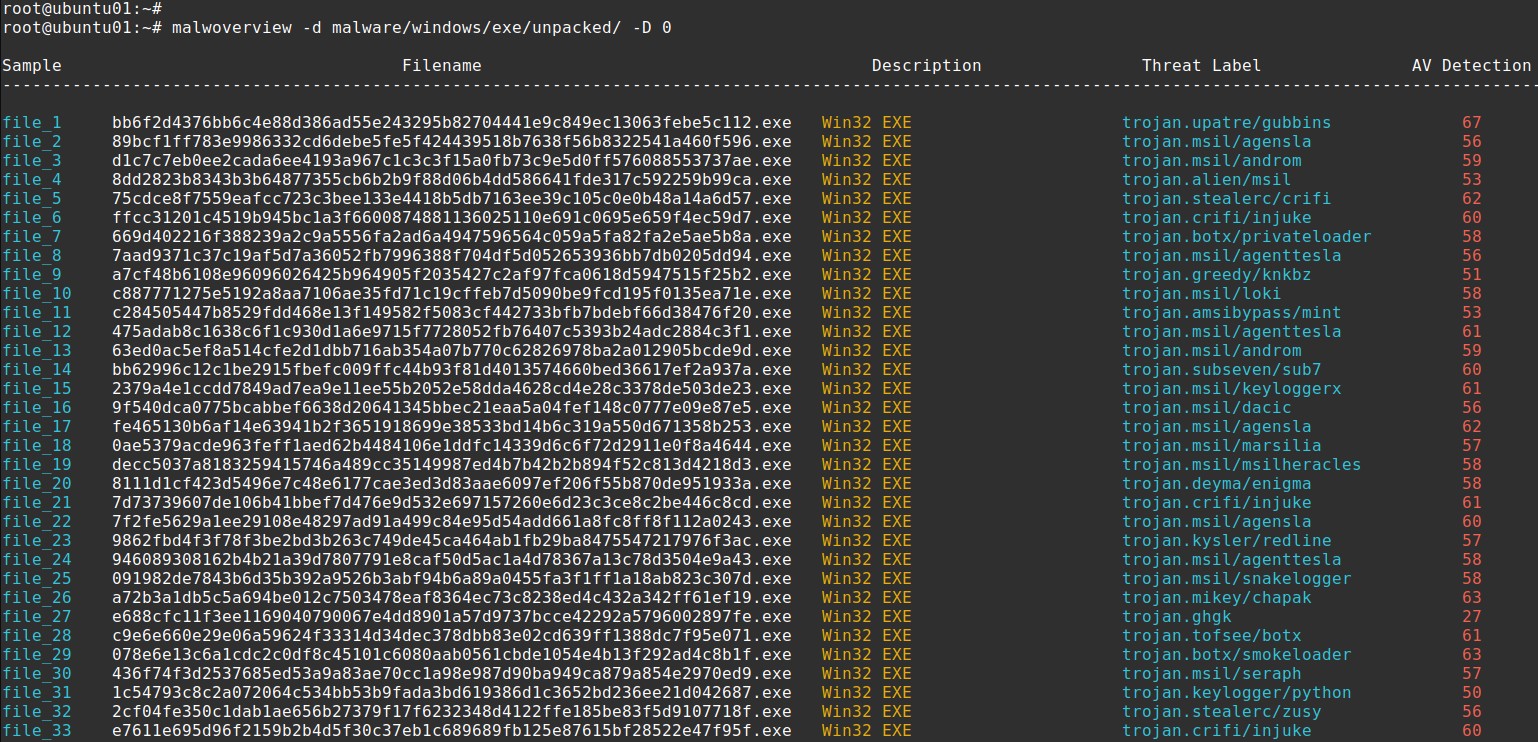 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.