
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
16 results
Umay preview

Umay

GitHubmucoze/umay

IoT Malware Similarity Analysis Platform
iot-securitymalware-analysisreverse-engineering+1
434 years ago
my-little-honeypot preview

my-little-honeypot

GitHubpandipanda69/my-little-honeypot

Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…

command-and-controliot-securitymalware-analysis+2
179 years ago
Barzakh preview

Barzakh

GitHubyasindce1998/barzakh

Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.

defensive-toolsembedded-systems-securityfirmware-analysis+6
1413 days ago
UEFI-Security-Research-Howyar-SysReturn-NetCopy preview

UEFI-Security-Research-Howyar-SysReturn-NetCopy

GitHubthemalwareguardian/uefi-security-research-howyar-sysreturn-netcopy

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
binary-analysisembedded-systems-securityexploitation+6
21 month ago
idahunt preview

idahunt

GitHubnccgroup/idahunt

idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
binary-analysisembedded-systems-securityfirmware-analysis+4
3943 years ago
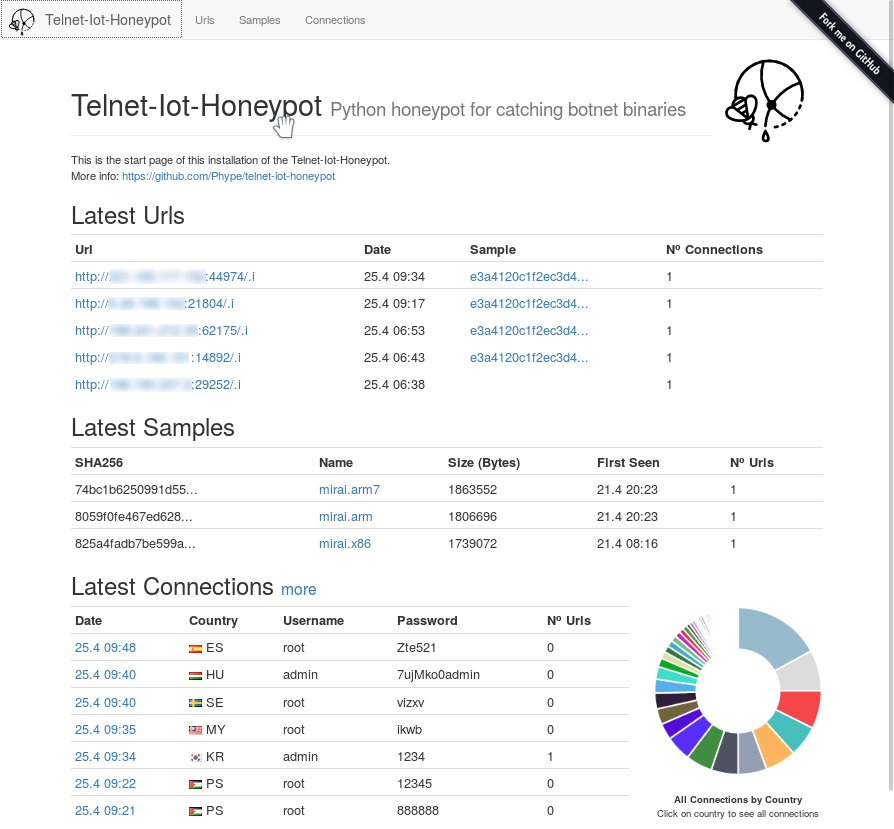
telnet-iot-honeypot preview

telnet-iot-honeypot

GitHubphype/telnet-iot-honeypot

Python telnet honeypot for catching botnet binaries
iot-securitymalware-analysisnetwork-security+1
3114 years ago
IoT-Implant-Toolkit preview

IoT-Implant-Toolkit

GitHubarthastang/iot-implant-toolkit

Toolkit for implant attack of IoT devices

binary-analysisembedded-systems-securityexploitation+8
1358 years ago
moria preview

moria

GitHubnmatt0/moria

IoT firmware identification and extraction

binary-analysisdigital-forensicsembedded-systems-security+7
4331 day ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
432 months ago
IoT-Home-Guard preview

IoT-Home-Guard

GitHubarthastang/iot-home-guard

A tool for malicious behavior detection in IoT devices
anomaly-detectionintrusion-detectioniot-security+2
777 years ago
DeadDialect preview

DeadDialect

GitHubengrbilal992/deaddialect

A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.
binary-analysiscryptographydefensive-tools+7
66 months ago
SecureTea-Project preview

SecureTea-Project

GitHubowasp/securetea-project

The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
defensive-toolsintrusion-detectioniot-security+4
3023 years ago
ThreatResearch preview

ThreatResearch

GitHubsecurityjoes/threatresearch

Python config extractors for malware families including PlugX, Remcos, templateX, and RedLine Stealer, supporting C2 configuration extraction for…
malware-analysisreverse-engineeringthreat-intelligence
603 years ago
p-invoke.net preview

p-invoke.net

GitHubricardojoserf/p-invoke.net

Curated collection of P/Invoke definitions from pinvoke.net with Microsoft documentation links, enabling quick Windows API prototyping for security…
malware-analysisreverse-engineeringutilities-frameworks
241 year ago
IcedID preview

IcedID

GitHubpr0xylife/icedid
malware-analysisreverse-engineeringthreat-intelligence
322 years ago
backdoor.mirai.helloworld preview

backdoor.mirai.helloworld

GitHubtpdlshdmlrkfmcla/backdoor.mirai.helloworld

backdoor.mirai.helloworld cve2018-20561, cve-2018-10562 해킹

command-and-controlexploitationiot-security+3
1 year ago