
Umay
 mucoze/umay
IoT Malware Similarity Analysis Platform
iot-securitymalware-analysisreverse-engineering+1
mucoze/umayIoT Malware Similarity Analysis Platform
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
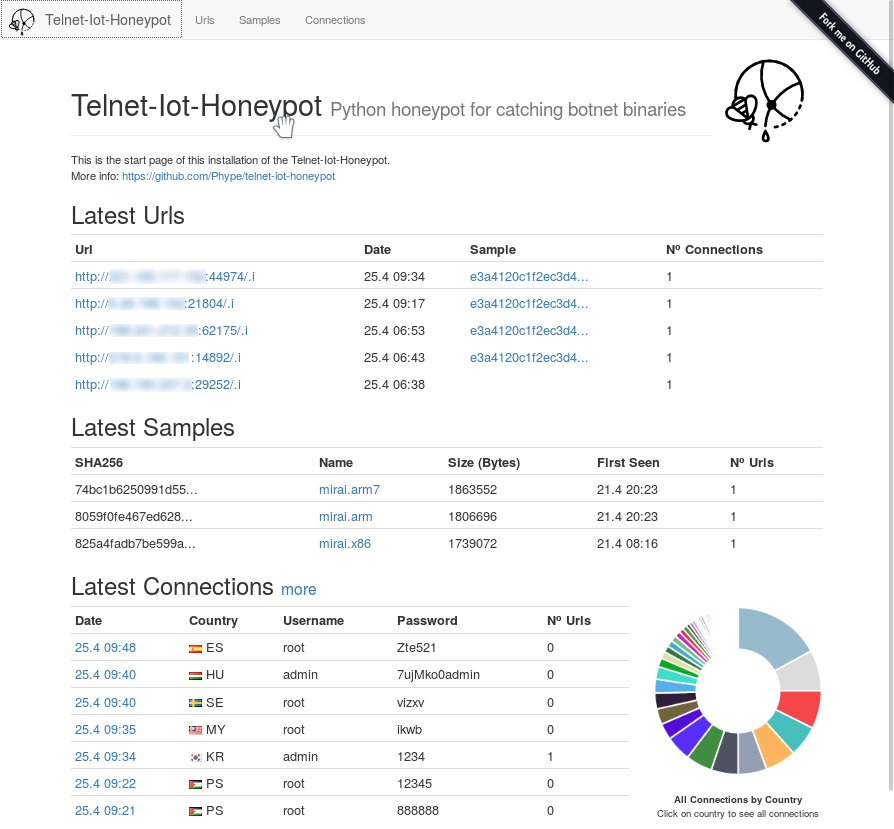 phype/telnet-iot-honeypot
Python telnet honeypot for catching botnet binaries
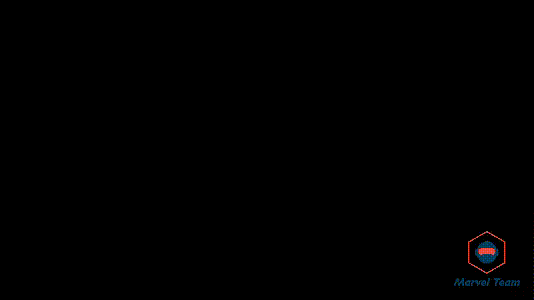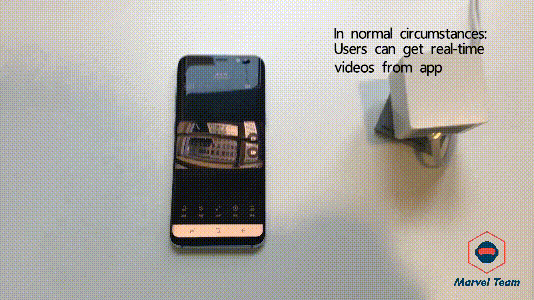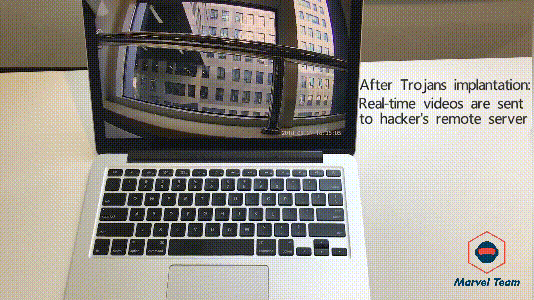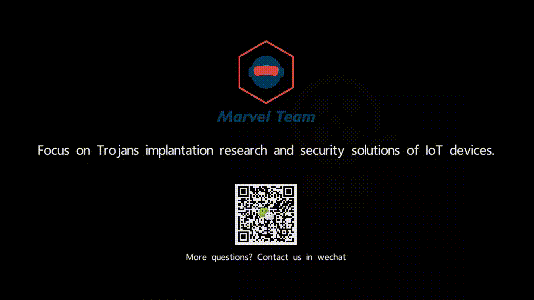 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 engrbilal992/deaddialect
A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.