
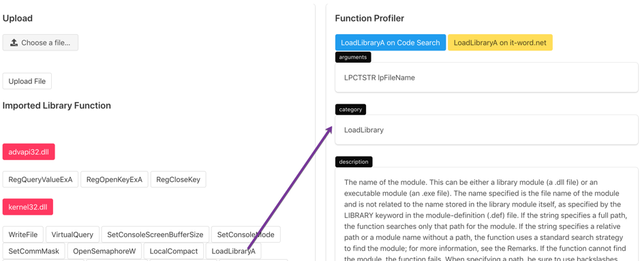
malwinx
 mohitdabas/malwinx
Just a normal flask web app to understand win32api with code snippets and references.
code-analysiseducationmalware-analysis
mohitdabas/malwinxJust a normal flask web app to understand win32api with code snippets and references.
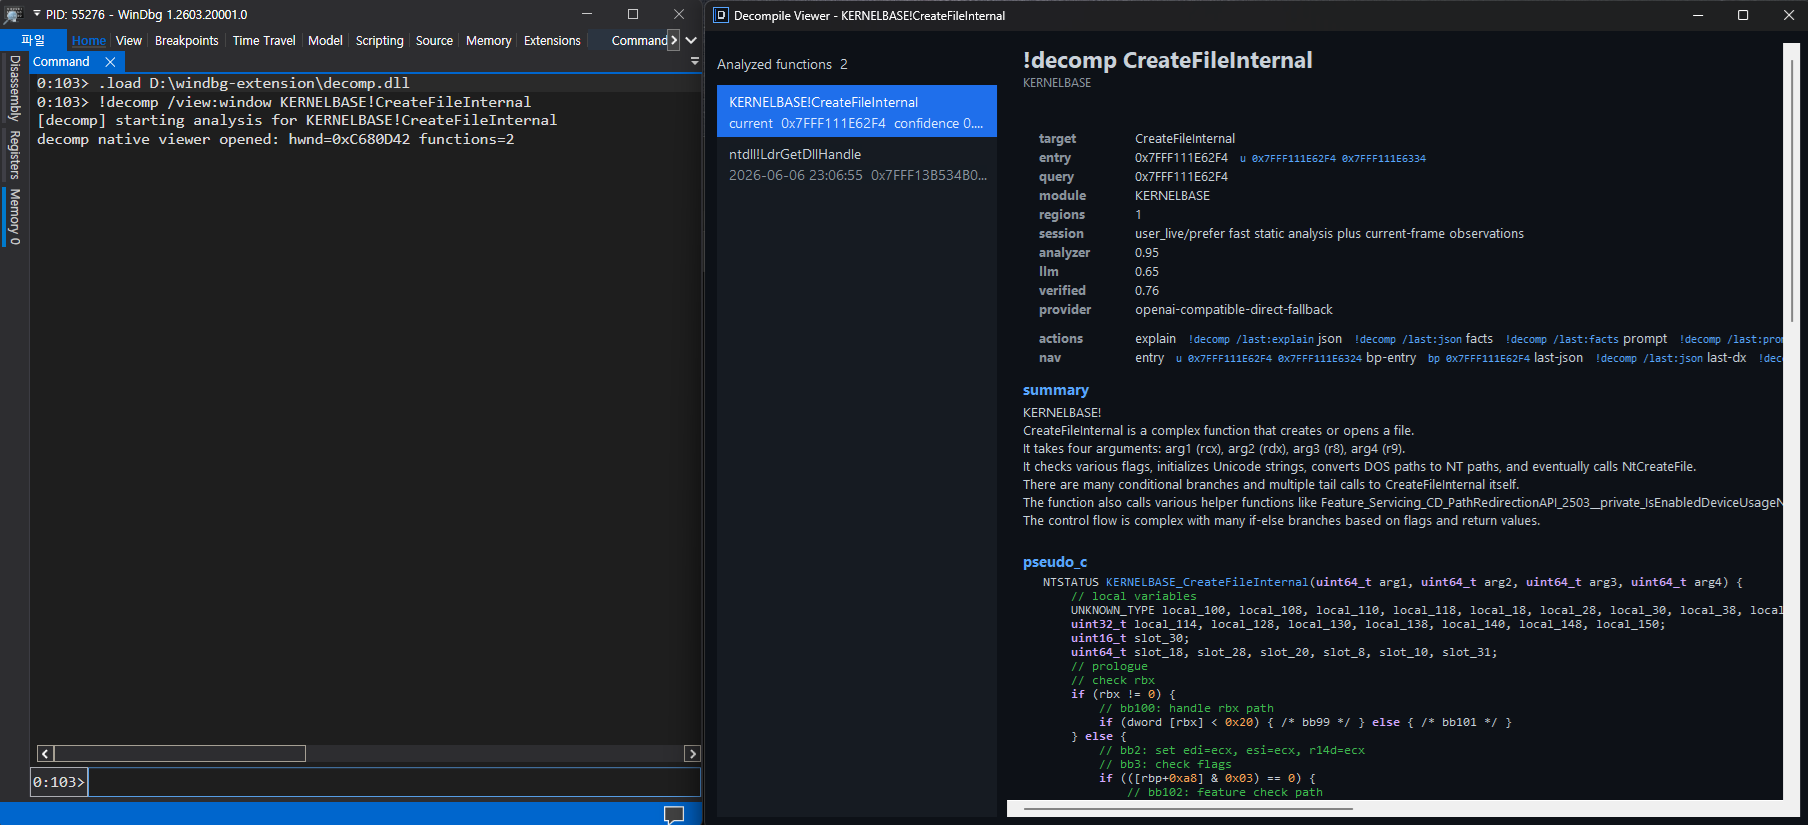 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
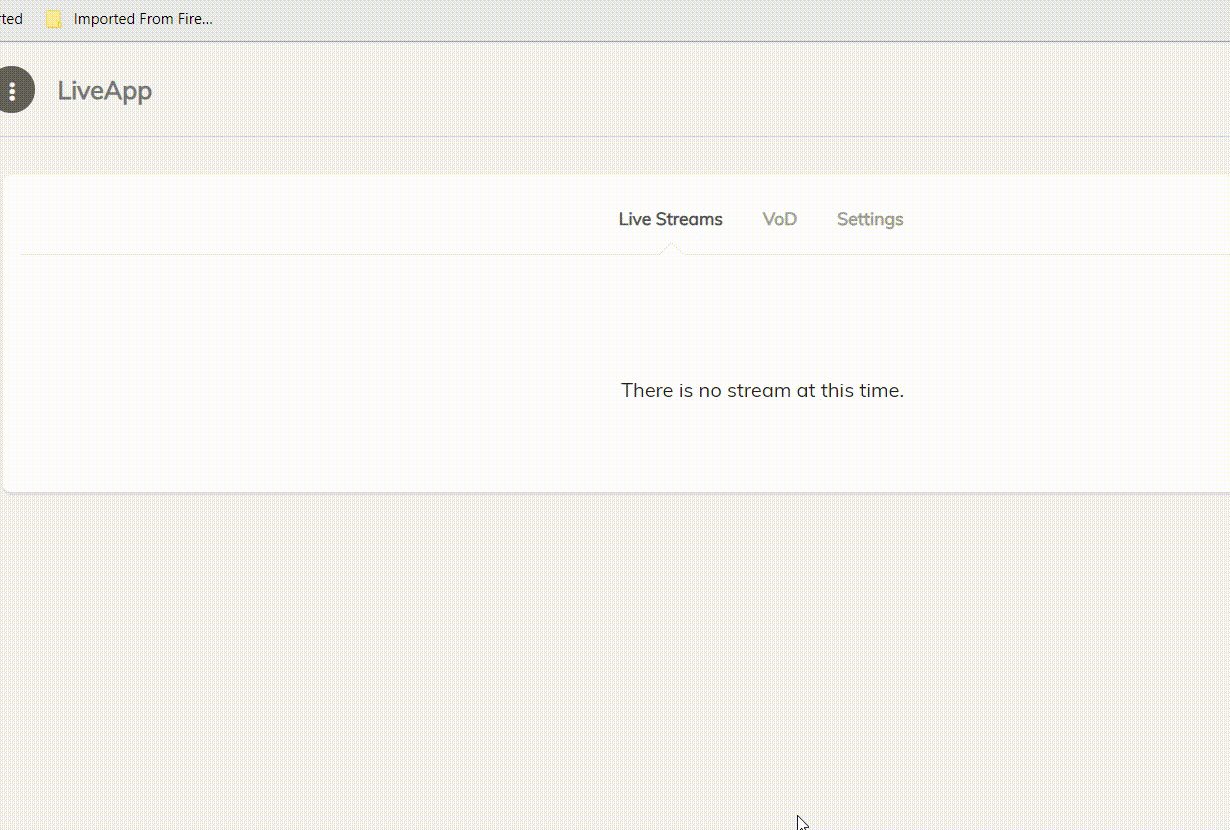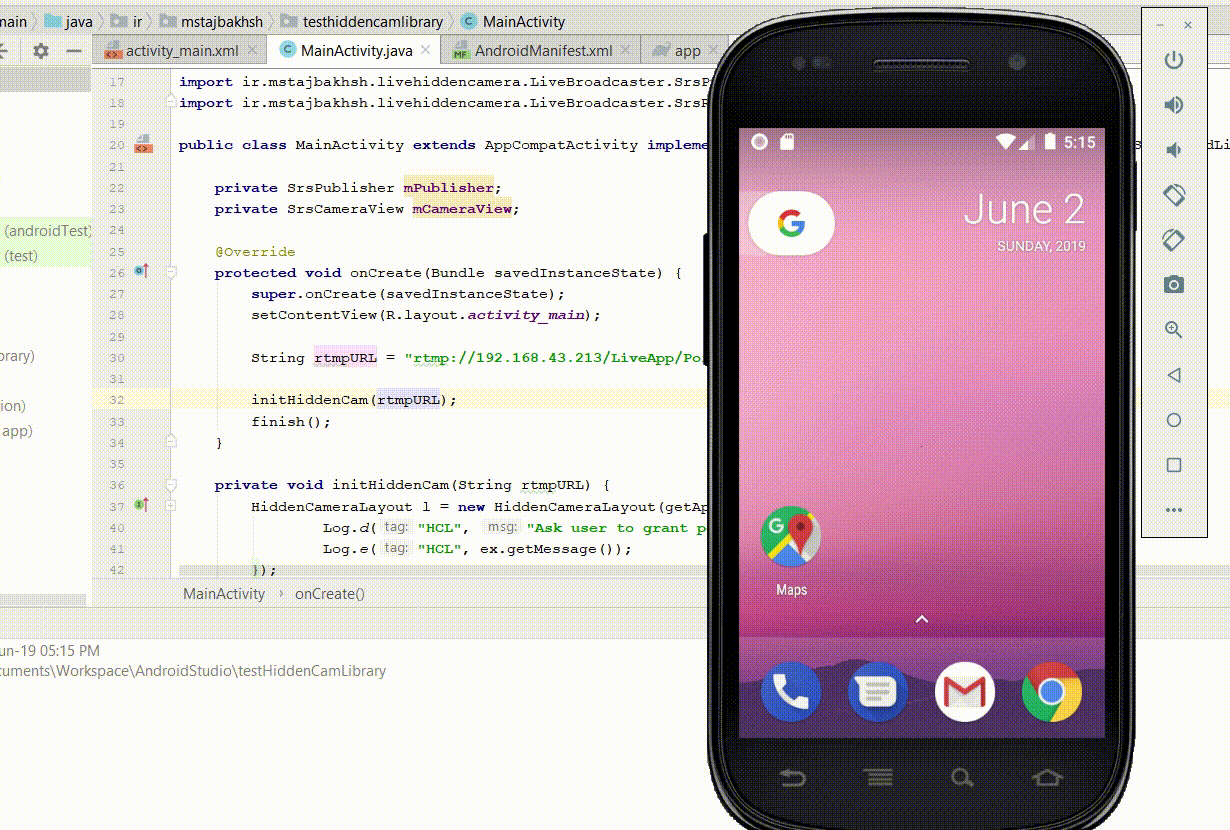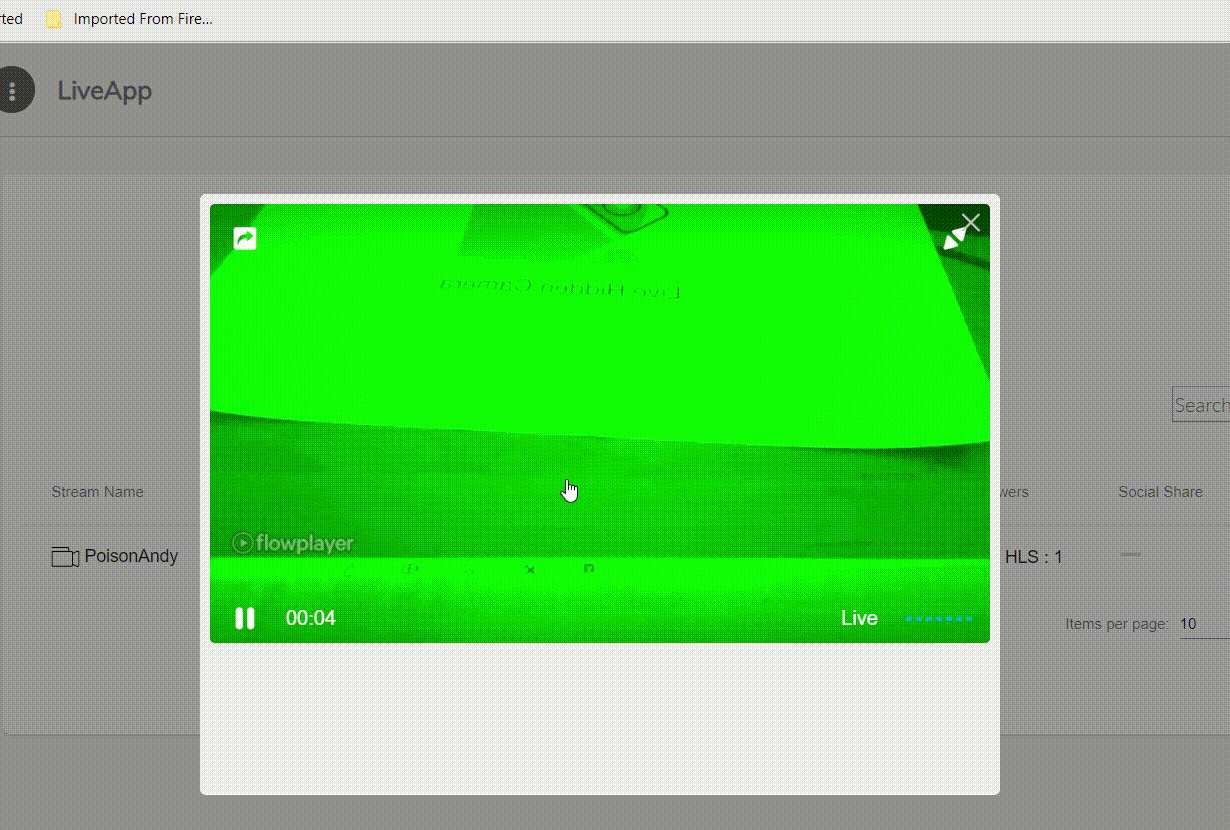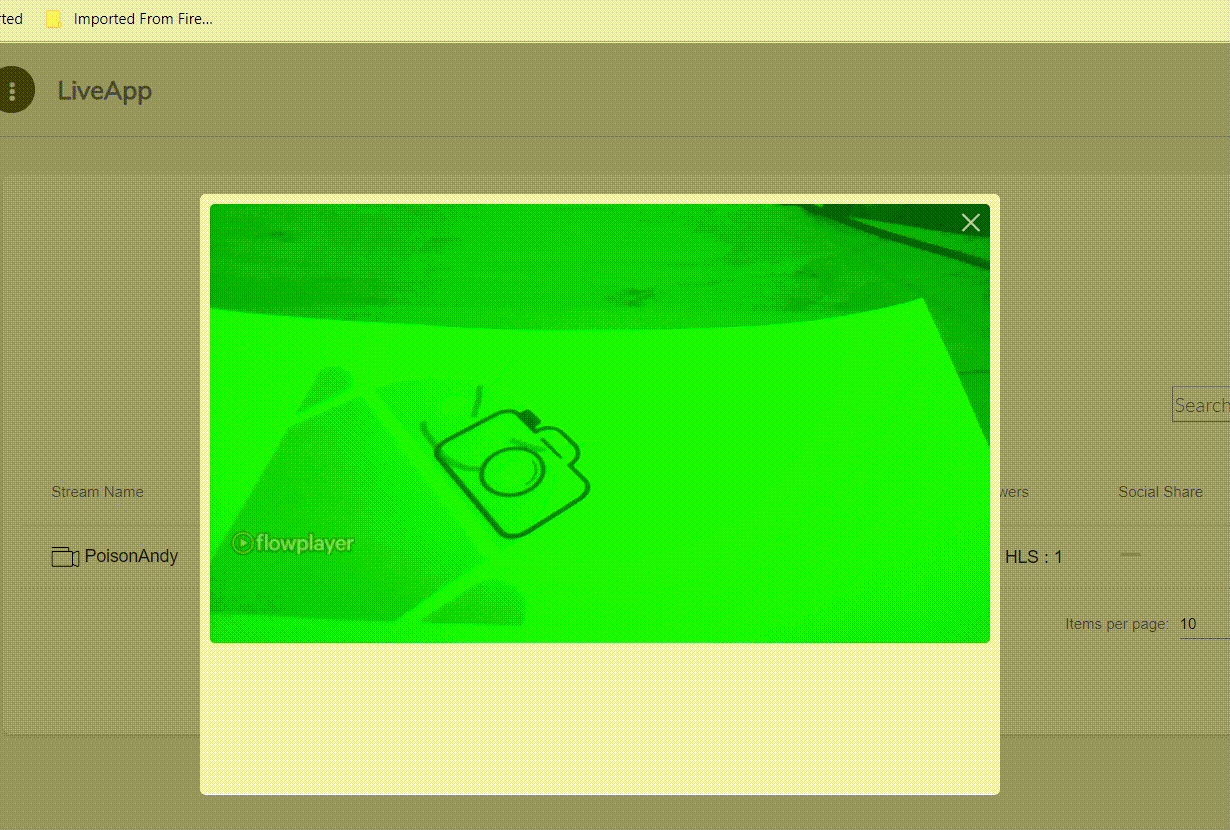 mirsamantajbakhsh/livehiddencamera
Live Hidden Camera is a library which record live video and audio from Android device without displaying a preview.
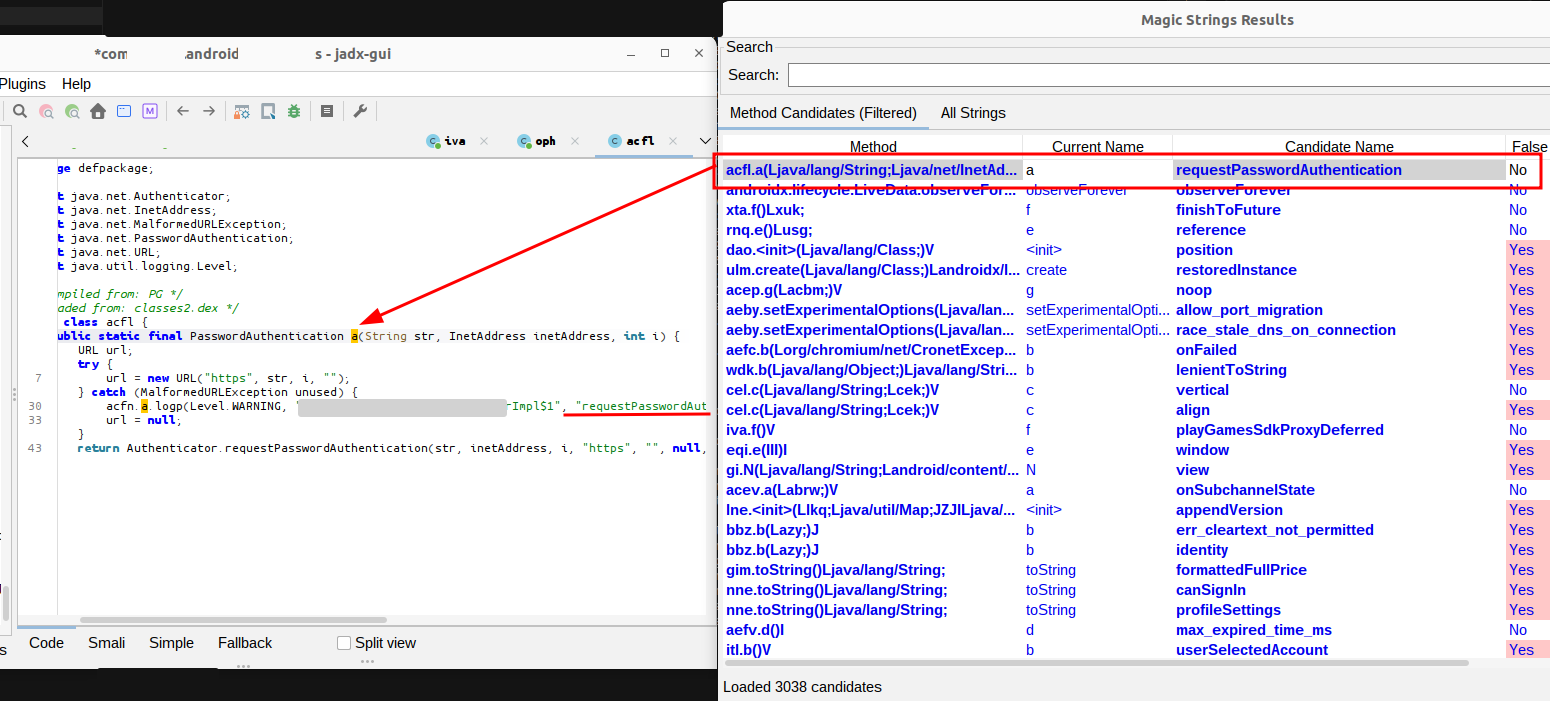 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
 sadopc/machscope
All-in-one macOS binary analysis: Mach-O parsing, ARM64 disassembly, code signatures, and debugging.
 thisislibra/m3
A simple and scalable Android bot emulation framework, as presented at Black Hat Europe 2021's Arsenal, as well as atHack 2021's Arsenal
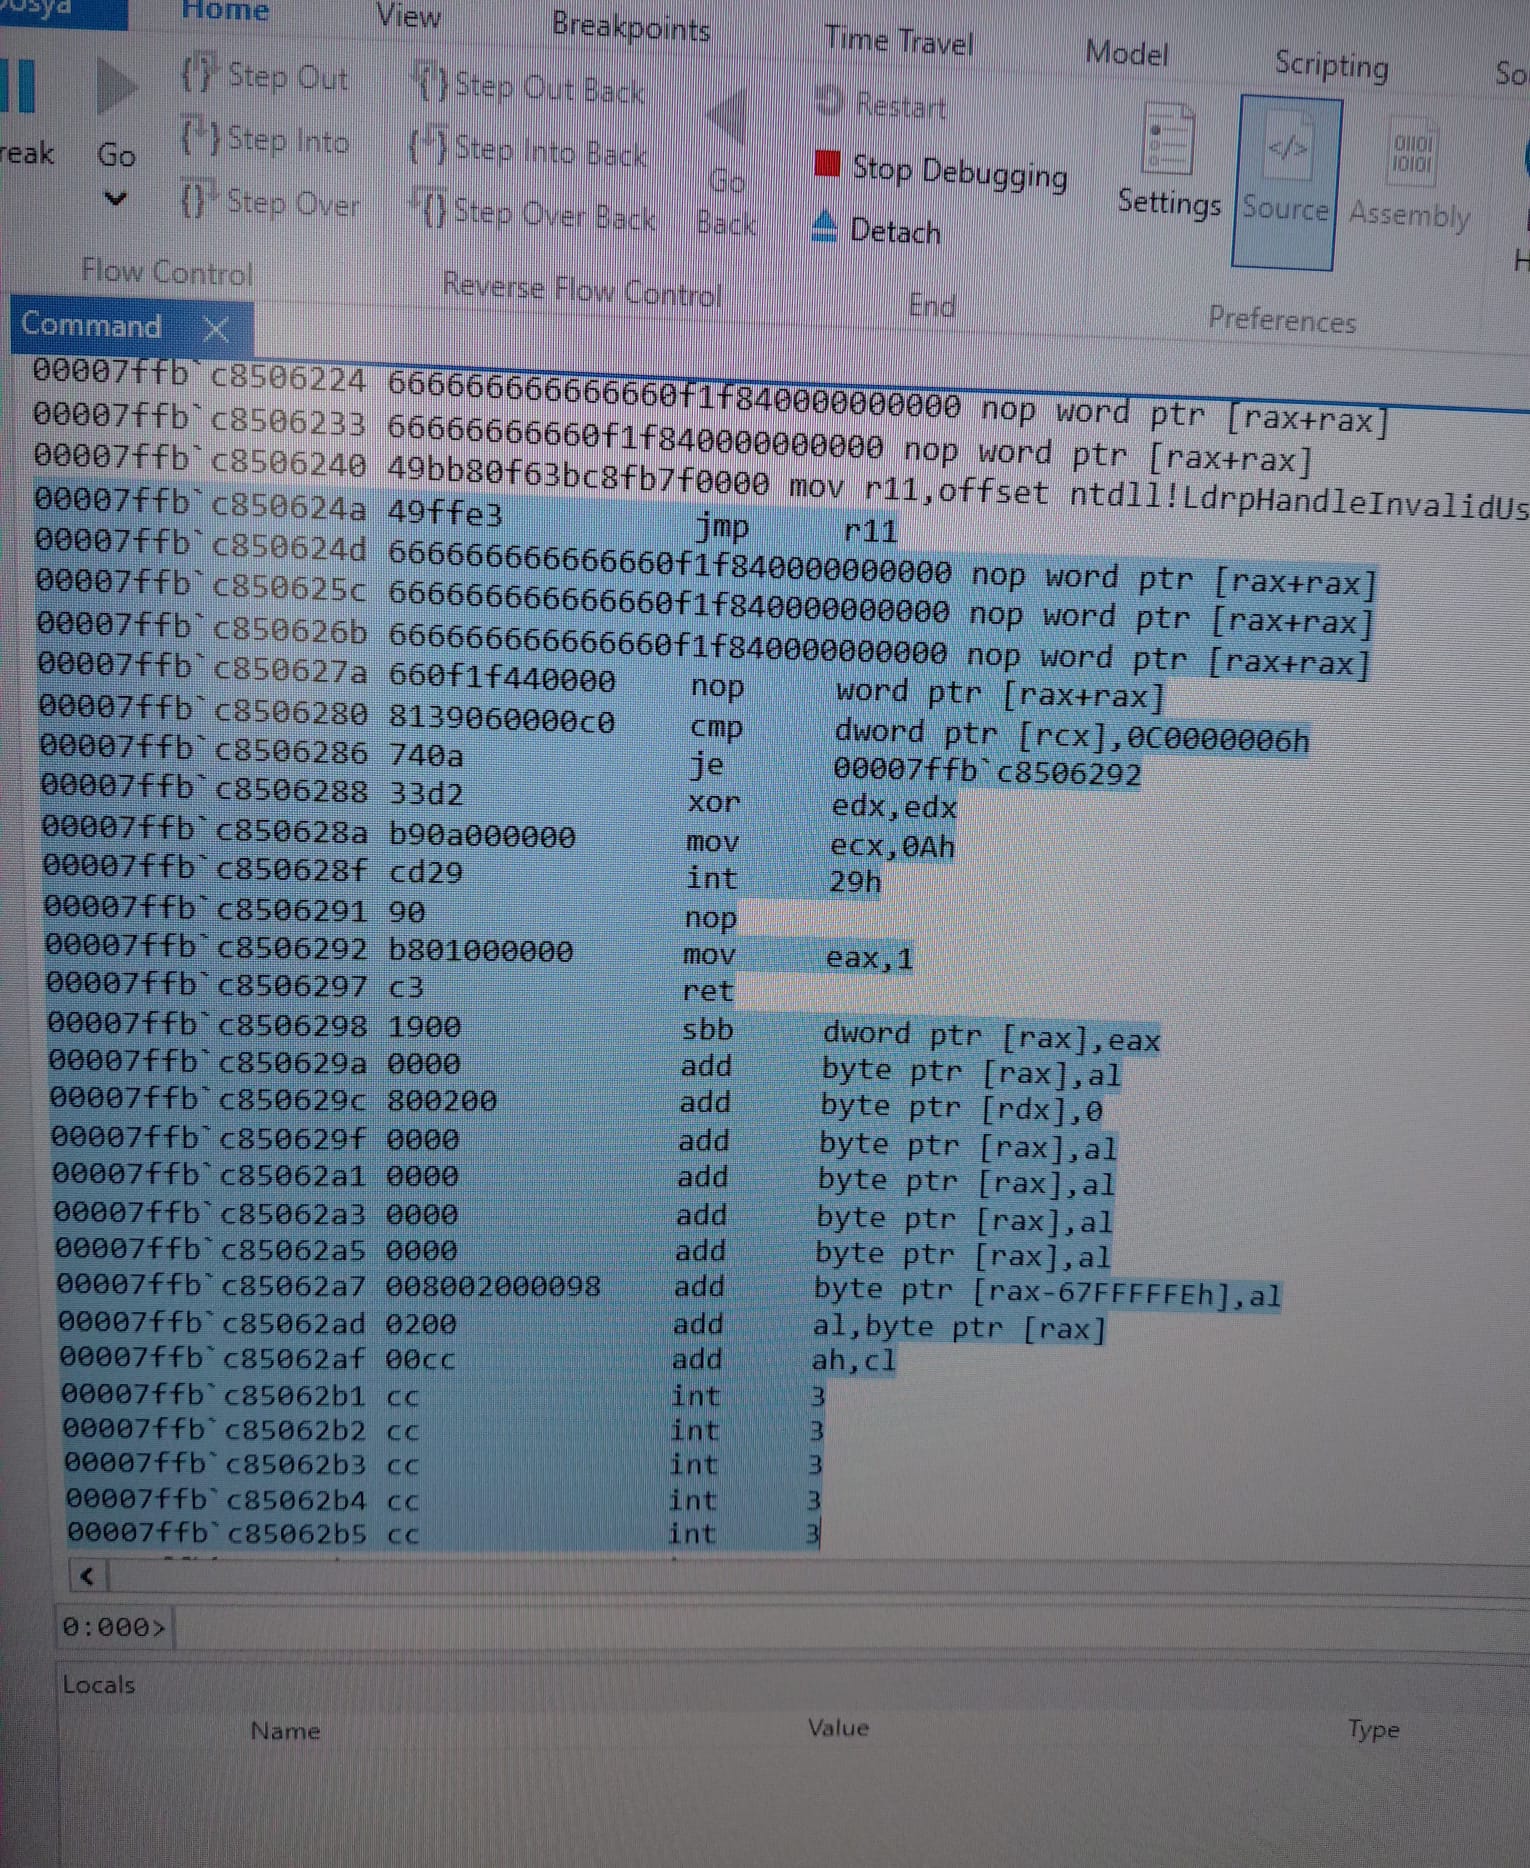 kaandemir993/advanced-loader-reverse-engineering
"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 gmh5225/eac
Compiles EAC and EOC anti-cheat SDKs, reversing research, and code resources to study how game anti-cheat systems integrate and operate.
 egorrsp/cve-2020-15368-asrdrv103-research
Reverse engineering research of ASRock AsrDrv103.sys (CVE-2020-15368), covering its driver interface, encrypted request protocol, and privileged…
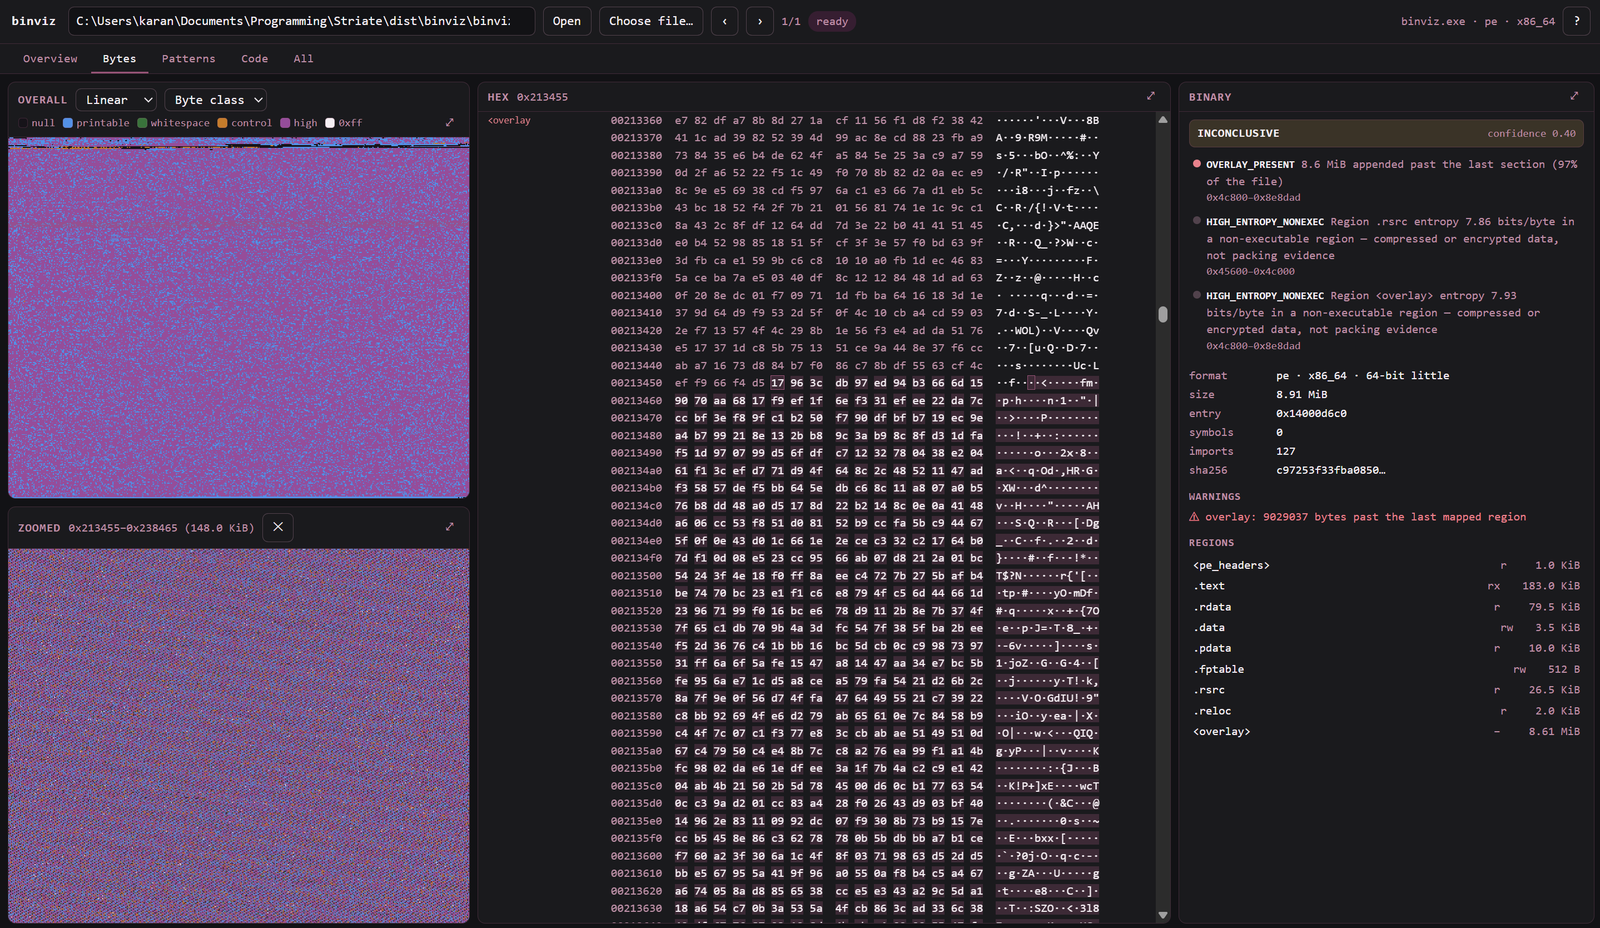 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 ffri/xprtestsuite
A collection of scripts and documents to help future XProtect Remediator (XPR) research
 demining/log4j-vulnerability
Educational analysis of the Log4Shell (CVE-2021-44228) vulnerability, detailing its exploitation in a cryptocurrency mining campaign with IoCs, MITRE…
 adityabhatt3010/cve-2025-8088-winrar-zero-day-path-traversal
An engaging walkthrough on uncovering, patching, and securing the WinRAR CVE-2025-8088 with a hands-on hacker’s twist.
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 j4ck3lsyn-gen2/reports
Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…
 blacksnufkin/blacksnufkin
Red team operator and malware developer specializing in evasion techniques, reverse engineering, and initial access operations. Active CVE researcher…