
jsunpack-n
 urule99/jsunpack-n
Automatically exported from code.google.com/p/jsunpack-n
dynamic-analysis-sandboxingmalware-analysisweb-security
urule99/jsunpack-nAutomatically exported from code.google.com/p/jsunpack-n
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 oalabs/frida-wshook
Script analysis tool based on Frida.re
 oalabs/frida-extract
Frida.re based RunPE (and MapViewOfSection) extraction tool
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
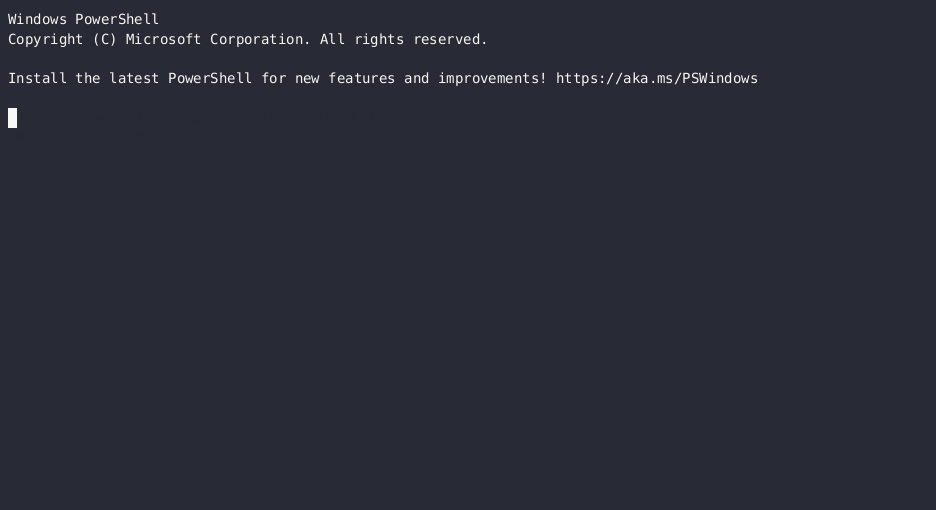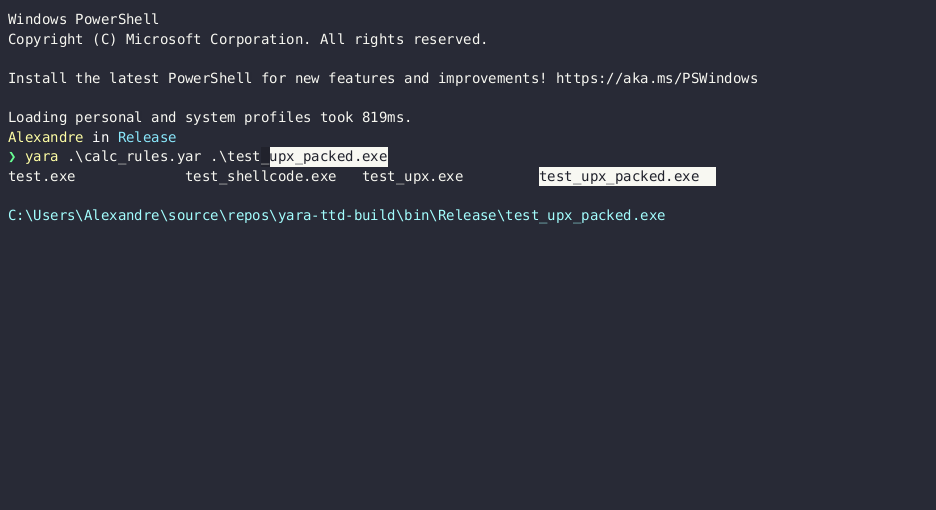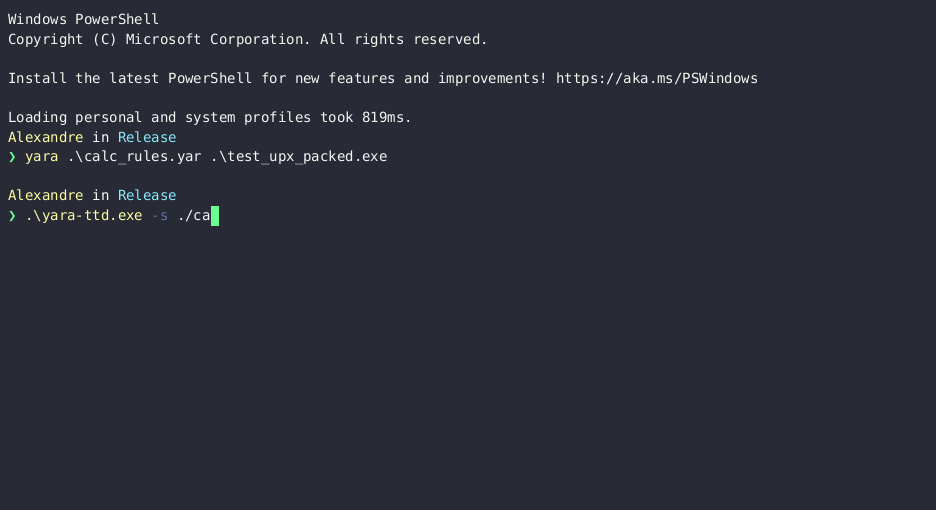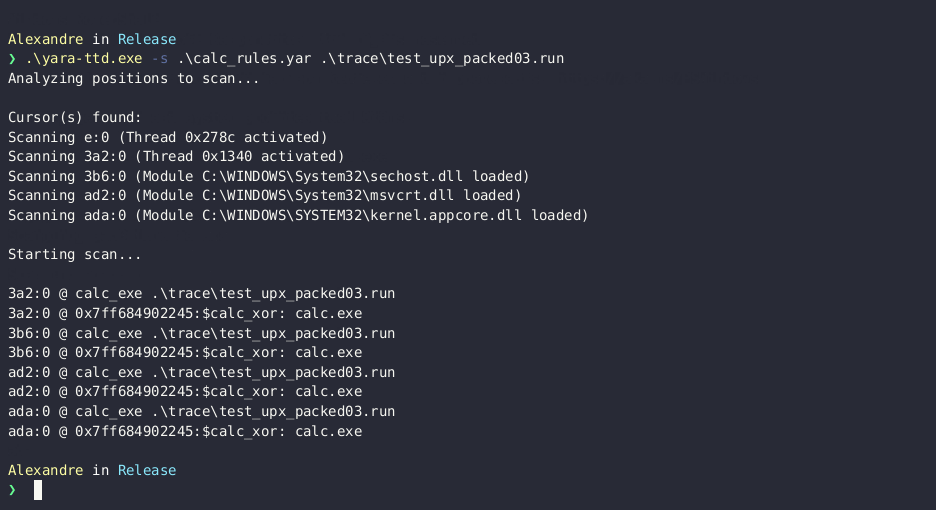 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
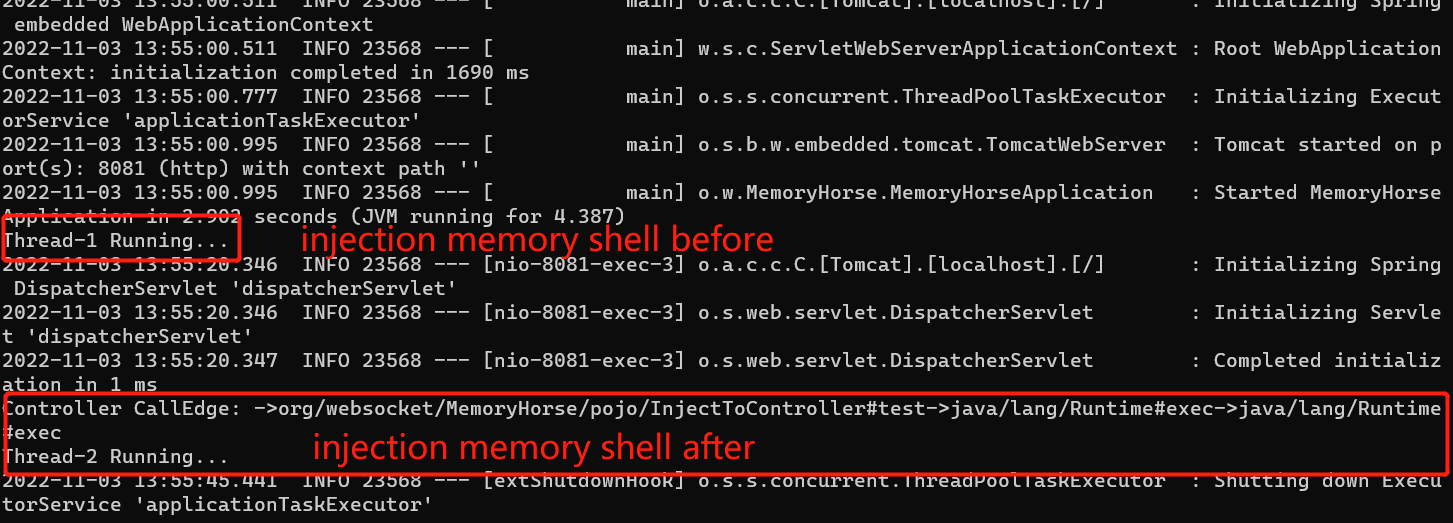 sf197/memoryshellhunter
Java Agent memory horse scanner combined with Call Graph modus
 capesandbox/cape-parsers
CAPE core and community parsers
 nexusfuzzy/raccoon_config
Scans a list of raccoon servers from Tria.ge and extracts the config
 jacobpimental/nanocore_extractor
Extracts nanocore sample from compile AutoIT script
 helgesverre/livewire-honeypot
High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…
 bcoles/rootkit-signal-hunter
Detect Linux rootkits which use signals to elevate process privileges.
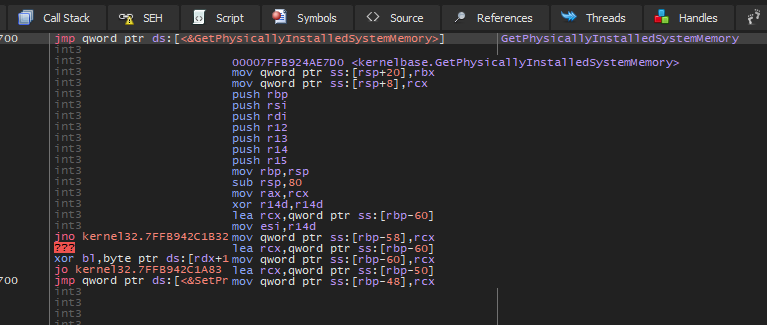 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 indominusrexes/cve-2025-4322-exploit
Critical CVE-2025-4322 exploit for Firefox on Windows enabling sandbox escape and arbitrary code execution. Includes download link and technical…
 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.