
botnet-hackpack
 treehacks/botnet-hackpack
Build a basic Command & Control botnet in C
command-and-controleducationmalware-analysis+3
4067 years ago
treehacks/botnet-hackpackBuild a basic Command & Control botnet in C
 silascutler/malpipe
Malware/IOC ingestion and processing engine
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
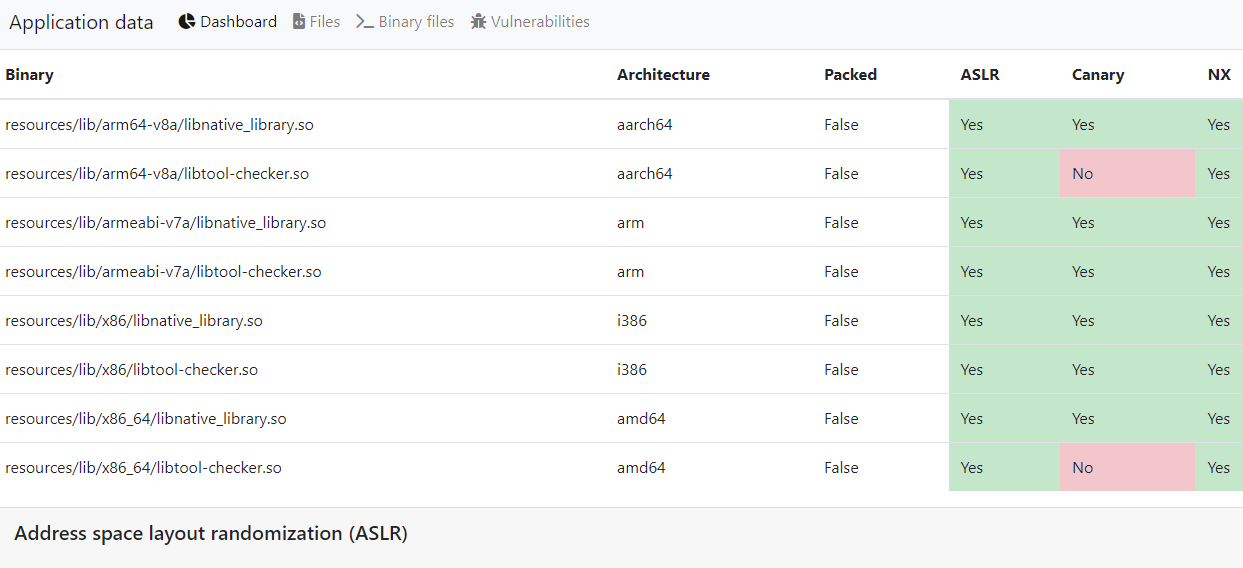 stefan2200/aparoid
Static and dynamic Android application security analysis
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 jacobsoo/amtracker
Android Malware Tracker
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 mohammadnassiri/yaasa
Yet Another APK Static Analyzer
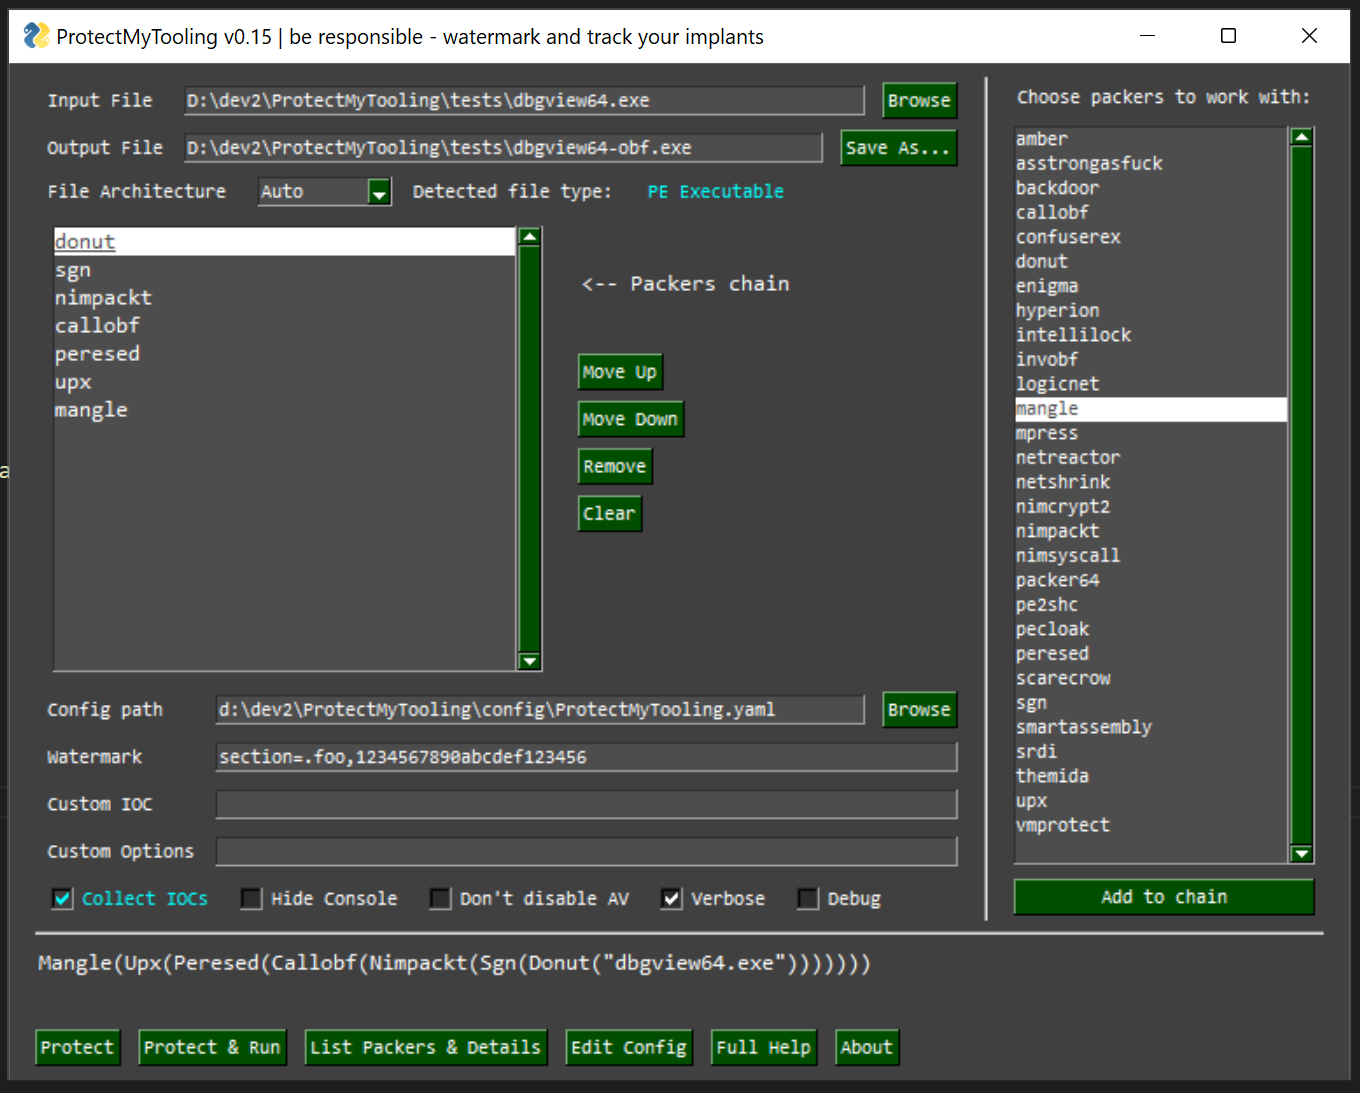 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 omriher/captipper
Malicious HTTP traffic explorer
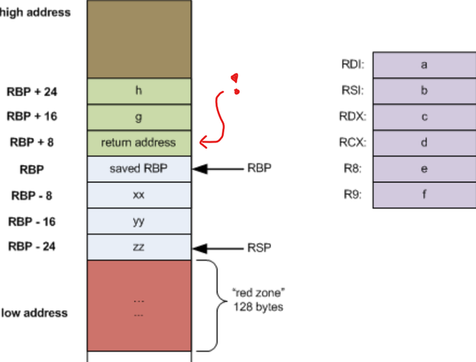 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
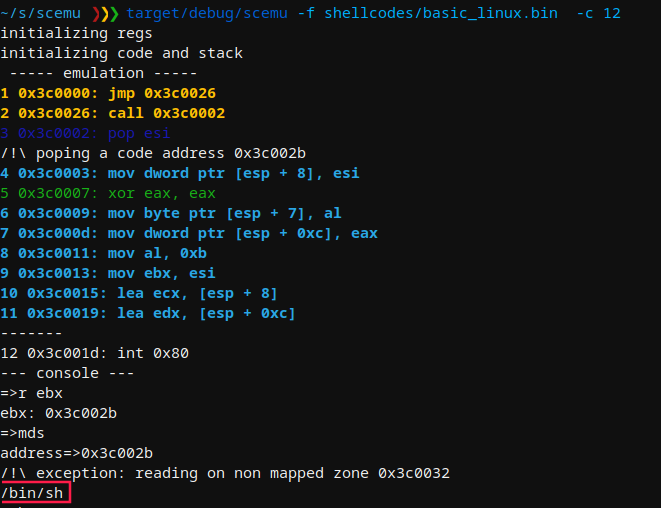 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
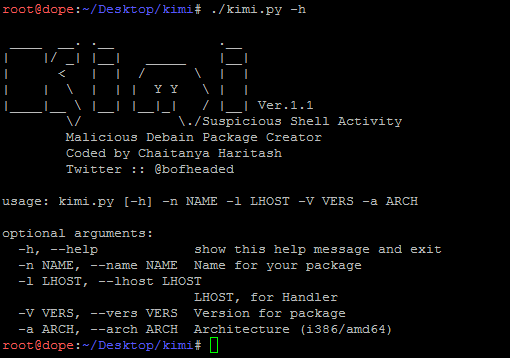 chaitanyaharitash/kimi
Script to generate malicious debian packages (debain trojans).
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research