CVE-2025-55891
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
binary-exploitationexploitationfuzzing+3
terribledactyl/cve-2025-55891Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 de4dot/de4dot
.NET deobfuscator and unpacker.
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
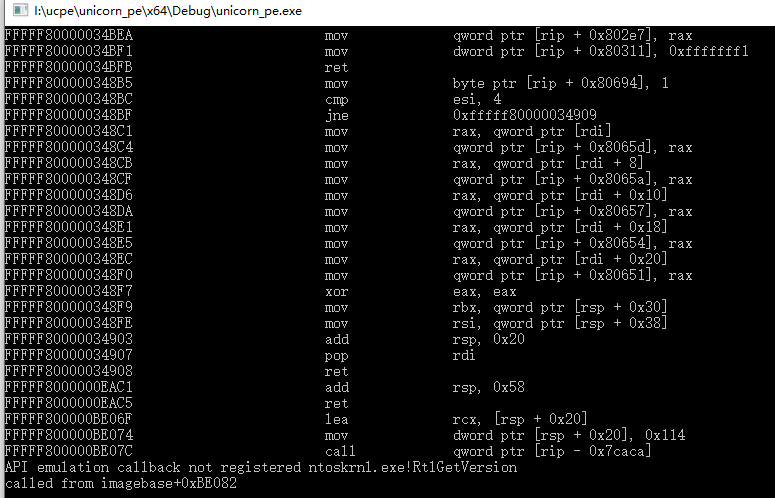 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…

 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).