
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
66 results
VMUnprotect.Dumper preview

VMUnprotect.Dumper

GitHubvoid-stack/vmunprotect.dumper

VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
binary-analysisdynamic-code-analysismalware-analysis+1
461
4 years ago
STrace preview

STrace

GitHubmandiant/strace

A DTrace on Windows Reimplementation

debuggersdynamic-code-analysisincident-response+2
3794 months ago
Reversecore_MCP preview

Reversecore_MCP

GitHubsjkim1127/reversecore_mcp

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…

binary-analysisdigital-forensicsdynamic-analysis-sandboxing+7
2051 day ago
pyREtic preview

pyREtic

GitHubmynameismeerkat/pyretic

pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering

binary-analysiscode-analysisdebuggers+5
2683 years ago
Brovan preview

Brovan

GitHubadvdebug/brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

binary-analysisdebuggersdynamic-analysis-sandboxing+3
1661 day ago
Flerken preview

Flerken

GitHubwe5ter/flerken

A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
code-analysisdefensive-toolsdynamic-code-analysis+3
1637 years ago
FileInsight-plugins preview

FileInsight-plugins

GitHubnmantani/fileinsight-plugins

FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
binary-analysiscode-analysiscryptography+7
1641 year ago
awesome-reverse-engineering-and-malware-analysis preview

awesome-reverse-engineering-and-malware-analysis

GitHubzx41r/awesome-reverse-engineering-and-malware-analysis

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
binary-analysisbinary-exploitationctf+8
911 day ago
ioc2rpz preview

ioc2rpz

GitHubhomas/ioc2rpz

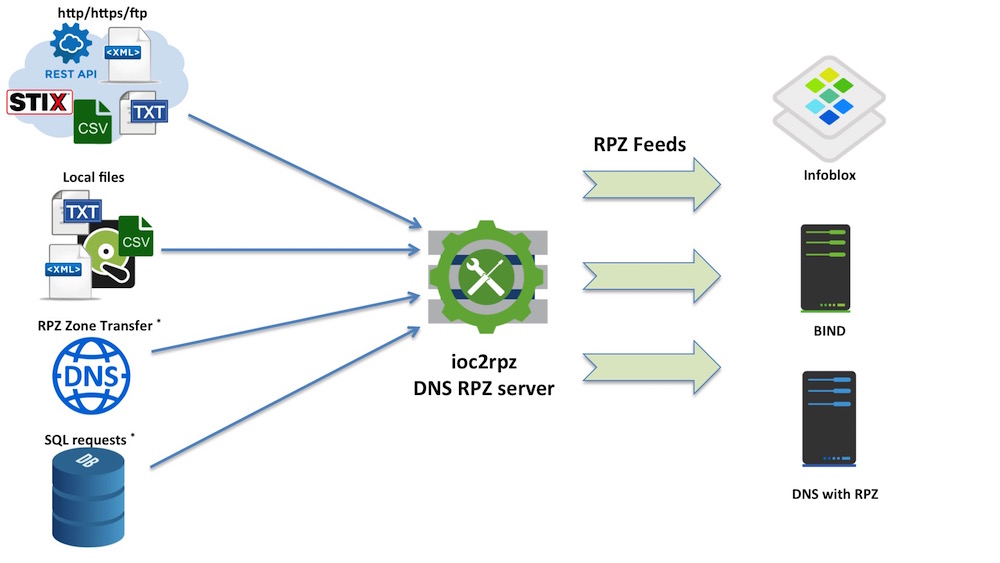
ioc2rpz is a place where threat intelligence meets DNS.
defensive-toolsdns-analysisdns-fuzzing+6
1162 months ago
NtDetours preview

NtDetours

GitHubrbmm/ntdetours

Detours implementation (x64/x86) which used only ntdll import
binary-analysiscode-analysisdebuggers+3
912 months ago
vaas preview

vaas

GitHubgdatasoftwareag/vaas

Verdict-as-a-Service SDKs: Analyze files for malicious content

api-securitycloud-securitymalware-analysis+1
383 months ago
spectrIDA-Reverse_Engineering_Stack preview

spectrIDA-Reverse_Engineering_Stack

GitHubggfuchsi-oss/spectrida-reverse_engineering_stack

Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…

ai-assisted-reversingbinary-analysisctf+8
612 months ago
flowinspect preview

flowinspect

GitHub7h3ram/flowinspect

A Network Inspection Tool

forensicsfuzzingintrusion-detection+5
828 years ago
fnprint preview

fnprint

GitHub1rhino2/fnprint

match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
binary-analysisdynamic-code-analysisfirmware-analysis+3
539 days ago
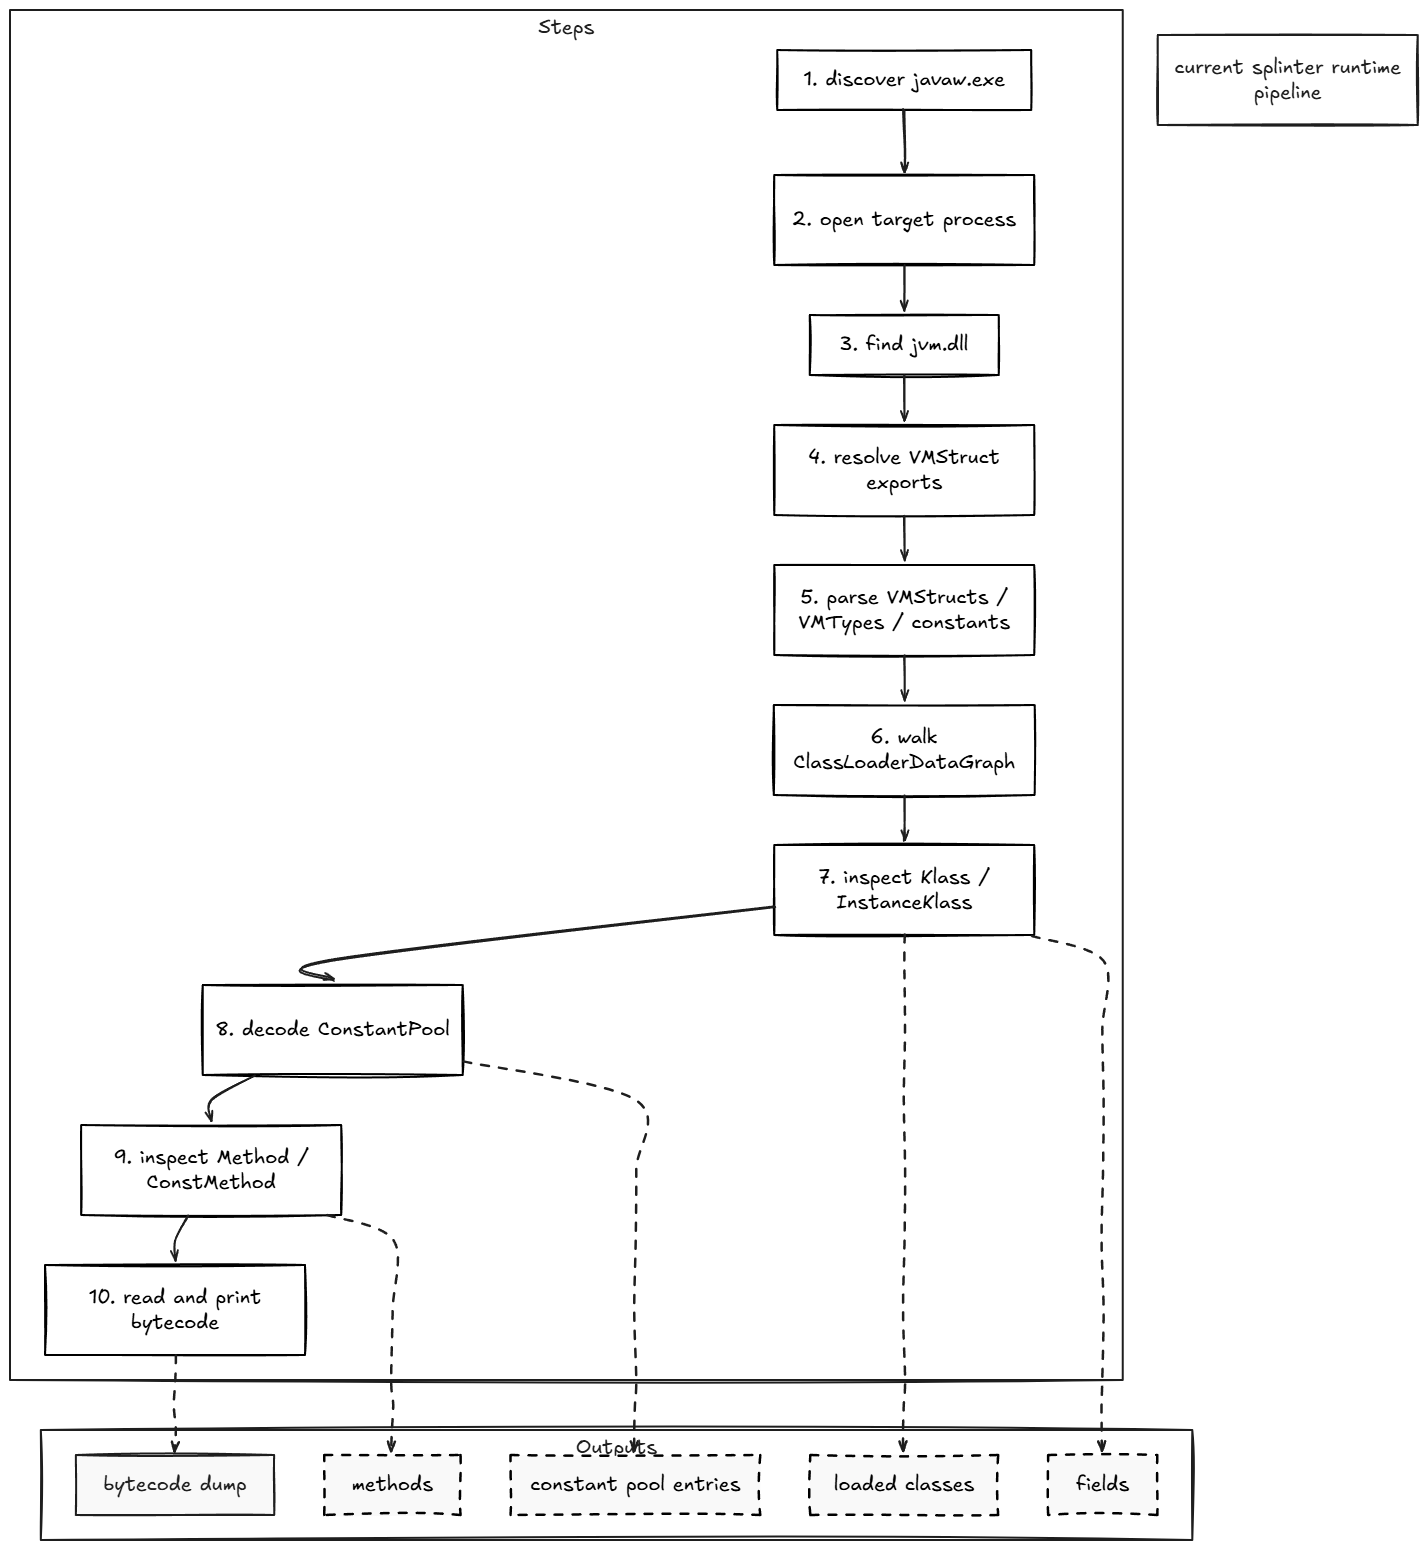
splinter preview

splinter

GitHubawrped/splinter

Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
binary-analysisdebuggersdynamic-analysis-sandboxing+4
911 month ago
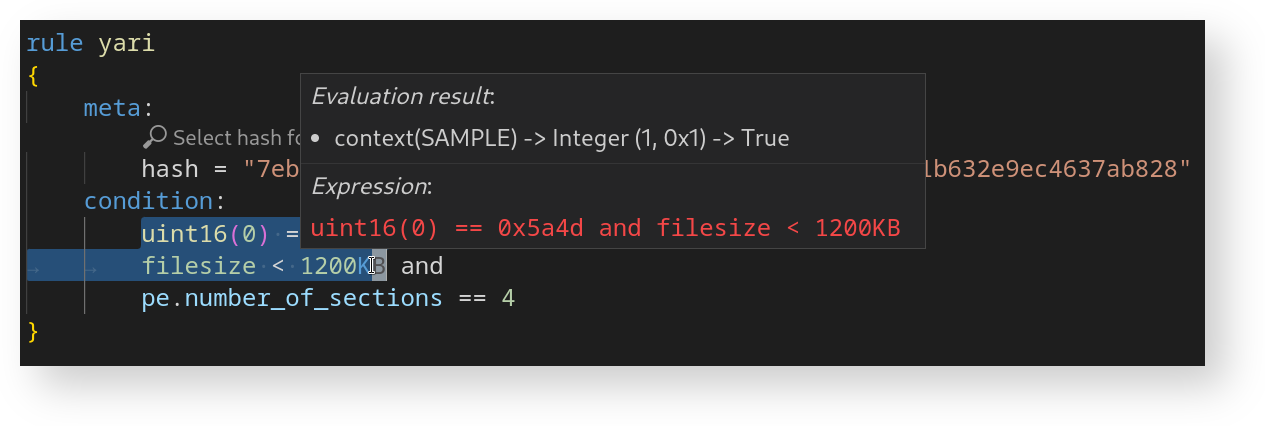
yari preview

yari

GitHubavast/yari

YARI is an interactive debugger for YARA Language.

binary-analysiscode-analysisdebuggers+2
901 year ago
maps_scanner preview

maps_scanner

GitHubhackinglz/maps_scanner

MAPS cloud scanner and response parser for Microsoft Defender research.
api-security-testingdynamic-analysis-sandboxingfuzzing+6
957 months ago
filterforge preview

filterforge

GitHubcloudflare/filterforge

Tool for solving BPF filters and crafting packets based on these.

binary-analysisforensicsfuzzing+5
646 months ago
Previous1234Next