
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
36 results
m3 preview

m3

GitHubthisislibra/m3

A simple and scalable Android bot emulation framework, as presented at Black Hat Europe 2021's Arsenal, as well as atHack 2021's Arsenal
android-securityeducationmalware-analysis+1
294 years ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications

api-security-testingbinary-analysisdebuggers+4
203 months ago
MalConfig preview

MalConfig

GitHubjacobsoo/malconfig

This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
android-securitycommand-and-controlinformation-gathering+3
77 years ago
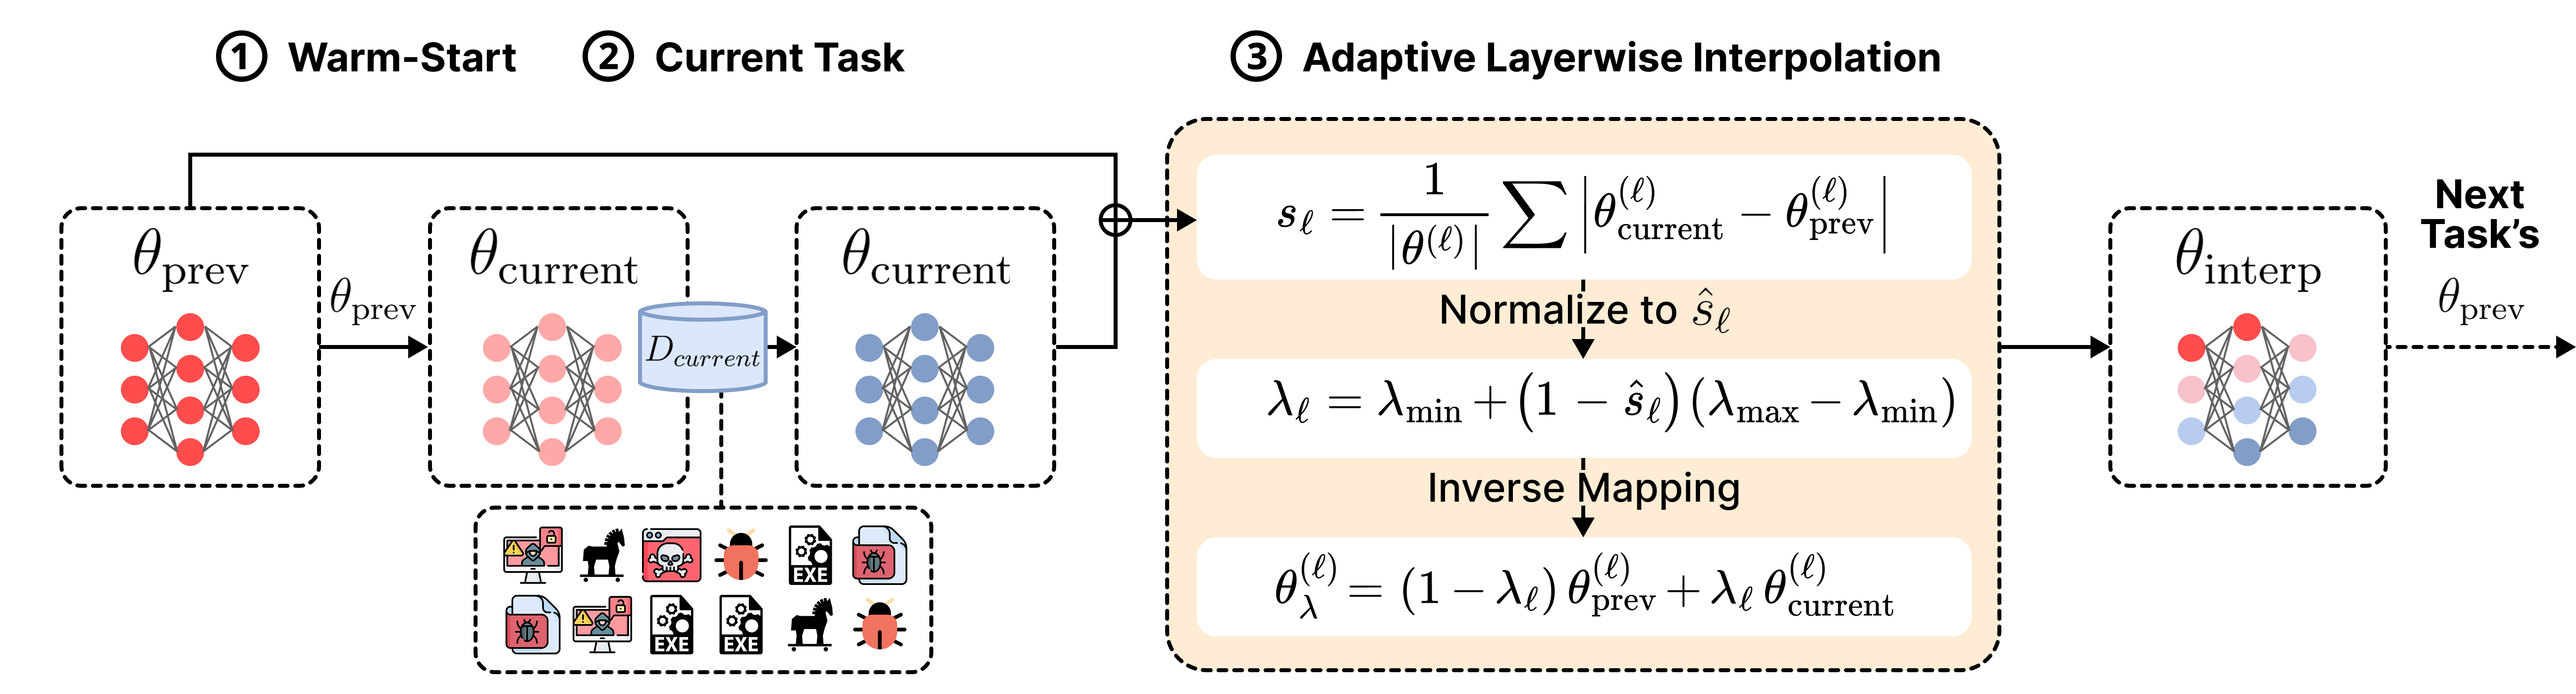
FreeMOCA preview

FreeMOCA

GitHubiqsec-lab/freemoca

Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
android-securityeducationmachine-learning+3
14 days ago
BIDO preview

BIDO

GitHubwhatishope/bido

Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
android-securityeducationmachine-learning+3
28 months ago
CrowdFMS preview
Archived

CrowdFMS

GitHubcrowdstrike/crowdfms

CrowdStrike Feed Management System. CrowdFMS is a framework for automating collection and processing of samples from VirusTotal, by leveraging the…

api-securitydynamic-analysis-sandboxingmalware-analysis+1
1337 years ago
viper preview
Archived

viper

GitHubviper-framework/viper

Binary analysis and management framework

binary-analysisexploit-frameworksforensics+3
1.6k3 years ago
Androl4b preview

Androl4b

GitHubsh4hin/androl4b

A Virtual Machine For Assessing Android applications, Reverse Engineering and Malware Analysis

android-securityeducationlabs-practice+4
1.2k6 years ago
aparoid preview

aparoid

GitHubstefan2200/aparoid

Static and dynamic Android application security analysis

android-securitydynamic-analysis-sandboxingmalware-analysis+5
782 years ago
amtracker preview

amtracker

GitHubjacobsoo/amtracker

Android Malware Tracker
android-securitycommand-and-controlinformation-gathering+3
292 years ago
MalEval preview

MalEval

GitHubzhengxr930/maleval

Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
ai-securityandroid-securitycode-analysis+5
52 months ago
YAASA preview

YAASA

GitHubmohammadnassiri/yaasa

Yet Another APK Static Analyzer
android-securitymalware-analysisstatic-analysis+1
18 years ago
ProtectMyTooling preview

ProtectMyTooling

GitHubmgeeky/protectmytooling

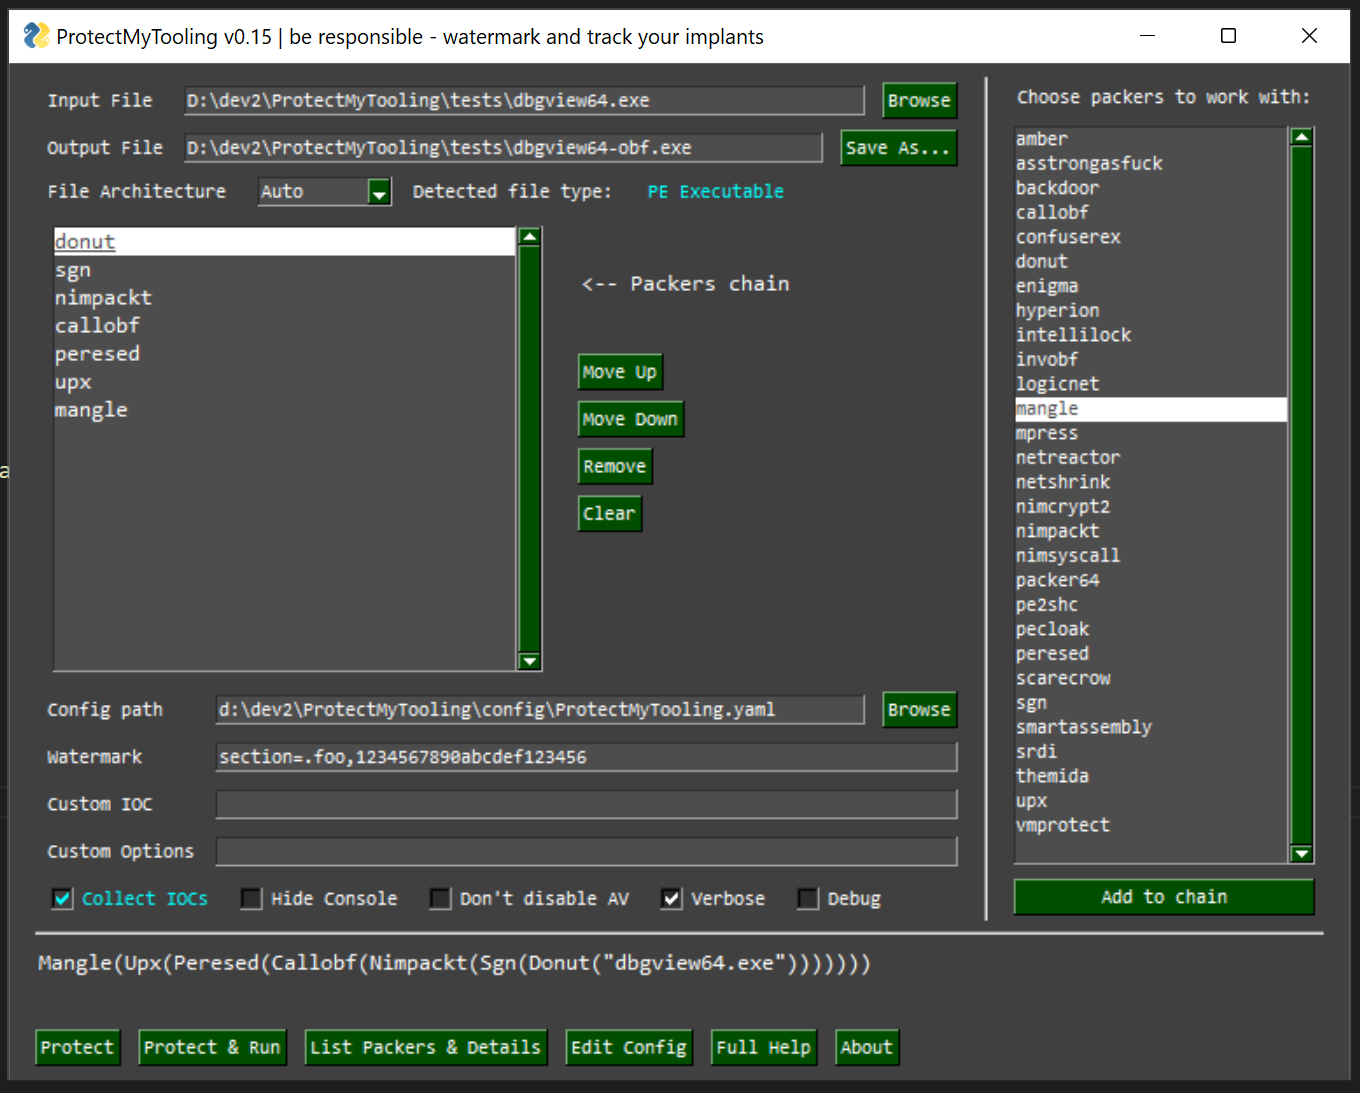
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
binary-analysisexploit-frameworksioc-management+5
1.1k11 months ago
CapTipper preview

CapTipper

GitHubomriher/captipper

Malicious HTTP traffic explorer
digital-forensicsexploit-frameworksforensics+5
7246 years ago
BDFProxy preview

BDFProxy

GitHubsecretsquirrel/bdfproxy

Patch Binaries via MITM: BackdoorFactory + mitmProxy.

binary-exploitationcommand-and-controlexploit-frameworks+8
1.0k5 years ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
3161 day ago
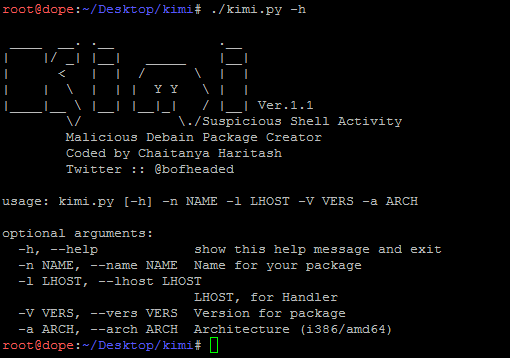
kimi preview

kimi

GitHubchaitanyaharitash/kimi

Script to generate malicious debian packages (debain trojans).
command-and-controlexploit-frameworksmalware-analysis+5
1247 years ago
CVE-2026-31431-Copy-Fail preview

CVE-2026-31431-Copy-Fail

GitHubrecofu/cve-2026-31431-copy-fail

Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…

container-escapeexploitationexploit-frameworks+3
5 months ago
Previous12Next