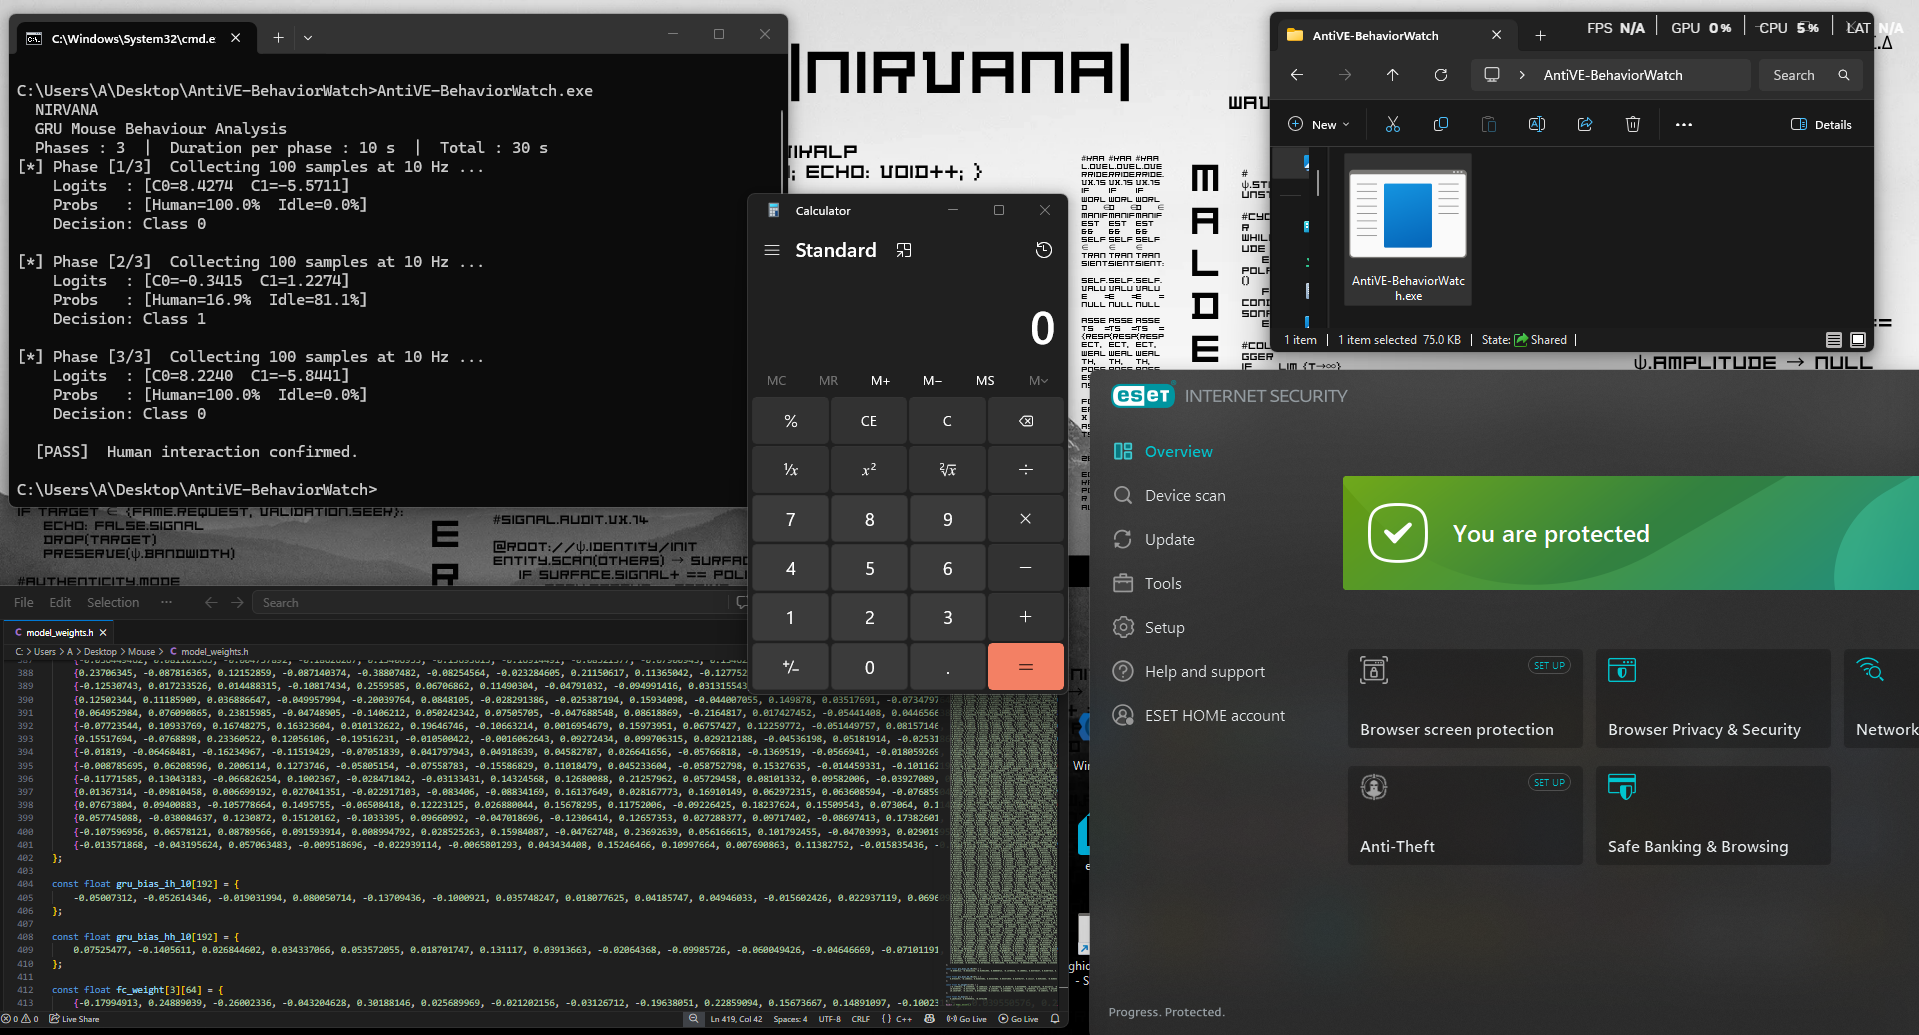
AntiVE-BehaviorWatch

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…

Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…

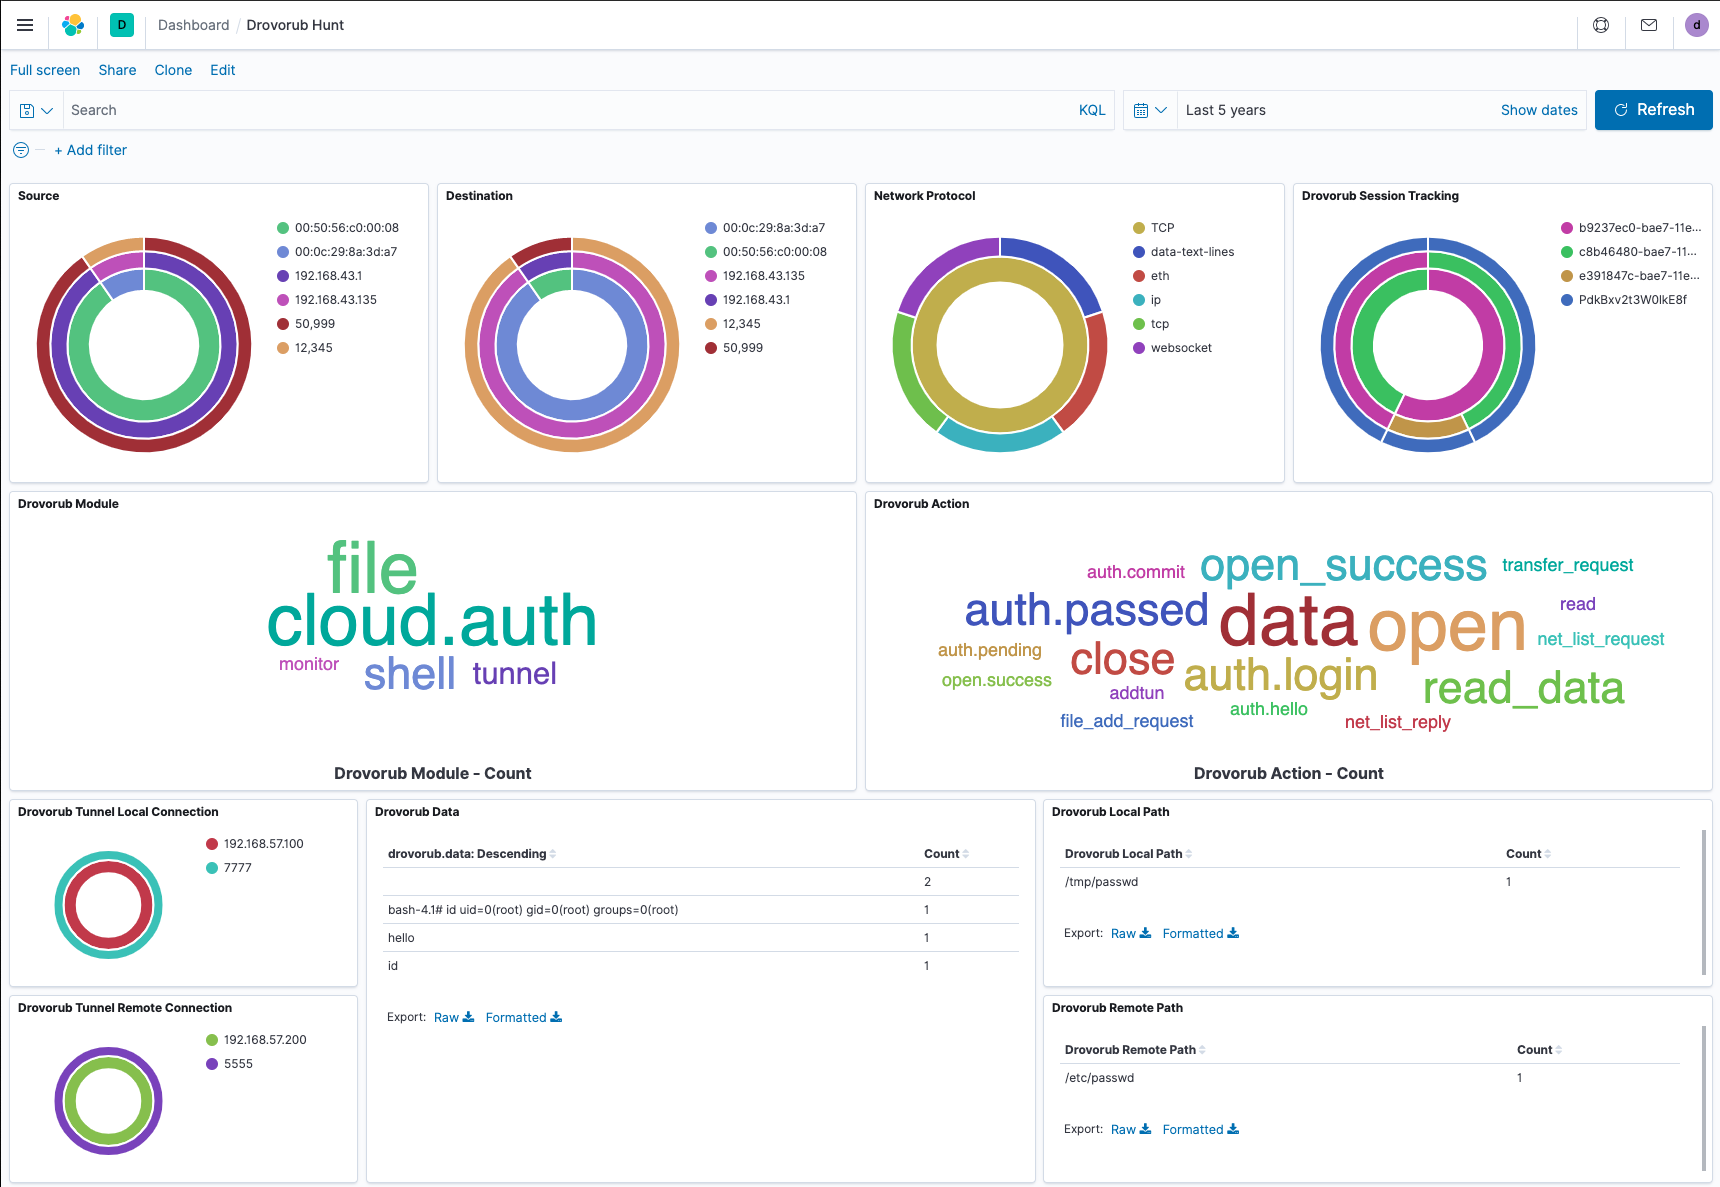
A tool to assist with network-based hunting for GRU's Drovorub malware c2

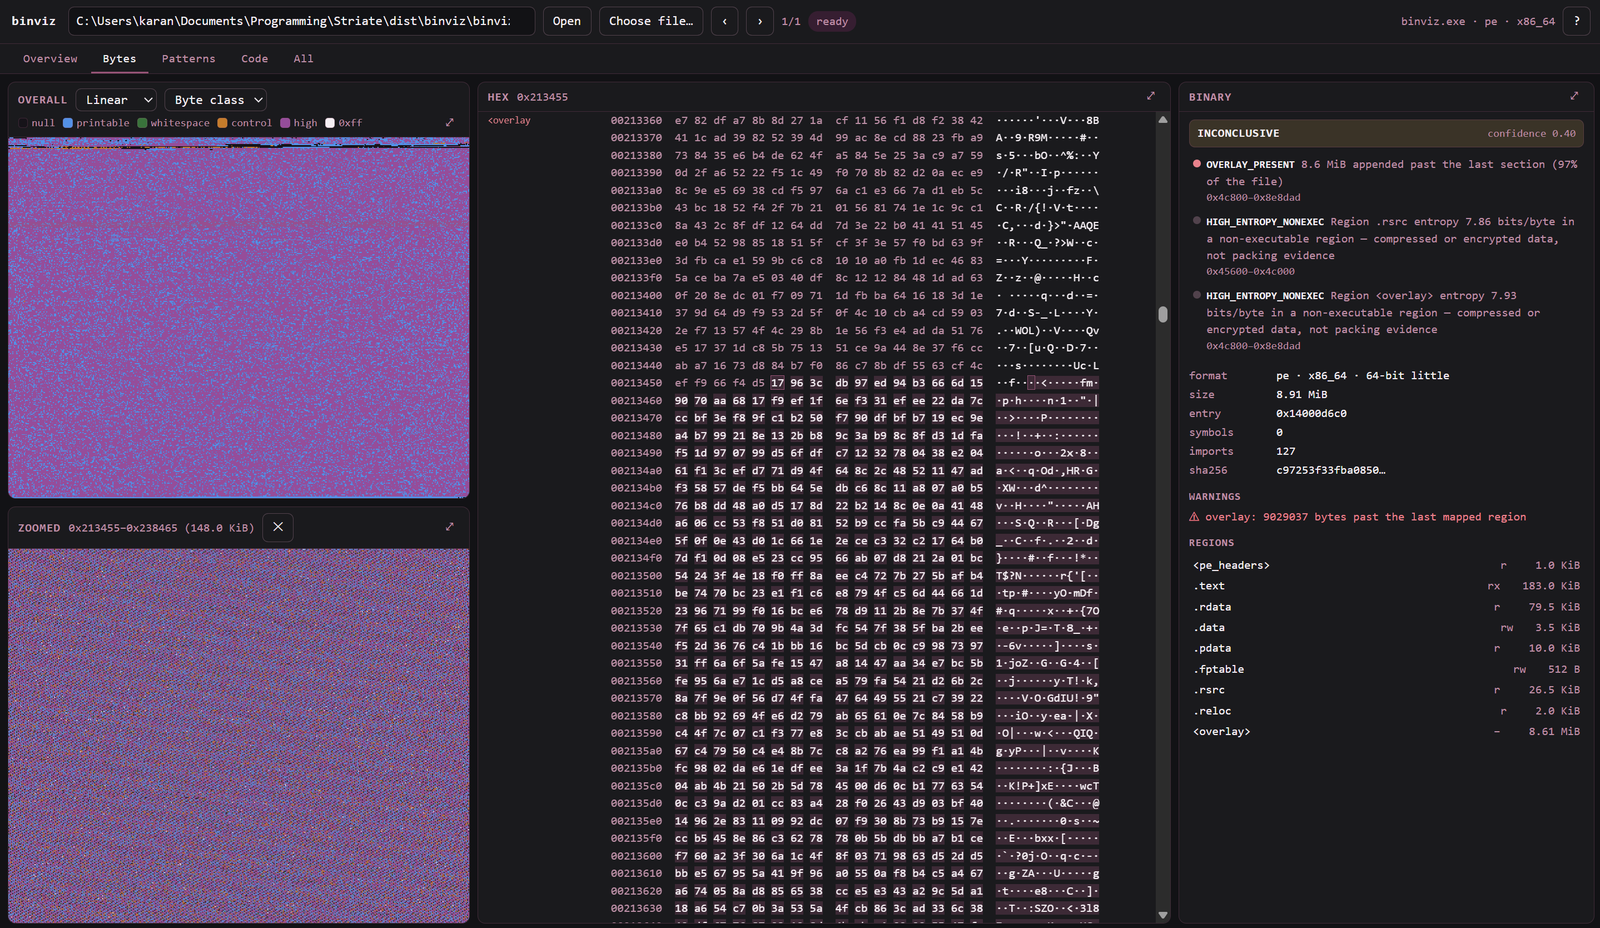
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.

Zeek detector for QuasarRat

Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…

List of Awesome CobaltStrike Resources

LKM rootkit for Linux Kernels 2.6.x/3.x/4.x/5.x/6.x (x86/x86_64 and ARM64)

Decrypted content of odd.tar.xz.gpg, swift.tar.xz.gpg and windows.tar.xz.gpg

Rust Weaponization for Red Team Engagements.

BlackLotus UEFI Windows Bootkit

RAT And C&C Resources. 250+ Open Source Projects, 1200+ RAT/C&C blog/video.

Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…

A framework for constructing self-spreading binaries

CVE-2021-40444 - Fully Weaponized Microsoft Office Word RCE Exploit

EXOCET - AV-evading, undetectable, payload delivery tool

Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…

Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…