RedTeaming-Tactics-and-Techniques

Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…

Comprehensive red teaming notes covering offensive security techniques including code injection, defense evasion, lateral movement, and persistence,…

The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…

Technical analysis of a multi-stage Adobe Acrobat PDF JavaScript sample, detailing environment triage, Acrobat API abuse, and in-memory payload…

Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…

Research and proof-of-concept for module stomping, a technique to hide malicious code in legitimate Windows modules, with documentation and…

Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office Word RCE) with a built-in HTTP server for payload delivery and…


Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…

An open source script to perform malware static analysis on Portable Executable

A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…

Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.

Major Security Vulnerability on PrestaShop Websites - CVE-2022-31101

Static analysis of 2 malicious Office documents on REMnux using oletools; identified CVE-2017-11882 and obfuscated macros.


Collection of some easy of use tools - in powershell.

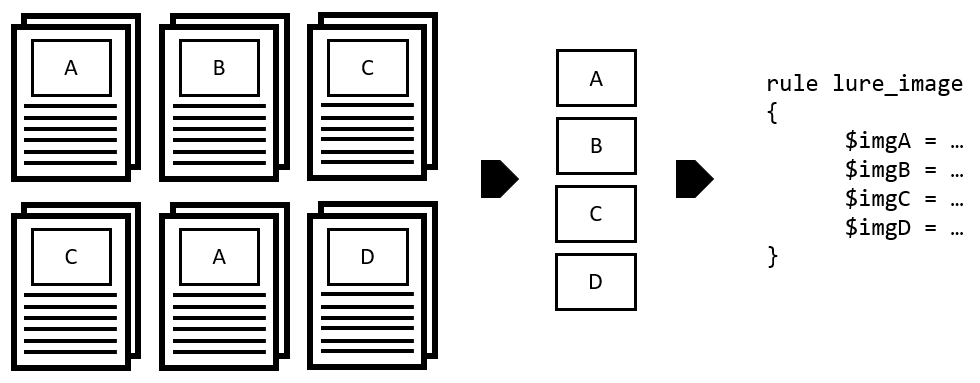
Automatically create YARA rules from malicious documents.

Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…