

Brovan
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
169
advdebug/brovanUser-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 cert-polska/drakvuf-sandbox
Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
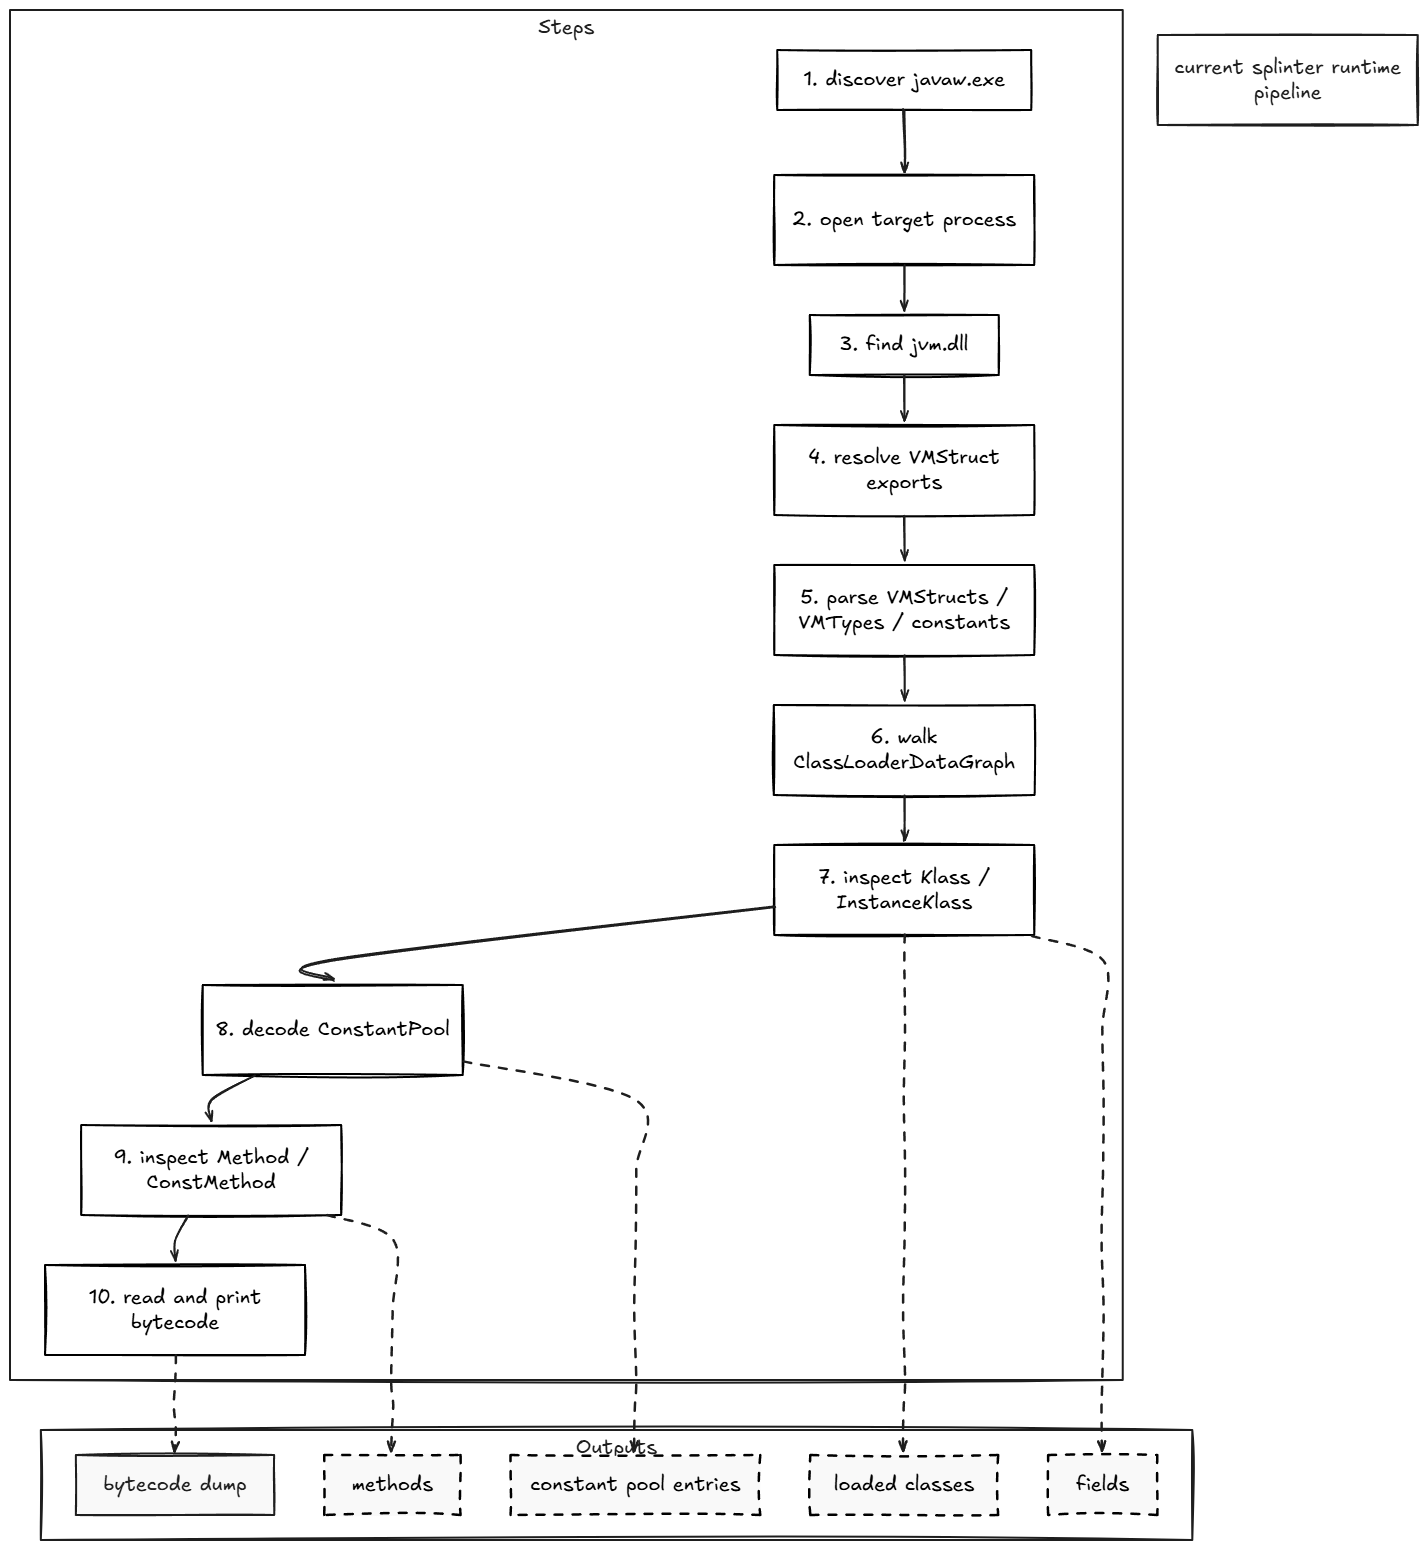 awrped/splinter
Runtime JVM analysis toolkit for inspecting classes, methods, fields, constant pool, and bytecode
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
 biitts/cve-2026-56121-feast-unauth-rce
CVE-2026-56121 — Feast <0.63.0 unauthenticated RCE via gRPC registry dill.loads of OnDemandFeatureView UDF (pre-auth). Lab + PoC, verified e2e.
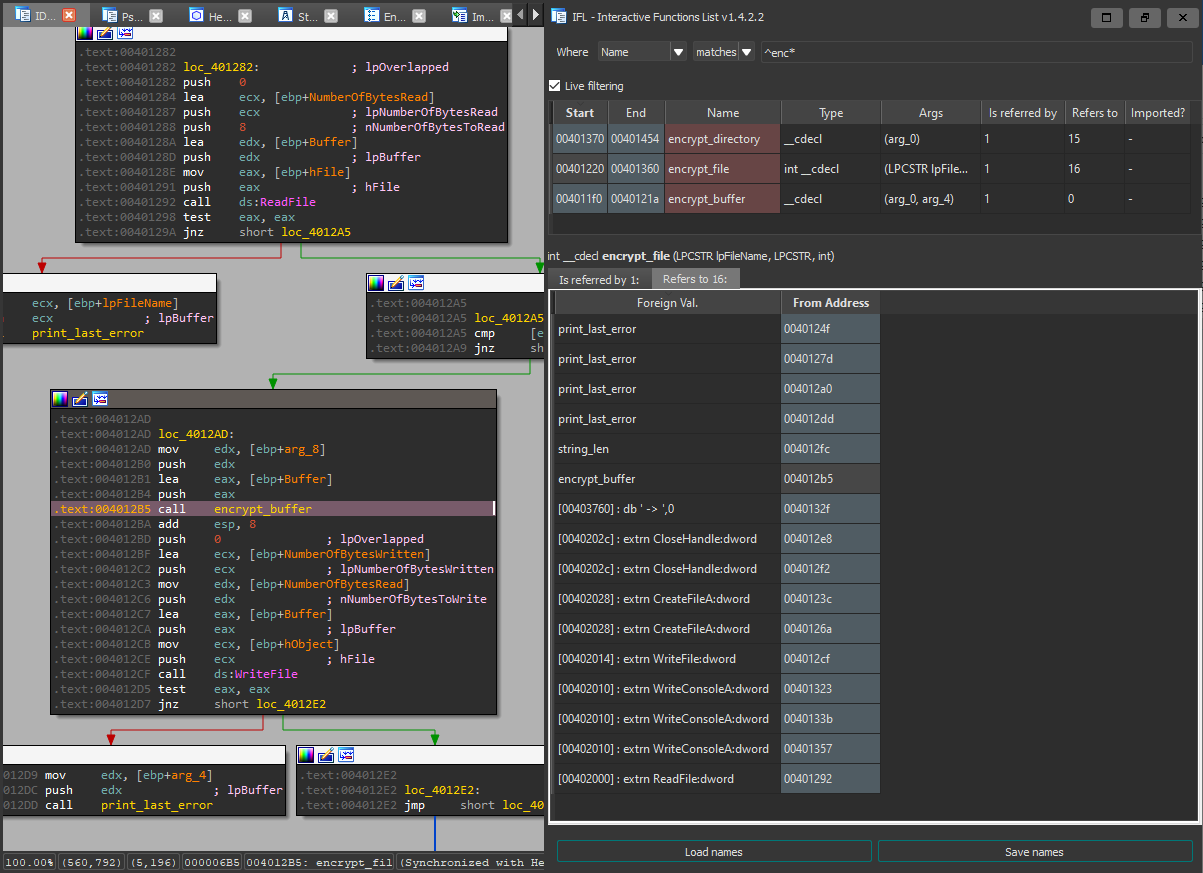 hasherezade/ida_ifl
IFL - Interactive Functions List (plugin for IDA Pro)
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 simoesctt/sctt-2026-33-0007-the-ole-vortex-laminar-bypass-
Microsoft just released emergency patches for CVE-2026-21509, a zero-day in the Office Suite that bypasses OLE/COM mitigations when a user simply…
 wowfunhappy/fix-apple-mail-cve-2020-9922
Patches the zero-click Apple Mail vulnerability (CVE-2020-9922) on macOS, preventing remote code execution without user interaction.
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 0x48piraj/incarcero
Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 gmh5225/offensivedriver
Windows kernel driver prototype that toggles process protection, adjusts process privileges, patches DSE policy, and manipulates AV/EDR kernel…