

PCAPdroid
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
android-securitydns-analysiseducation+8
emanuele-f/pcapdroidNo-root network monitor, firewall and PCAP dumper for Android
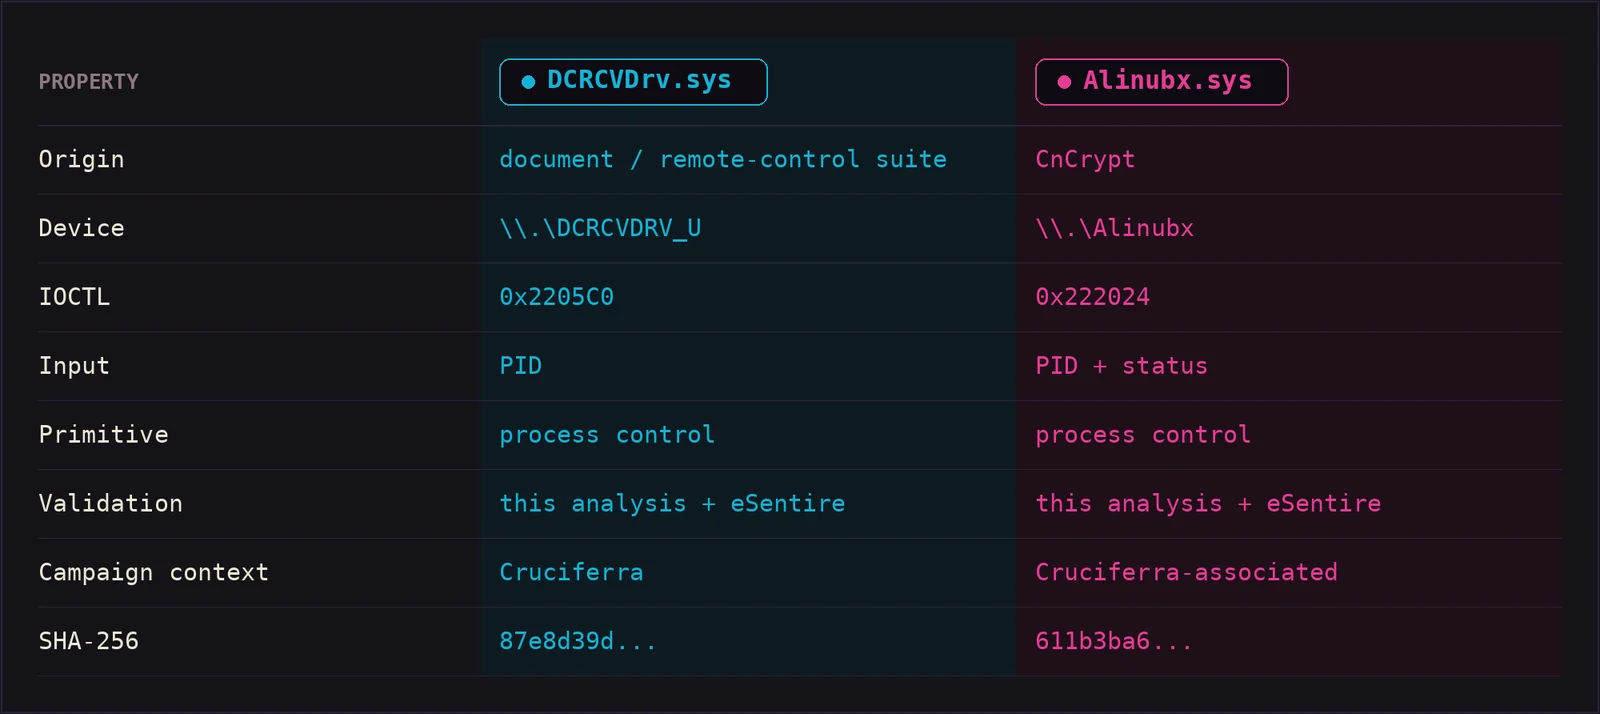 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 i014n/pngloader
Hides arbitrary payloads in PNG images using nibble-to-ASCII encoding and Fibonacci LSB steganography, with a C++ loader that extracts and executes…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 ashishb/android-security-awesome
A collection of android security related resources
 bst04/cybersources
A curated list of cybersecurity tools and resources.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 buter-chkalova/rvbbit-arsenal
Offensive & defensive Linux kernel security research focused on rootkit behavior, observable artifacts and detection.
 buter-chkalova/project-rvbbit
Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
 namegabevictoire01-sys/cs50-cybersecurity-final-project
CS50 Cybersecurity Final Project - Analysis of CVE-2024-3094
 ytisf/thezoo
Curated repository of live malware samples and source code for educational malware analysis and research, with an organized database and CLI tools…
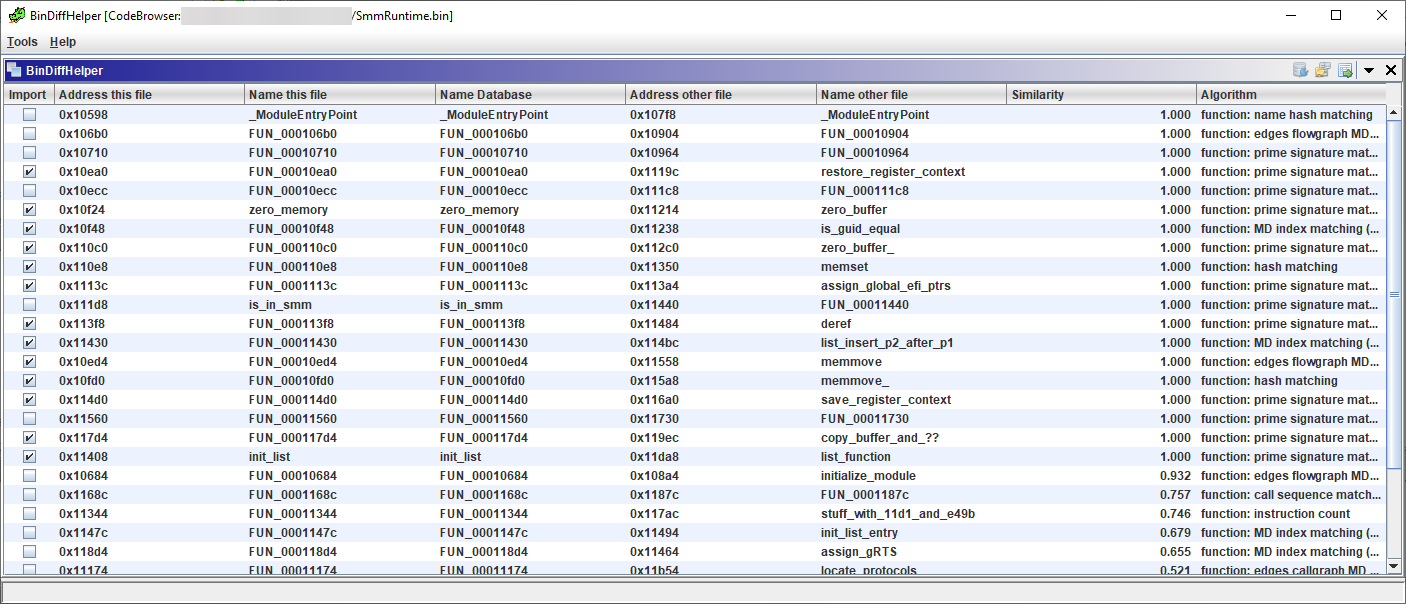 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
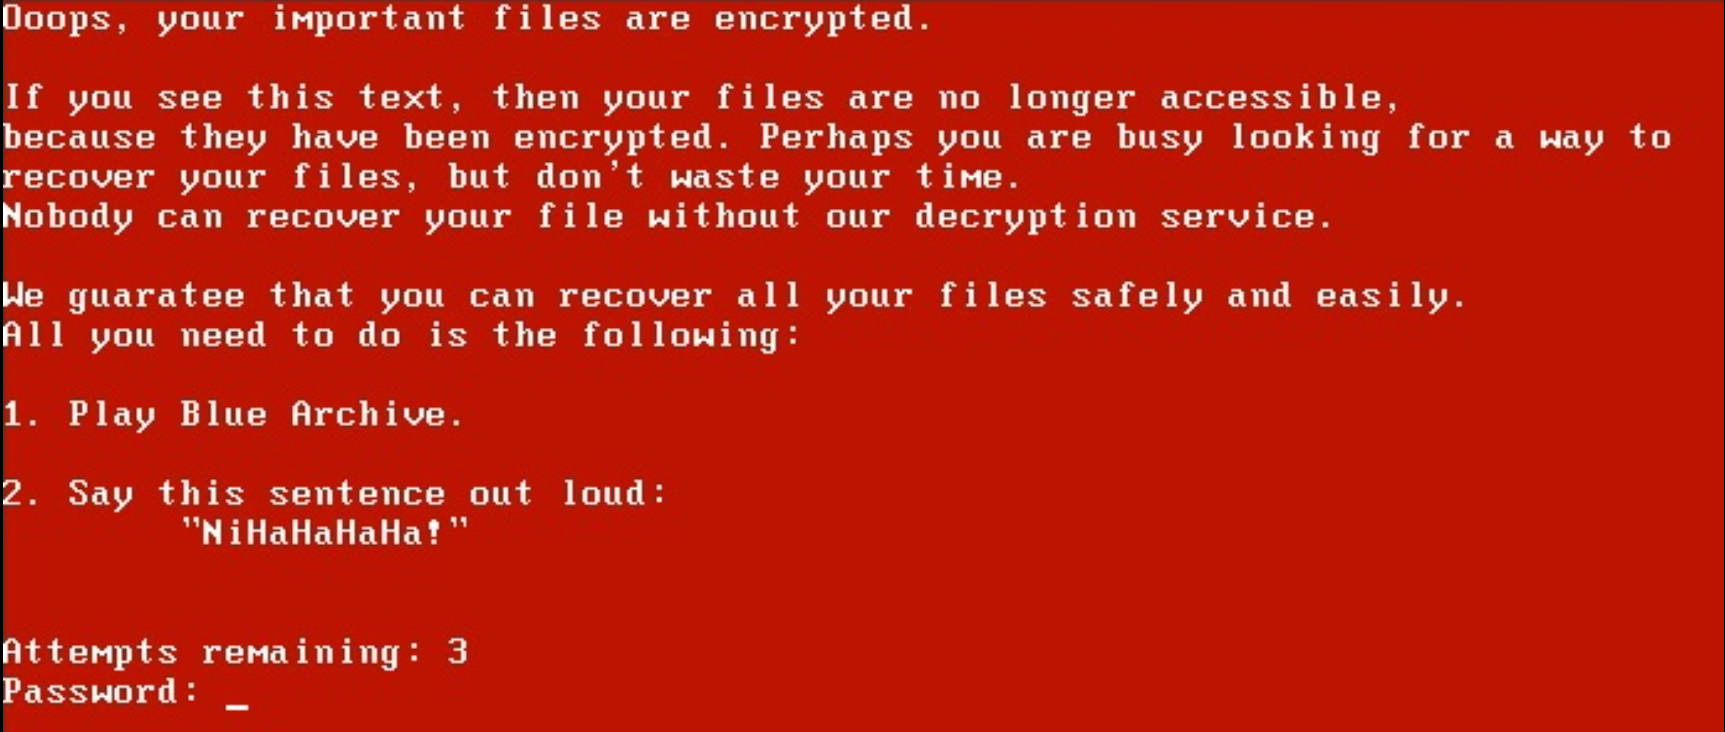 iss4cf0ng/openpetya
A Proof-of-Concept bootkit and UEFI boot application inspired by Petya ransomware, written in Assembly, C, and C++
 mhicairo-hue/cs50-cybersecurity-final-project
Technical analysis of the XZ Utils backdoor (CVE-2024-3094), explaining the supply chain attack, obfuscation techniques, and impact on OpenSSH via…
 cert-polska/drakvuf-sandbox
Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
 swastiksagar/wazuhlabproject
Hands-on Wazuh SIEM/XDR home lab covering OVA deployment, agent enrollment, file integrity monitoring, VirusTotal malware detection, and MITRE ATT&CK…