

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
24.8k
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 ev-flow/quark-engine
Rule-based Android malware scoring engine that analyzes APKs using static and dynamic analysis to detect vulnerabilities, identify malware families,…
 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
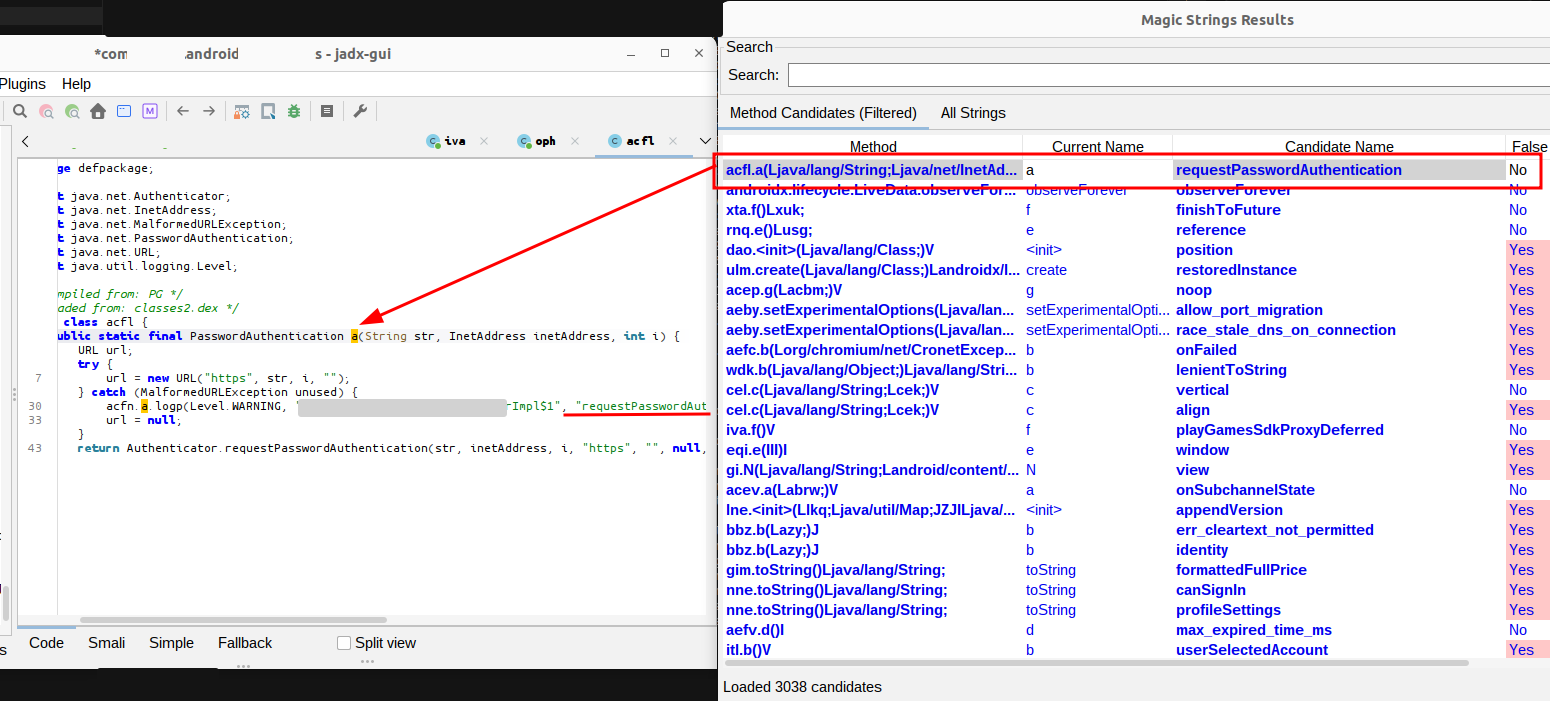 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
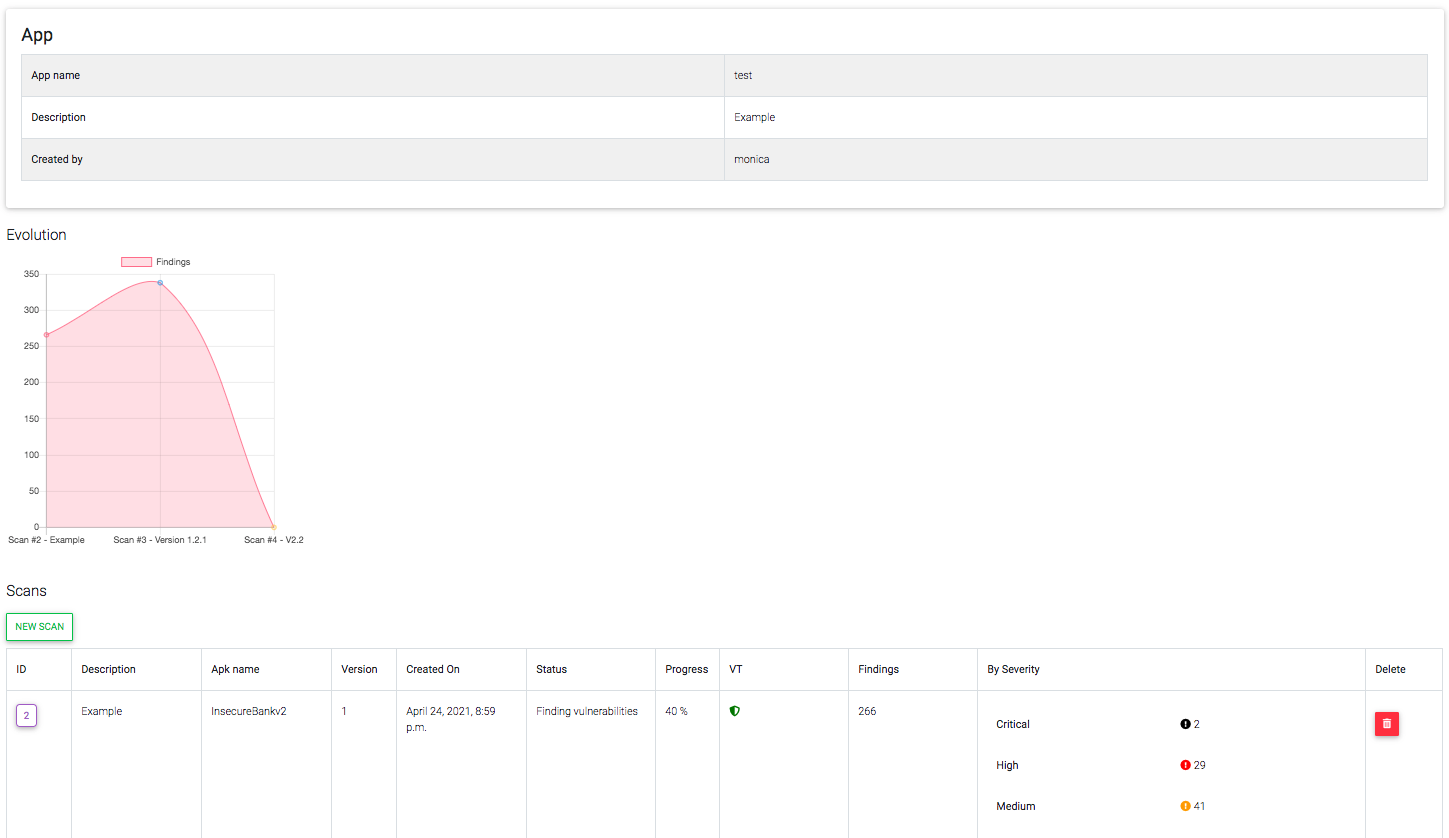 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 ashishb/android-security-awesome
A collection of android security related resources
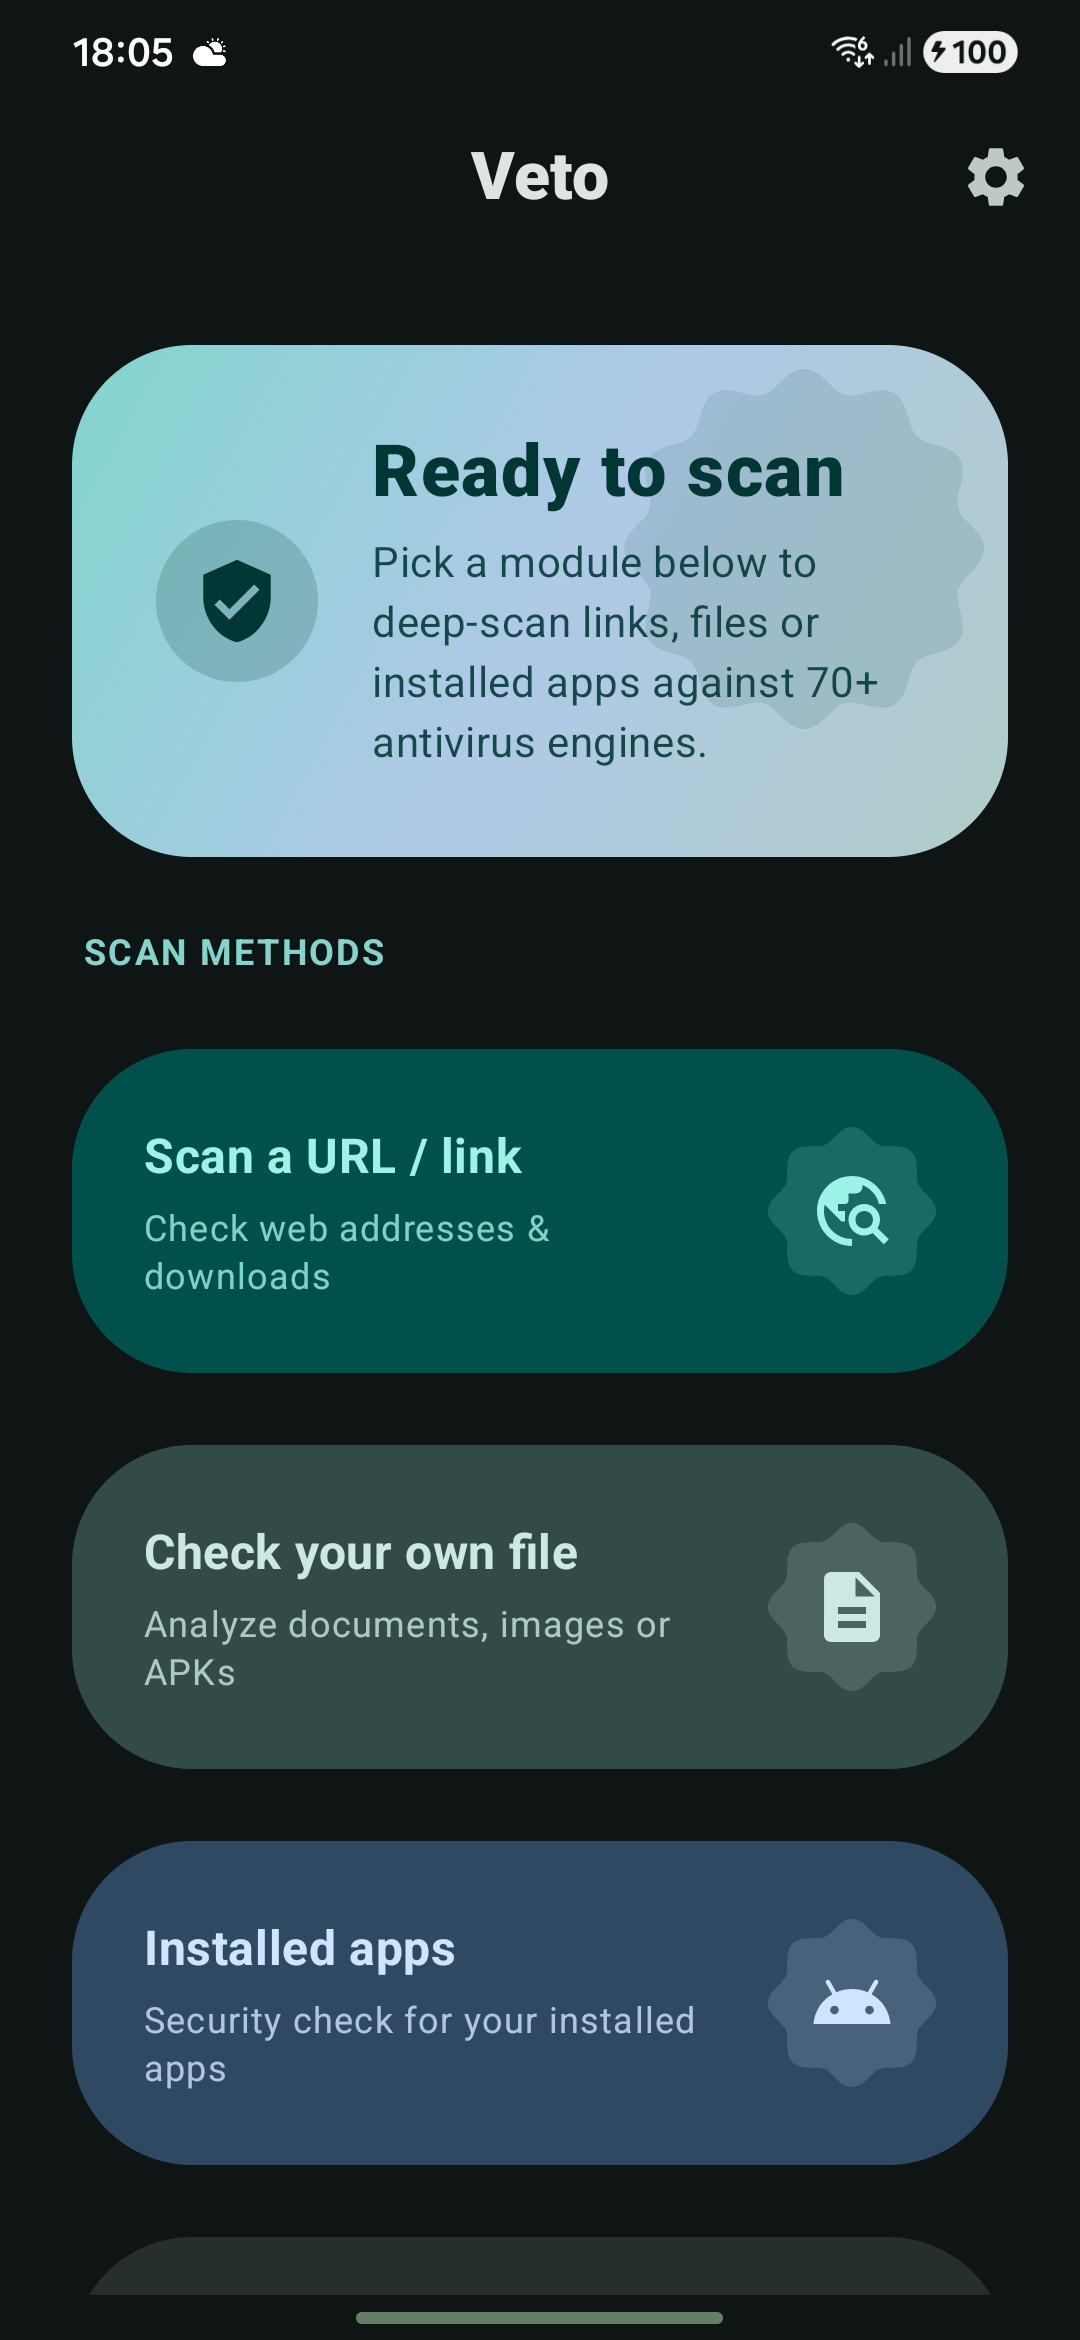 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
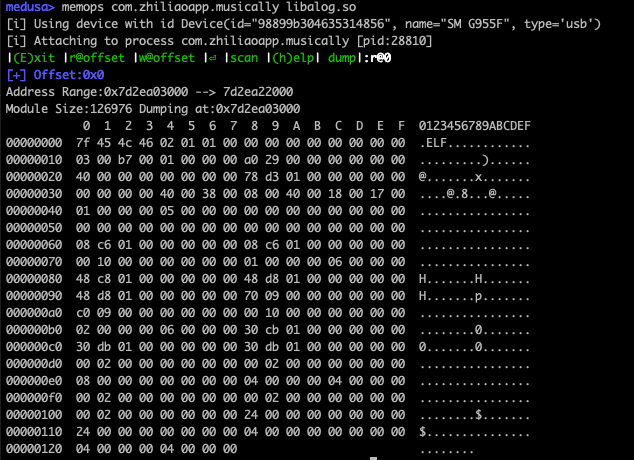 ch0pin/medusa
Mobile Edge-Dynamic Unified Security Analysis
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 androguard/androguard
Reverse engineering and pentesting for Android applications
 saeidshirazi/awesome-android-security
A curated list of Android Security materials and resources For Pentesters and Bug Hunters