

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
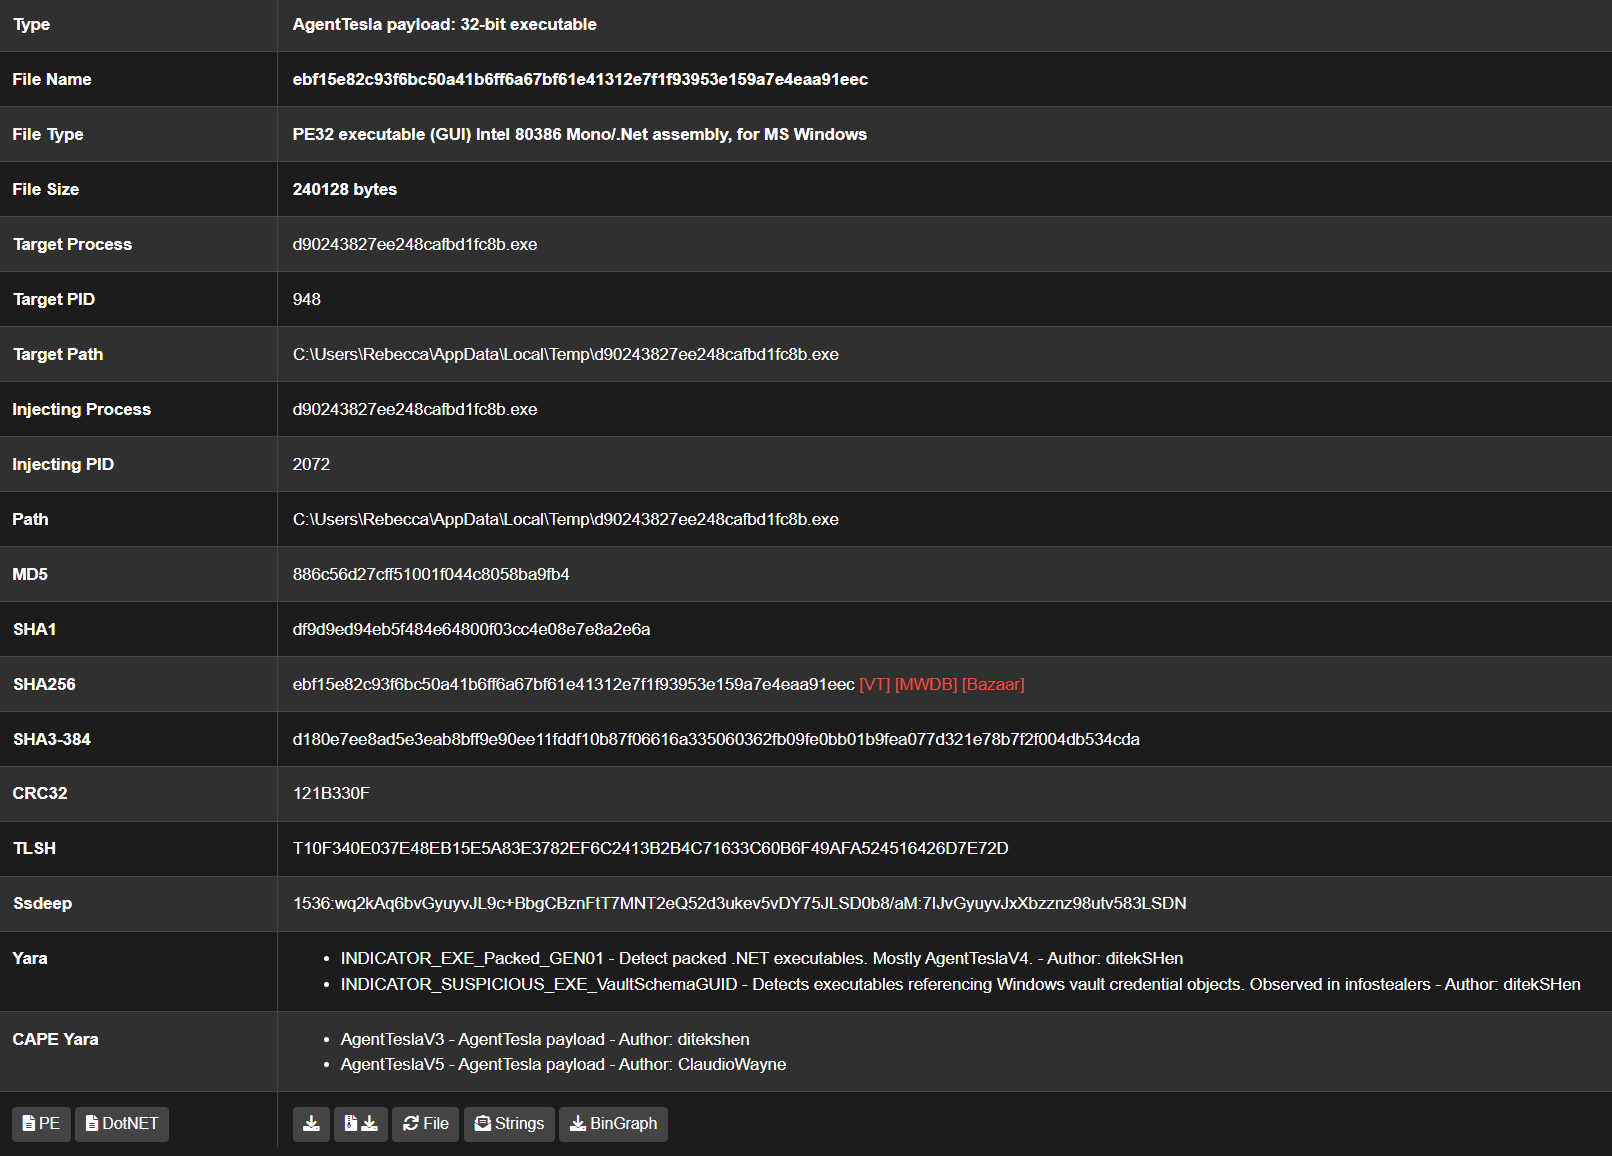 kevoreilly/capev2
Malware Configuration And Payload Extraction

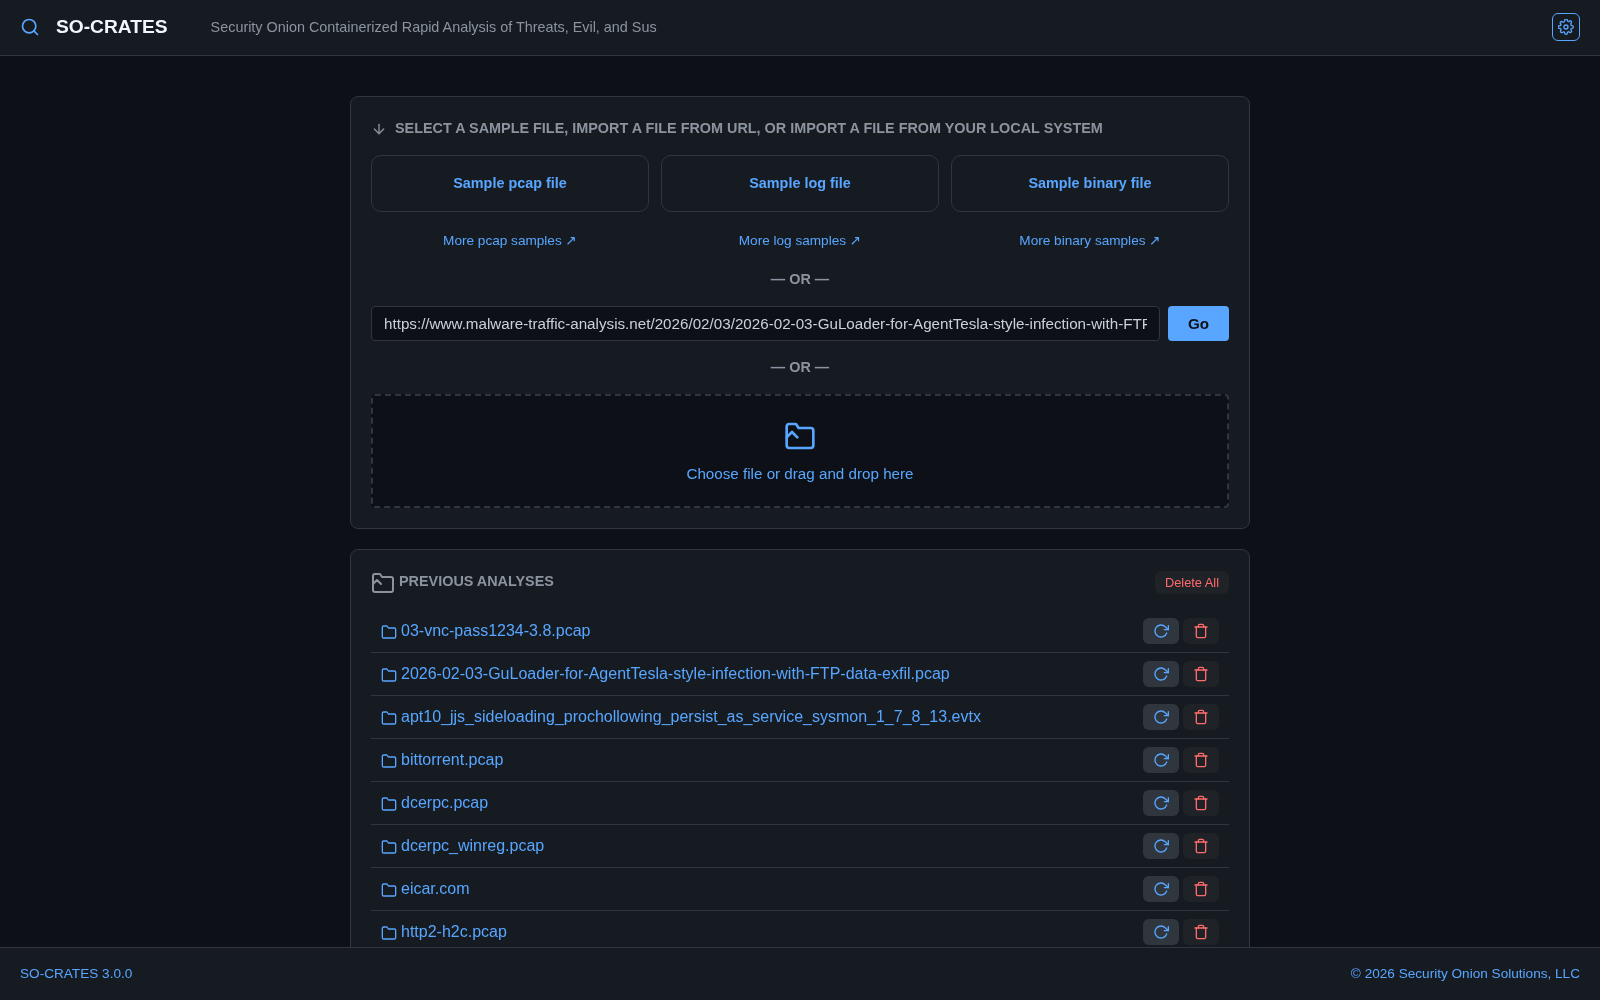 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 toborrm9/malicious_extension_sentry
Malicious Extension Database

 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 bb1nfosec/information-security-tasks
Curated infosec knowledge base of practitioner notes, methodologies, and daily-updated CVE, news, and tool digests organized by offensive, defensive,…
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 nmatt0/moria
IoT firmware identification and extraction