

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
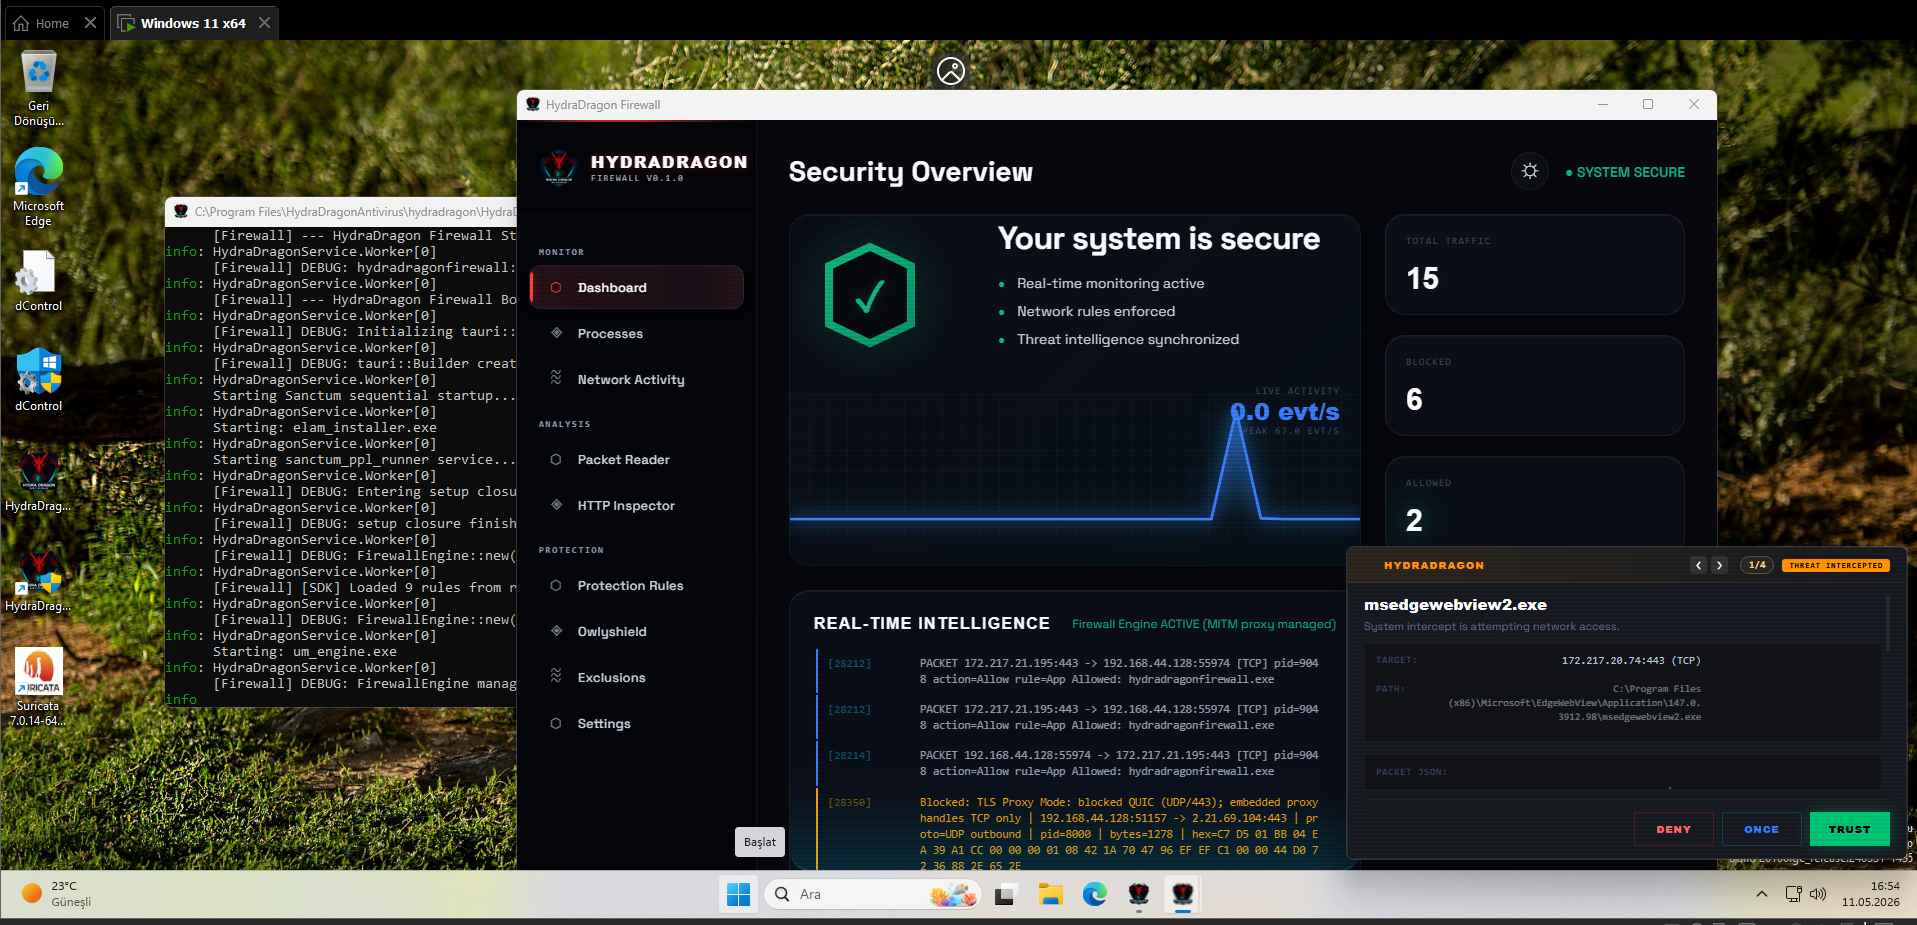 hydradragonantivirus/hydradragonantivirus
Dynamic and static analysis with Real Time Malware Analysis with Antivirus for Windows, including open-source XDR (3 EDR projects), ClamAV, YARA-X,…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.

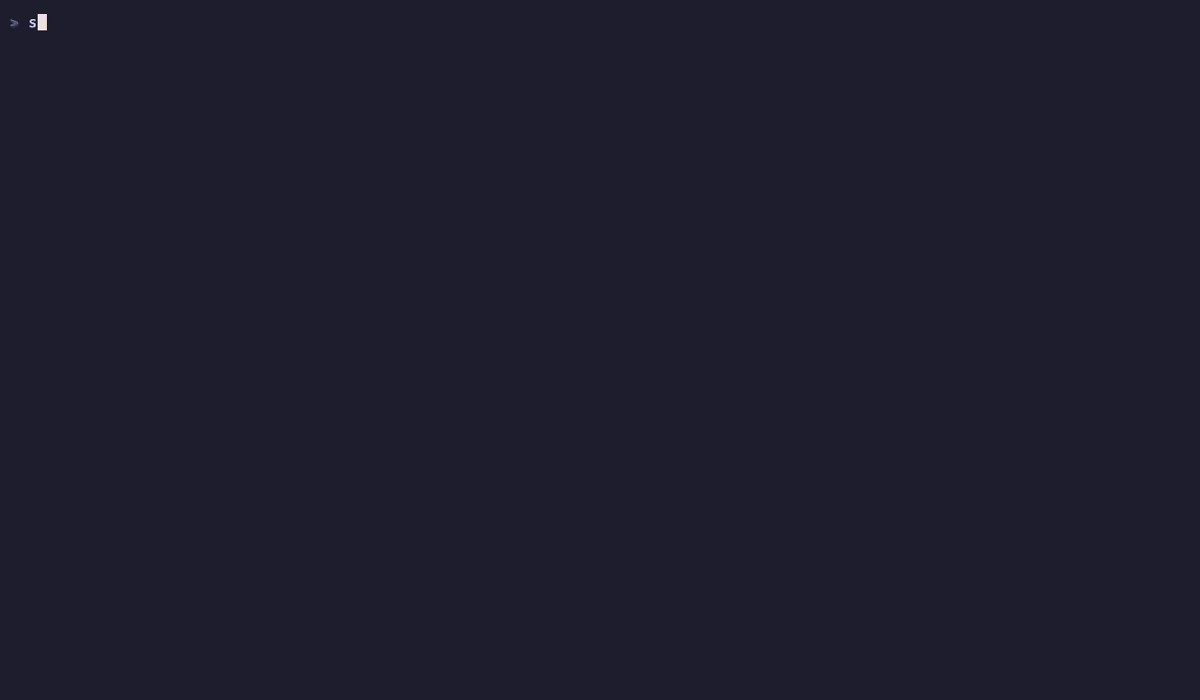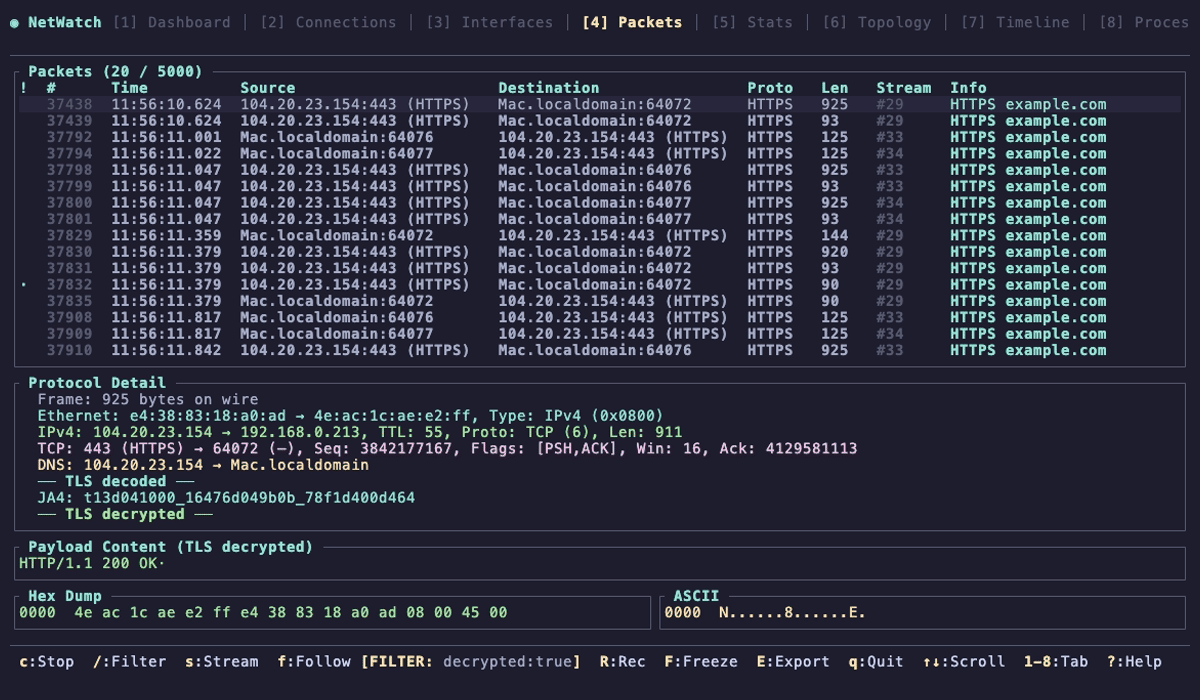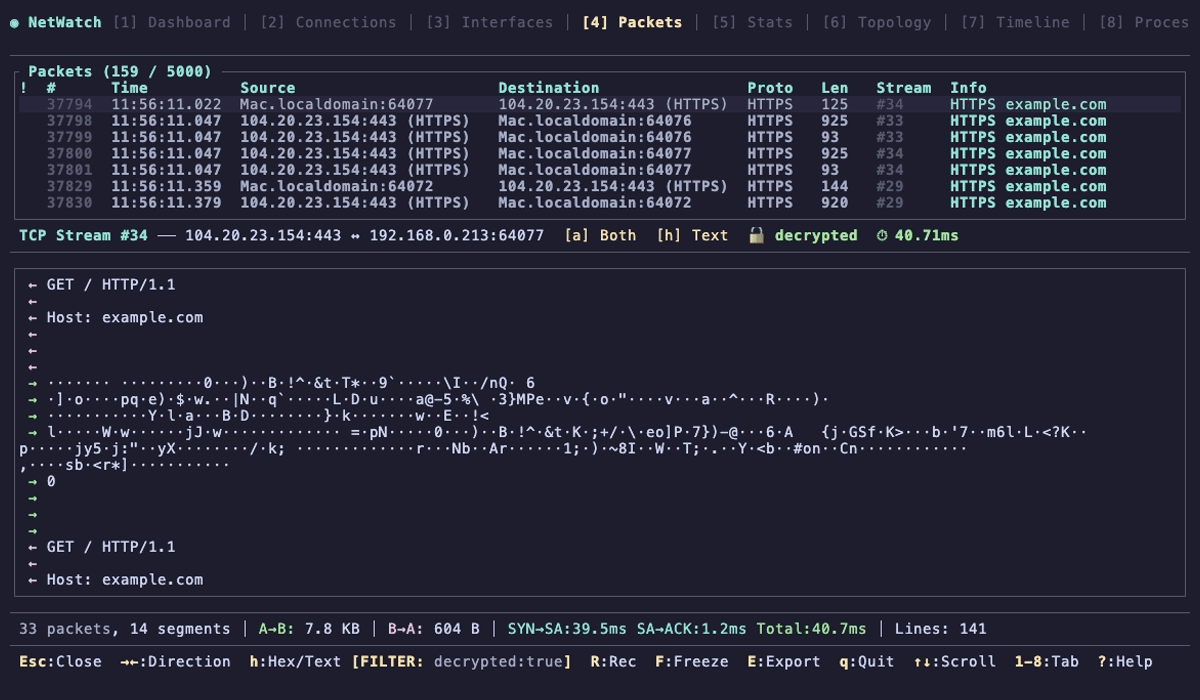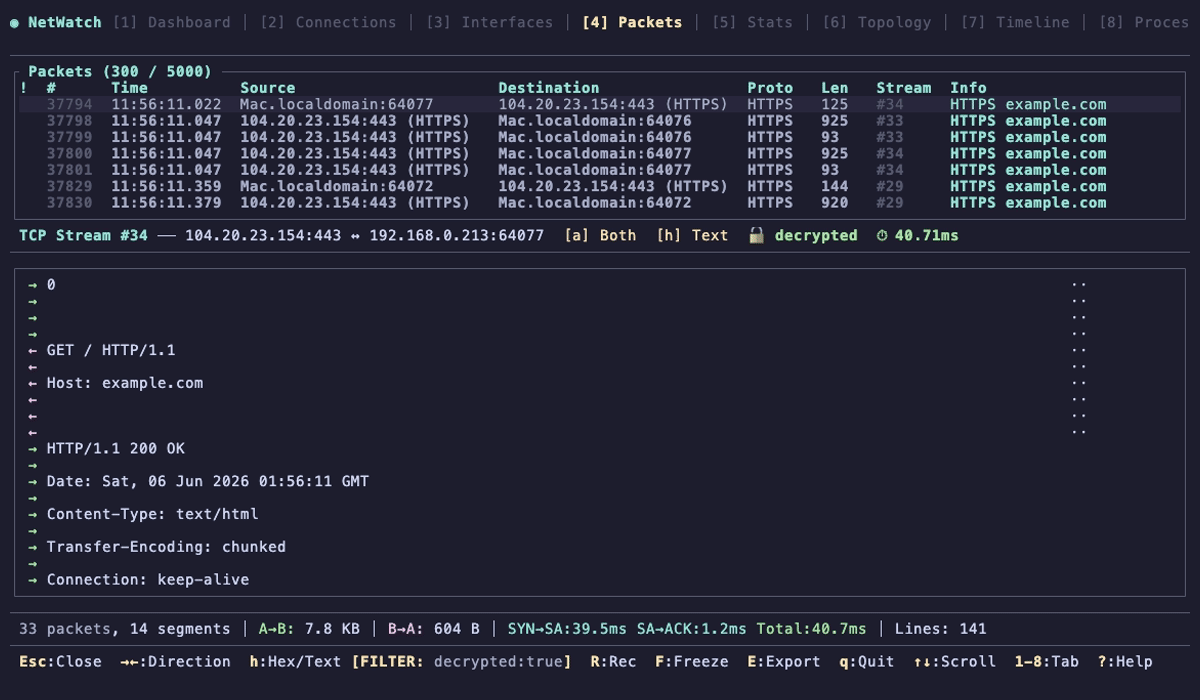 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 captmag/maldev
Creation of multiple Malware tools consisting of evasion, enumeration and exploitation
 nmatt0/moria
IoT firmware identification and extraction
 virustotal/vt-go
The official Go client library for VirusTotal API
 virustotal/vt-py
The official Python 3 client library for VirusTotal
 kevoreilly/capev2
Malware Configuration And Payload Extraction