
cowrie
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
defensive-toolsincident-responseinformation-gathering+3
cowrie/cowrieCowrie SSH/Telnet Honeypot https://docs.cowrie.org/
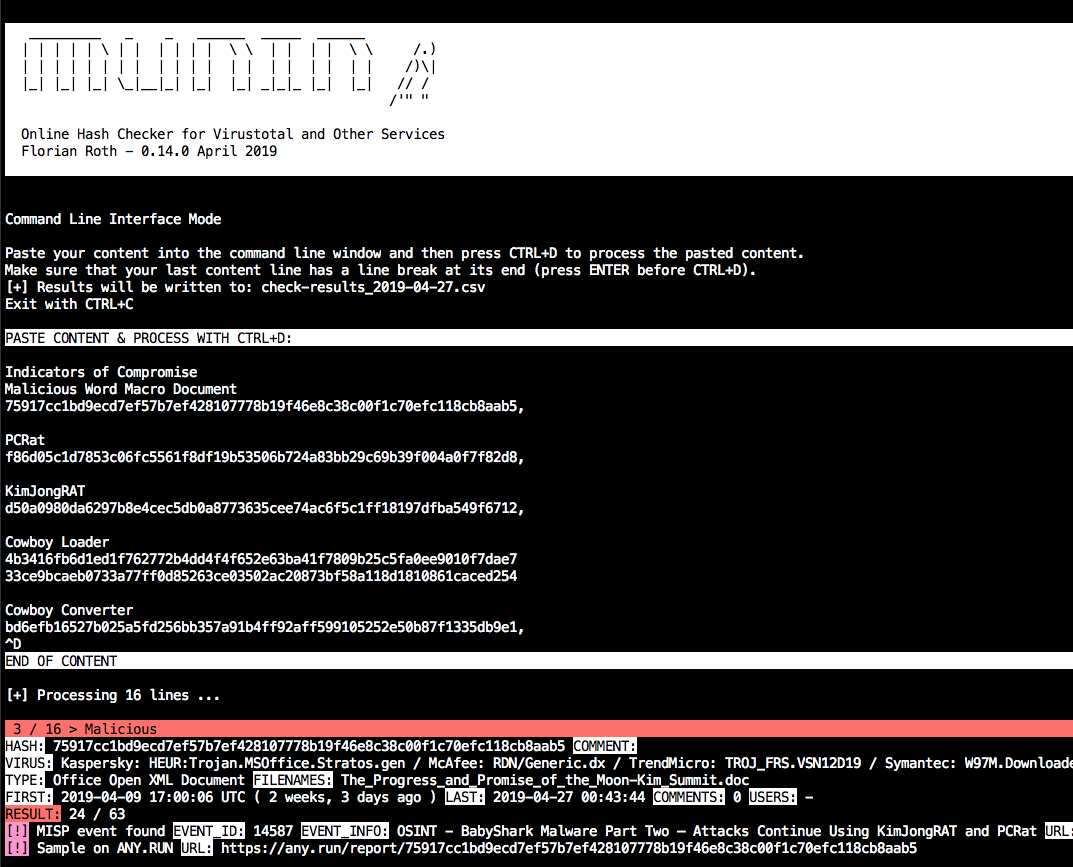 neo23x0/munin
Online hash checker for Virustotal and other services
 oalabs/hashdb
Assortment of hashing algorithms used in malware
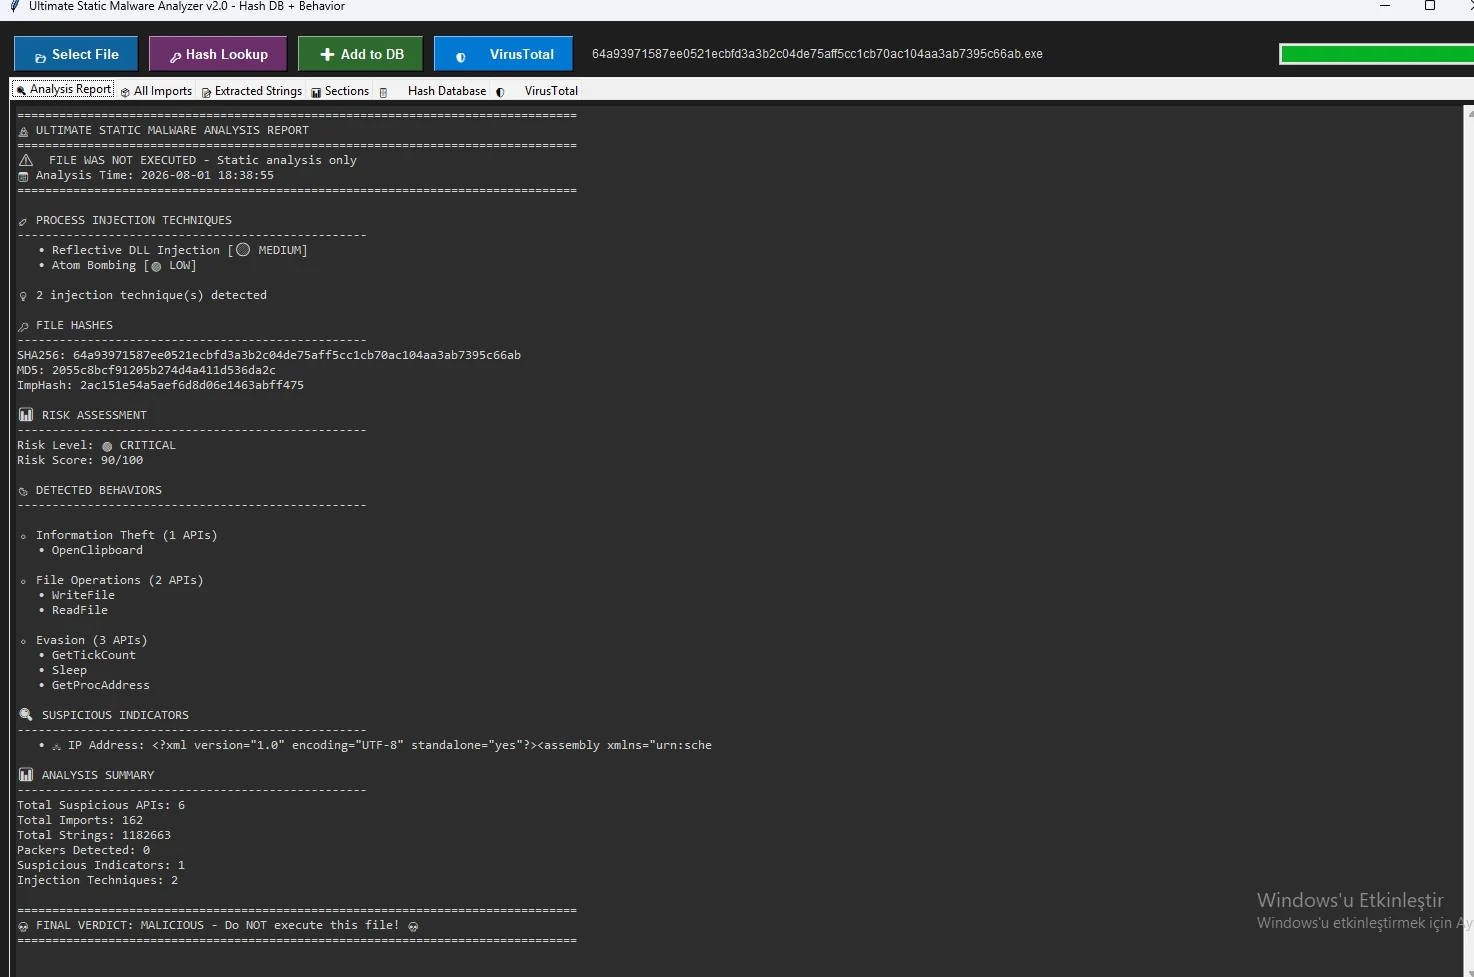 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
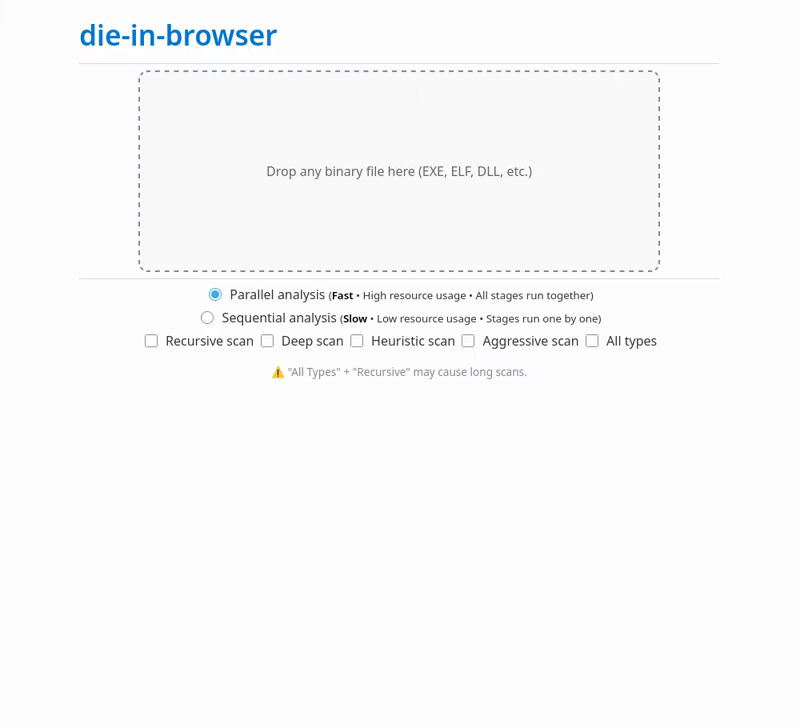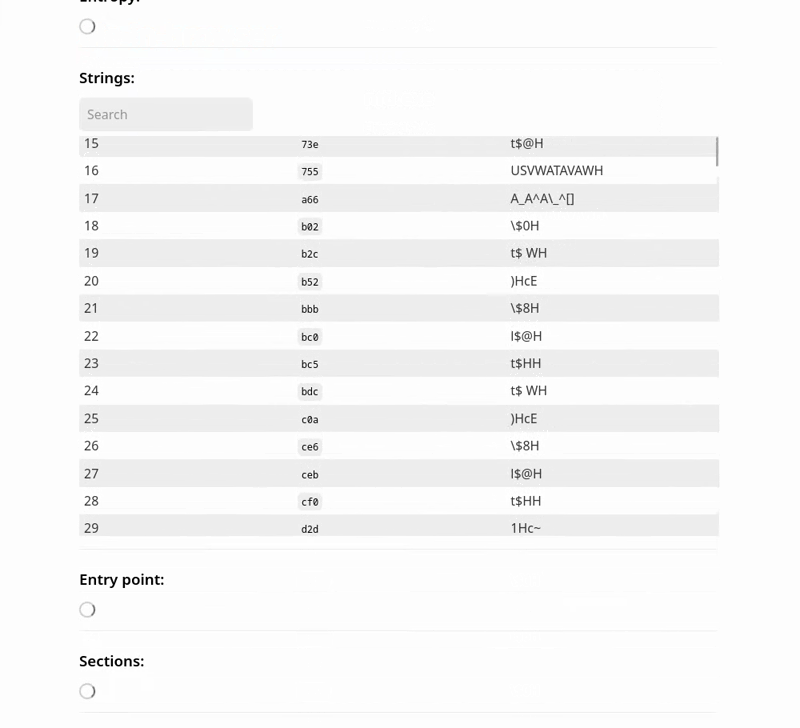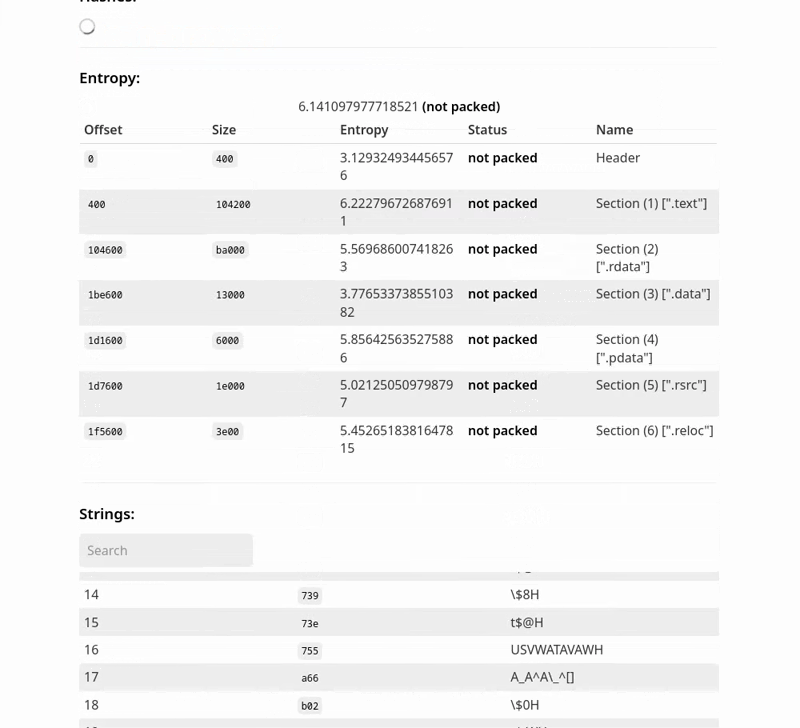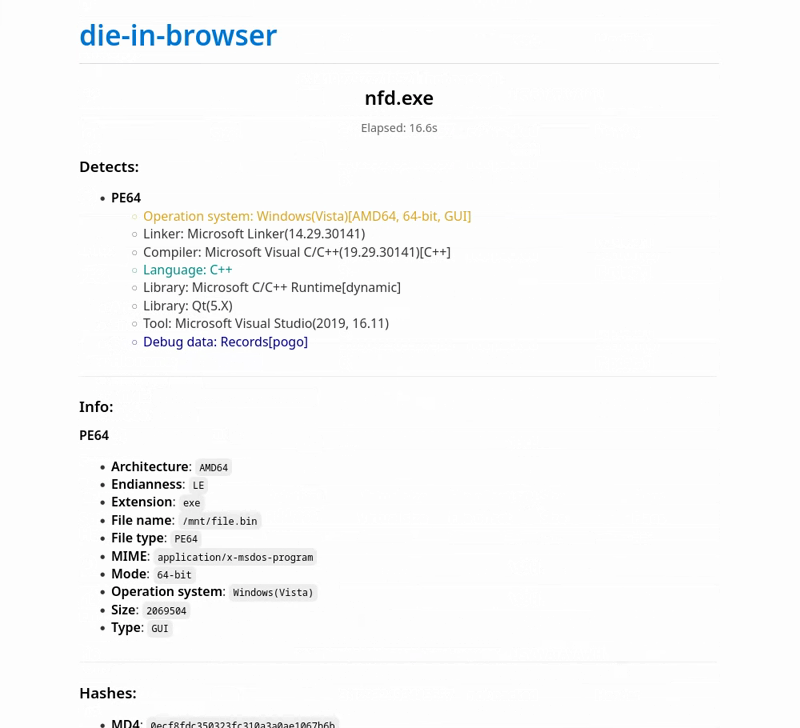 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 oalabs/hashdb-ida
HashDB API hash lookup plugin for IDA Pro
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 squiblydoo/certreport
A tool to support the reporting of Authenticode Certificates by reducing the effort on individuals to report.
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 neorai/vt-py-scanner
Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
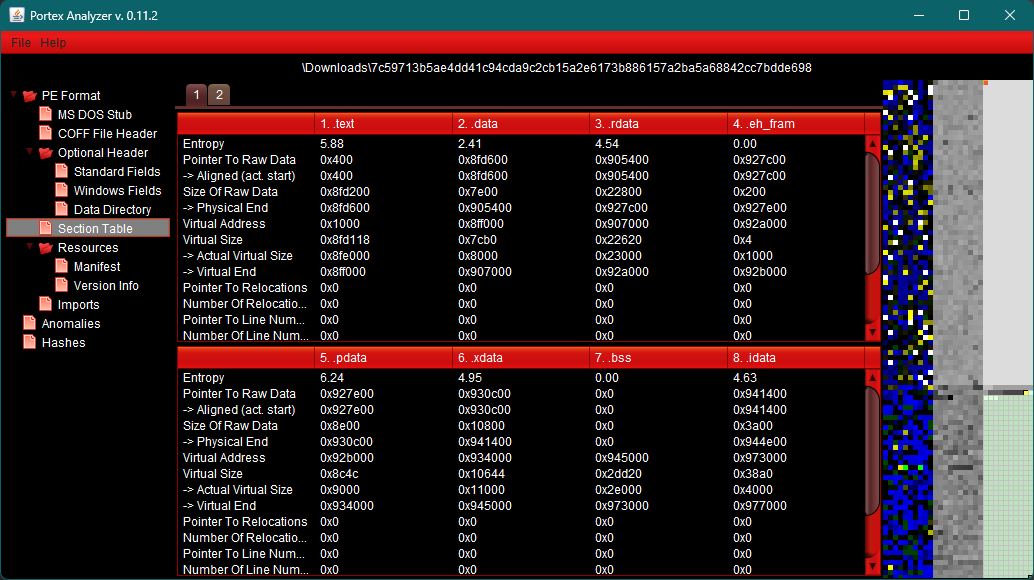 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library

 password123456/malwarescanner
Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
 abusech/yaraify
Open YARA scan- and search engine
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.