
pmg
 safedep/pmg
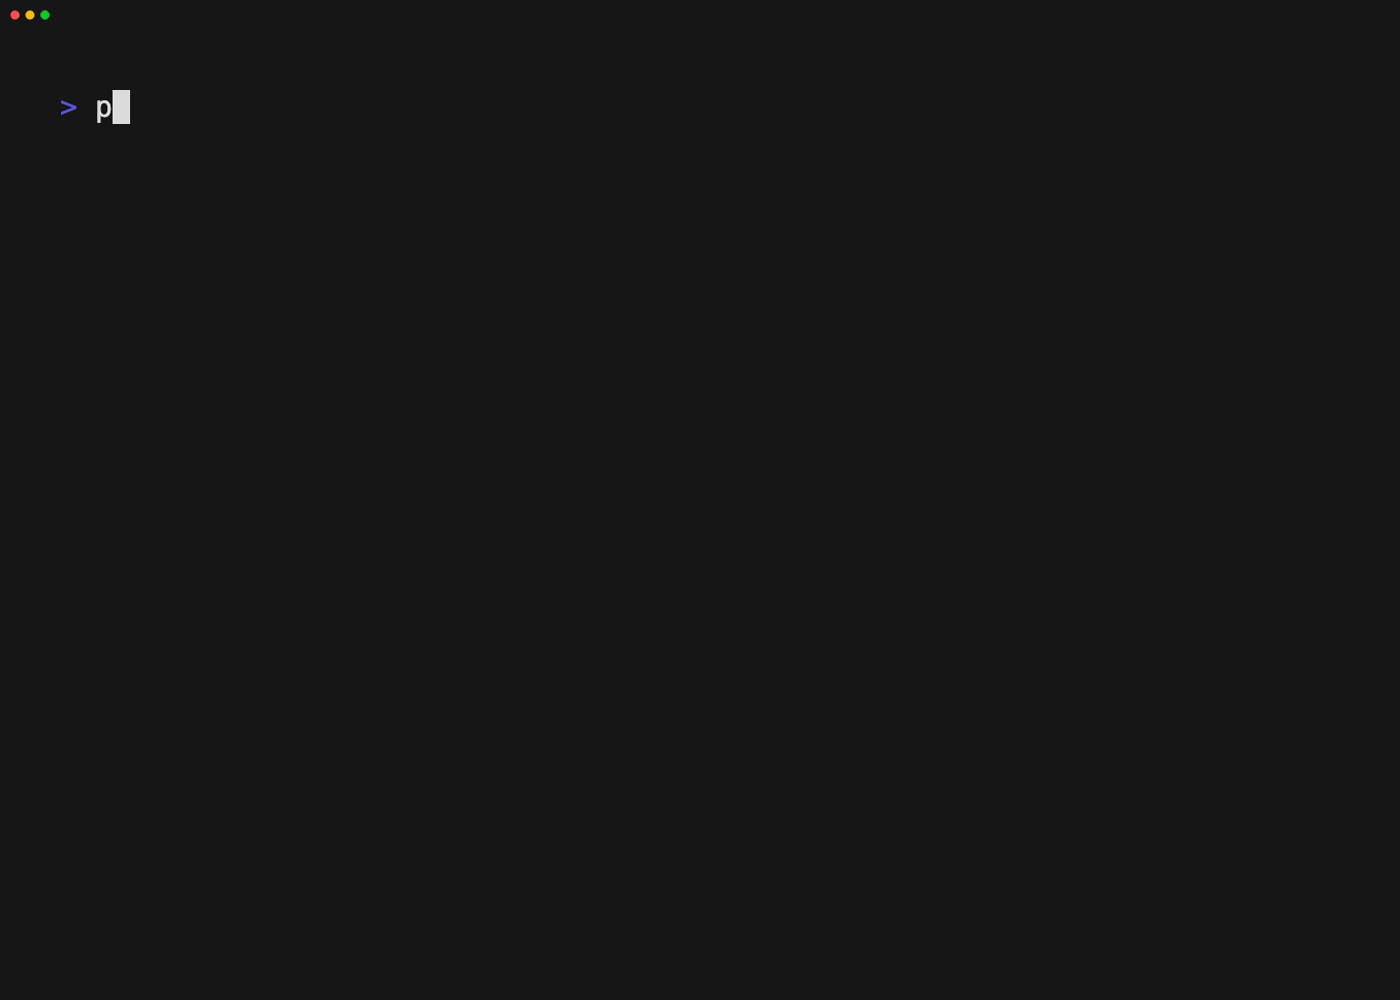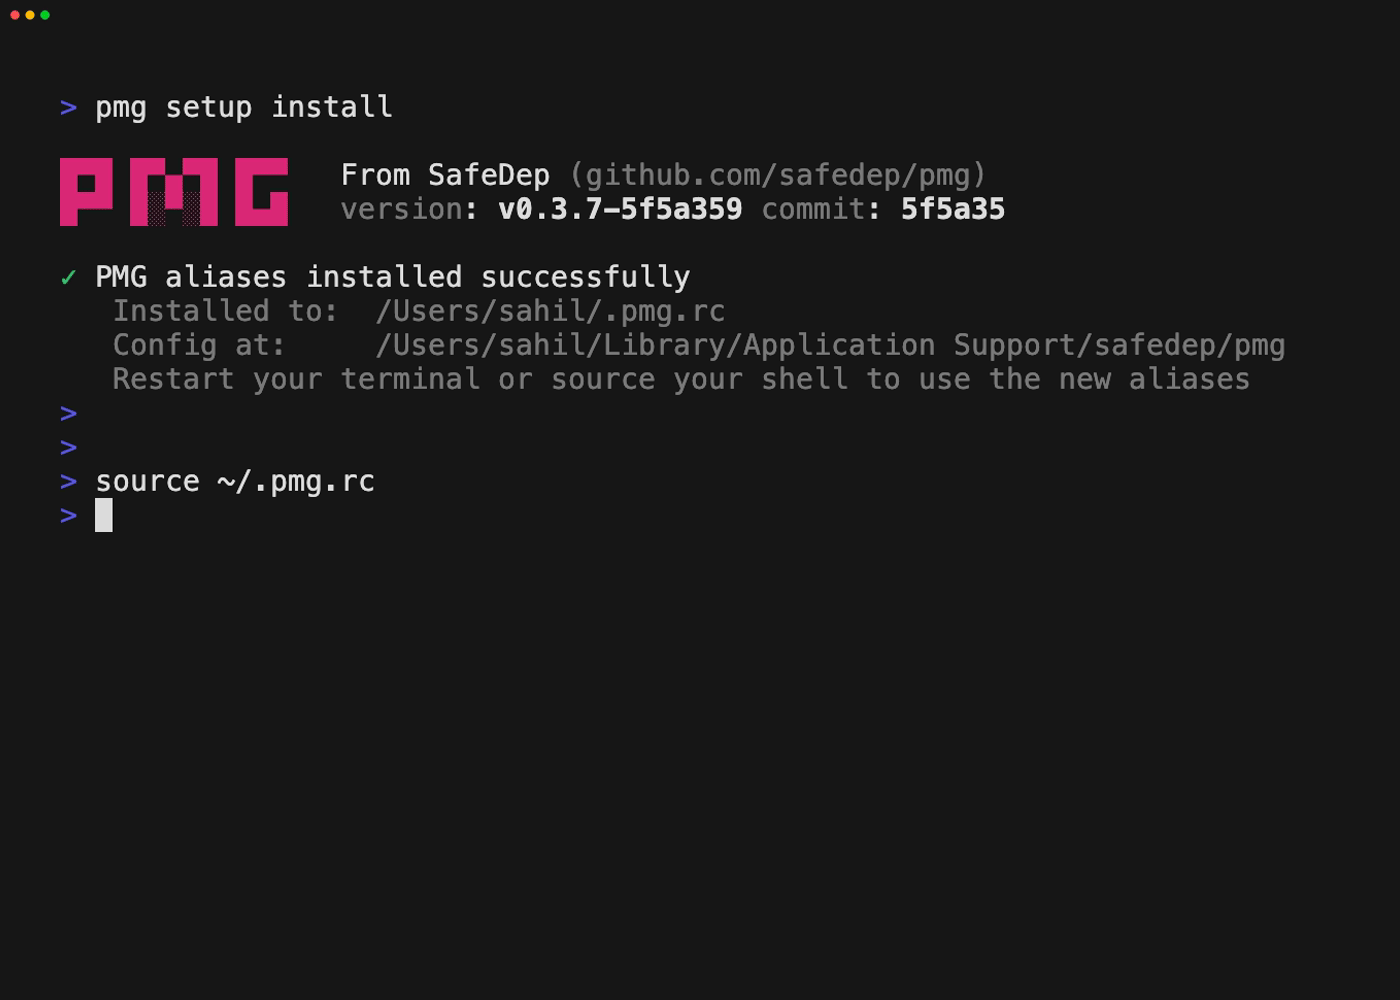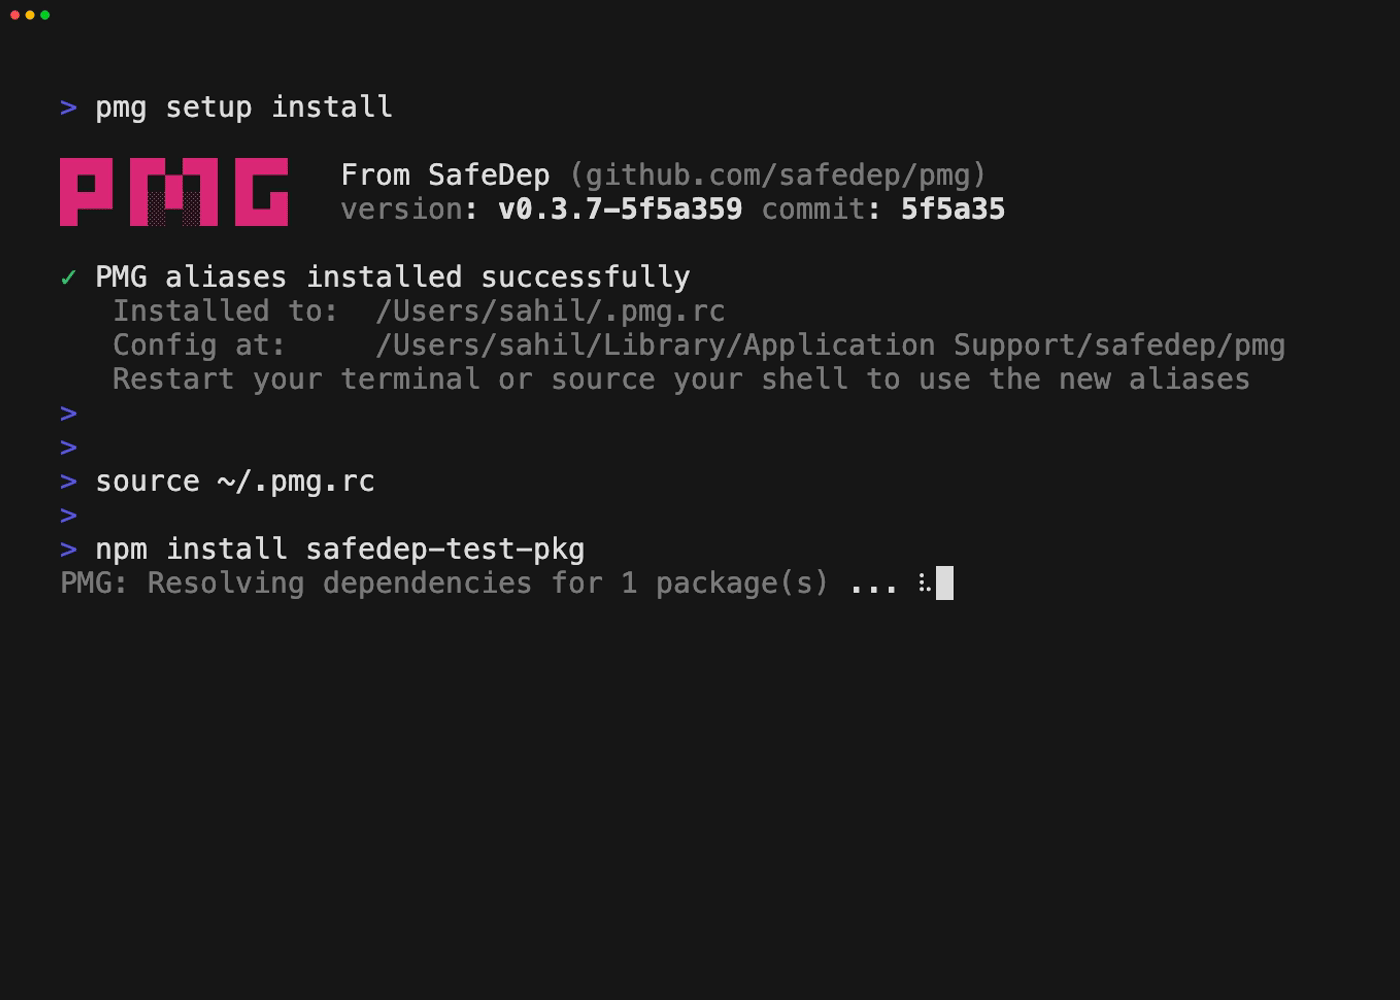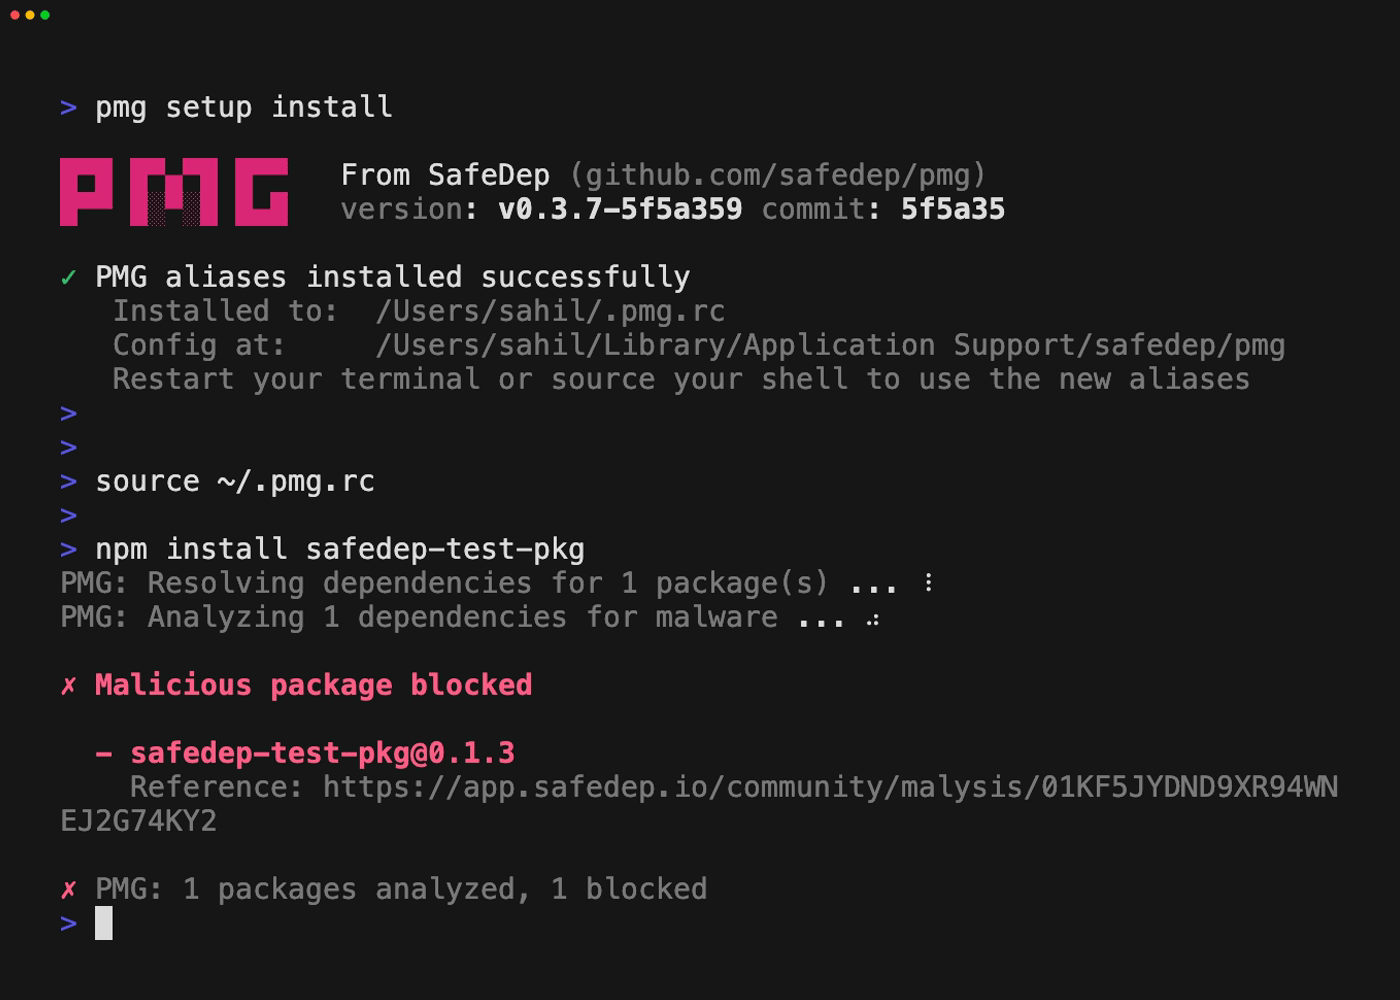
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
cloud-securitycontainer-securitydevsecops+6
5137 days ago
safedep/pmgPMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
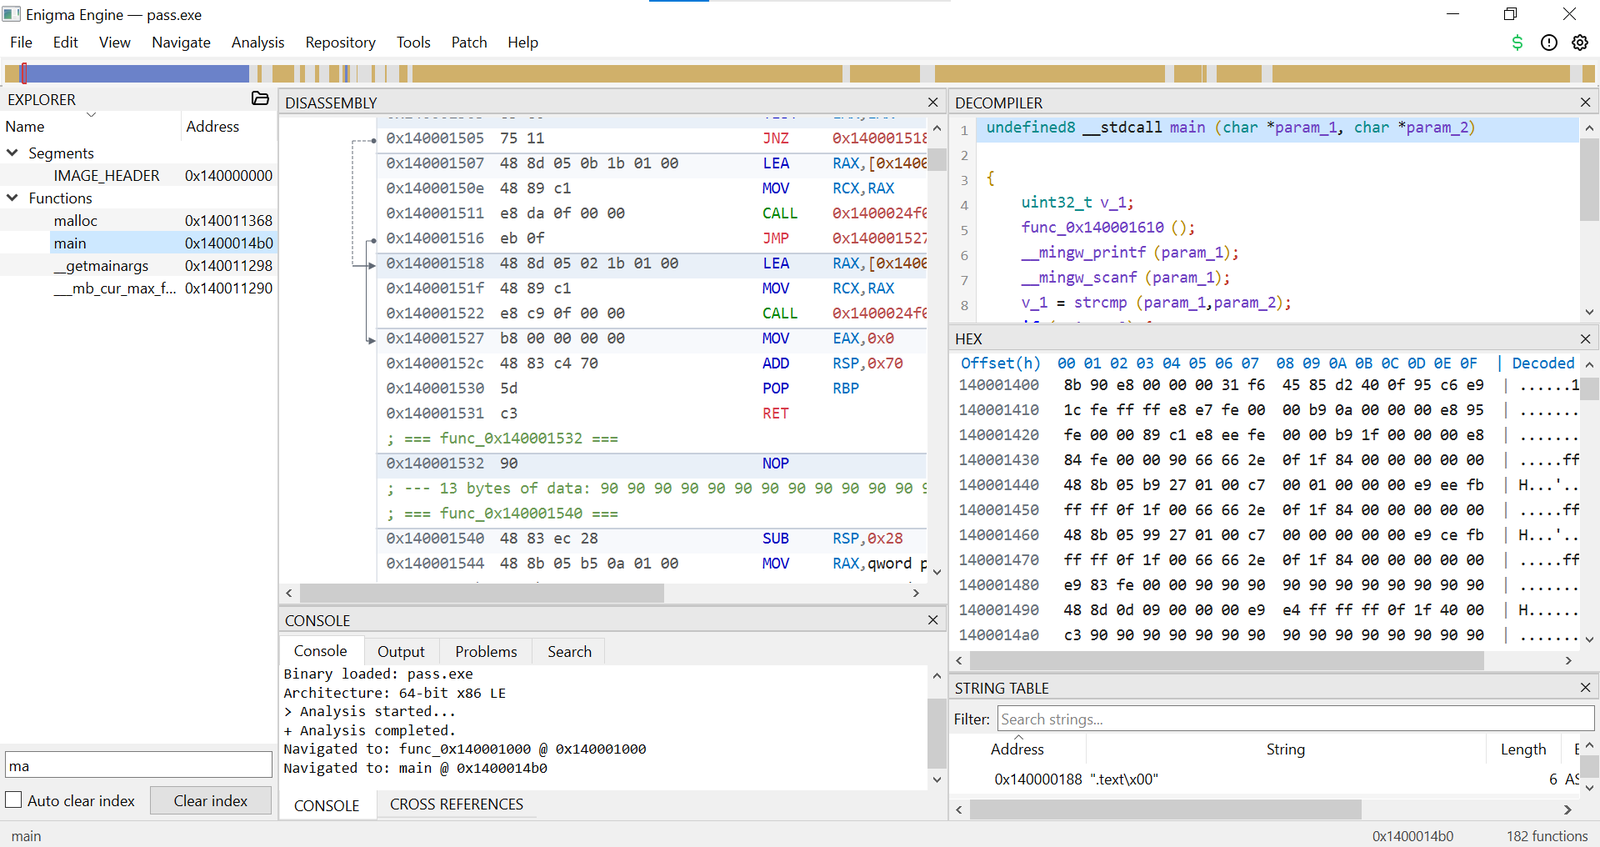 bunnybuzz/enigma
Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
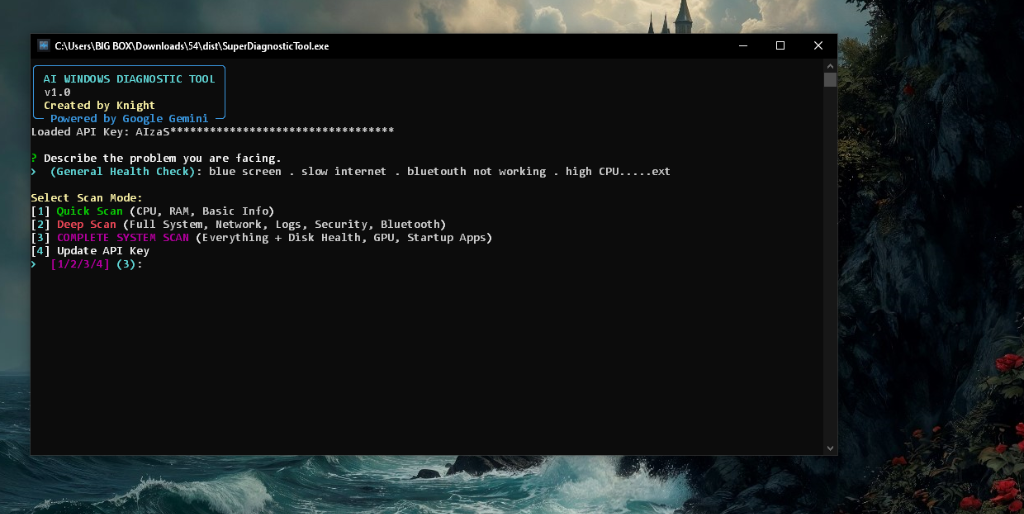 guettaf-hossam/superdiagnostictool
AI-powered Windows diagnostic & auto-repair tool using Google Gemini. Detect crashes, optimize performance, scan for malware, and generate PowerShell…
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…
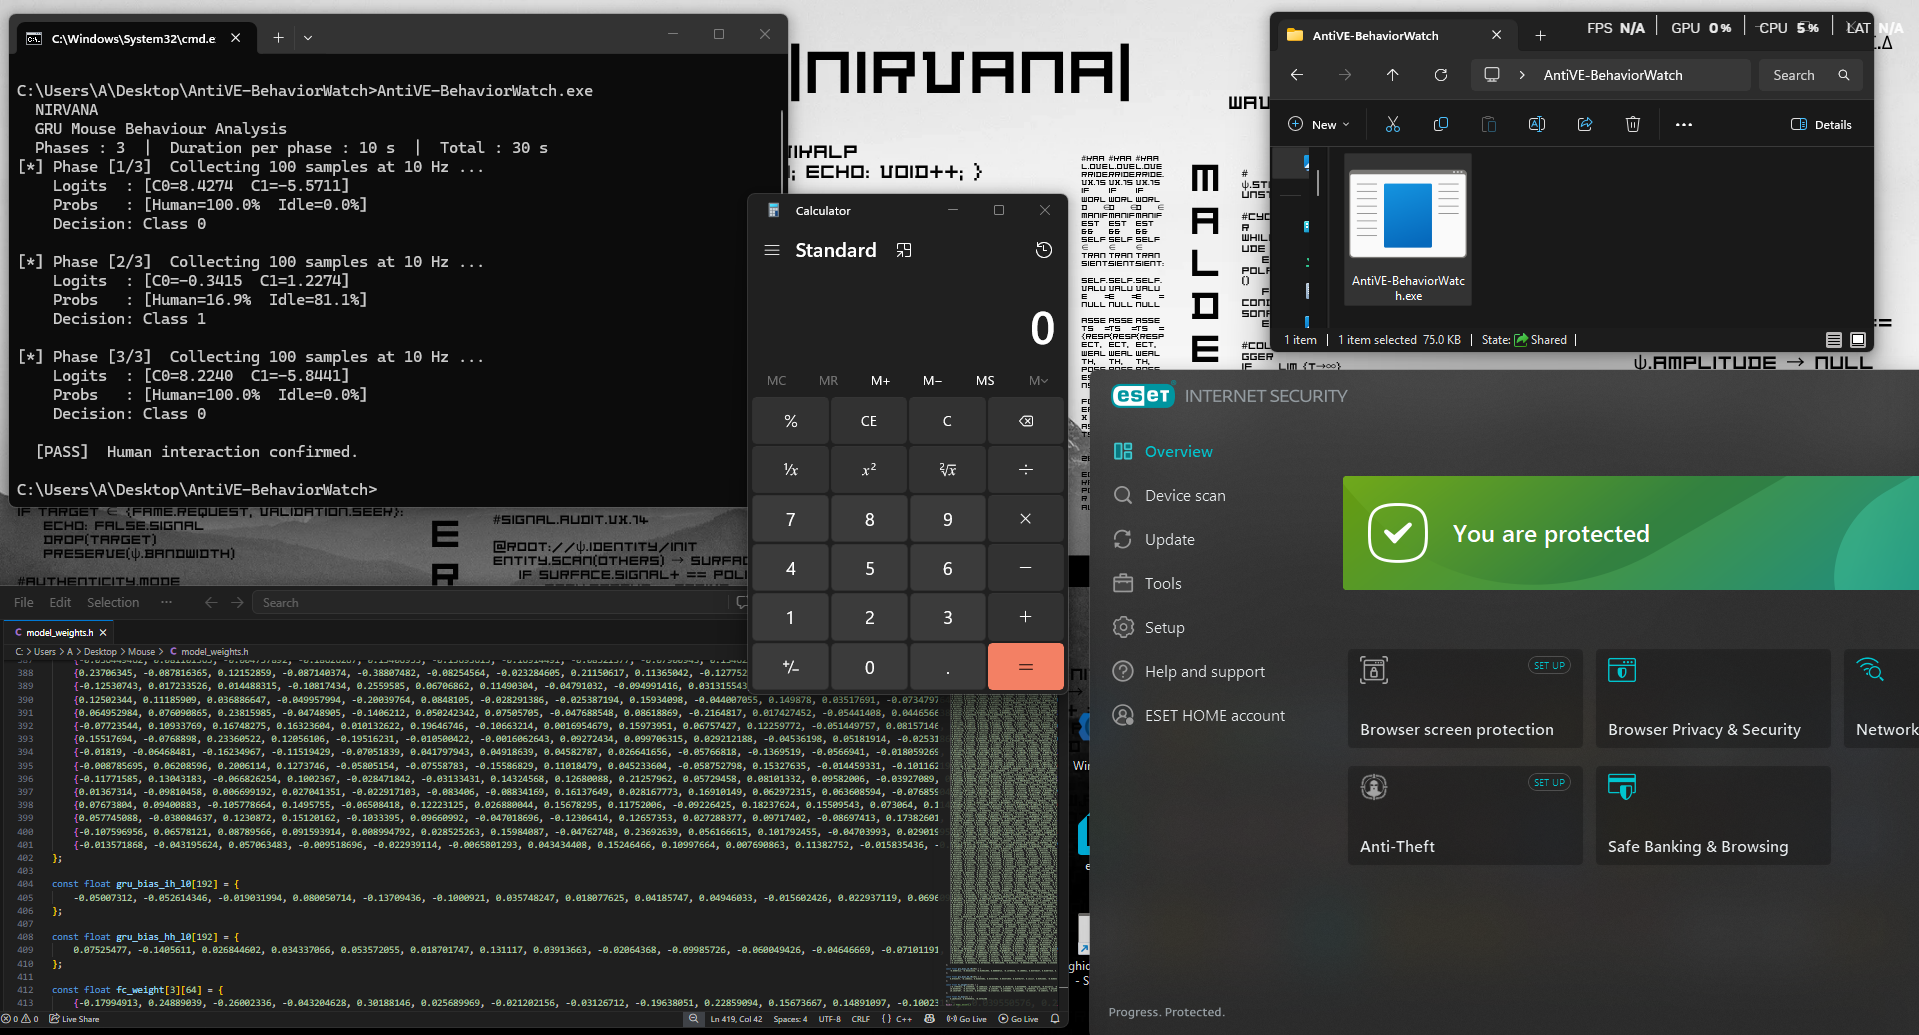 nirvanaon/antive-behaviorwatch
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 bedrock-safeguard/gentlemen-decryptor
First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 ichhyak22/eternalblue-exploit-demonstration-ms17-010
Cybersecurity lab demonstrating exploitation of CVE-2017-0144 (EternalBlue) using Metasploit against a vulnerable Windows 7 VM, achieving…
 dannic145/eternalblue-exploit-demonstration
Educational lab demonstrating EternalBlue (MS17-010) exploitation against Windows 7 using Metasploit, including post-exploitation, WannaCry…
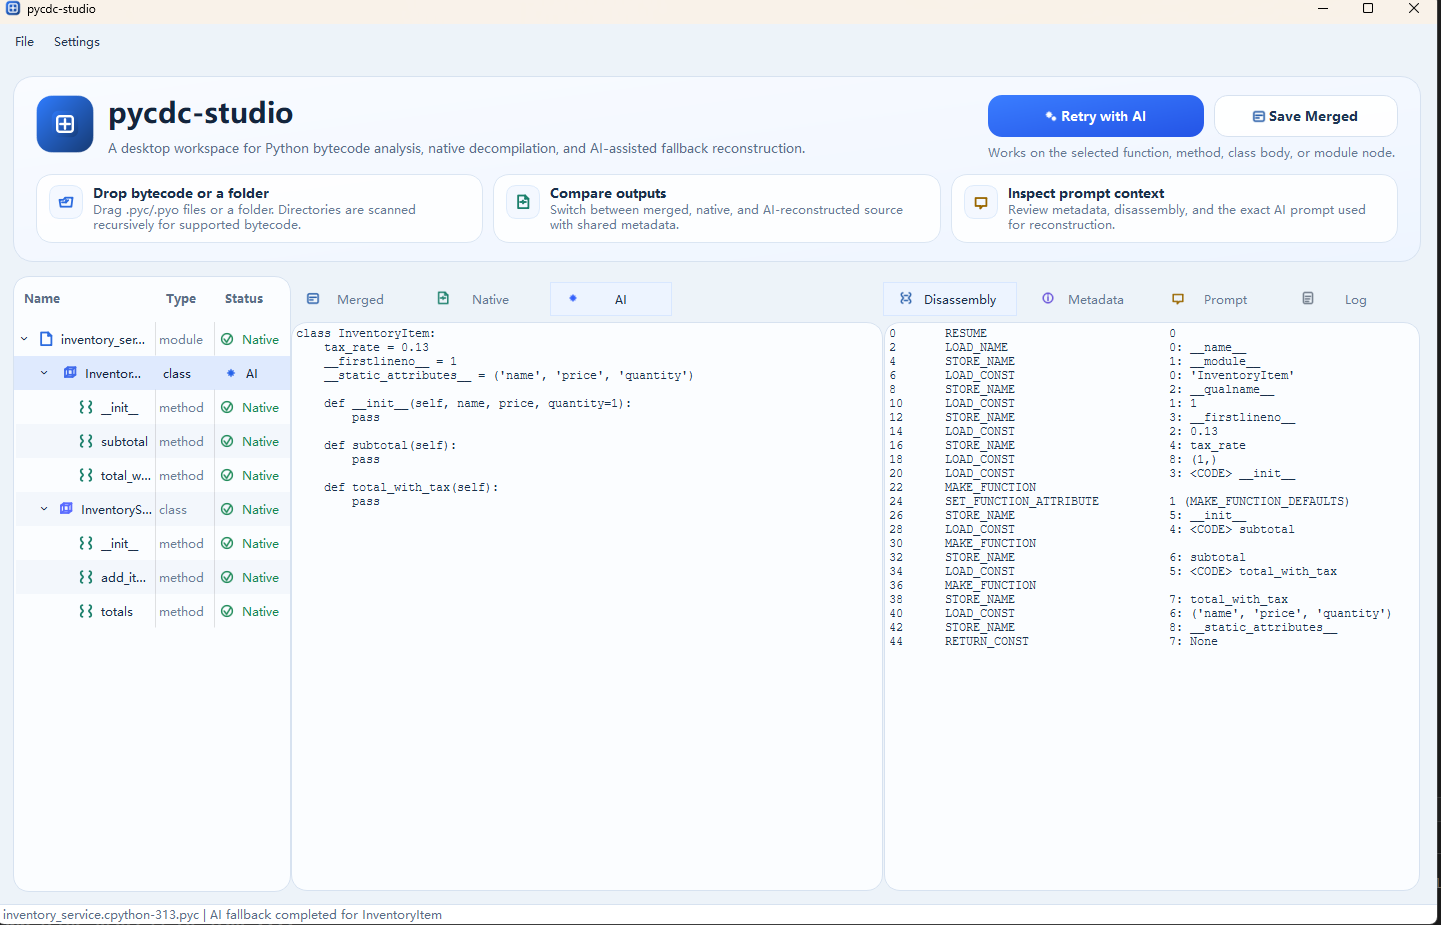 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
 justjeff211/conti-ransomware-writeup
Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…
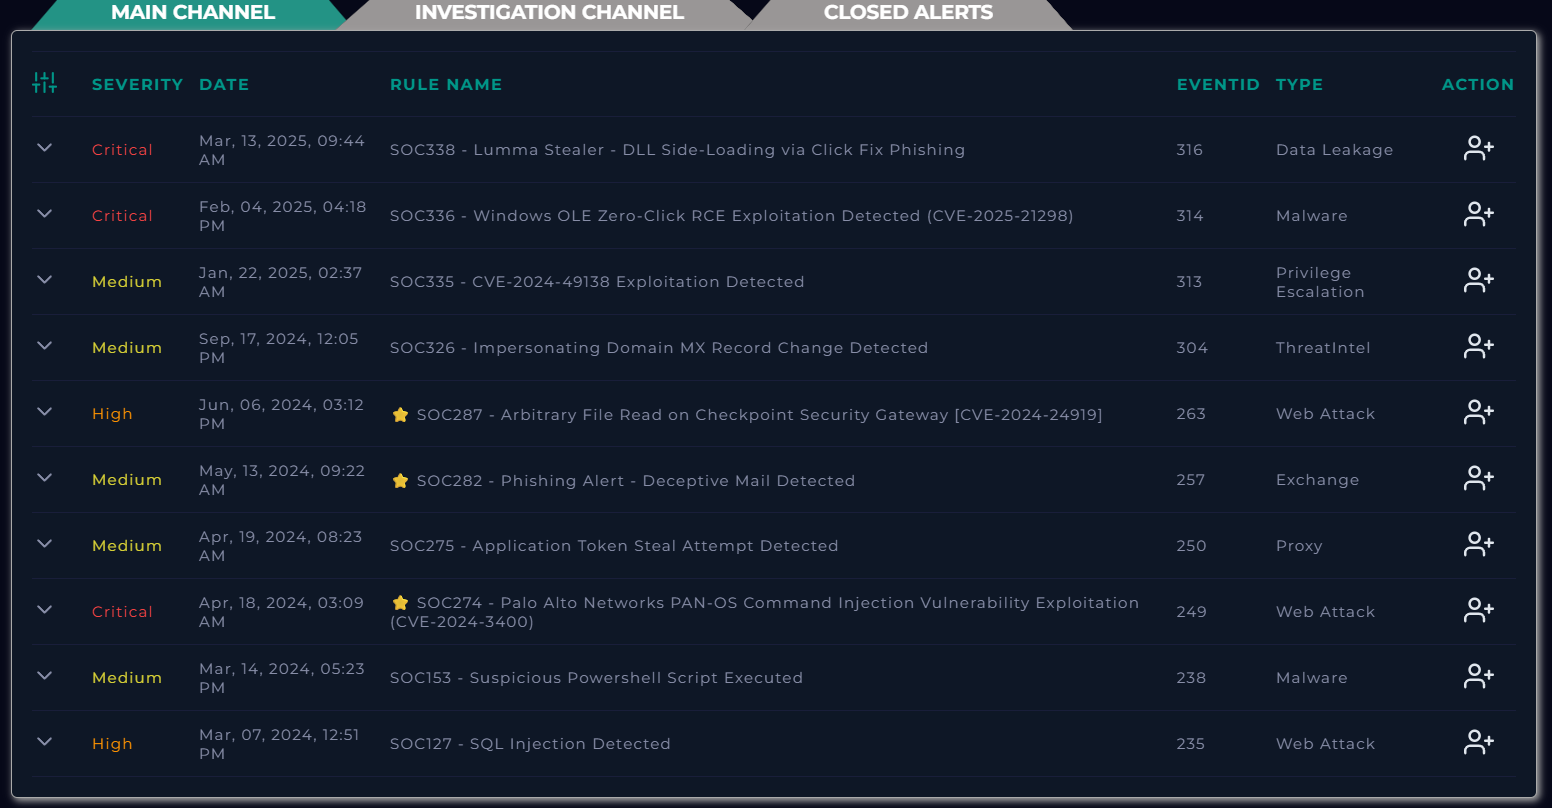 tarunbharathe/zero-click-rce-incident-response-cve-2025-21298
Technical investigation and host containment of a Critical-severity Zero-Click RCE exploit (CVE-2025-21298) using EDR telemetry and static malware…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
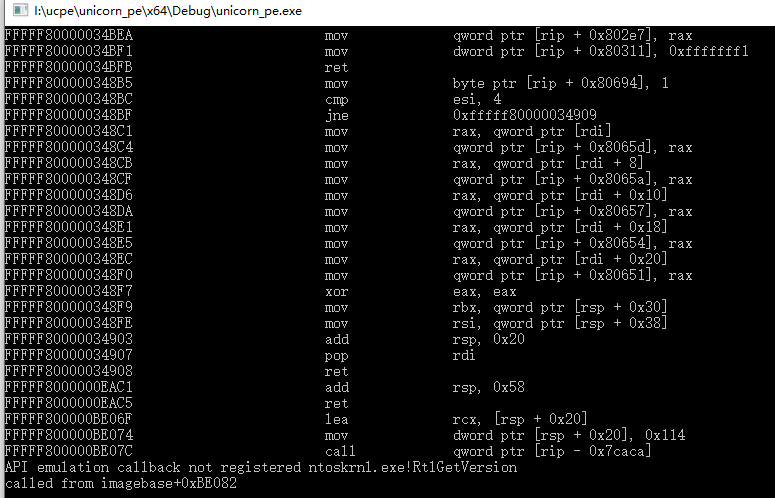 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.
 bbaboha/cve-2025-65318-and-cve-2025-65319
Insecure attachment handling when using Canary Mail or Blue mail
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex