

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 aikidosec/safe-chain
Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.
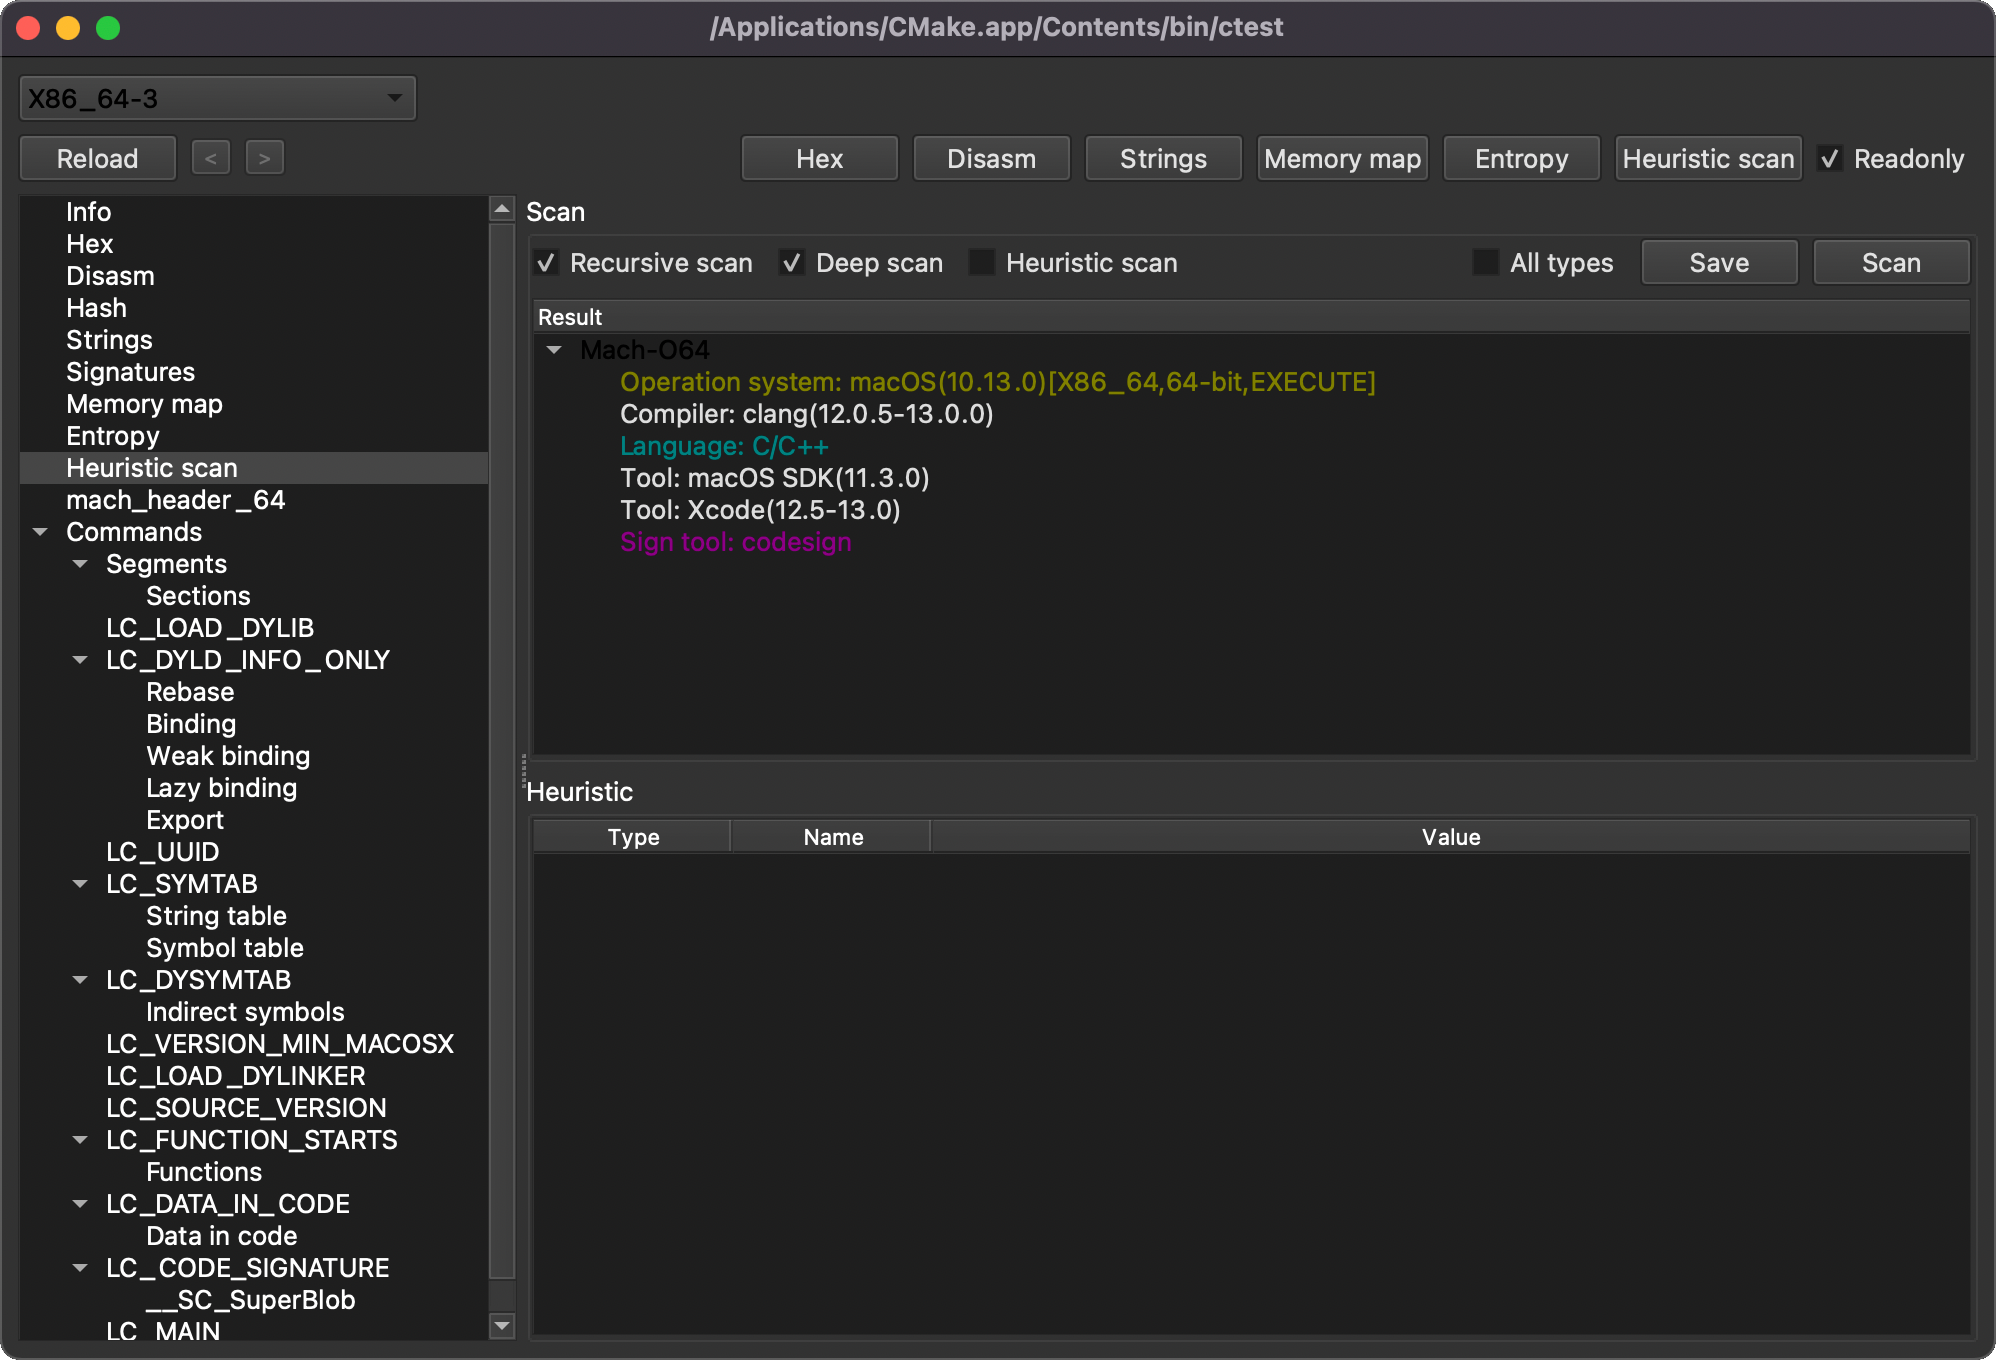 horsicq/xmachoviewer
XMachOViewer is a Mach-O viewer for Windows, Linux and MacOS
 blackorbird/apt_report
Interesting APT Report Collection And Some Special IOCs
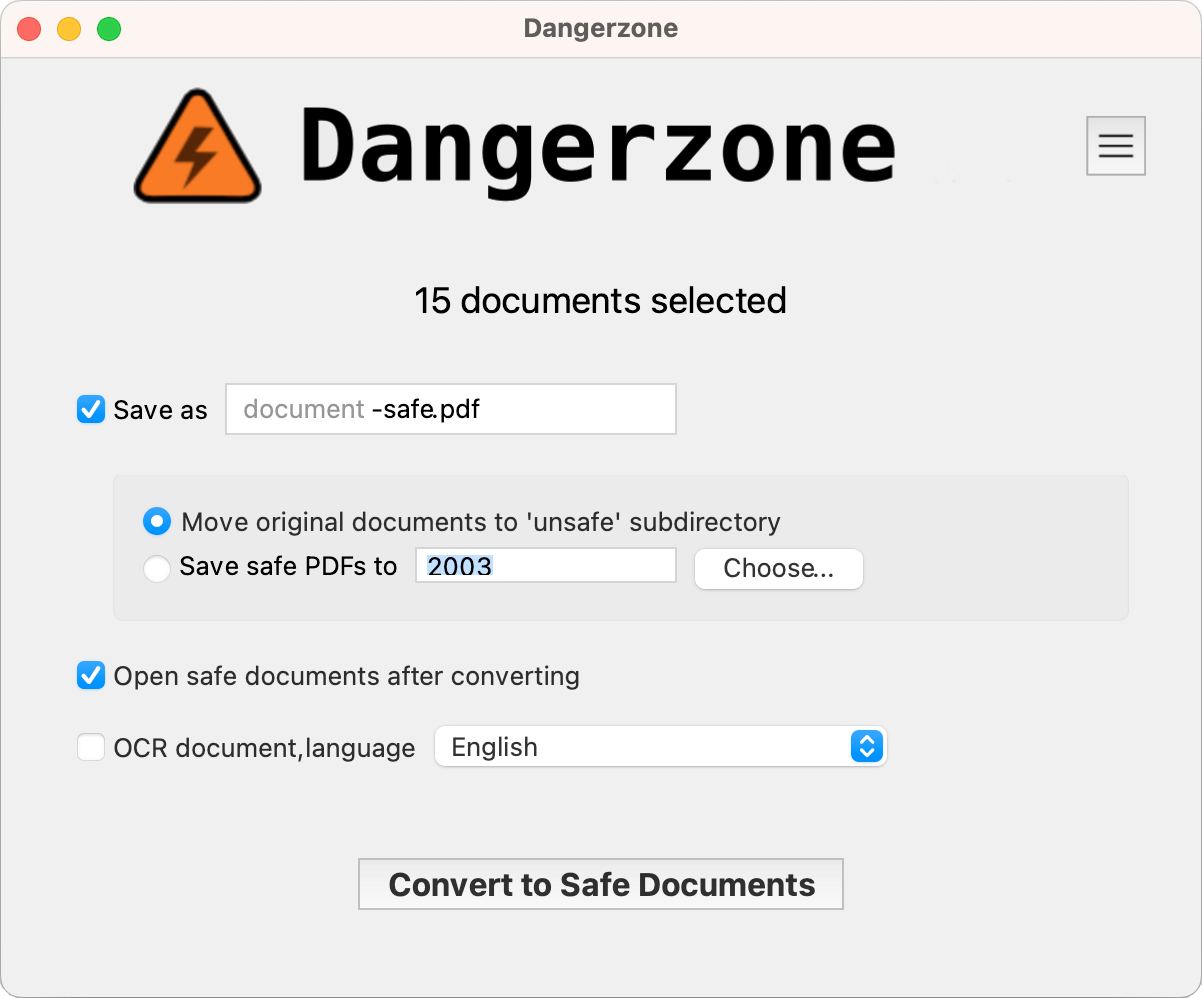 freedomofpress/dangerzone
Take potentially dangerous PDFs, office documents, or images and convert them to safe PDFs
 tjnel/certgraveyard_yara
Automated YARA rule generation from the Cert Central compromised certificate database.
 cristianzsh/freki
Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 nemo22/retrokit
Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…