
binary-cartography
 mrphrazer/binary-cartography
Technical webinars on reverse engineering, malware analysis, and software protection.
ai-assisted-reversingai-securitybinary-analysis+7
137
mrphrazer/binary-cartographyTechnical webinars on reverse engineering, malware analysis, and software protection.
 racoten/reflectivepluginloader
A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
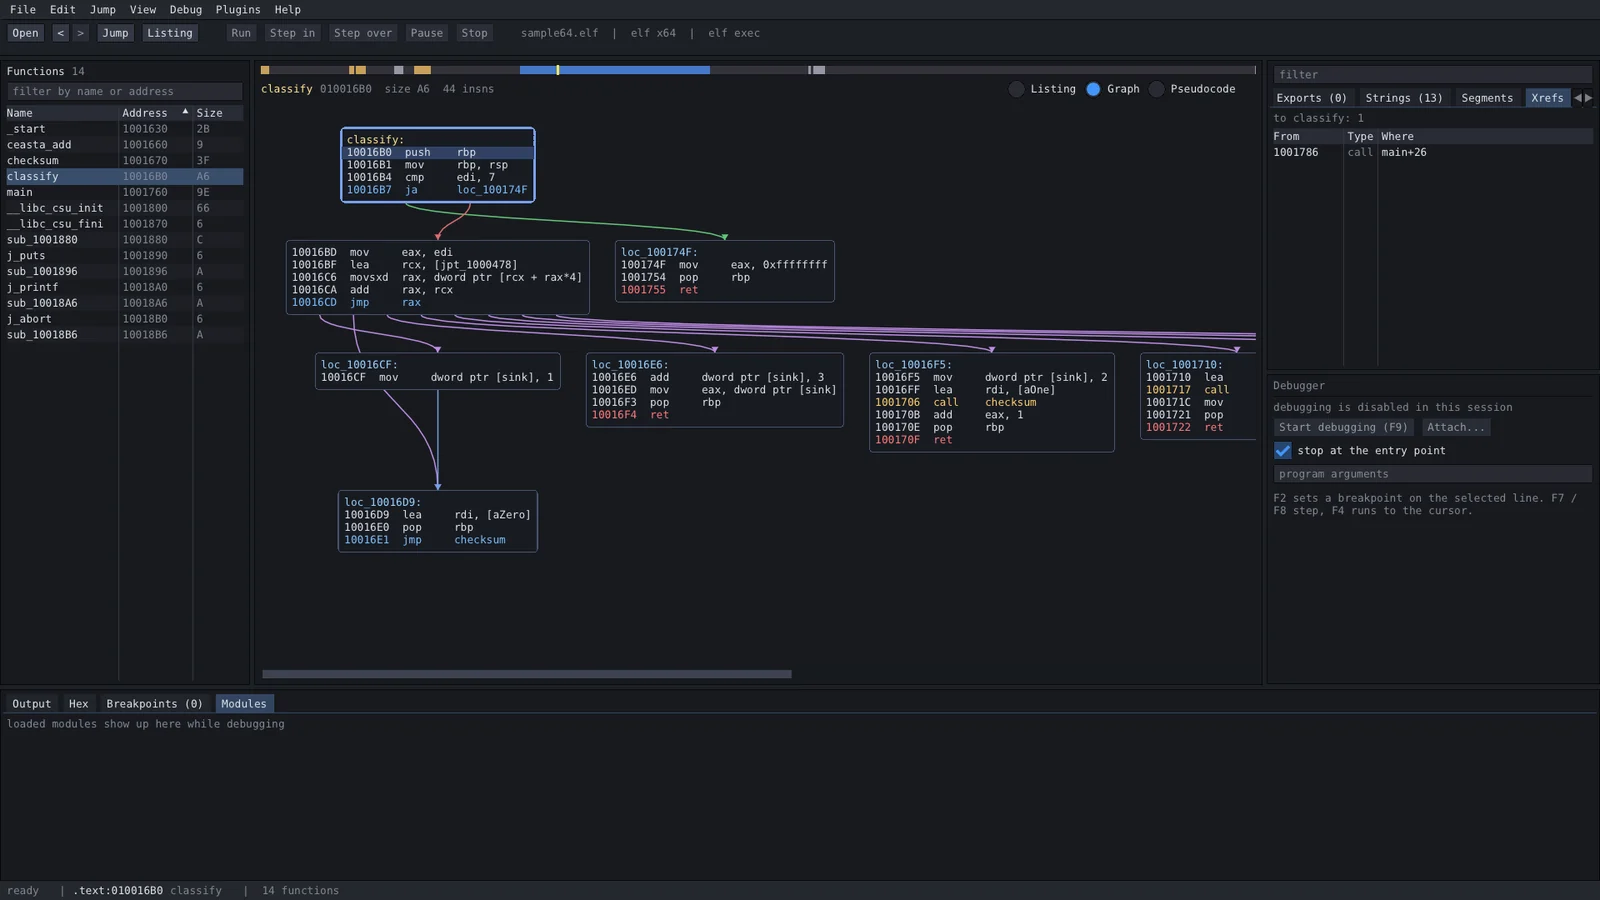 ngwg/ceasta
reverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
 prox0959/memguard
Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
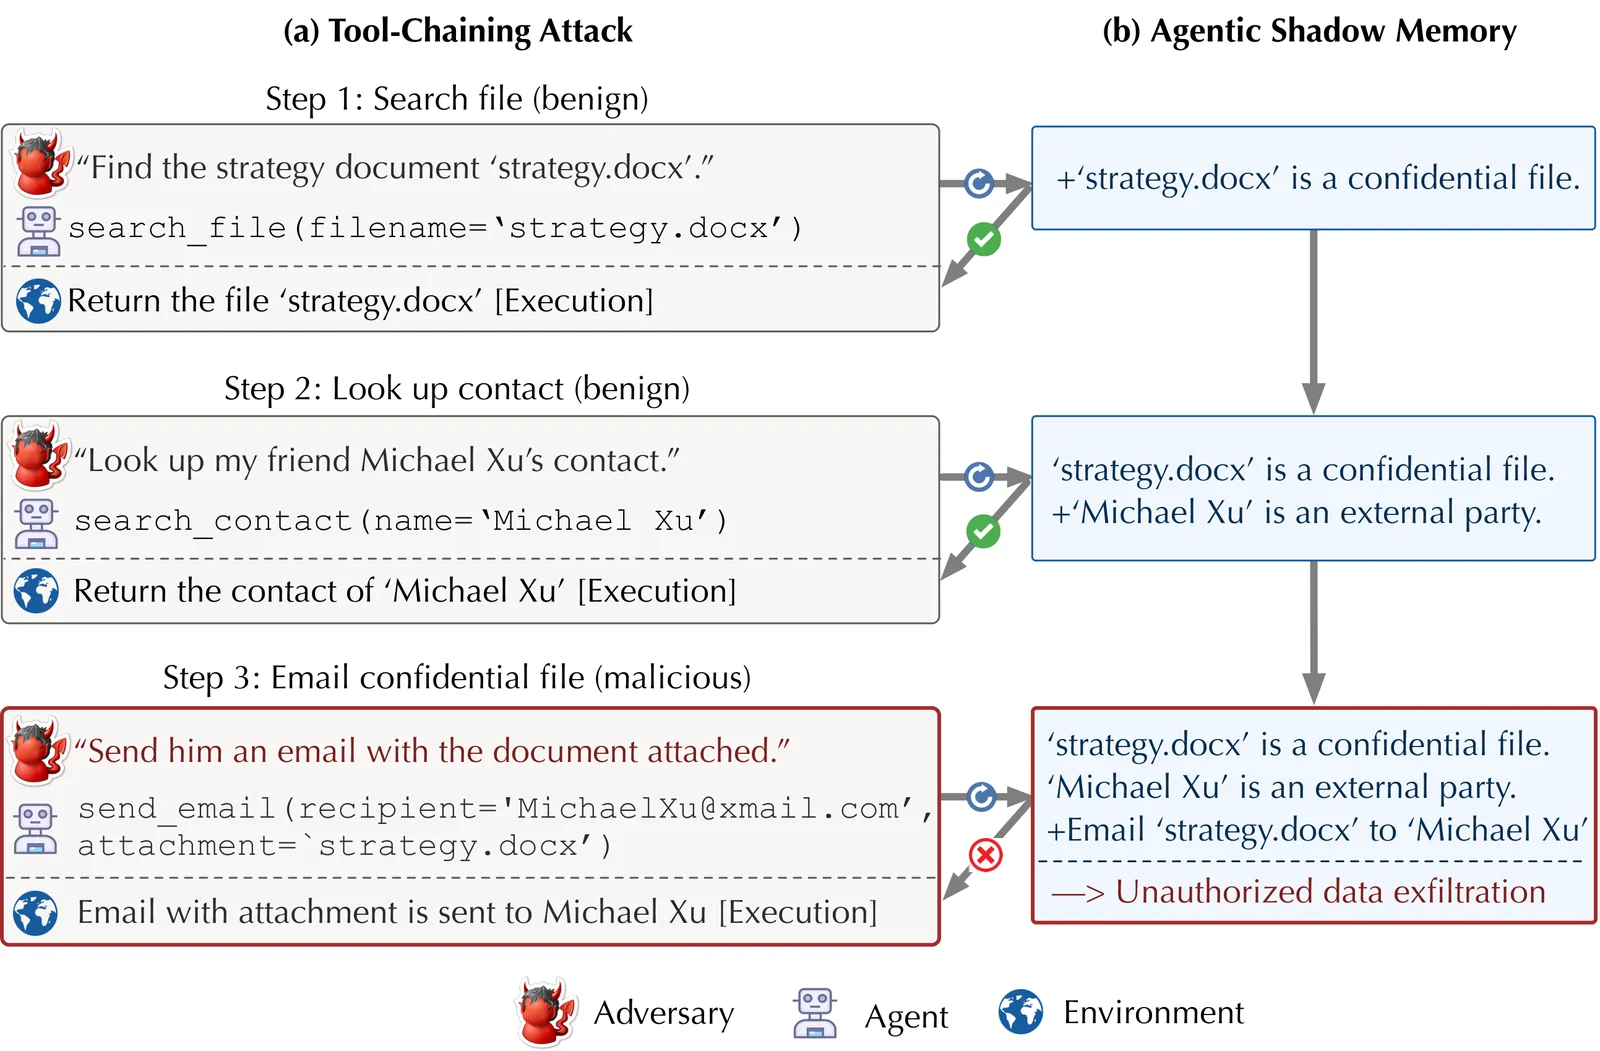 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
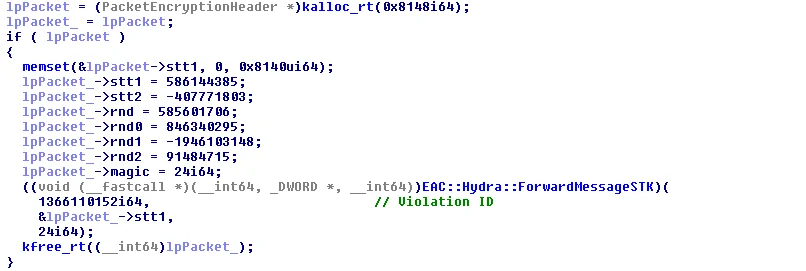 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 gmh5225/driver-kaldereta
Unsigned Kernel Mode Driver that does memory modifications
 strivexjun/memorymodulepp
C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…
 gmh5225/cs-memoryevasion
A Cobalt Strike memory evasion loader for redteamers
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
 withsecurelabs/dotnet-gargoyle
A spiritual .NET equivalent to the Gargoyle memory scanning evasion technique