Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
402 results
veneficus-implant-public preview

veneficus-implant-public

GitHubabraxas/veneficus-implant-public

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…

command-and-controldata-exfiltrationexploitation+9

1 month ago
veneficus preview

veneficus

GitHubabraxas/veneficus

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

command-and-controldata-exfiltrationids-ips-evasion+8
21 month ago
SigLens preview

SigLens

GitHubst0rn/siglens

Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…

binary-analysisdefensive-toolsdigital-forensics+7
33 days ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).

ai-assisted-reversingbinary-analysisbinary-exploitation+7
21 days ago
NativePe preview

NativePe

GitHubhabanada/nativepe

Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…

binary-analysisbinary-exploitationdynamic-analysis-sandboxing+5
14 days ago
quipu preview

quipu

GitHubcorelight/quipu

A desktop workbench for writing, validating, compiling, and testing YARA rules.

code-analysisdefensive-toolsdigital-forensics+6
3 days ago
injection-2 preview

injection-2

GitHubgmh5225/injection-2

Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…

curated-resourcesdefensive-toolsexploitation+4
73 years ago
SOC335---CVE-2024-49138-Exploitation-Detected preview

SOC335---CVE-2024-49138-Exploitation-Detected

GitHubfabianch20/soc335---cve-2024-49138-exploitation-detected

SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…

digital-forensicseducationincident-response+7
19 days ago
cortex preview

cortex

GitHubpdb333/cortex

A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.

ai-assisted-reversingai-securitybinary-analysis+7
54 days ago
KernelFlirt preview

KernelFlirt

GitHubakatorich/kernelflirt

Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…

ai-assisted-reversingai-securityanti-bot+9
324 months ago
HookTools preview

HookTools

GitHubgmh5225/hooktools

Basic injectable for analyzing the behavior of evasive malware

binary-analysisdebuggersdefensive-tools+3
2 years ago
IAT-Hook preview

IAT-Hook

GitHubgmh5225/iat-hook

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…

binary-exploitationcode-analysismalware-analysis+4
4 years ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.

binary-exploitationdefensive-toolseducation+7
4720 days ago
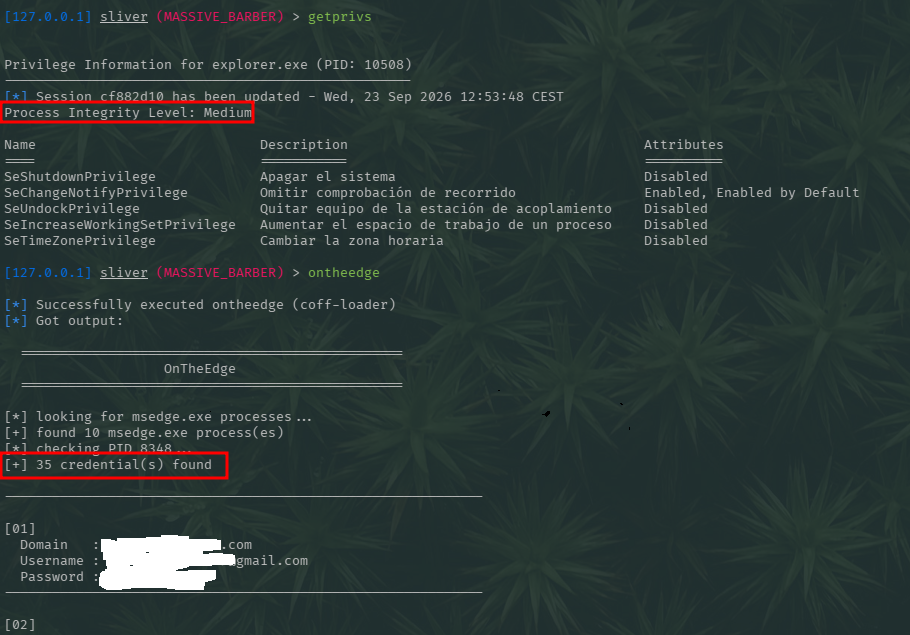
OnTheEdge preview

OnTheEdge

GitHubjssngc/ontheedge

Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…

command-and-controldata-exfiltrationmalware-analysis+4
1112 days ago
disrobe preview

disrobe

GitHub1-3-7/disrobe

Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…

android-securitybinary-analysisfirmware-analysis+4
1413 days ago
javajive preview

javajive

GitHubyaklang/javajive

Pure-Go Java Decompiler and Serialization Operator

binary-analysiscode-analysismalware-analysis+4
1915 days ago
ceasta preview

ceasta

GitHubngwg/ceasta

disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…

ai-assisted-reversingbinary-analysisbinary-exploitation+6
1389 days ago
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering

anti-botbinary-analysisdefensive-tools+4
33313 days ago
Previous12…23Next