
disrobe
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
android-securitybinary-analysisfirmware-analysis+4
113
1-3-7/disrobeRust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
 osmancanvural/cve-2026-21436
Proof-of-concept exploit for CVE-2026-21436, demonstrating path traversal in Solus OS eopkg package manager allowing arbitrary file write during…
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…
 maddiestone/conpresentations
Slide decks from my conference presentations
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 amnestytech/inside-pegasus
A curated set of NSO Group internal documents, product materials and sworn testimony that entered the public record in WhatsApp Inc. and Meta…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
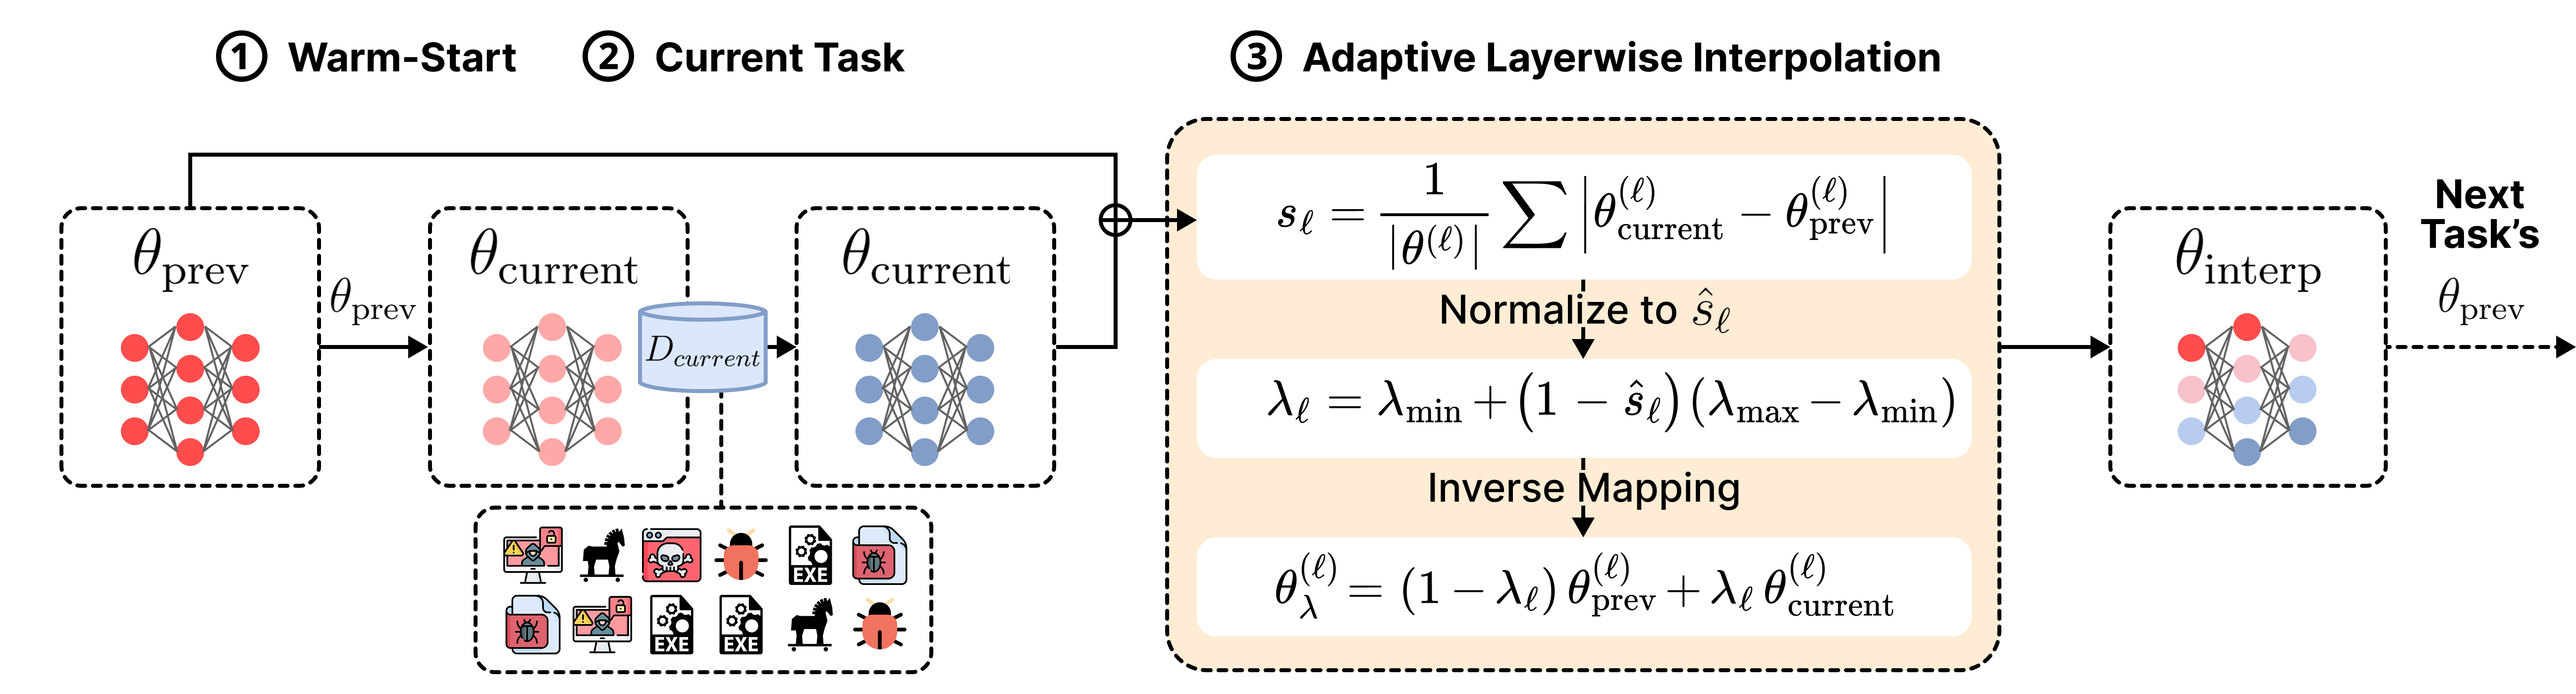 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 santoku/santoku-linux
Linux Distro for Mobile Security, Malware Analysis, and Forensics
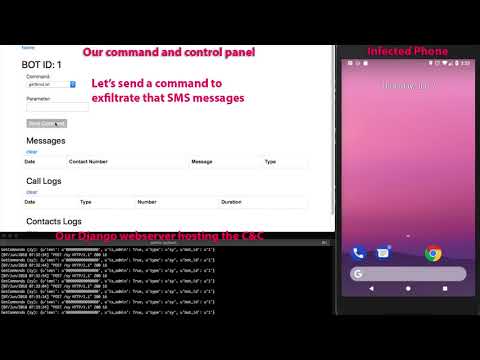 bizdak/silverboxcc
Reverse engineered android malware, and this is a C&C server for it
 sensepost/snoopy
Snoopy: A distributed tracking and data interception framework