awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

A repository to share publicly available Velociraptor detection content

Tools for hunting for threats.

Strelka Web UI for File Submission and Analysis

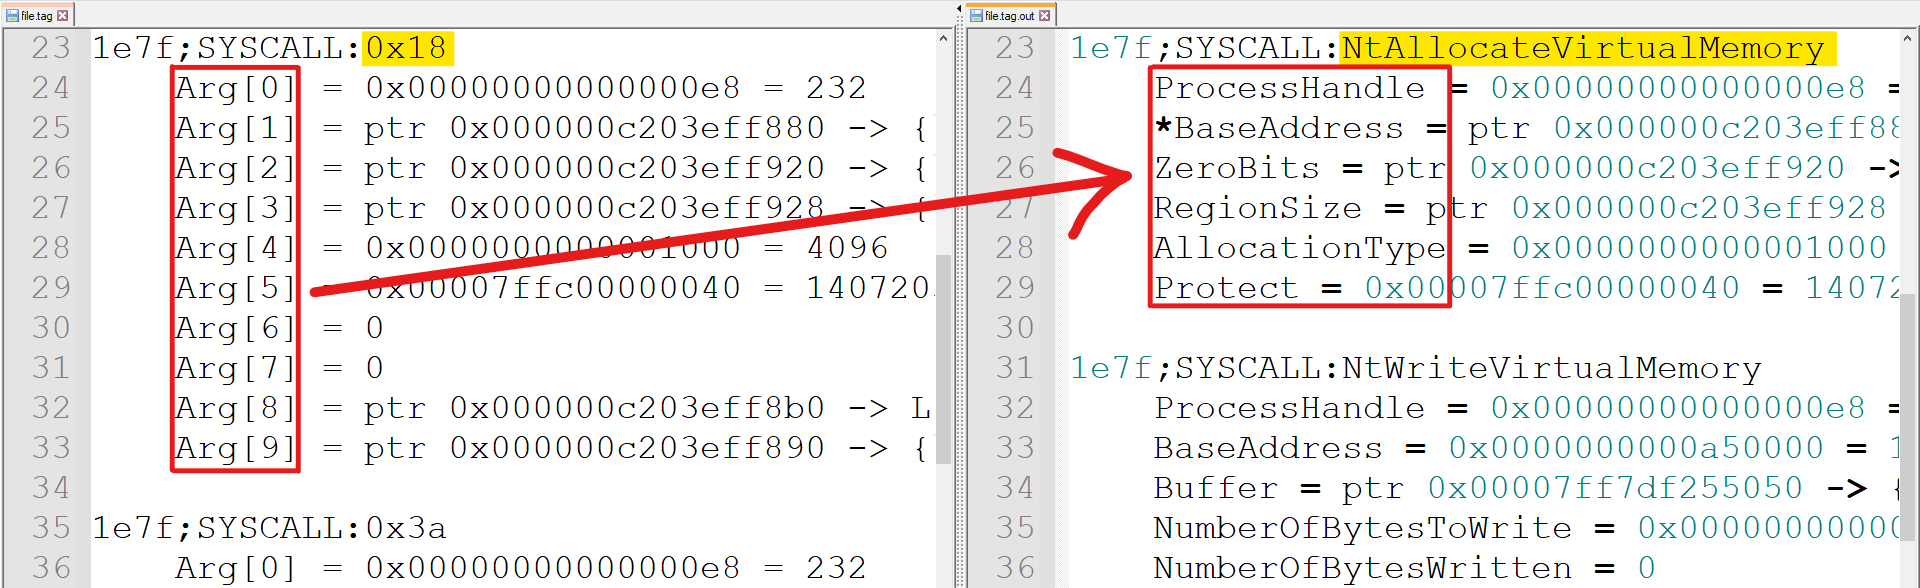
A post-processing script for TinyTracer

A ProcessMonitor visualization application written in rust.

Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…

IOC feed and analysis toolkit for EITest campaigns, featuring C2 data decryption, victim payload decoding, and sinkhole log processing for threat…

Documented incident response case for CVE-2024-49138 exploitation, featuring log analysis, hash validation, C2 detection, and containment procedures…

Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

Conducted a full SOC investigation into a Conti ransomware compromise of an Exchange server using Splunk 8.2.2. Analysed 28,145 events across Windows…

SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough

Use after free in Windows Common Log File System Driver allows an authorized attacker to elevate privileges locally.

Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…

Java-based Bluetooth honeypot that captures and stores malware from BlueBugging and BlueSnarfing attacks, with a GUI for monitoring and log analysis.

Drltrace is a library calls tracer for Windows and Linux applications.