
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
298 results
injection-2 preview

injection-2

GitHubgmh5225/injection-2

Curated collection of Windows process injection techniques, linking write-ups on Conhost, PROPagate, KernelCallbackTable, KnownDlls poisoning and…
curated-resourcesdefensive-toolsexploitation+4
7
3 years ago
honeypot-stuff preview

honeypot-stuff

GitHubjeeberrr/honeypot-stuff

Stuff like malware analysis reports on things I captured from my honeypot

curated-resourcesforensicsincident-response+3
5 days ago
badbox-h713-projector preview

badbox-h713-projector

GitHubflorentineprinzessinzusachsen/badbox-h713-projector

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…

android-securitydigital-forensicsembedded-systems-security+8
17 days ago
ablation preview

ablation

GitHubablation-tool/ablation

Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
ai-assisted-reversingandroid-securitybinary-analysis+7
666h 53m ago
binary-cartography preview

binary-cartography

GitHubmrphrazer/binary-cartography

Technical webinars on reverse engineering, malware analysis, and software protection.
ai-assisted-reversingai-securitybinary-analysis+7
14310 days ago
polychrome-rs preview

polychrome-rs

GitHubdovelus/polychrome-rs

A PoC on how to use a Compute Shader as Payload

defensive-toolsencryption-decryption-toolsexploitation+5
712 days ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

android-securitycryptographydynamic-analysis-sandboxing+8
1026 days ago
disrobe preview

disrobe

GitHub1-3-7/disrobe

Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…

android-securitybinary-analysisfirmware-analysis+4
1412 days ago
apk-reverse preview

apk-reverse

GitHubnewliver666/apk-reverse

Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…

android-securitybinary-analysiscode-analysis+8
3.2k10 days ago
ceasta preview

ceasta

GitHubngwg/ceasta

disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
1387 days ago
SOC335-CVE-2024-49138-Exploitation-Detected preview

SOC335-CVE-2024-49138-Exploitation-Detected

GitHubmohamedbrek/soc335-cve-2024-49138-exploitation-detected

LetsDefend SOC lab investigating CVE-2024-49138 exploitation and related malicious activity.
digital-forensicseducationincident-response+6
8 days ago
frida-stalker-NtStrace preview

frida-stalker-NtStrace

GitHubgmh5225/frida-stalker-ntstrace

frida-stalker based system call tracer on windows(x64).
binary-analysisdebuggersdynamic-analysis-sandboxing+4
33 years ago
EvilKaspersky preview

EvilKaspersky

GitHubgmh5225/evilkaspersky

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
defensive-toolsmalware-analysismemory-forensics+3
22 years ago
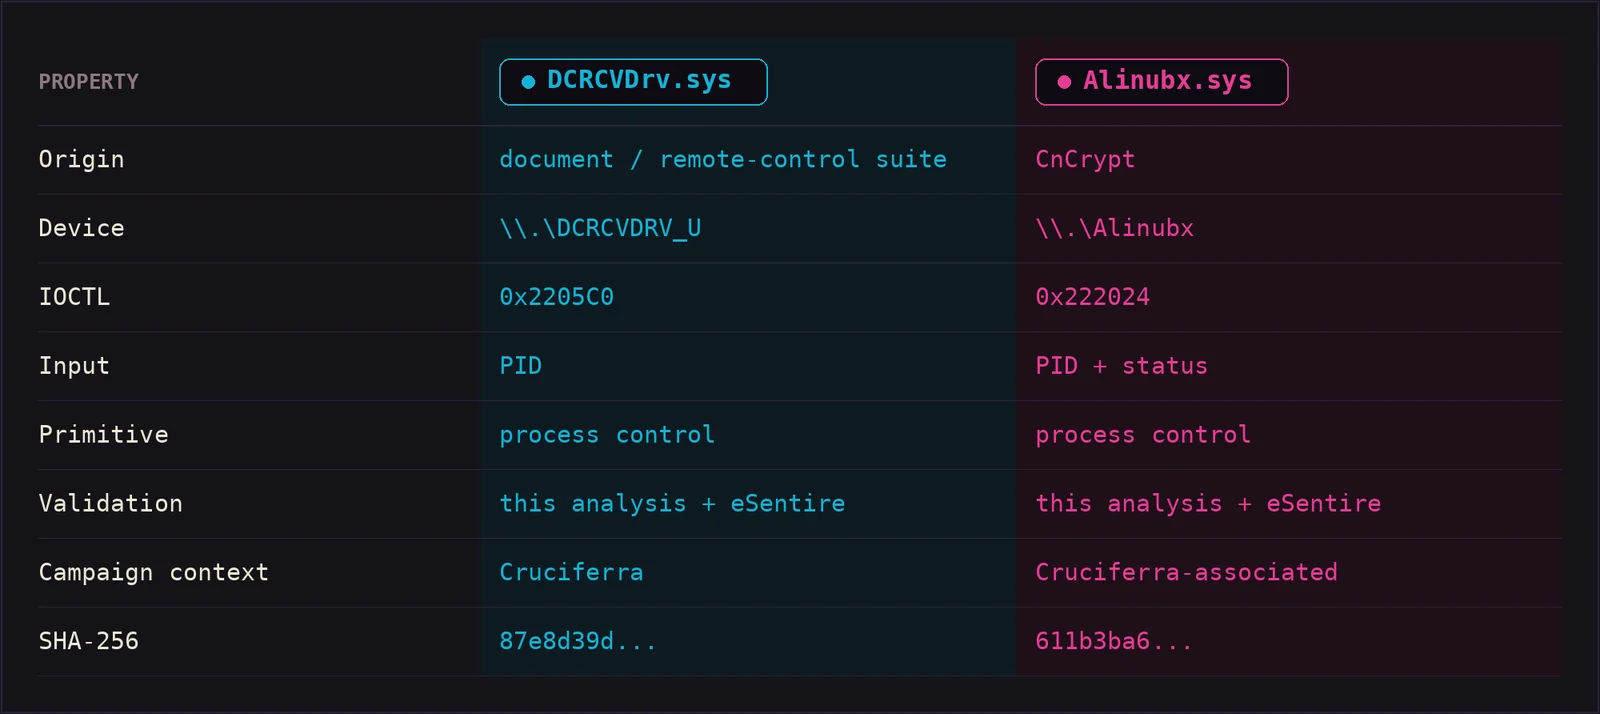
0xCr0ssCrush preview

0xCr0ssCrush

GitHubdeathshotxd/0xcr0sscrush

Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
binary-analysisdefensive-toolsexploitation+4
363 days ago
Silverseal preview

Silverseal

GitHubidov31/silverseal

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
16623 days ago
xz-utils-backdoor-case-study preview

xz-utils-backdoor-case-study

GitHubmichel-dv/xz-utils-backdoor-case-study

Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
educationincident-responsemalware-analysis+6
19 days ago
ReArk preview

ReArk

GitHublkimuk/reark

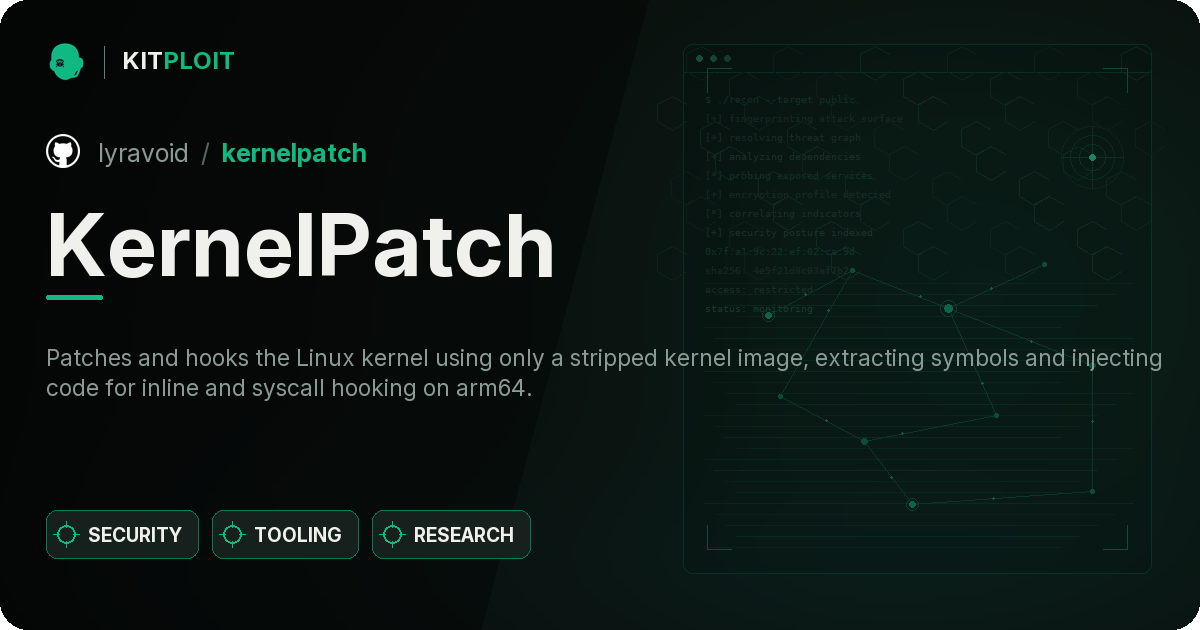
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
ai-assisted-reversingandroid-securitybinary-analysis+6
44416 days ago
KernelPatch preview

KernelPatch

GitHublyravoid/kernelpatch

Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.

android-securitybinary-analysisbinary-exploitation+6
138 days ago
Previous12…17Next