

Barzakh
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
defensive-toolsembedded-systems-securityfirmware-analysis+6
14
yasindce1998/barzakhRing -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 nmatt0/moria
IoT firmware identification and extraction
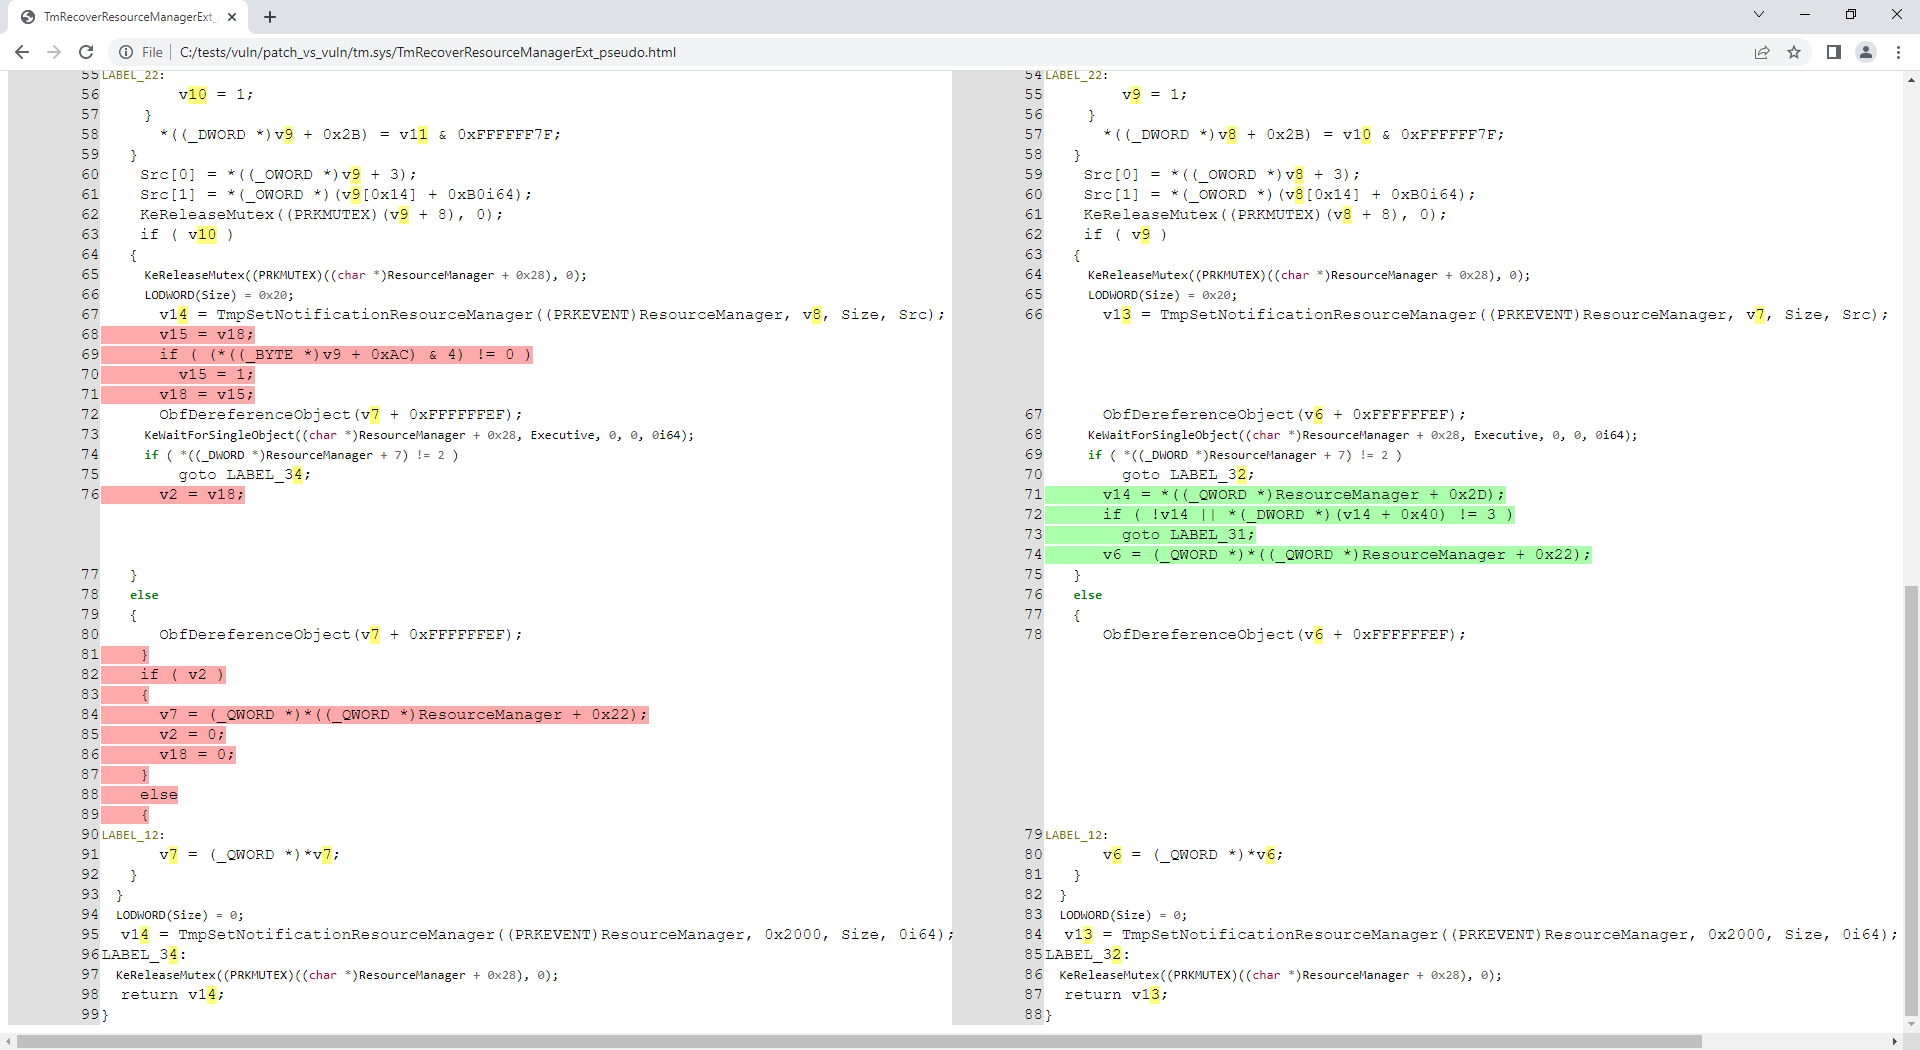
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 securityjoes/threatresearch
Python config extractors for malware families including PlugX, Remcos, templateX, and RedLine Stealer, supporting C2 configuration extraction for…
 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 pandipanda69/my-little-honeypot
Lightweight telnet honeypot for capturing IoT malware samples and identifying active command-and-control infrastructure, designed for educational…
 tpdlshdmlrkfmcla/backdoor.mirai.helloworld
backdoor.mirai.helloworld cve2018-20561, cve-2018-10562 해킹
 engrbilal992/deaddialect
A session-unique RISC-V ISA — every boot speaks a different dialect. Old binaries become invalid. Malware cannot persist.
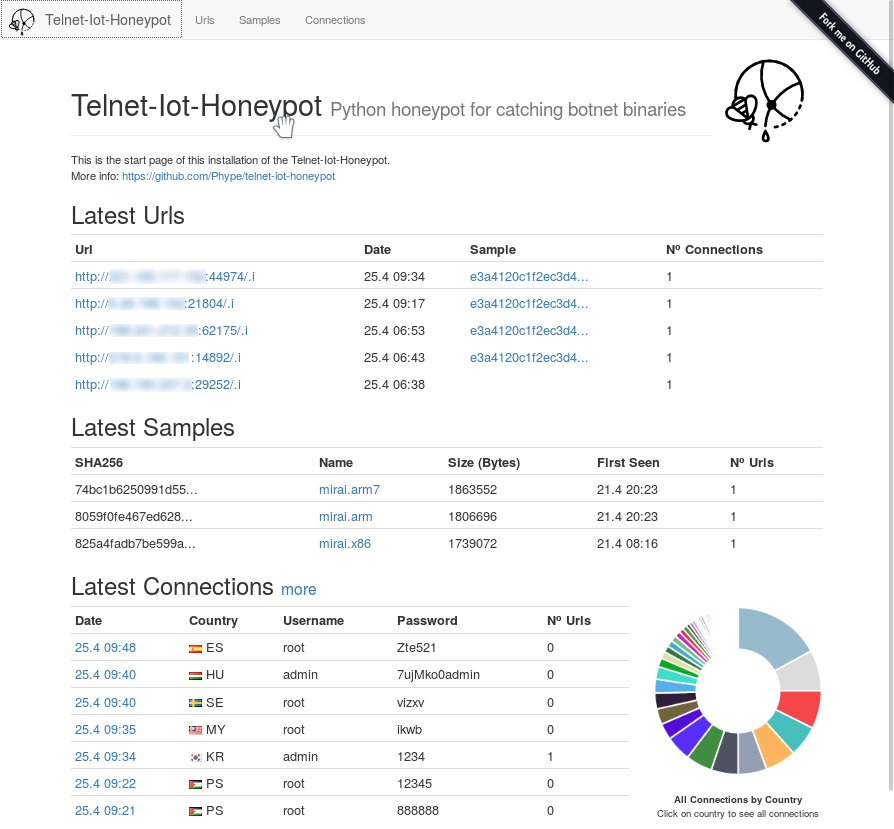 phype/telnet-iot-honeypot
Python telnet honeypot for catching botnet binaries
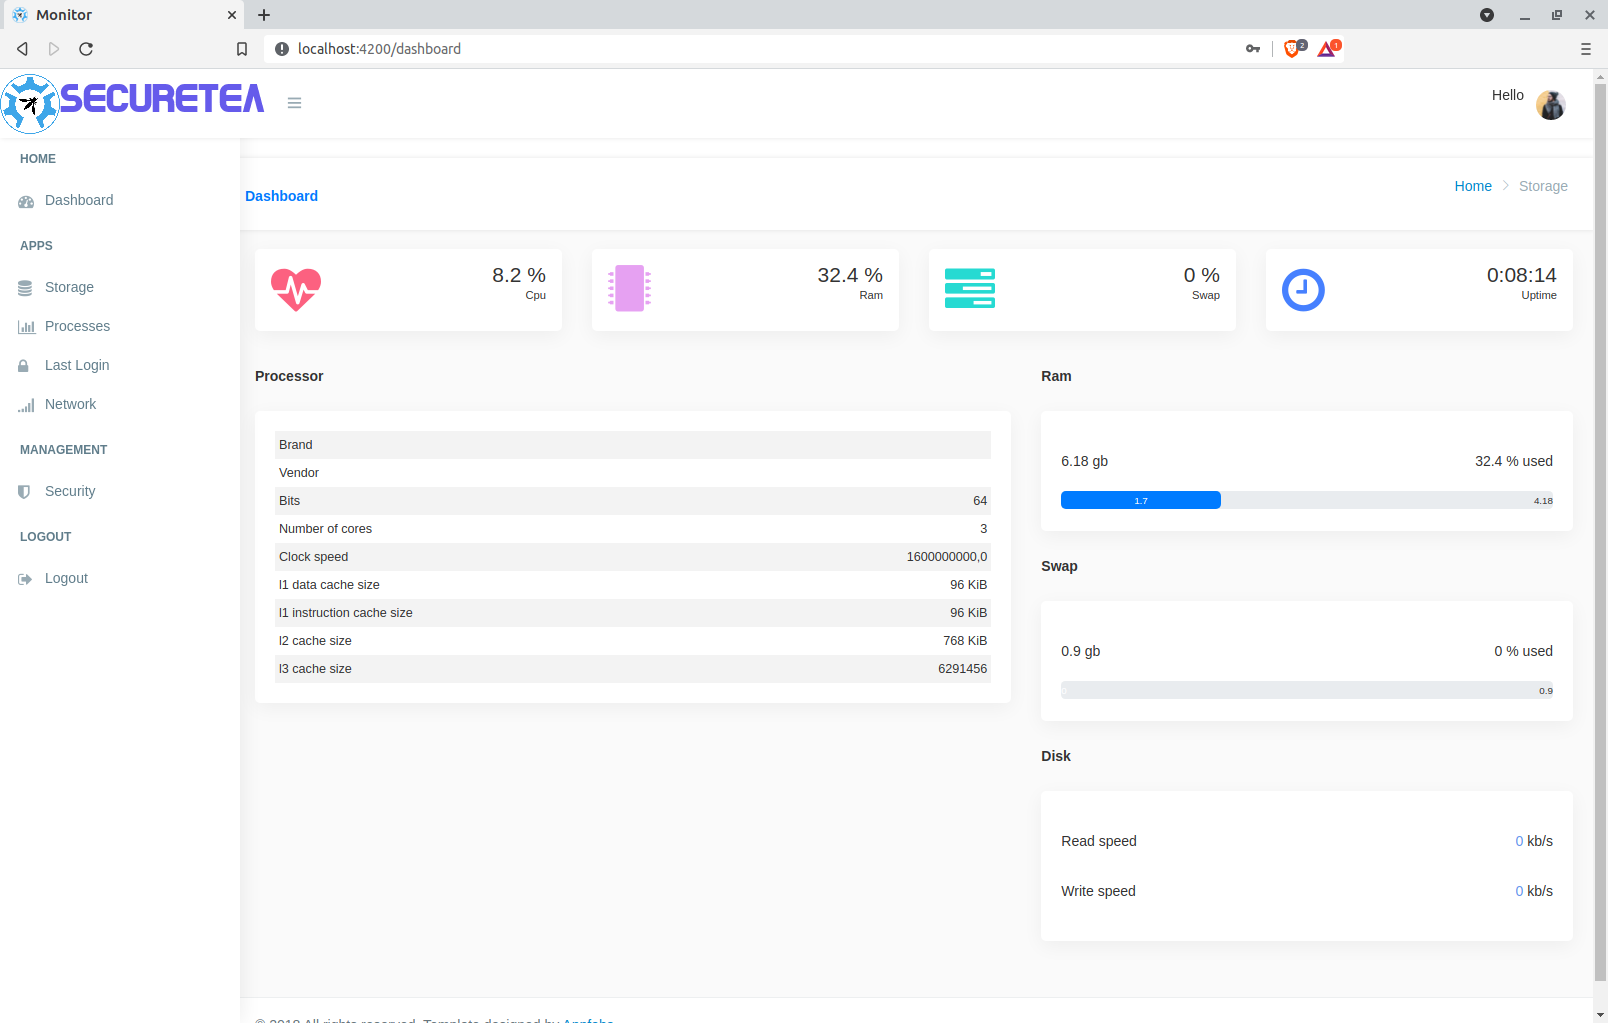 owasp/securetea-project
The OWASP SecureTea Project provides a one-stop security solution for various devices (personal computers / servers / IoT devices)
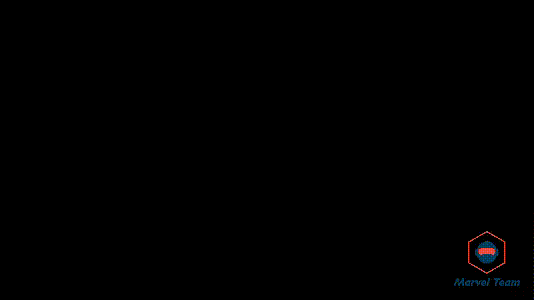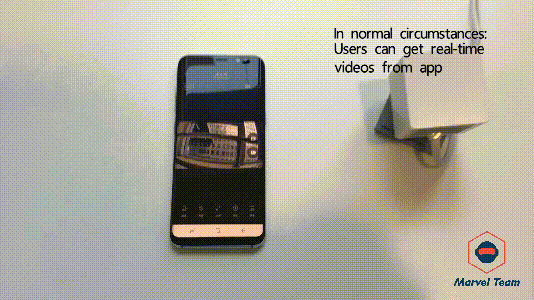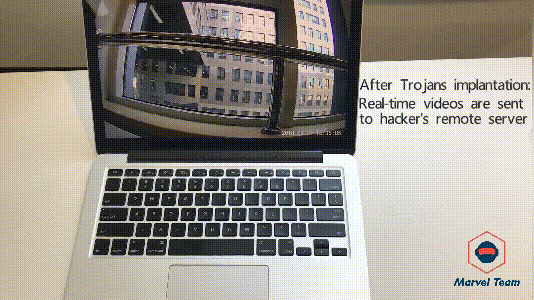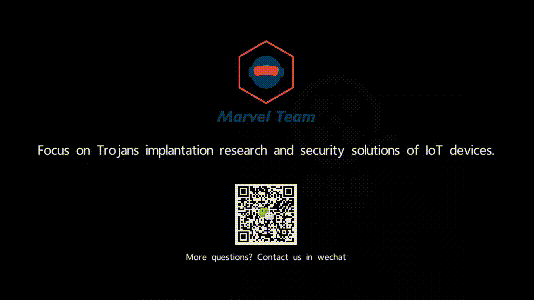 arthastang/iot-home-guard
A tool for malicious behavior detection in IoT devices
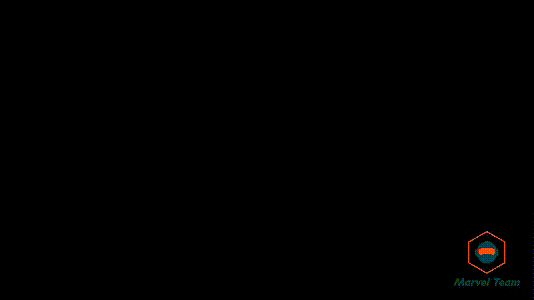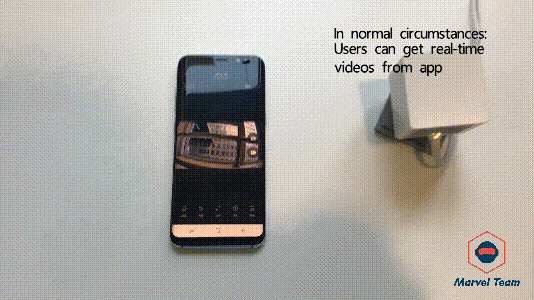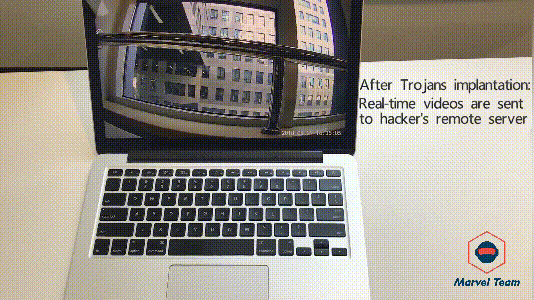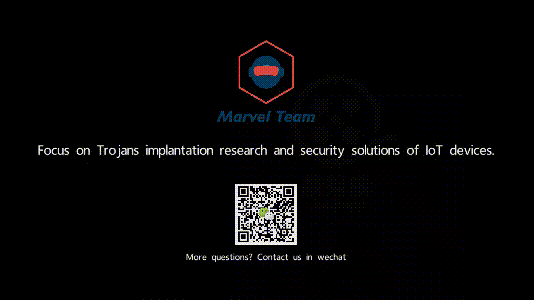 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 ricardojoserf/p-invoke.net
Curated collection of P/Invoke definitions from pinvoke.net with Microsoft documentation links, enabling quick Windows API prototyping for security…
 mucoze/umay
IoT Malware Similarity Analysis Platform