

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
systeminformer preview

systeminformer

GitHubwinsiderss/systeminformer

Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…

debuggersdigital-forensicsforensics+6
16.3k
15h 1m ago
qiling preview

qiling

GitHubqilingframework/qiling

A True Instrumentable Binary Emulation Framework

binary-analysisdebuggersdynamic-analysis-sandboxing+7
6.2k1 month ago
awesome-linux-attack-forensics-purplelabs preview

awesome-linux-attack-forensics-purplelabs

GitHubcr0nx/awesome-linux-attack-forensics-purplelabs

This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.

container-securitycurated-resourcesdigital-forensics+8
3423 years ago
DFIR-LABS preview

DFIR-LABS

GitHubazr43lkn1ght/dfir-labs

Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…

ctfdigital-forensicsdisk-forensics+6
6101 month ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…

digital-forensicsforensicsincident-response+2
4.5k11 days ago
fibratus preview

fibratus

GitHubrabbitstack/fibratus

Security sensor for realtime threat detection and protection
defensive-toolsforensicsincident-response+3
2.6k25 days ago
FalconGate preview

FalconGate

GitHuba3sal0n/falcongate

A smart gateway to stop cyber criminals - Sponsored by Falcon Guard

defensive-toolsdns-analysisintrusion-detection+5
2554 years ago
volatility preview
Archived

volatility

GitHubvolatilityfoundation/volatility

An advanced memory forensics framework
digital-forensicsforensicsincident-response+4
8.1k1 year ago
cybersecurity-projects preview

cybersecurity-projects

GitHubosxninja/cybersecurity-projects

This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
ai-securitycurated-resourcesdigital-forensics+7
301 month ago
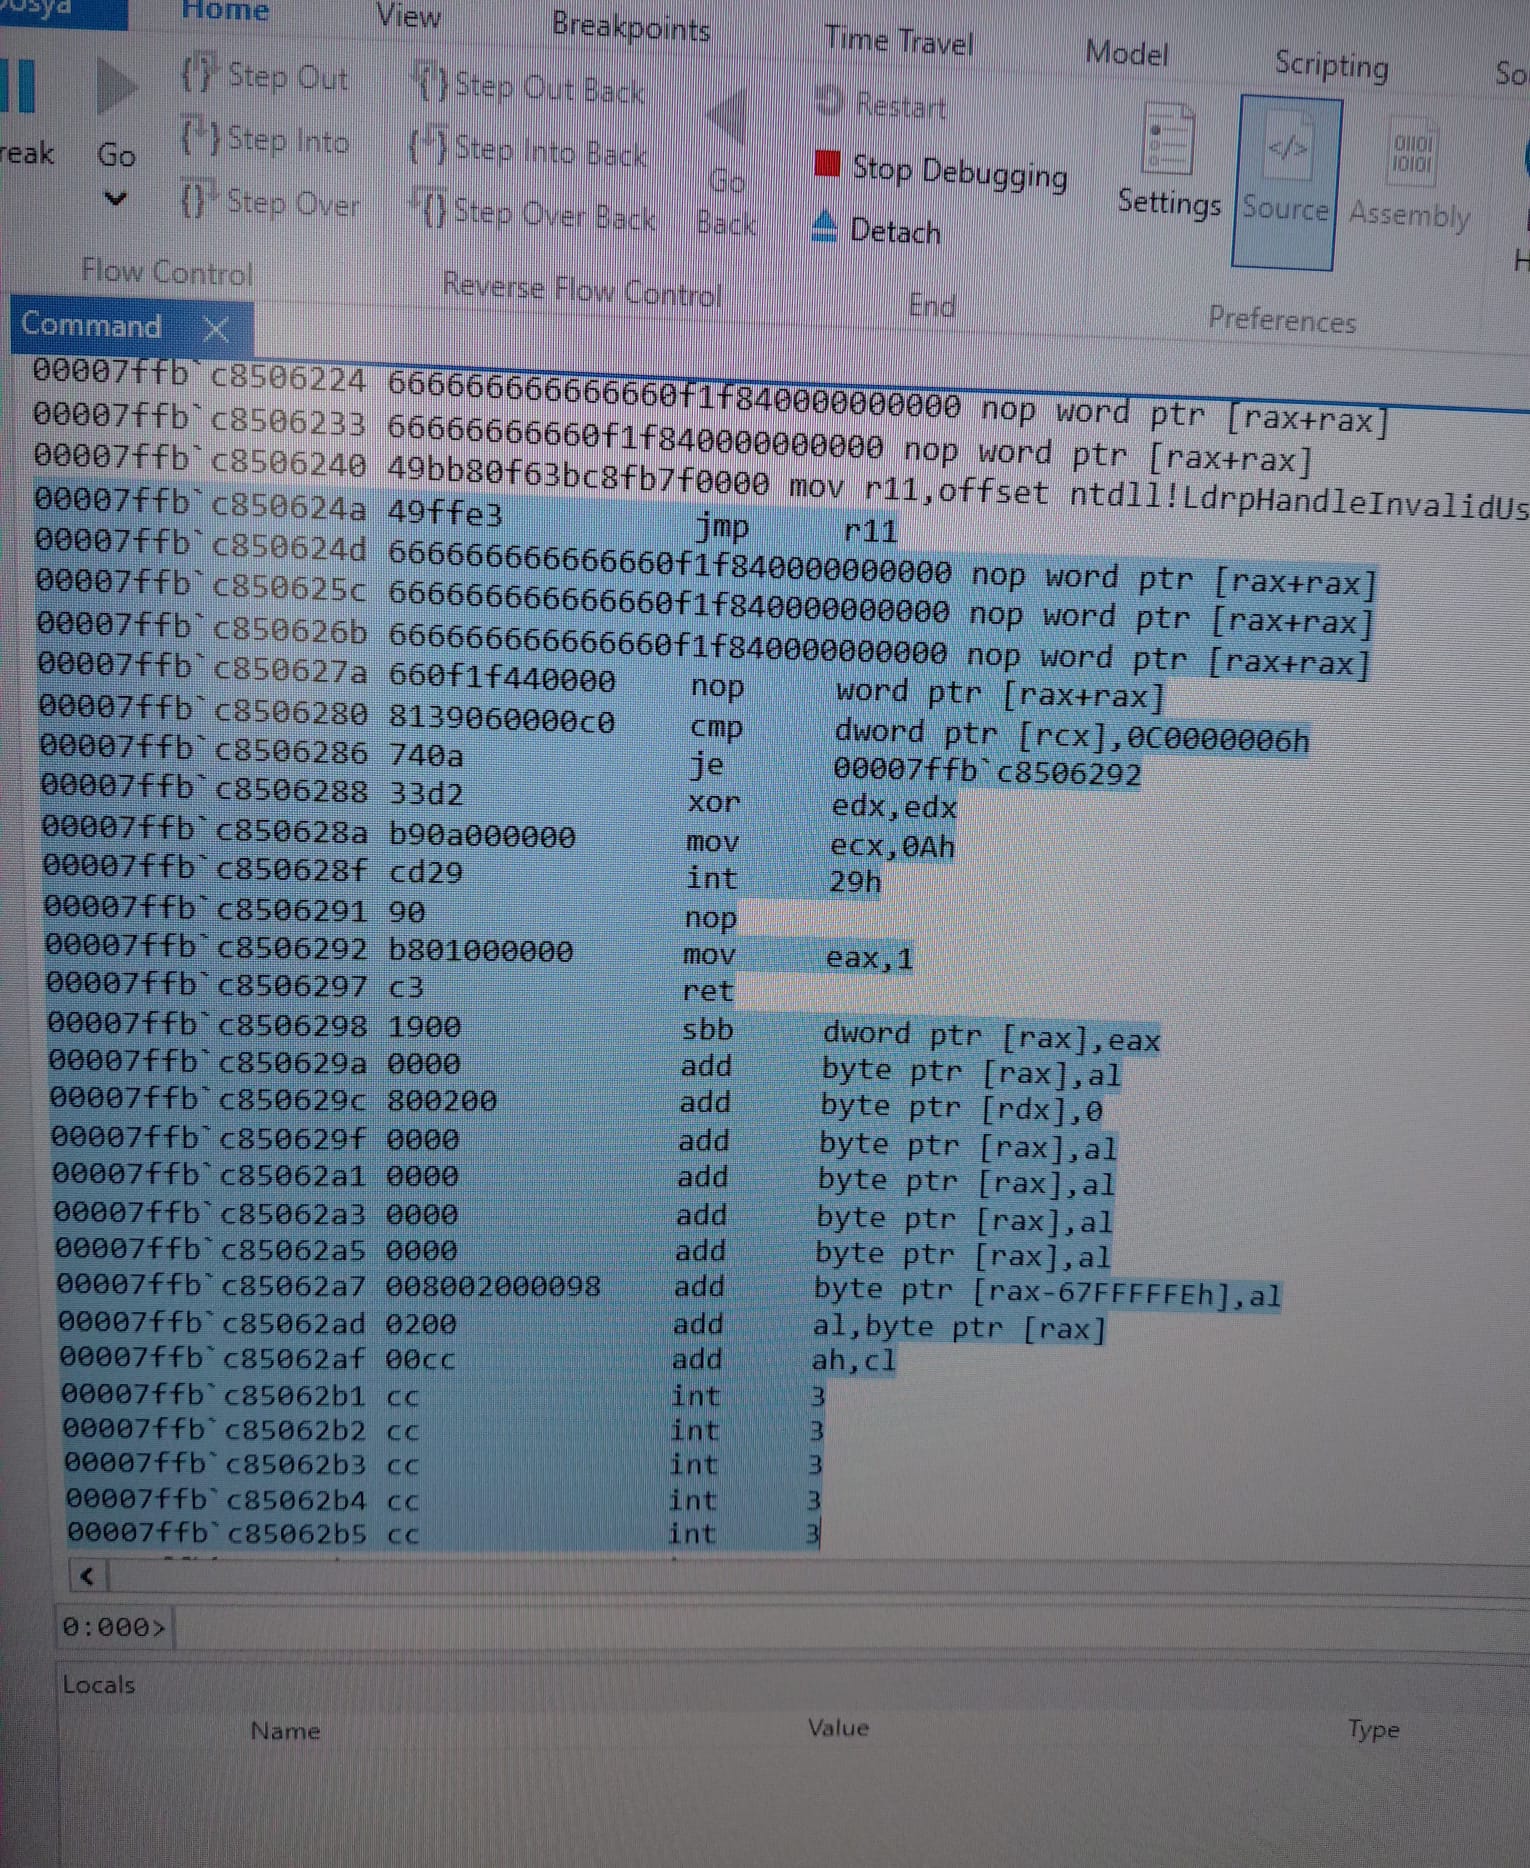
Advanced-Loader-Reverse-Engineering preview

Advanced-Loader-Reverse-Engineering

GitHubkaandemir993/advanced-loader-reverse-engineering

"In-depth reverse engineering analysis of an advanced multi-phase loader targeting Shellhost.exe, amsi.dll, mstscax.dll, and clbcatq.dll using module…

binary-analysiscode-analysiseducation+8
143 months ago
gef preview

gef

GitHubhugsy/gef

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k2 months ago
ABD preview

ABD

GitHubmalrev/abd

Course materials for Advanced Binary Deobfuscation by NTT Secure Platform Laboratories
binary-analysiseducationlabs-practice+2
1.2k5 years ago
EmailXpose preview

EmailXpose

GitLabroxanne_ardary/emailxpose

EmailXpose is an open source AI-powered email security system that detects phishing, spam, scams, malware, and social engineering attacks. It goes…
ai-securitydynamic-analysis-sandboxingemail-security+8
1 month ago
VMDragonSlayer preview

VMDragonSlayer

GitHubpoppopjmp/vmdragonslayer

Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
binary-analysisdebuggersdynamic-analysis-sandboxing+8
4491 year ago
Dr0p1t-Framework preview
Archived

Dr0p1t-Framework

GitHubd4vinci/dr0p1t-framework

A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
anti-botcommand-and-controlexploitation+9
1.5k7 years ago
Pegasus-Malware-Scan preview

Pegasus-Malware-Scan

GitHubsobri3195/pegasus-malware-scan

Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…
educationforensicsincident-response+3
61 year ago
GoRedOps preview
Archived

GoRedOps

GitHubkiexitdispatcher/goredops

🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
anti-botbinary-analysiscommand-and-control+9
6711 year ago
MalwareForge---Advanced-Static-Malware-Analyzer preview

MalwareForge---Advanced-Static-Malware-Analyzer

GitHubkaandemir993/malwareforge---advanced-static-malware-analyzer

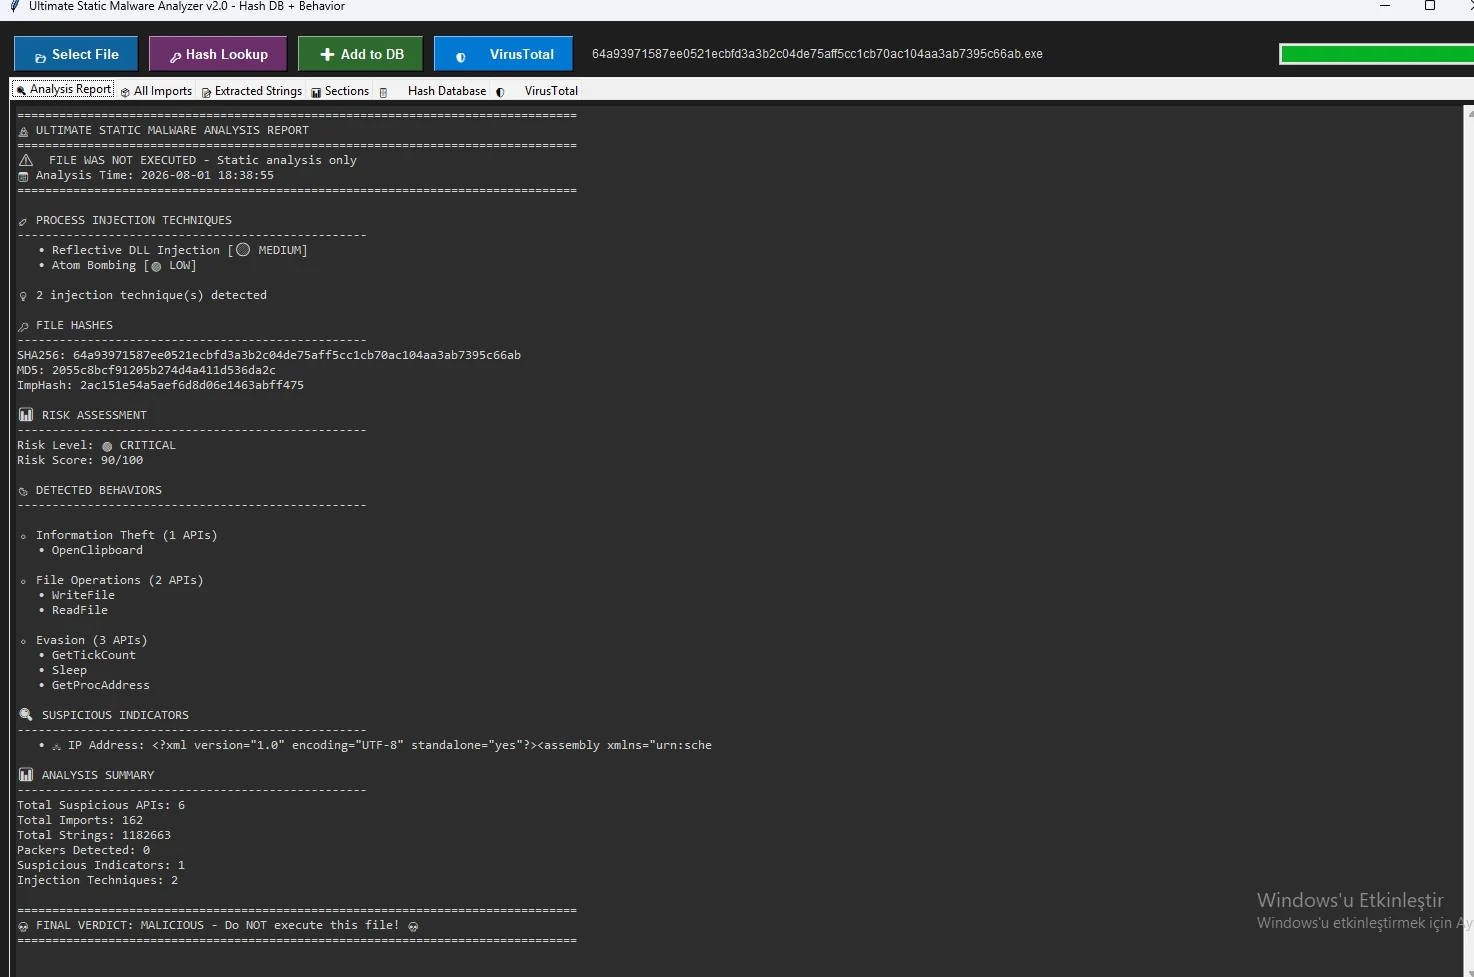
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

binary-analysishash-analysismalware-analysis+2
52 months ago
Previous12Next
