SOC-Analyst-Portfolio

A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…

A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…

Programmable packet inspection engine with NIDS, DNS classification, frequency analysis, and auto-regex generation. Supports Python/Ruby/Java/Lua…

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…

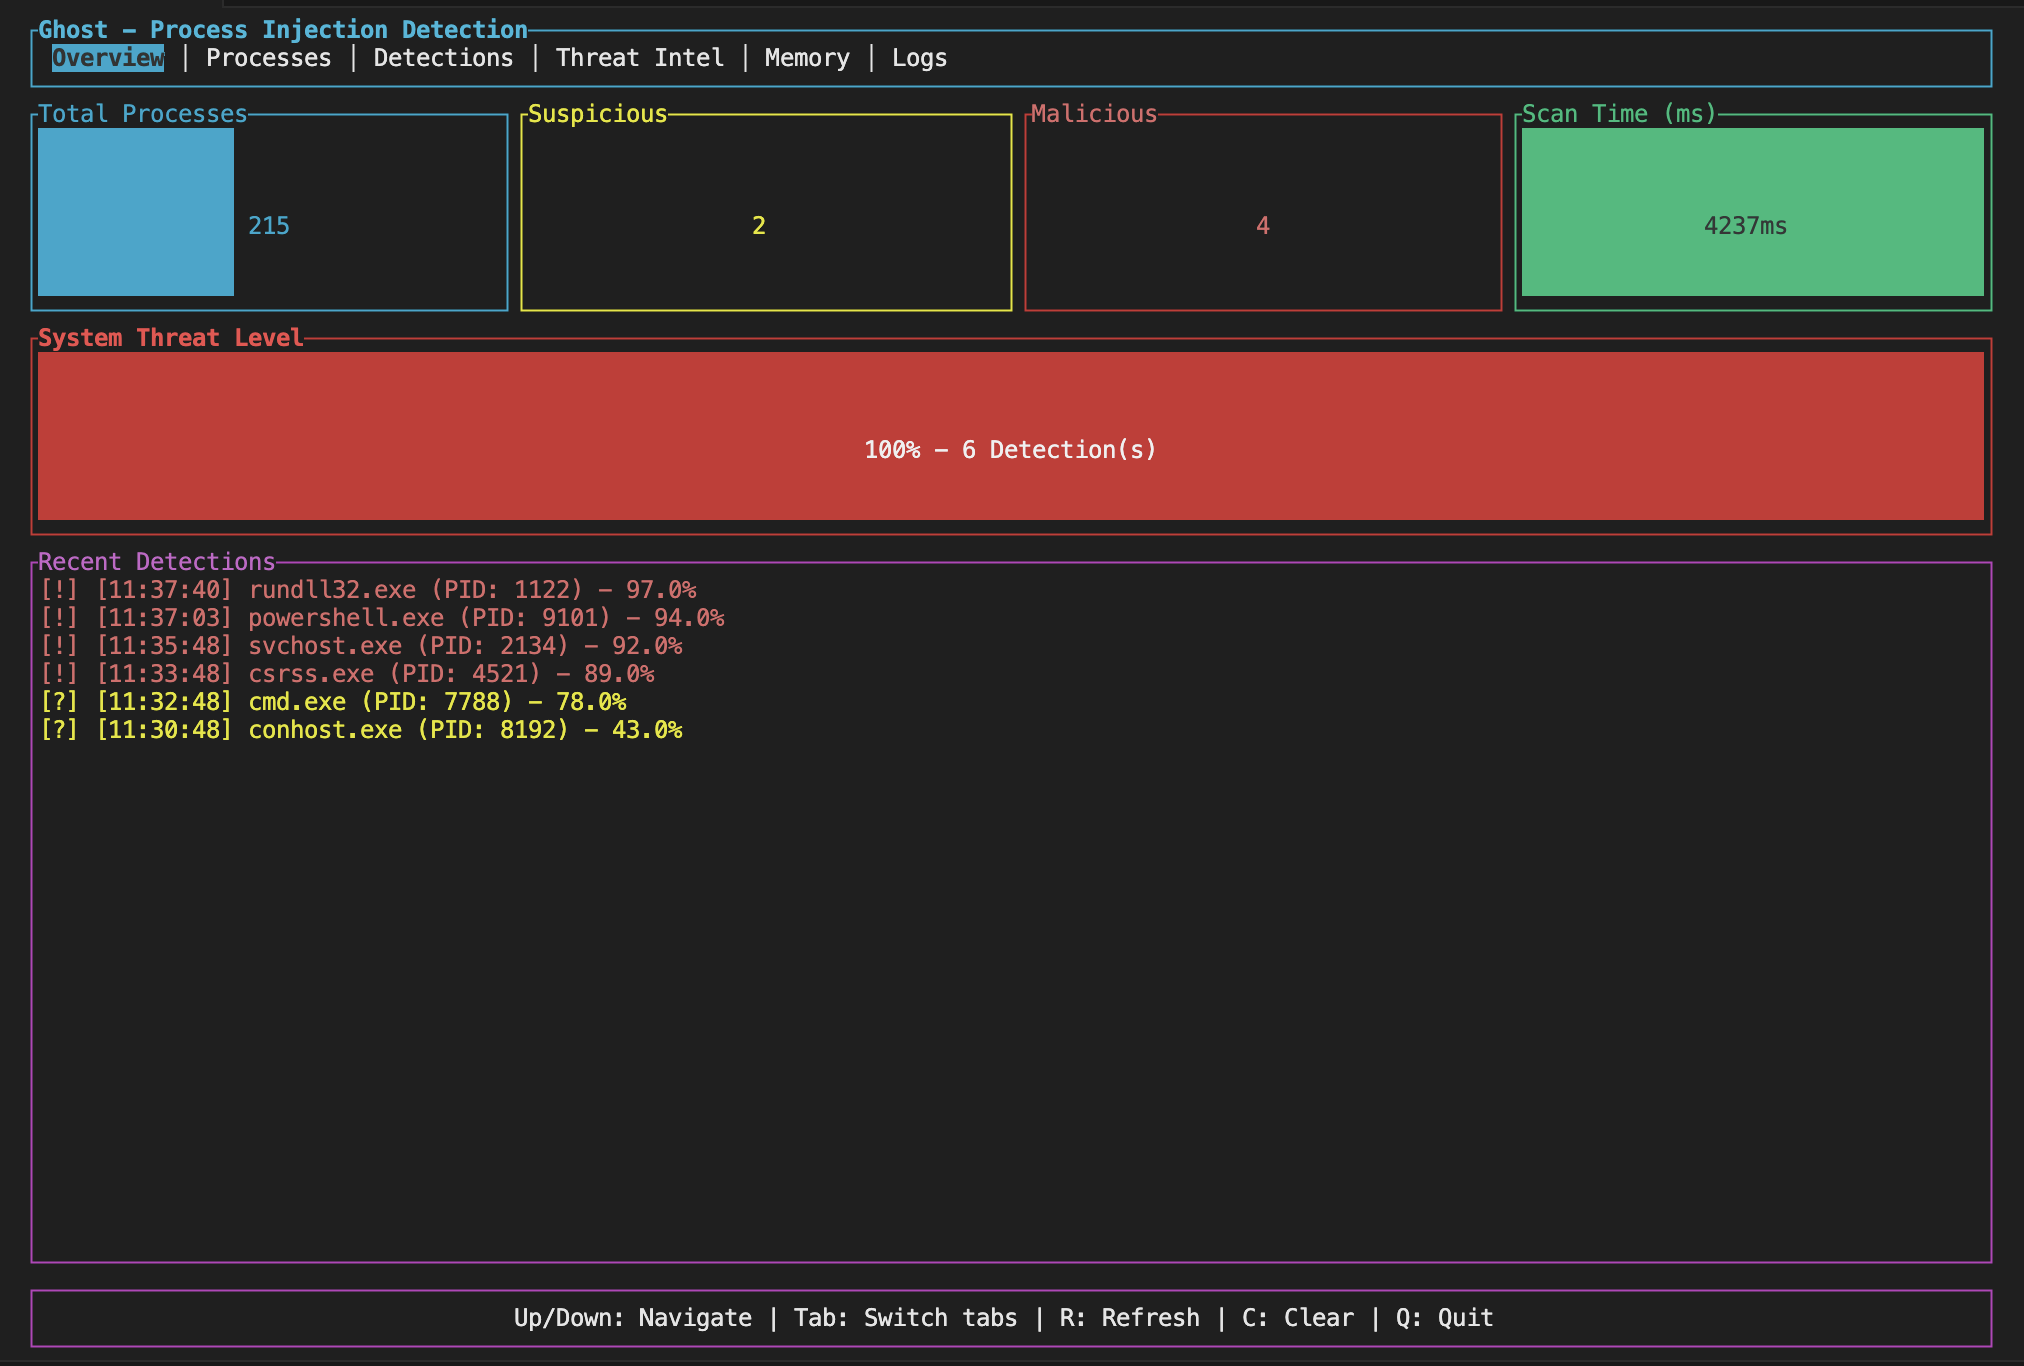
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

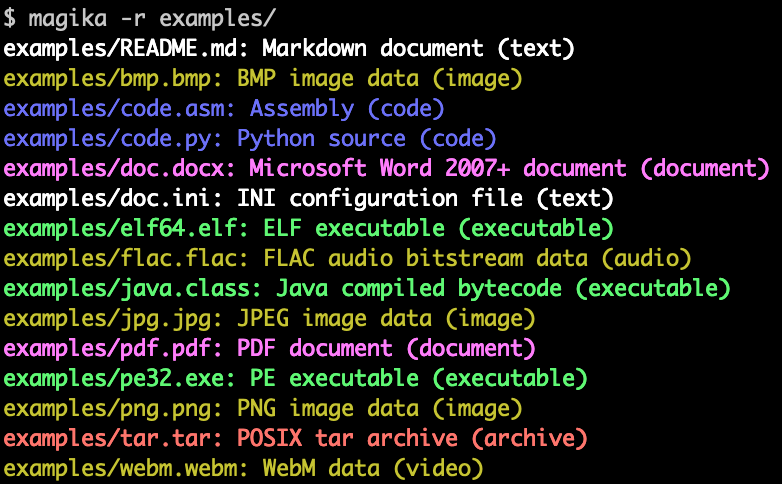
Fast and accurate AI powered file content types detection

A network packet forensics tool for SSH

AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…

Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…

Serverless AWS security automation framework that ingests threat intelligence, applies ML-based anomaly detection (RCF, IP Insights), and enriches…

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…

ML-driven threat detection and continuous monitoring platform built for federal zero trust architectures.

Semantic search over videos using Gemini Embedding 2 or Qwen3-VL.