
BIDO
 whatishope/bido
Image-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
android-securityeducationmachine-learning+3
2
whatishope/bidoImage-based Android malware detection framework tackling obfuscation and concept drift. Includes curated datasets and Python code for training…
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 lauriewired/ghidramcp
MCP Server for Ghidra
 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 google/oss-fuzz-gen
LLM powered fuzzing via OSS-Fuzz.
 aloshdenny/reverse-synthid-text
reverse engineering SynthID for text
 jhuapl/codecut
A Ghidra plugin for locating object file boundaries.
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 qbnasasn/google-tensor-chips
Google Tensor Cracks
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.
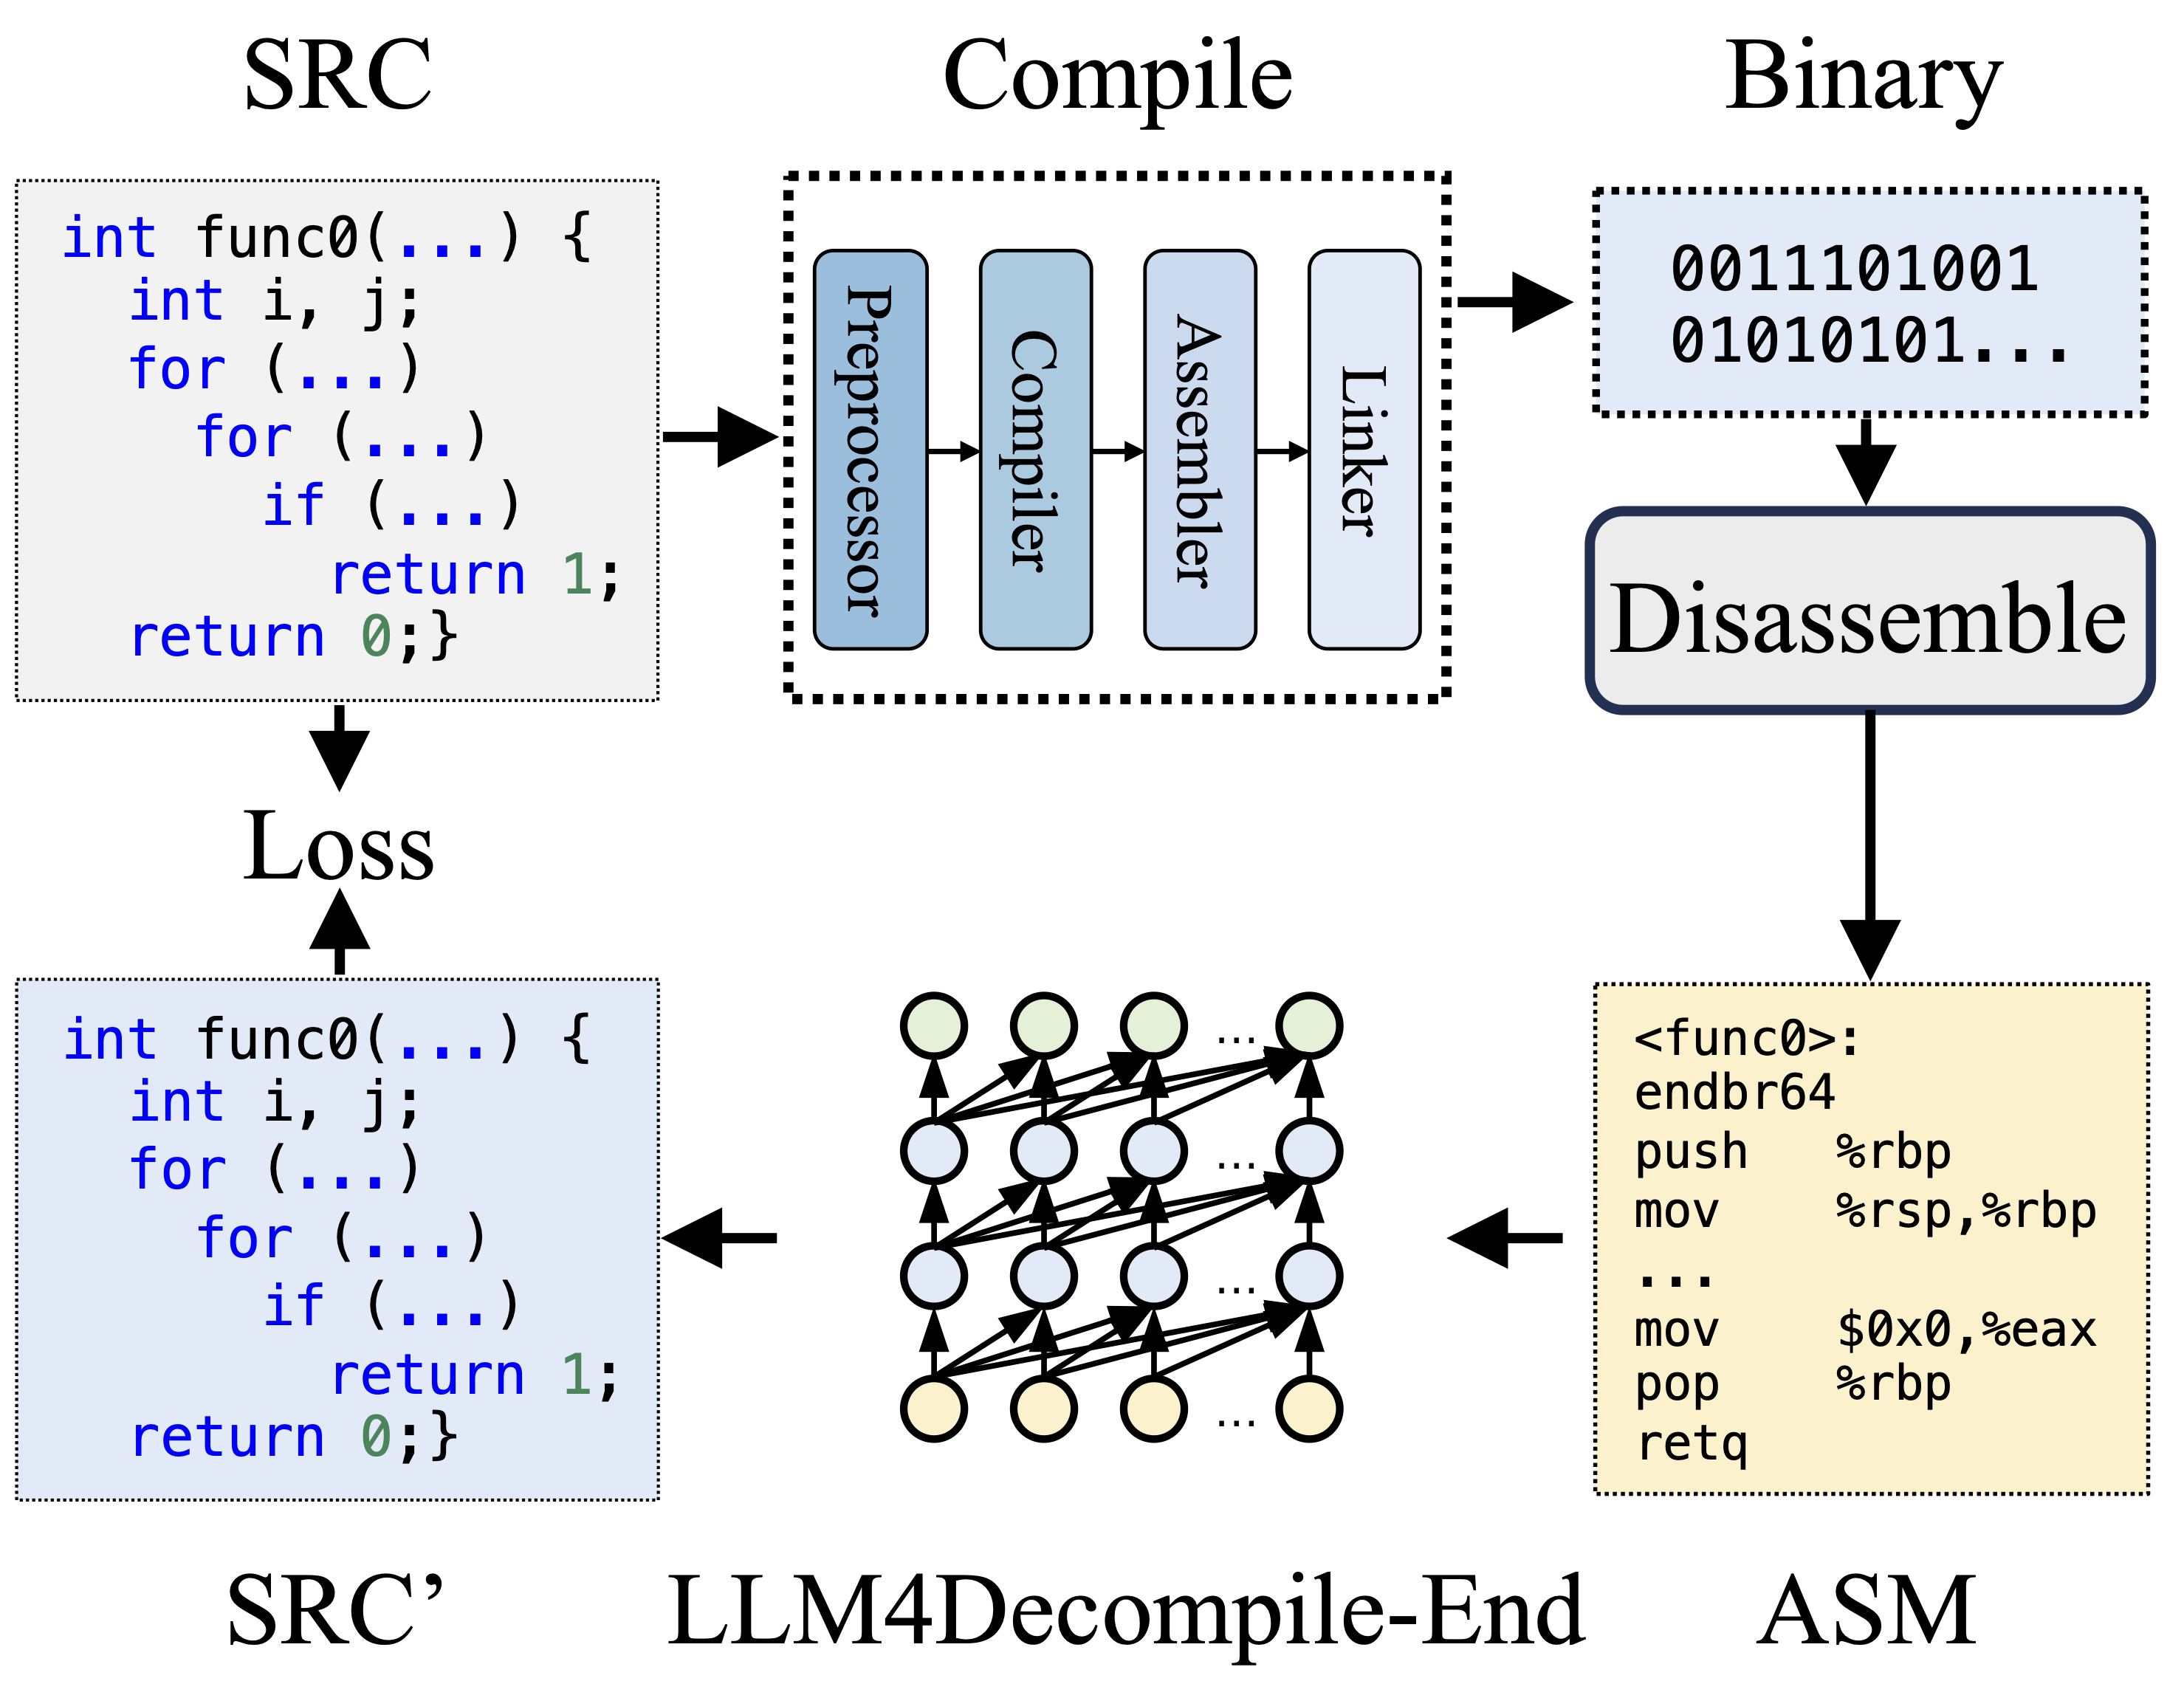 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
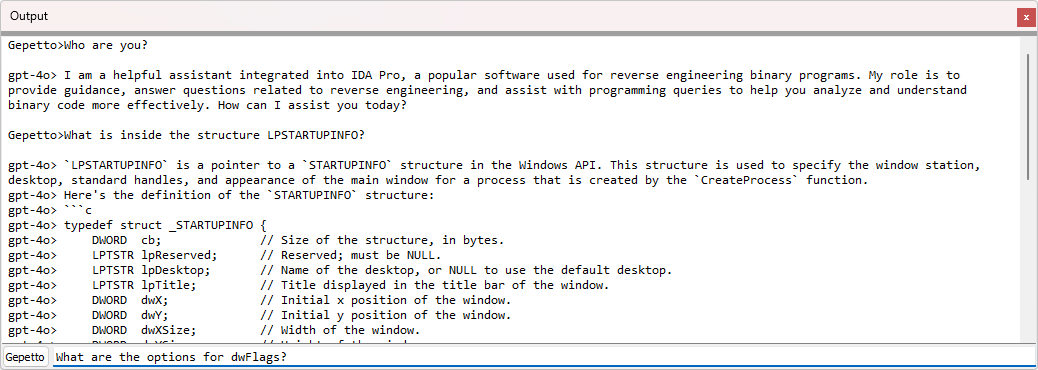 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 gadiluna/safe
SAFE: Self-Attentive Function Embeddings for binary similarity