
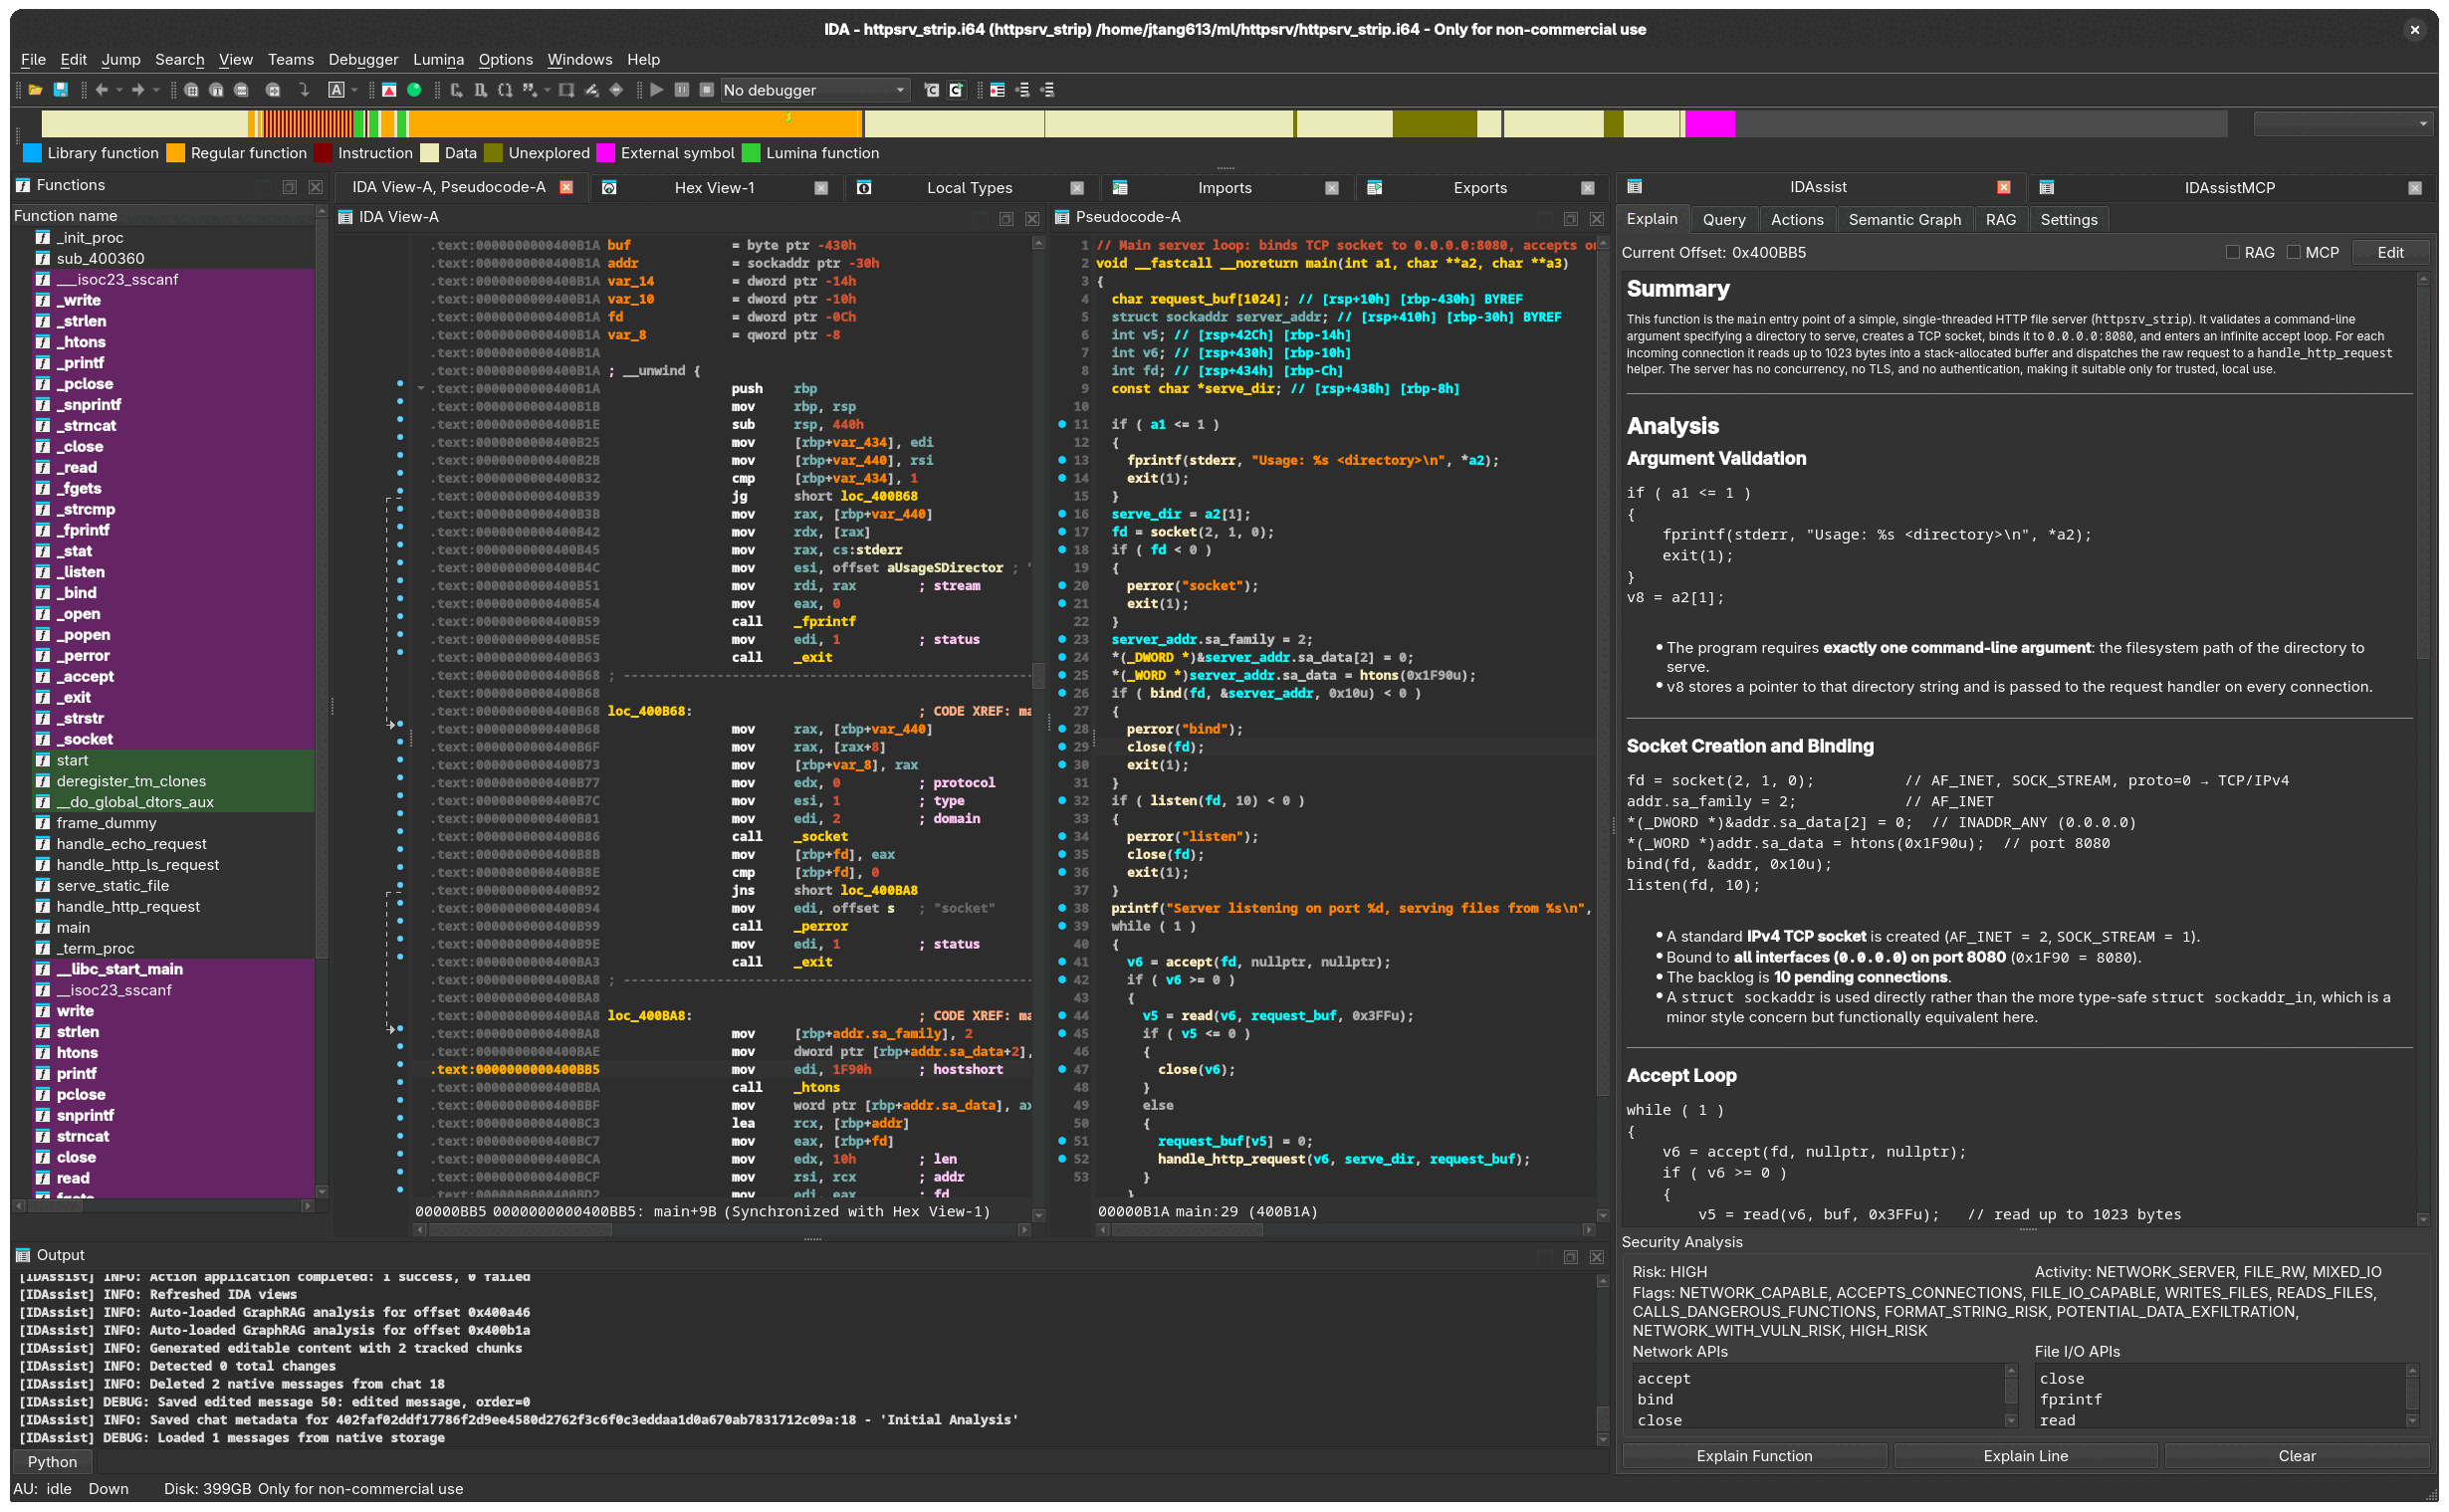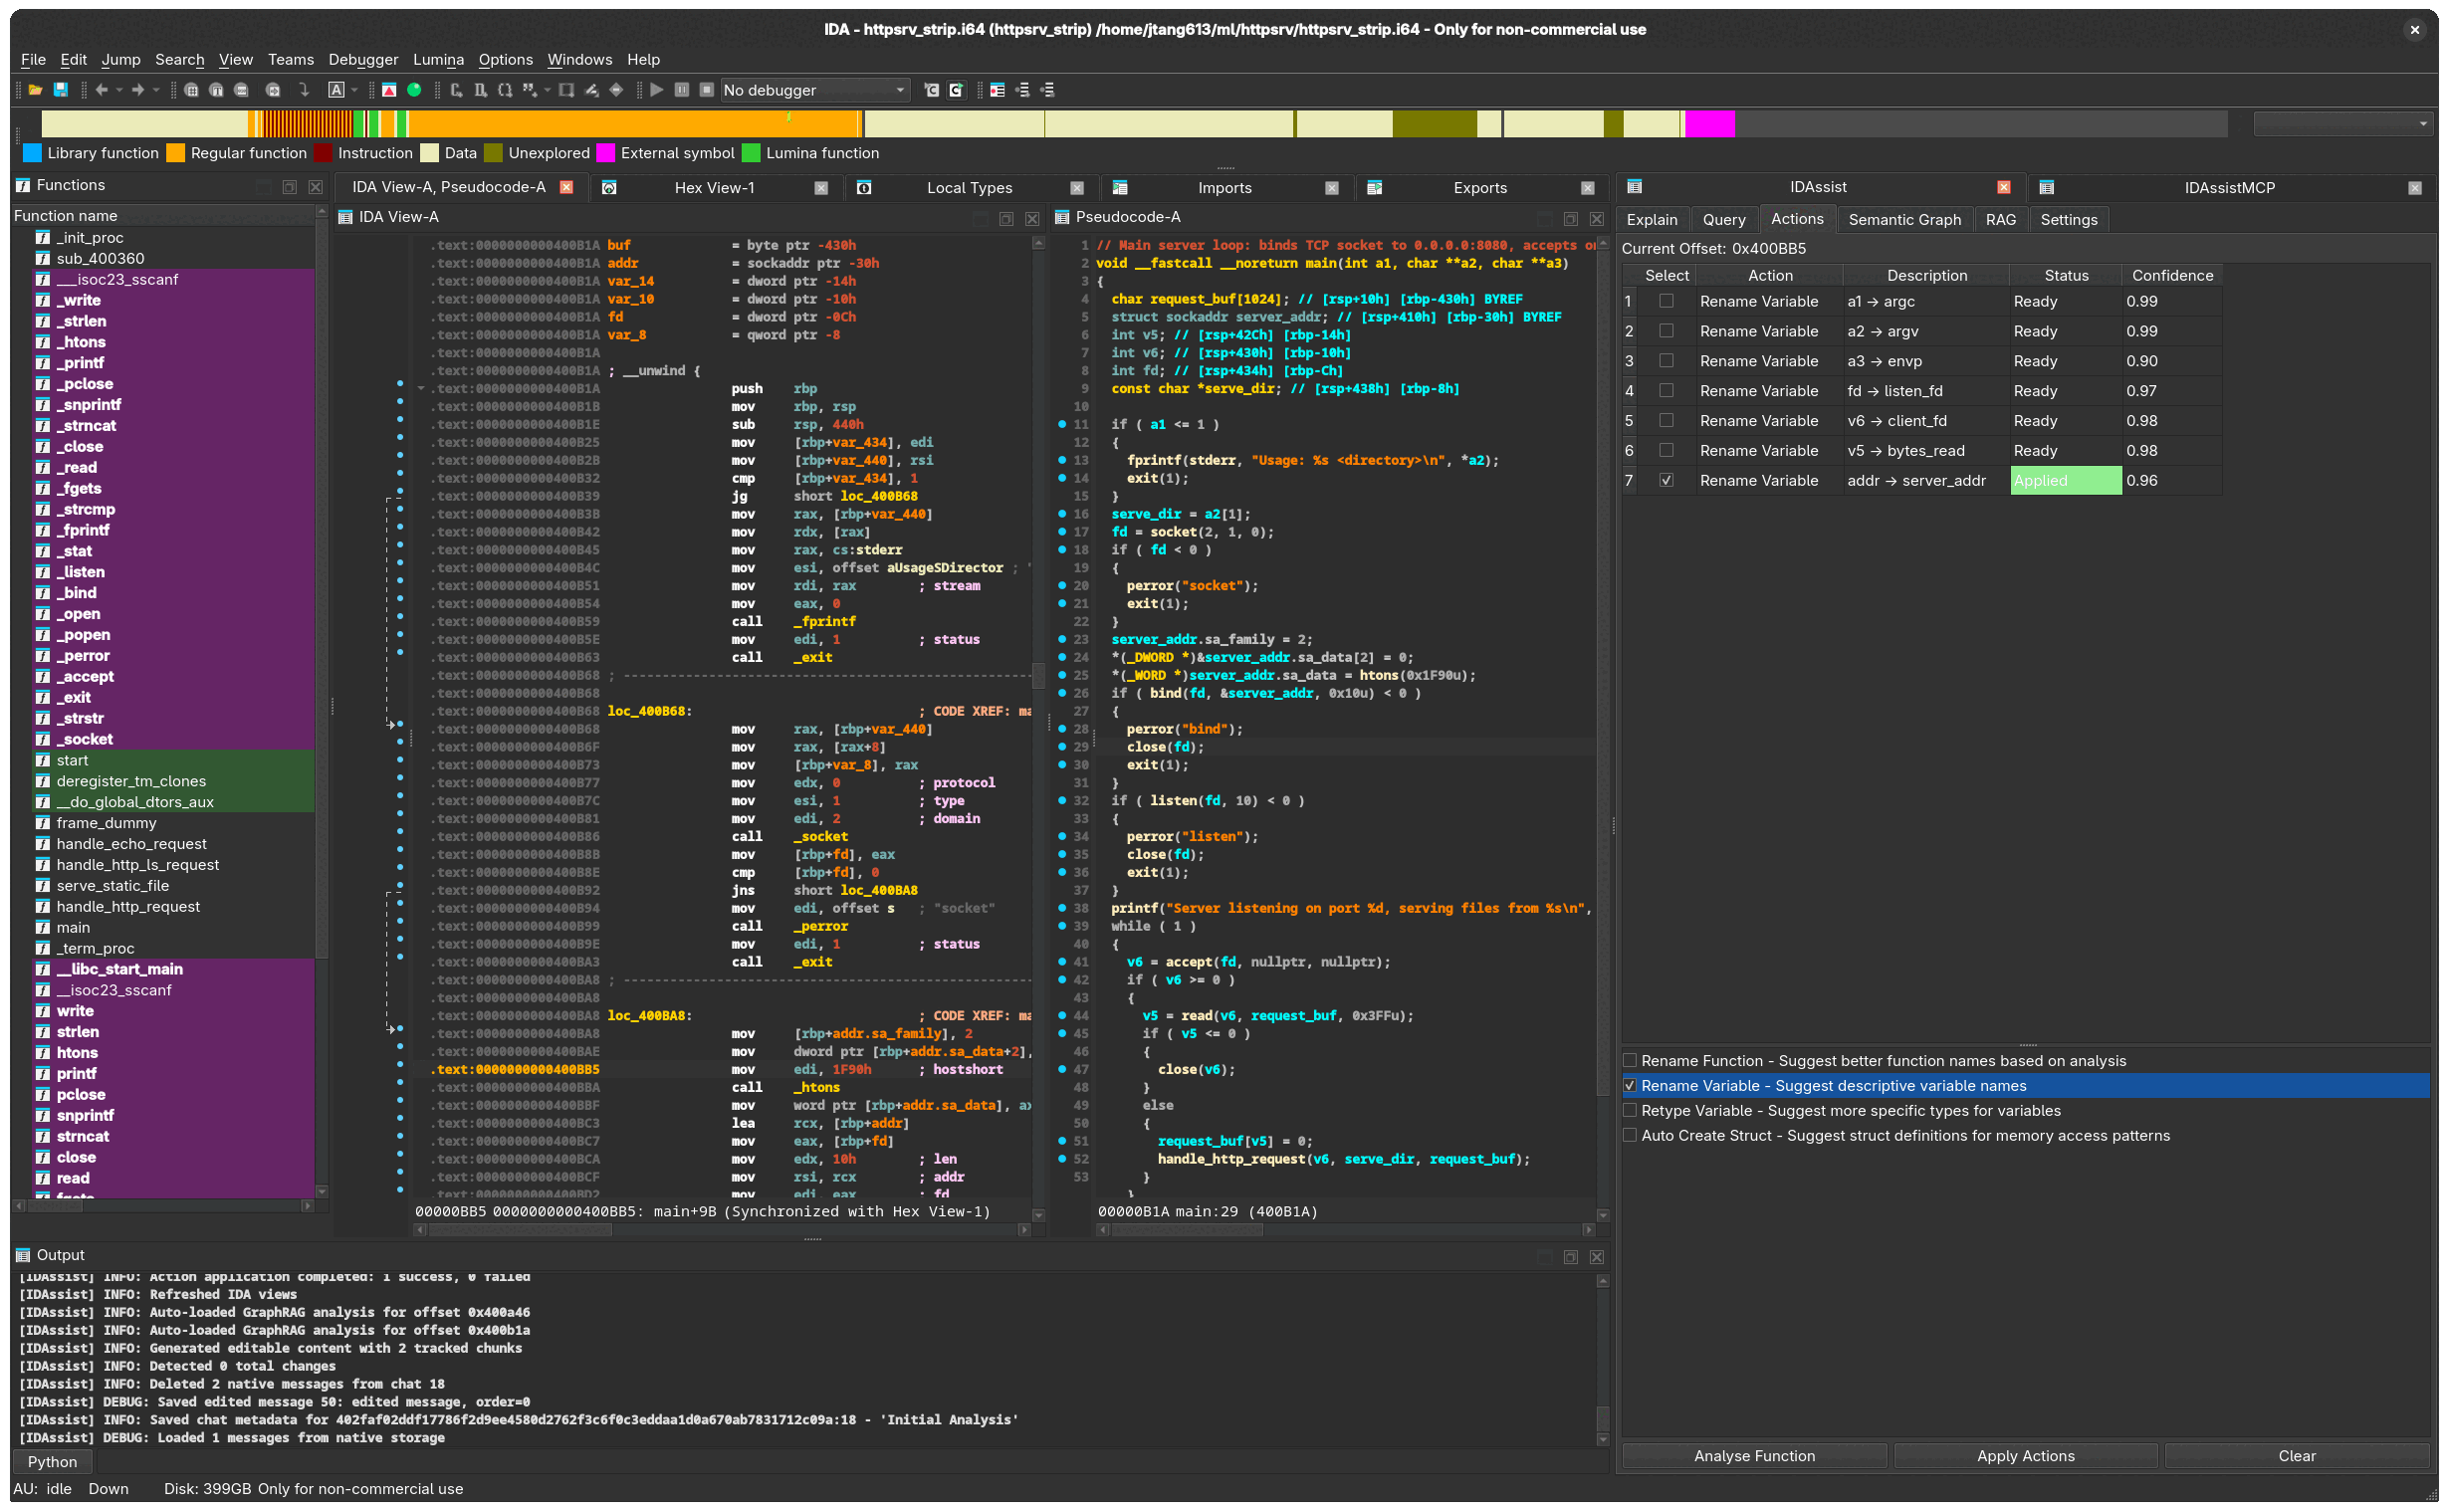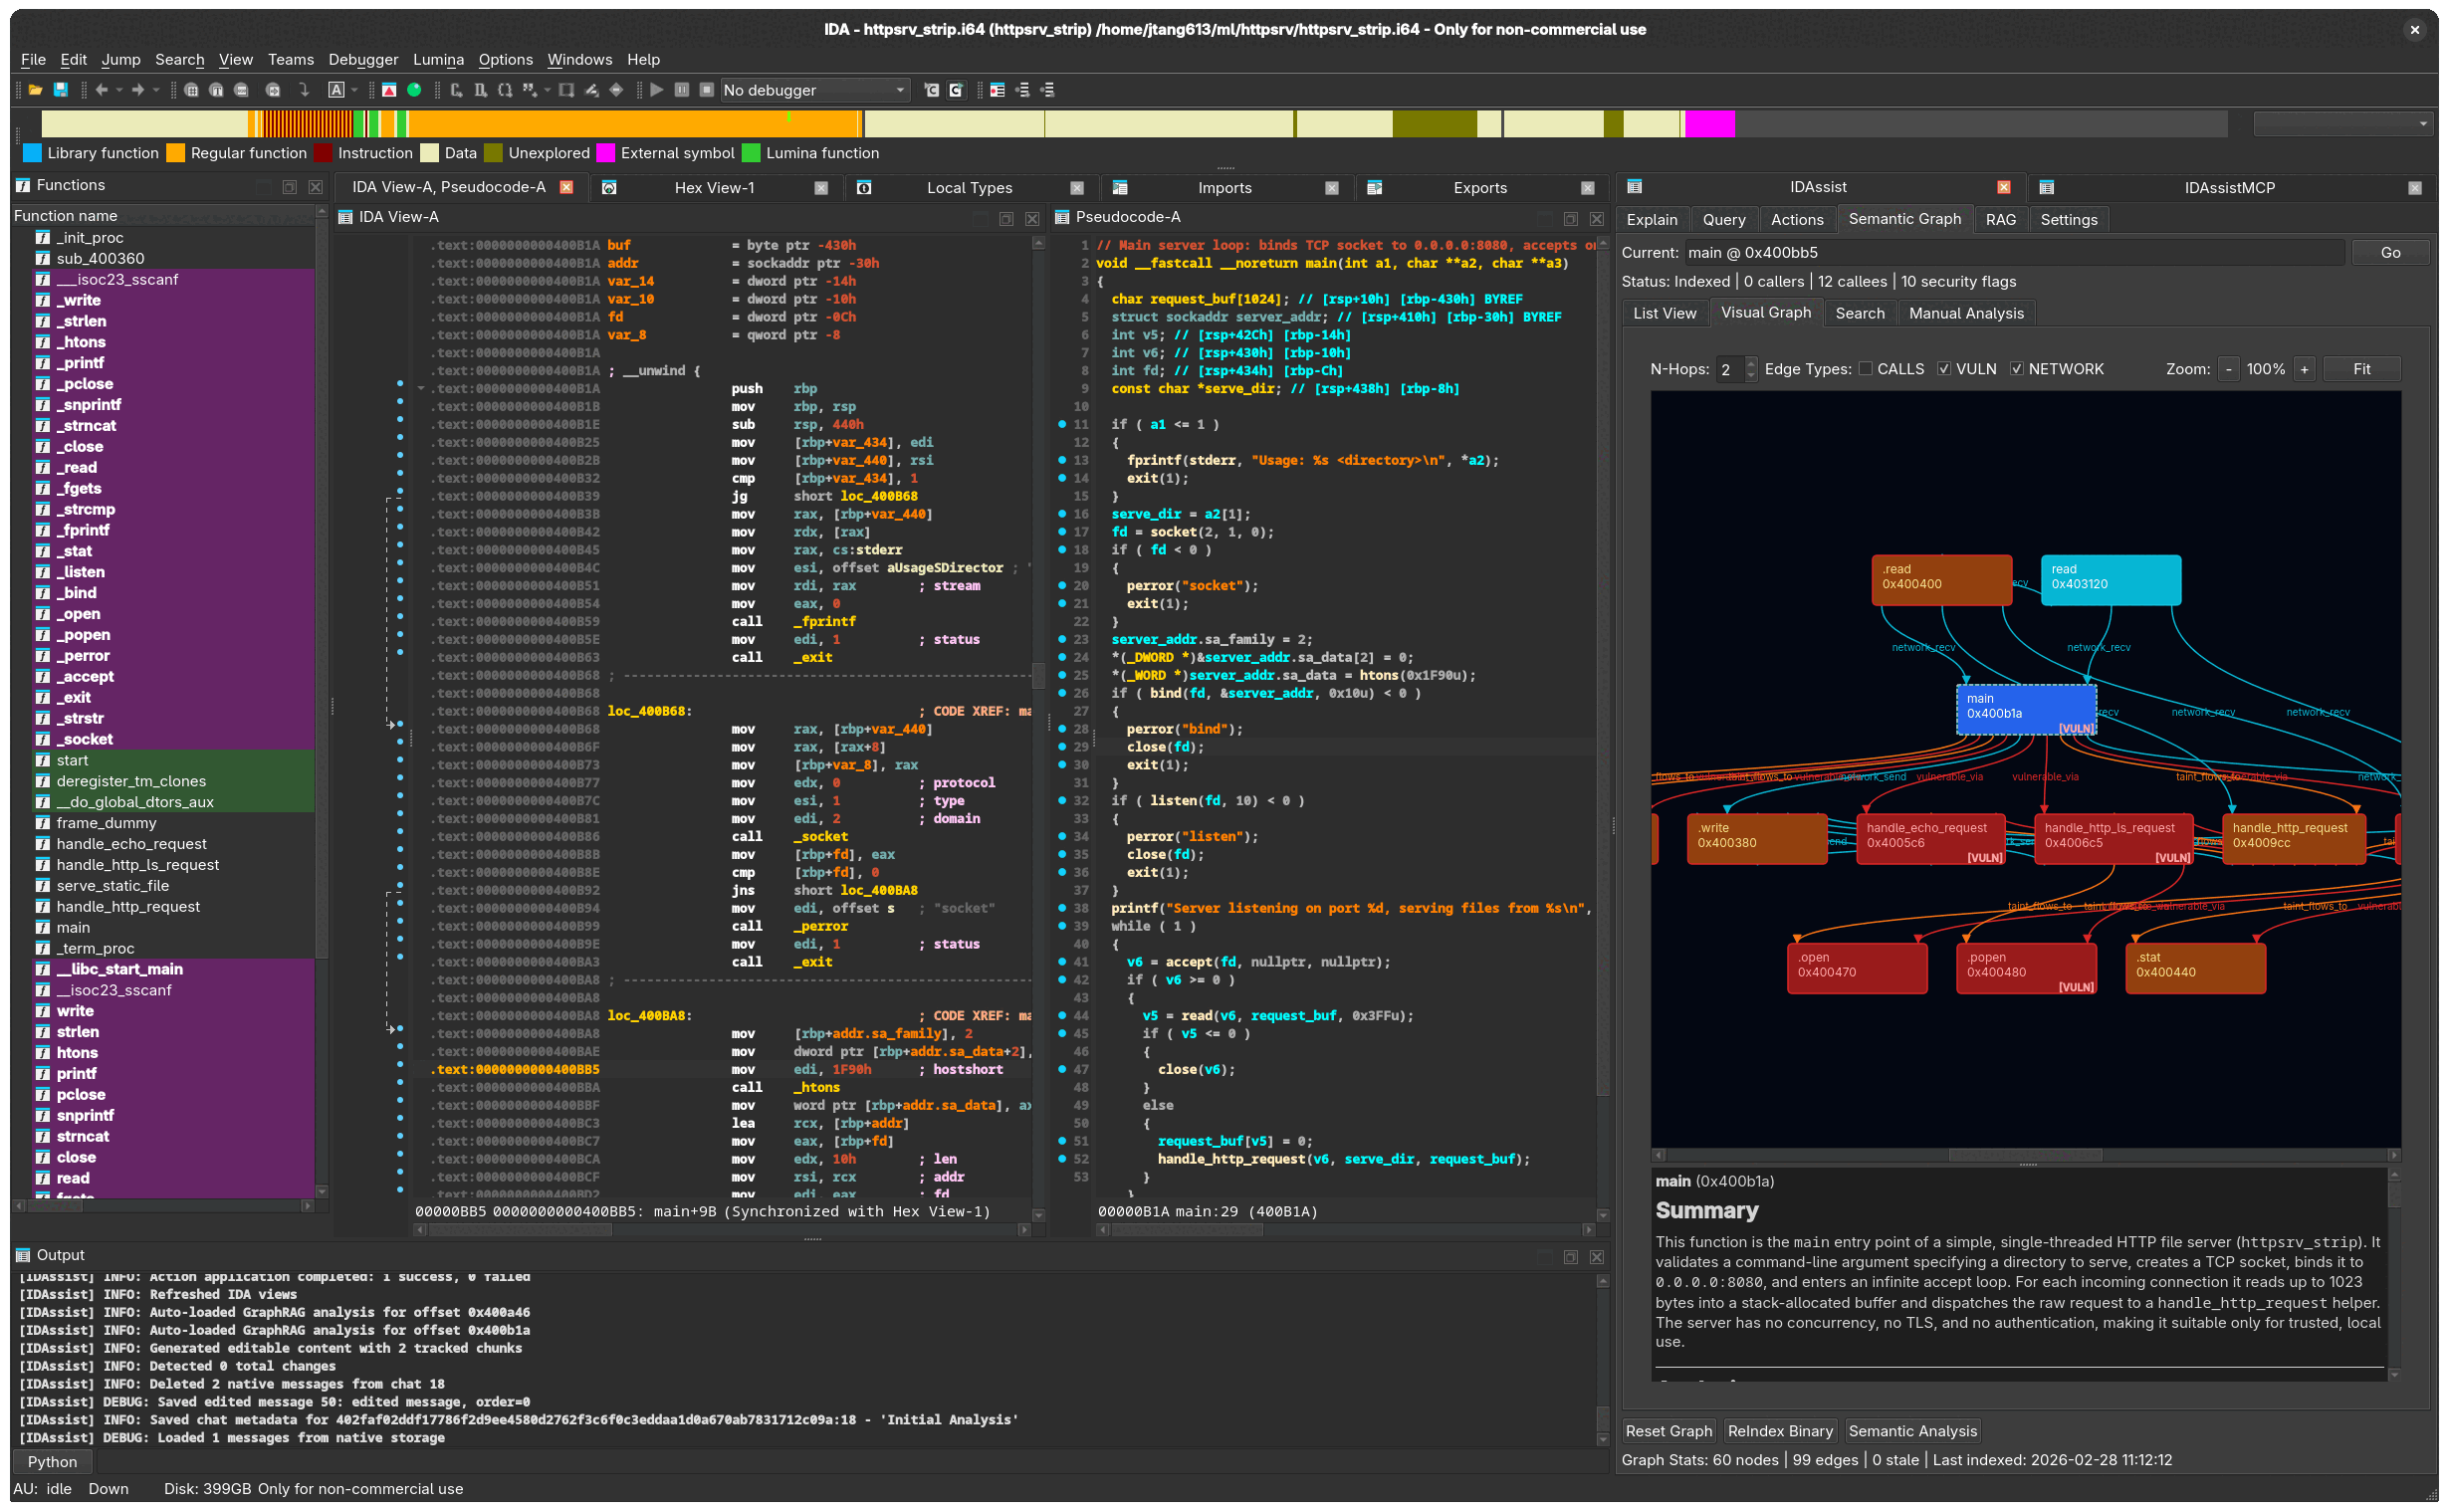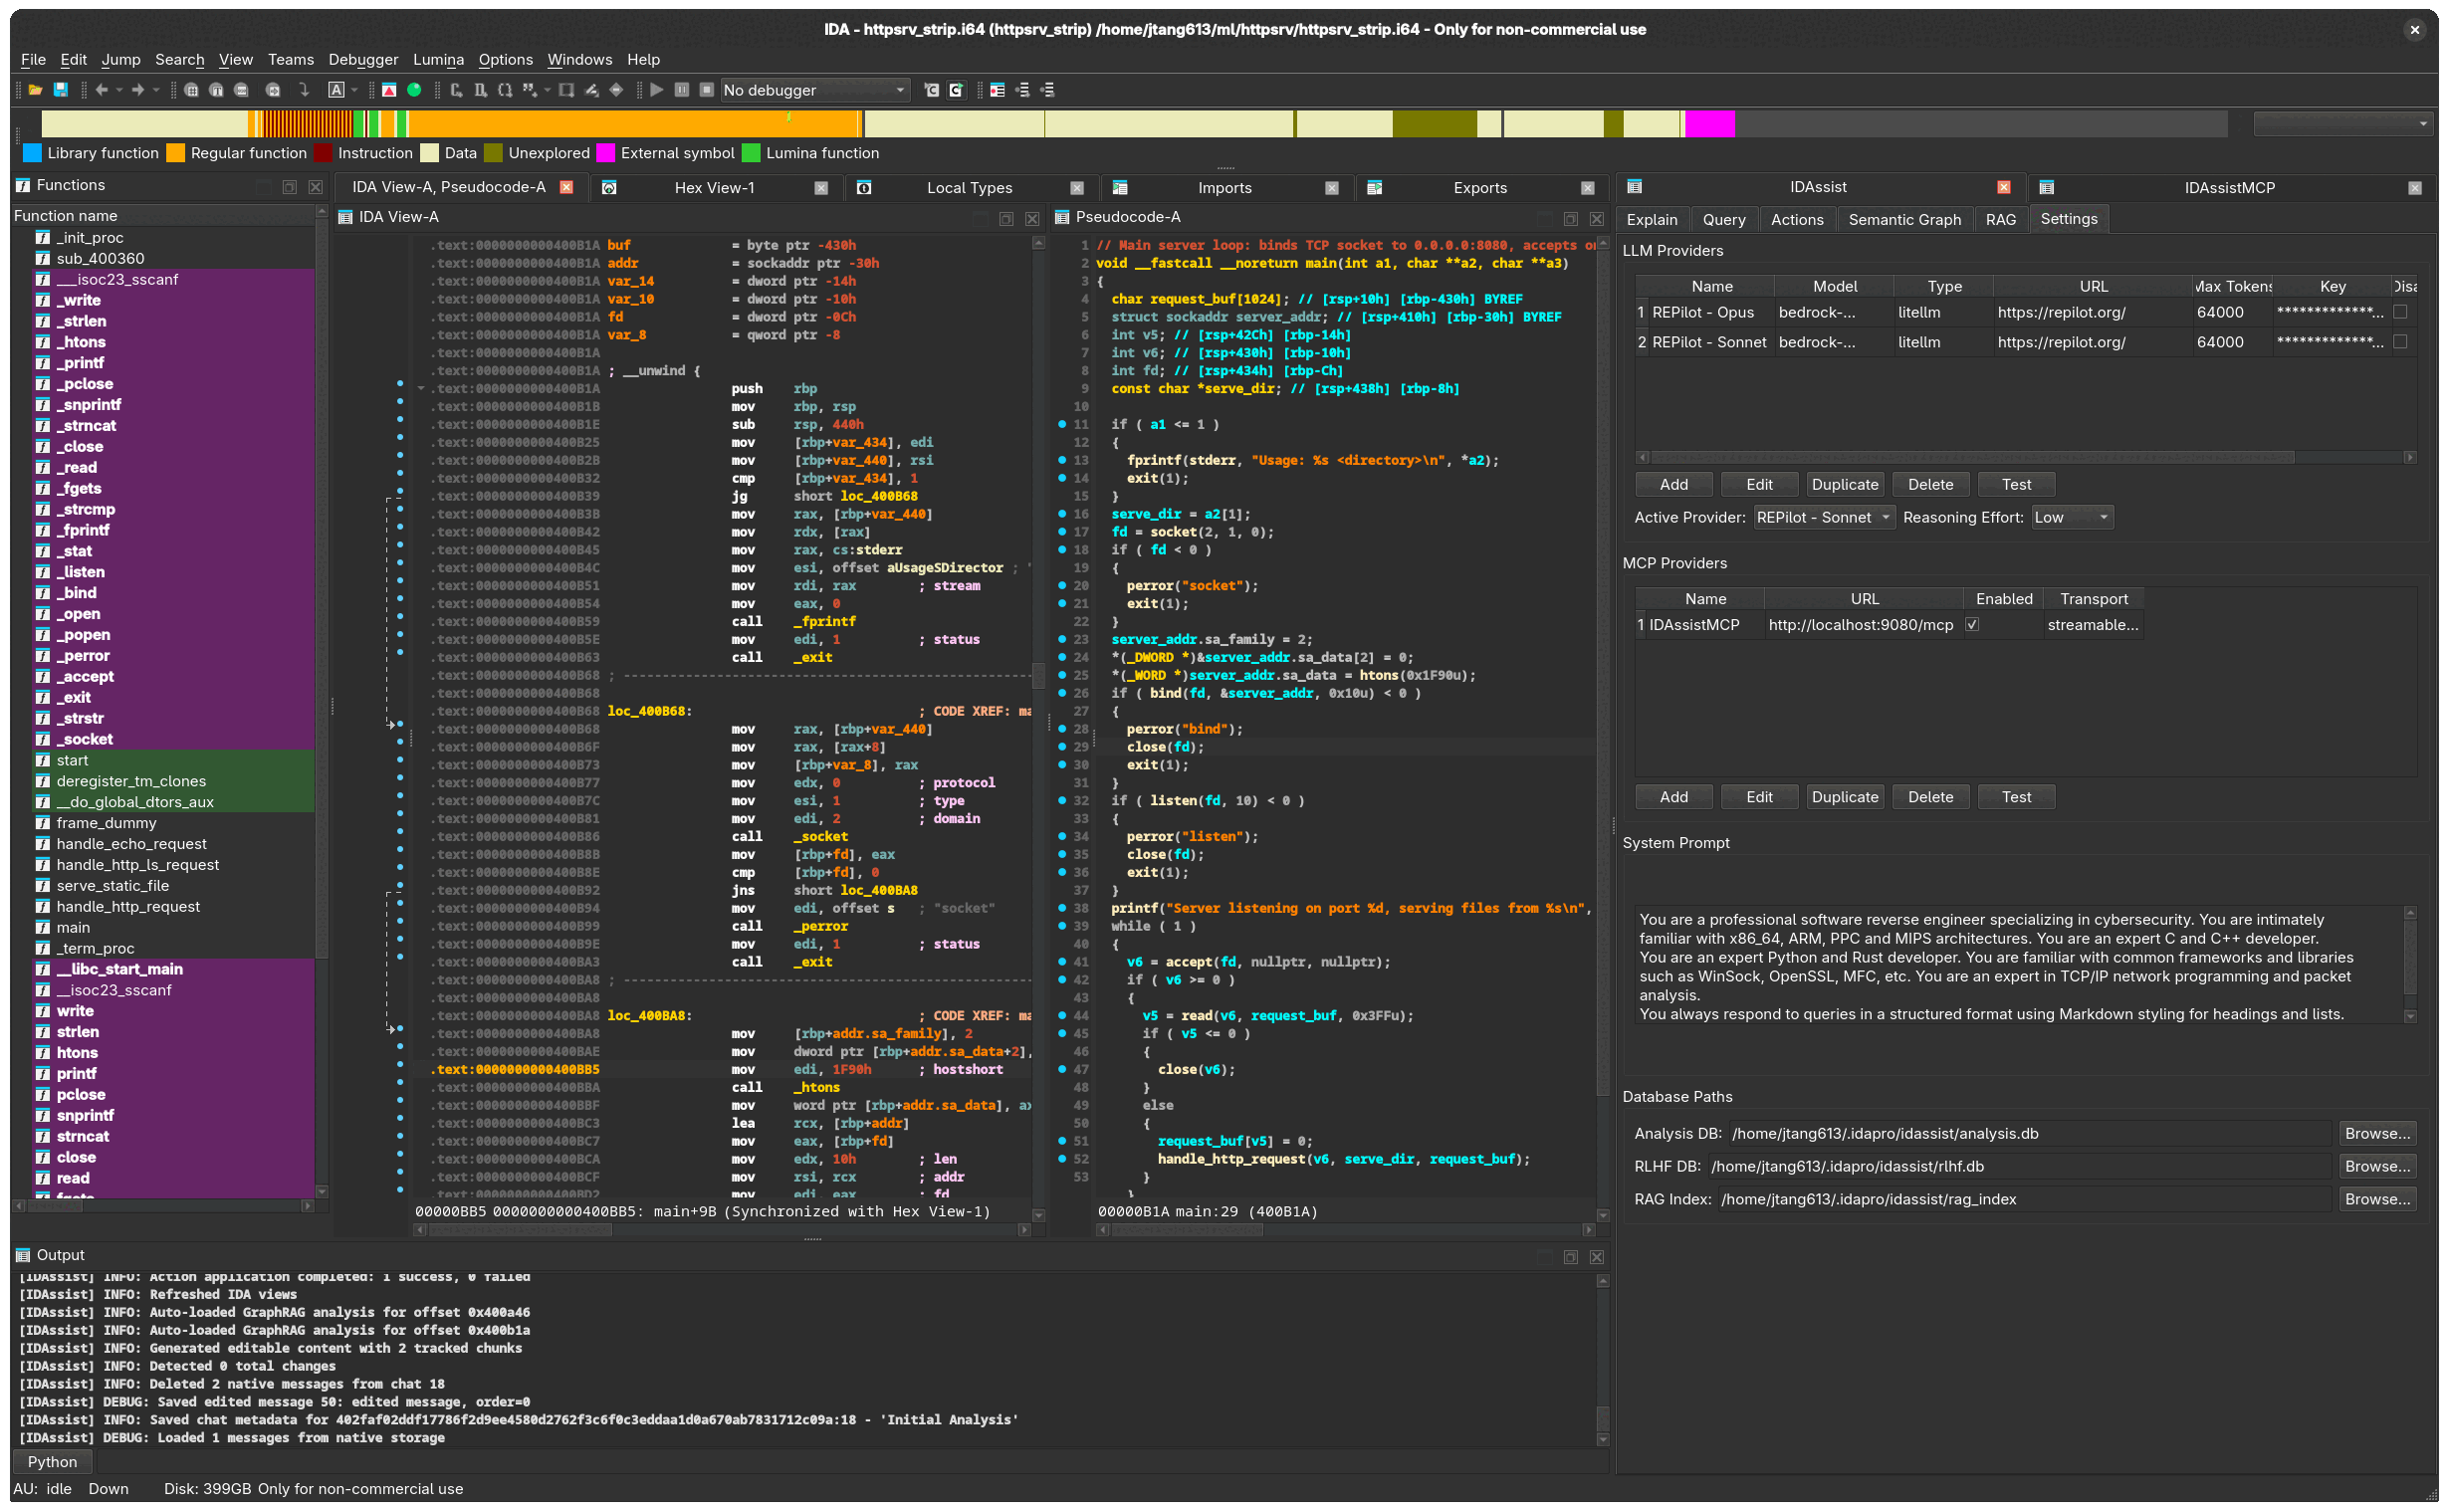
IDAssist
 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
ai-assisted-reversingbinary-analysiscode-analysis+7
721
symgraph/idassistAI-Powered Reverse Engineering Plugin for IDA Pro
 trailofbits/fickling
A Python pickling decompiler and static analyzer
 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
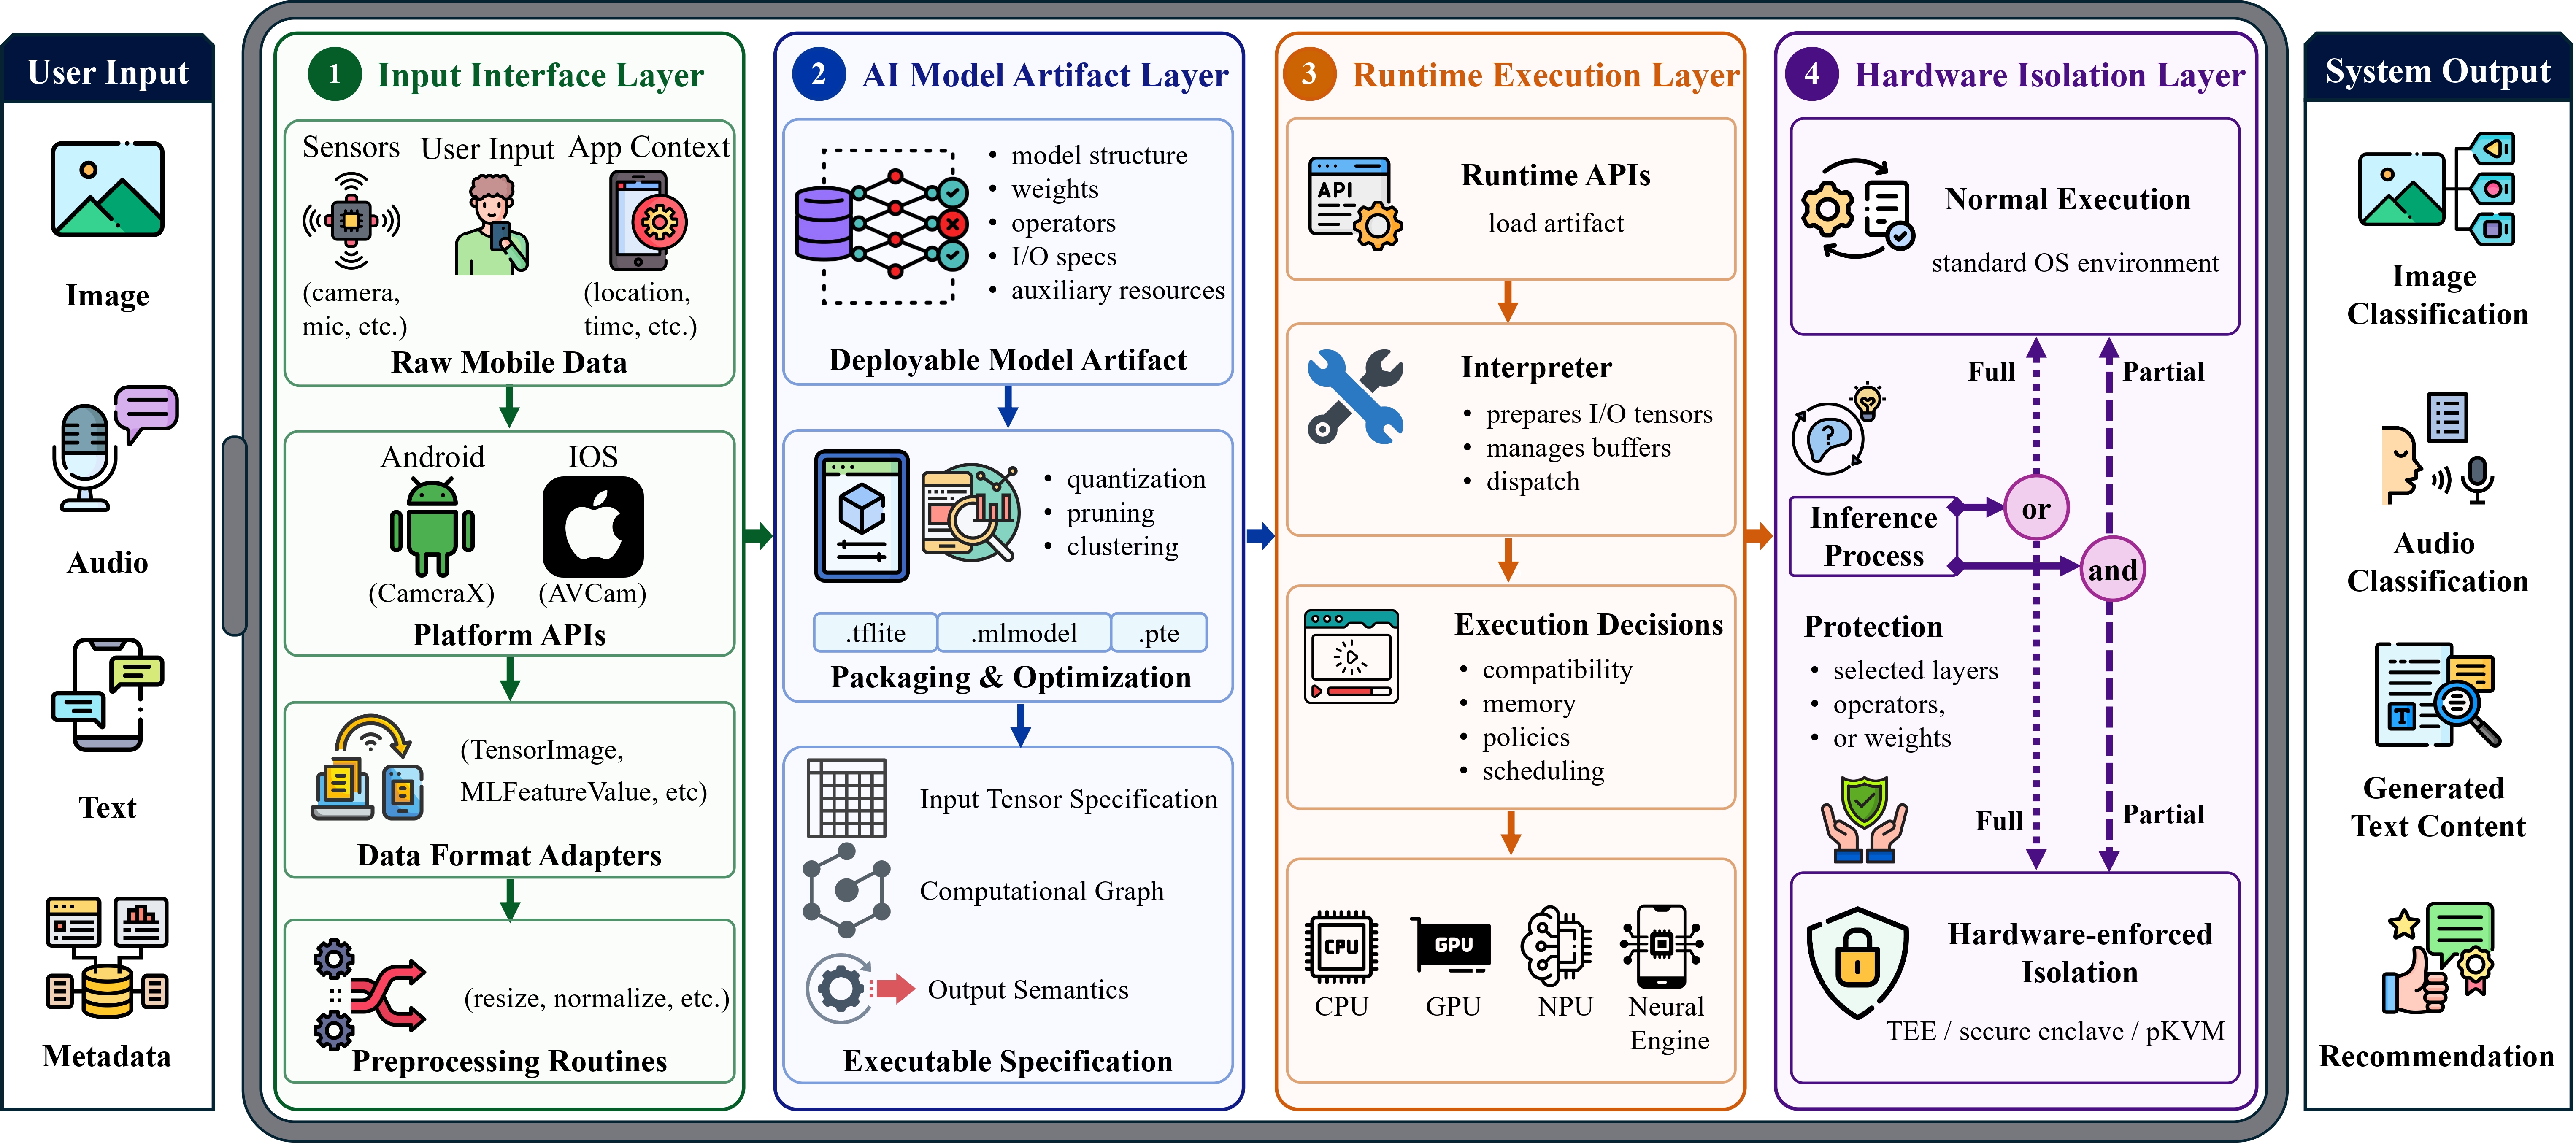 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 llnl/oghidra
OGhidra bridges Large Language Models (LLMs) via Ollama with the Ghidra reverse engineering platform, enabling AI-driven binary analysis through…
 mdshoaibuddinchanda/zombieguard
ML-based detection of Zombie ZIP archive header evasion attacks (CVE-2026-0866)
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…
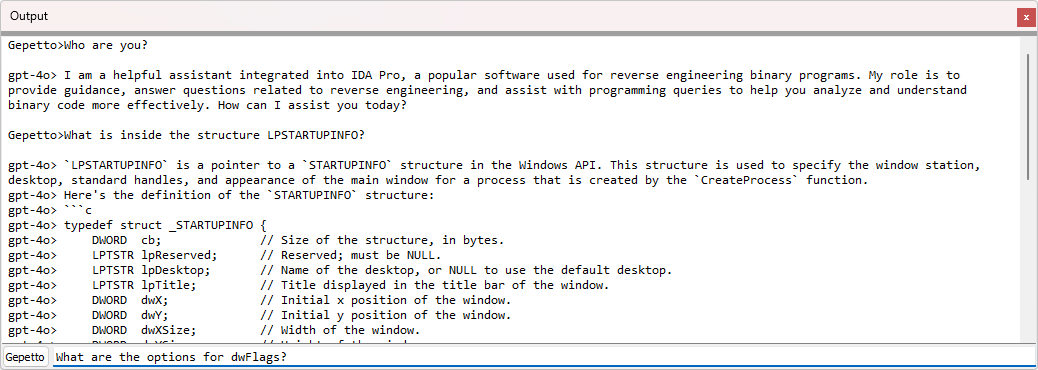 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
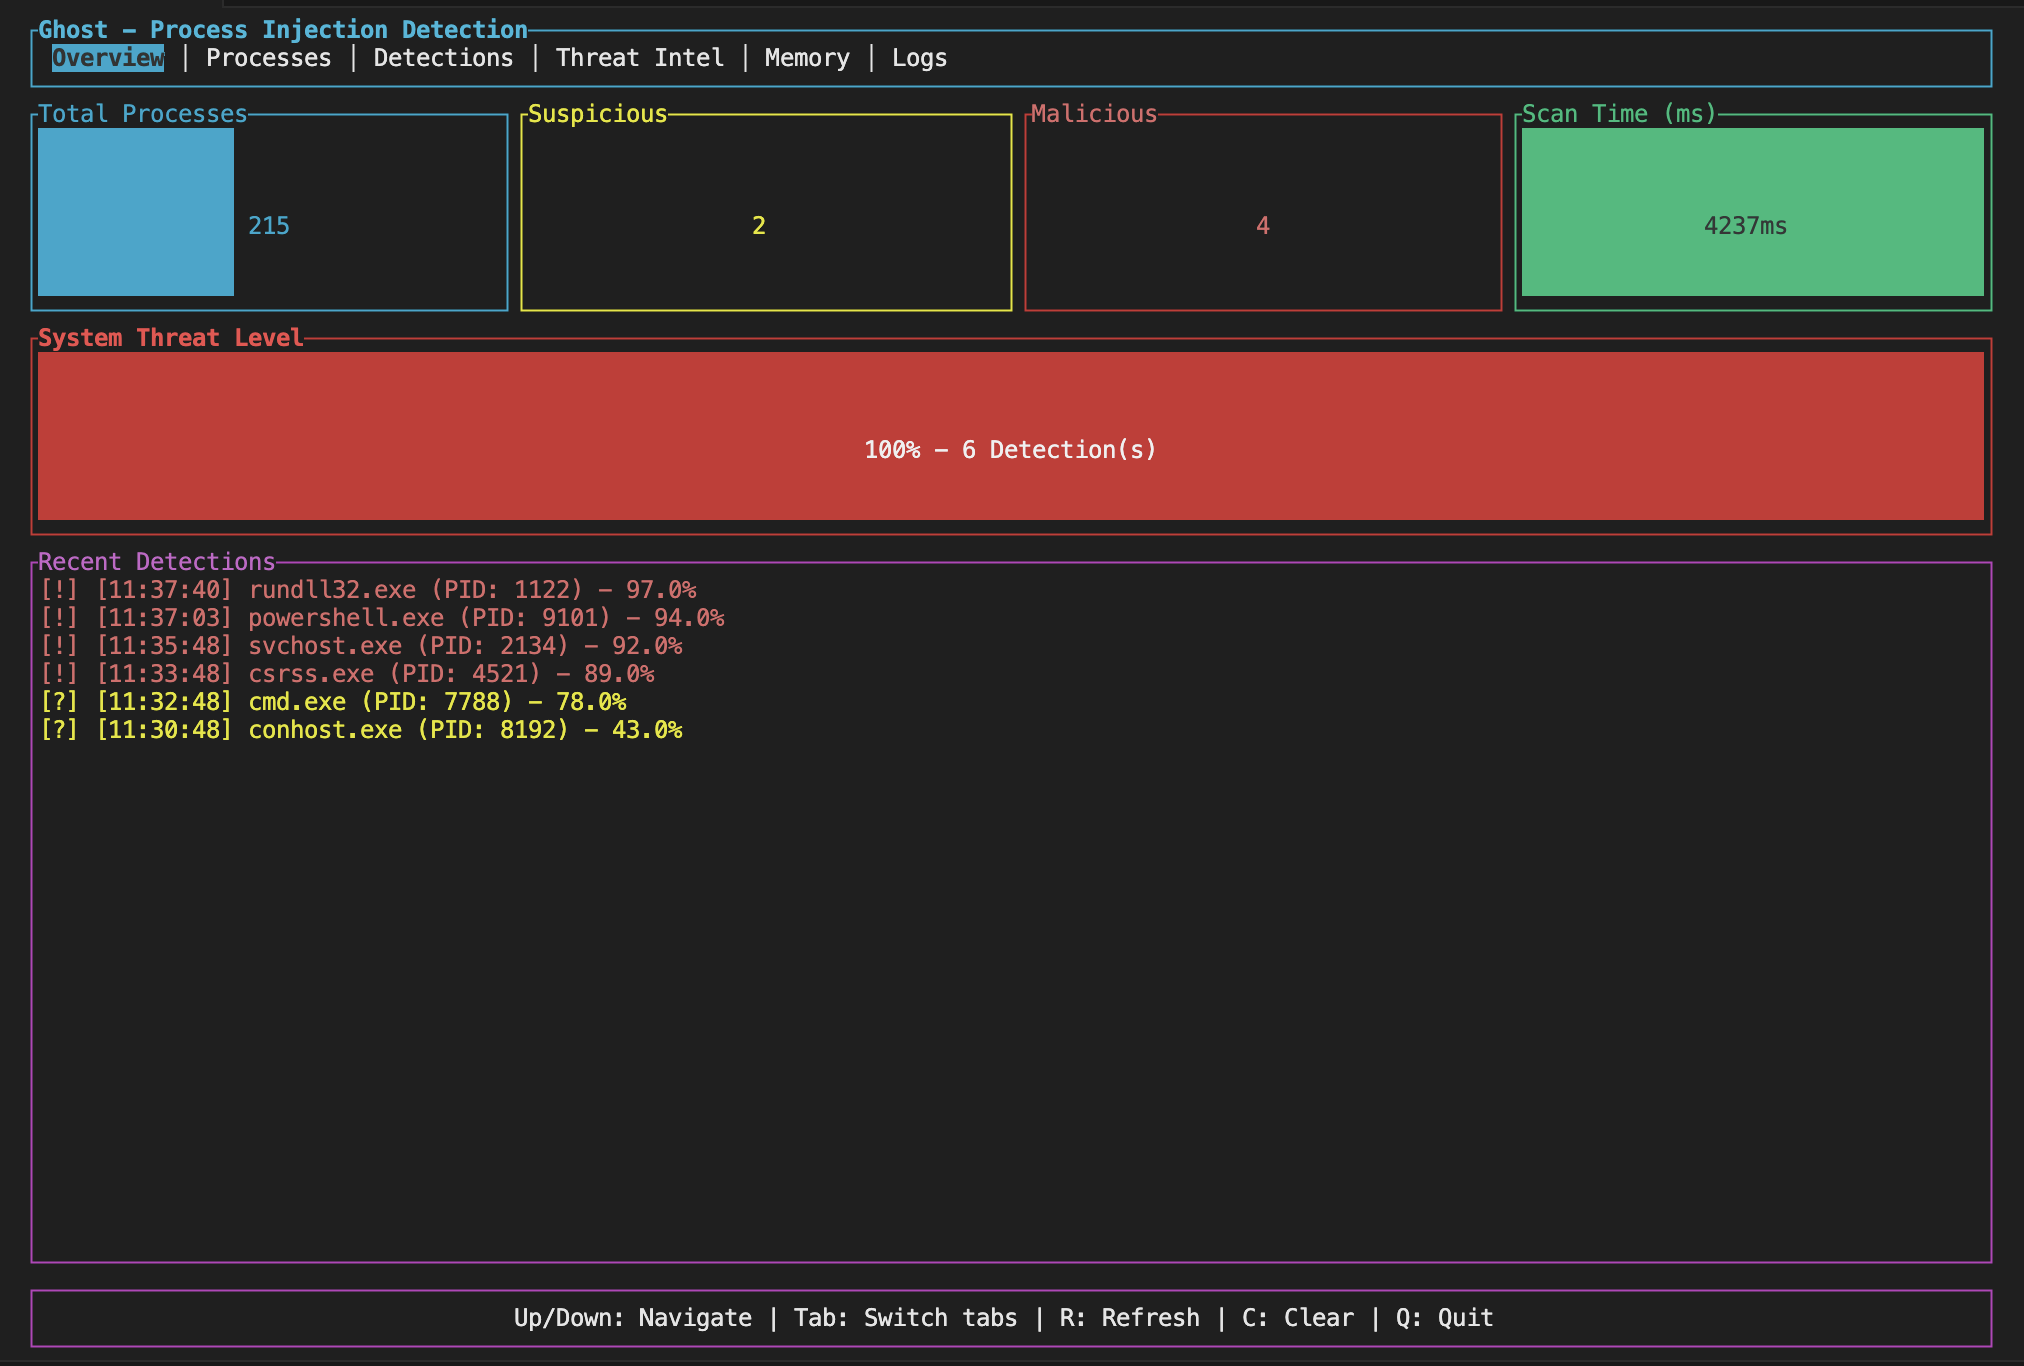 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 zhengxr930/maleval
Official code for the ISSTA 2026 paper: Is "Knowing It’s Malicious" Enough? Evaluating LLMs for Fine-Grained Malware Behavior Auditing
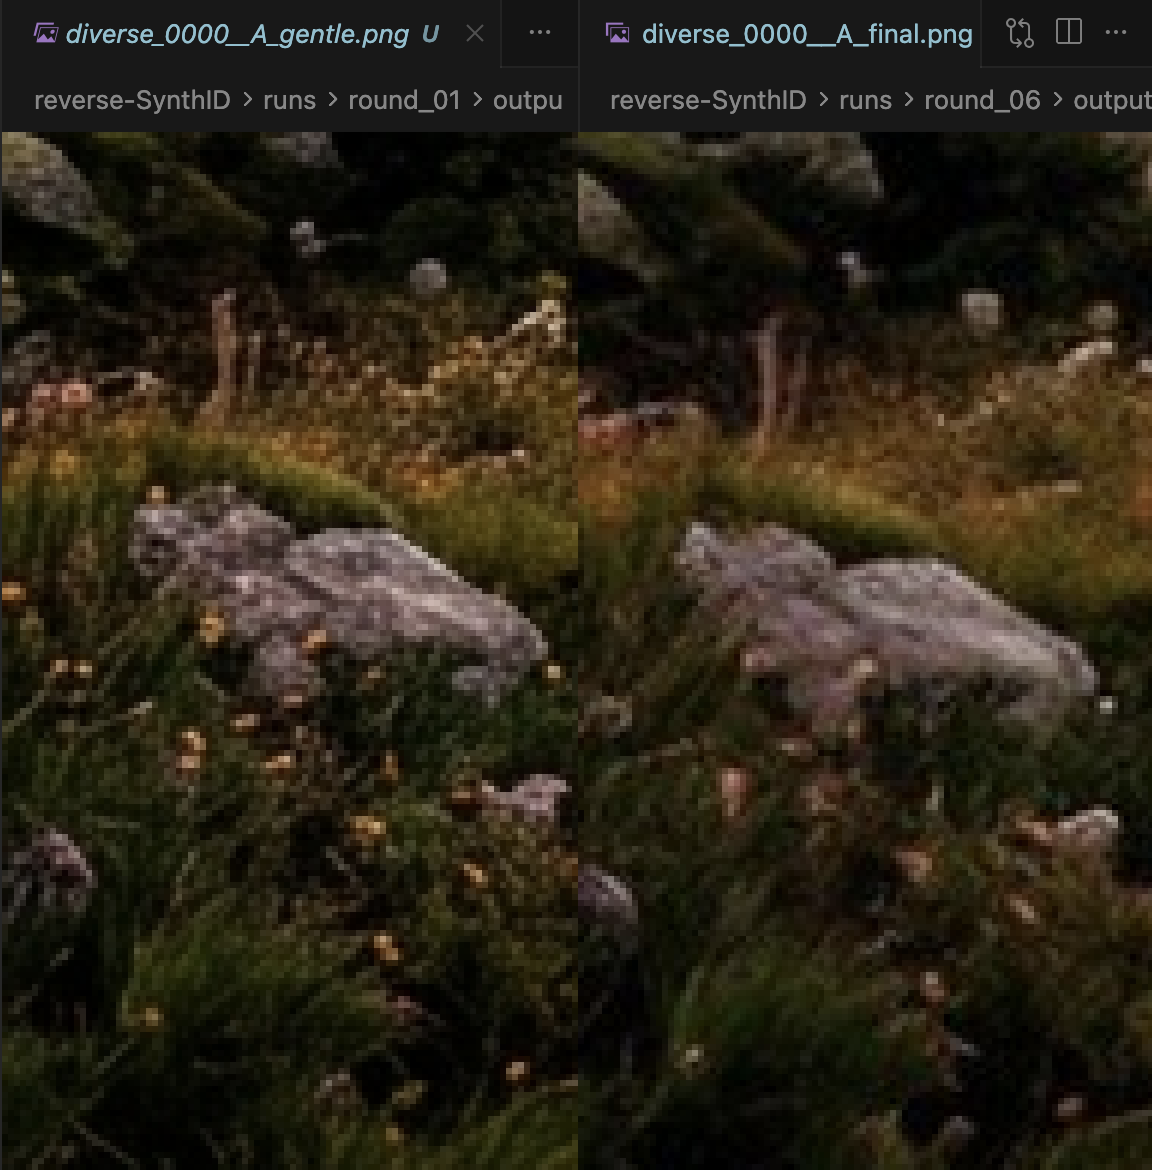 aloshdenny/reverse-synthid
reverse engineering Gemini's SynthID detection
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
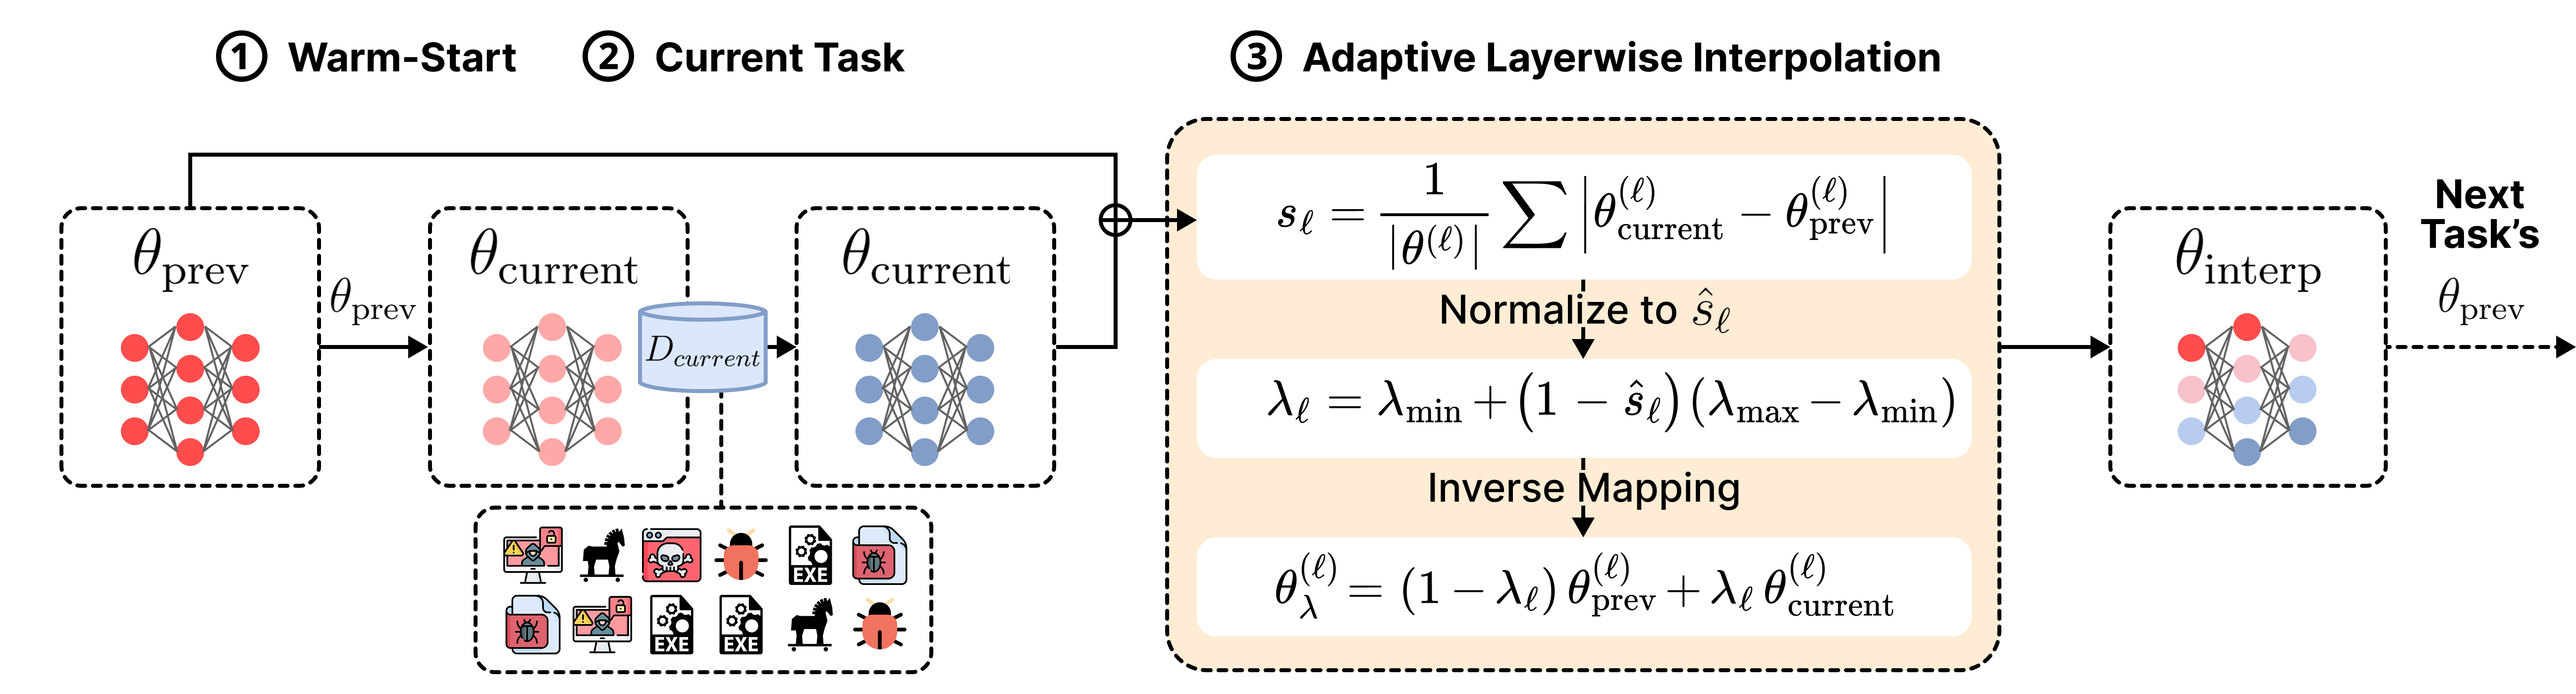 iqsec-lab/freemoca
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…
 qbnasasn/google-tensor-chips
Google Tensor Cracks
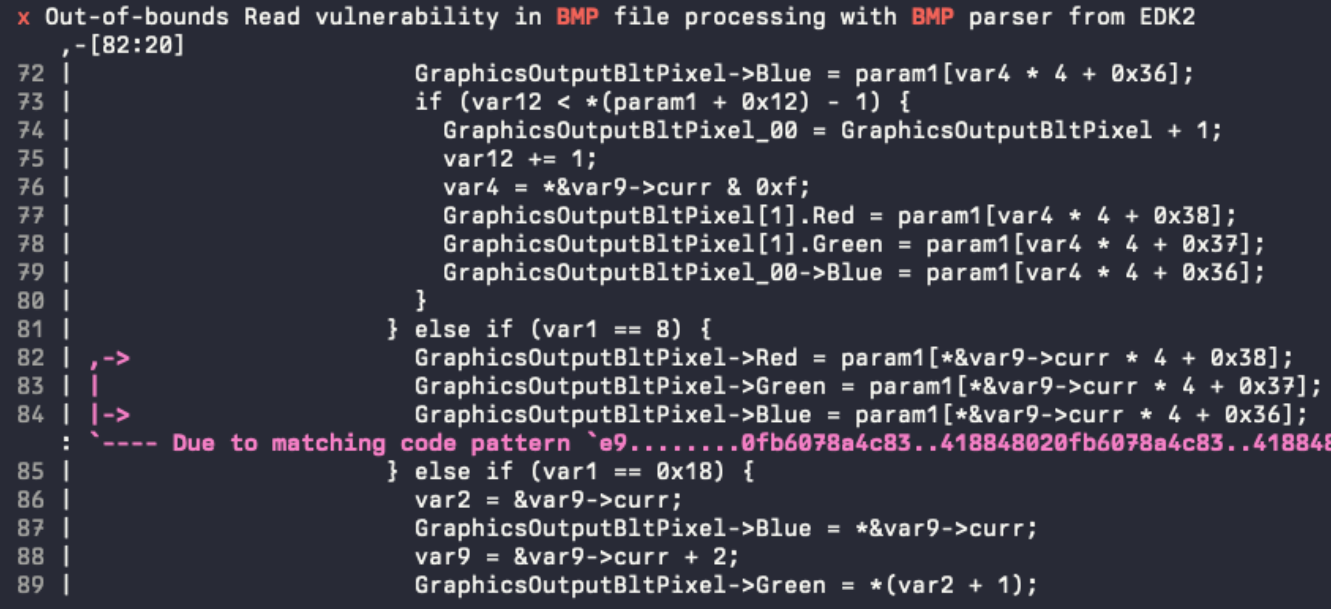 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…