Awesome-LLMs-for-Vulnerability-Detection

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.

A python library for user-friendly forecasting and anomaly detection on time series.

Streaming machine learning library for incremental learning on data streams, providing online estimators, drift and anomaly detection, pipelines,…

DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.

Re-evaluating prompt-injection detectors on LLM agent tool outputs (paper draft, scripts, scores)

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

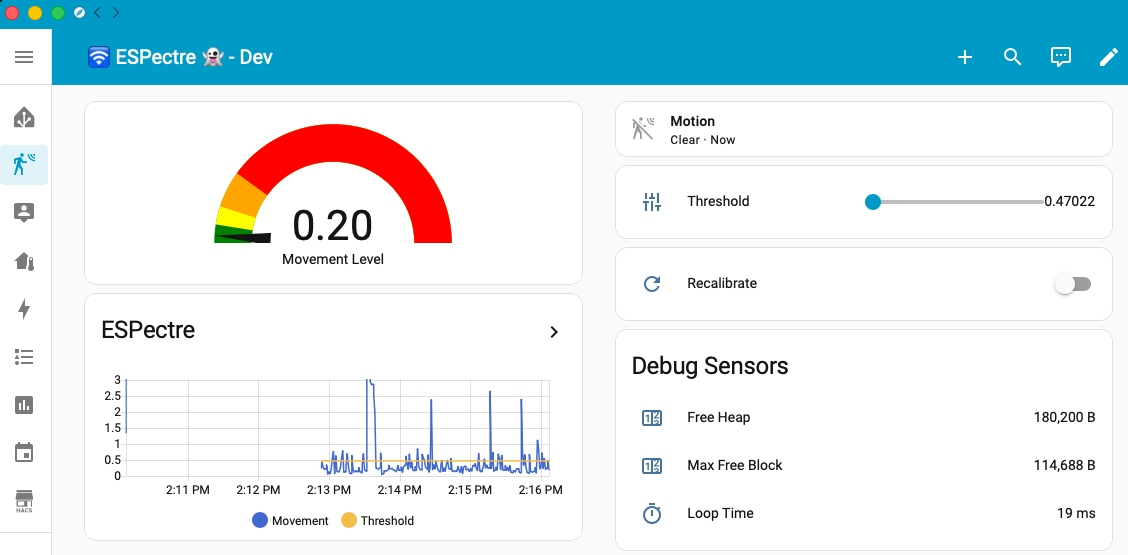
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.

A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…

Research code for measuring jailbreak attack success rates (ASR and stepwise ASR) against LLMs, with implementations of attacks such as GCG and…

AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…

C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…

LLM-driven agentic group shilling attack framework that manipulates black-box collaborative-filtering recommender rankings using adaptive multi-role…

Adversarial image attacks on vision-language web agents, from visual grounding to browser execution


Defense framework that mitigates malicious fine-tuning of LLMs using selective layer recovery and dynamic routing, with training, harmfulness…

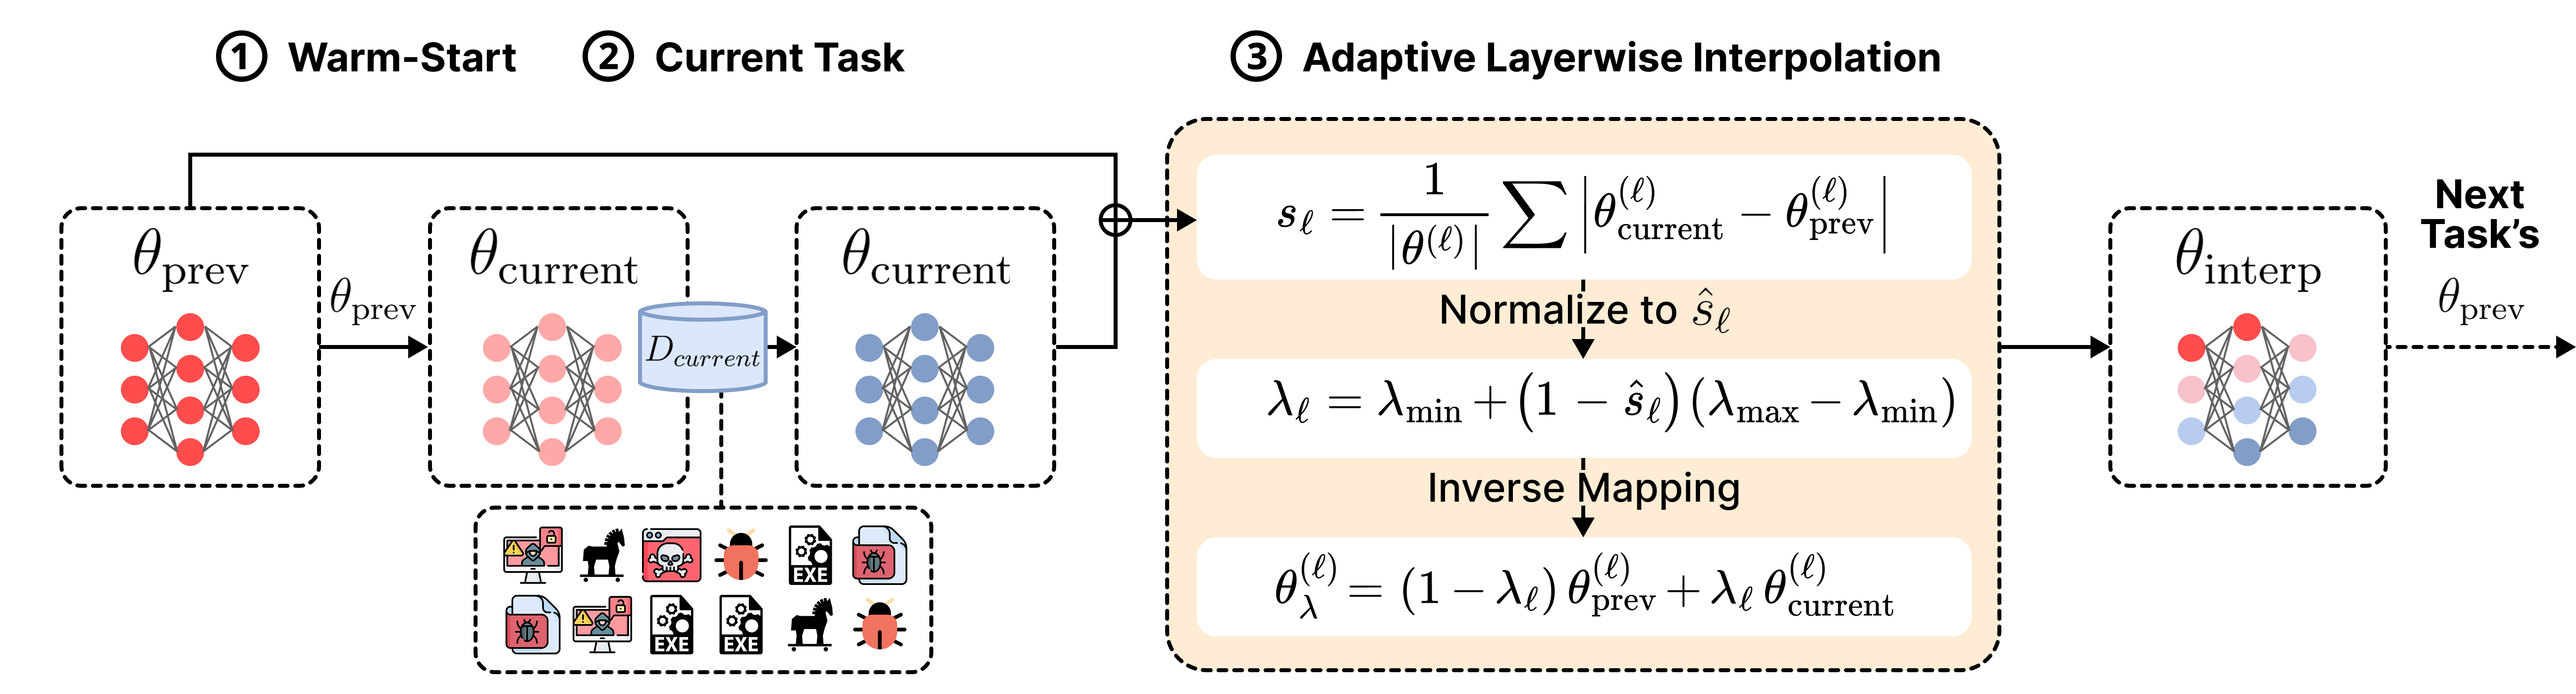
Memory-free continual learning framework for malware classification using mode connectivity-based interpolation. Supports class-incremental and…

Research code for a gray-box trojan attack that flips a single KV-cache bit in fine-tuned LLM classifiers and measures per-class attack success rate.