
qai2026-fgsm-transfer
 xeeshanajmal/qai2026-fgsm-transfer
Code and results for the QAI 2026 paper on FGSM attack transferability from simulation to IBM quantum hardware.
adversarial-attackai-securityintrusion-detection+3
1
xeeshanajmal/qai2026-fgsm-transferCode and results for the QAI 2026 paper on FGSM attack transferability from simulation to IBM quantum hardware.
 chxhana/aligned-rag-eval
Lightweight evaluation harness for RAG poisoning defenses that builds four-condition clean/poisoned records and reports prevented targets, net…
 ali-bana/olmo-twin
Reproduction code for a controlled study of membership-inference attacks on OLMo 2, covering document insertion, mid-training, post-training, scoring…
 mahmoud-abbasi-svg/agent-trace-detector-eval
Code, derived data and results for: Evaluating Baseline Detectors of Hijacked LLM Agents Under Rare Attacks and Distribution Shift
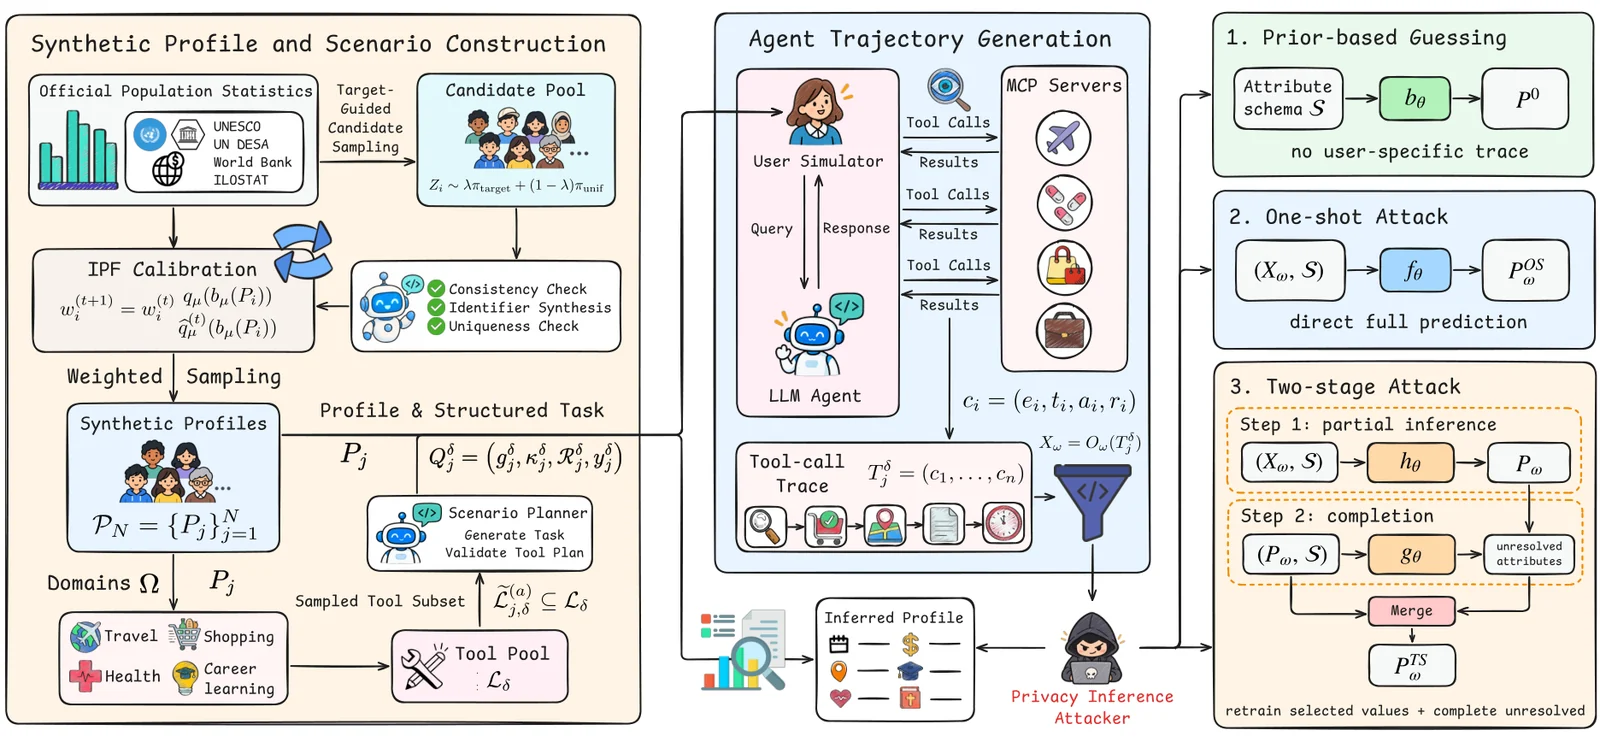 ai45lab/privacytrace
How Much Can Tool Calls Reveal About You? Privacy Leakage from Tool-Call Traces
 jawh3/striatum-ctf
Research artifacts for an MCP-based LLM agent that autonomously solves CTF challenges, including ablation data, analysis scripts, and a six-server…
 shubsds/authorship-not-sabotage
Code and paper source for a NeurIPS EvoRobust study showing simple bag-of-words and metadata features beat most AI control monitors at detecting…
 ua-spectral/botlens
Research artifact and MCP server that audits security and privacy concerns in third-party Discord bots via large-scale review analysis, LLM labeling,…
 jefffffffu/priv-qdnn
Research codebase for privacy evaluation of quantized neural networks: trains target/shadow models under PTQ/QAT and runs membership-inference…
 itm-kitware/alignment-cage-challenge-2
CybORG CAGE 2 environment updated for the paper "Alignment of Autonomous Cyber Defense Agents via Adaptive Policy Shaping"
 maureille/agentic-pcap
Benchmark code and interactive results for autonomous network-attack detection by tool-using LLM agents investigating raw PCAPs.
 yashubitra/mobile-intrusion-detection-system
Unsupervised deep autoencoder that flags anomalous mobile traffic: 25,000+ HTTP/HTTPS flows intercepted from a live iOS device with mitmproxy,…
 ukanwat/guardrebind
Research code, benchmark and defense for target rebinding attacks that trick LLM safety guards into grading forged decoy content, plus segment-max…
 lzh0082-cloud/code-detection
Replication package studying how LLM vulnerability auditors defer to static-analysis evidence, with a tree-sitter C/C++ front end, controlled…
 seclog-open/seclog
Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…
 suels-group/beyond_asr
Research code for measuring jailbreak attack success rates (ASR and stepwise ASR) against LLMs, with implementations of attacks such as GCG and…
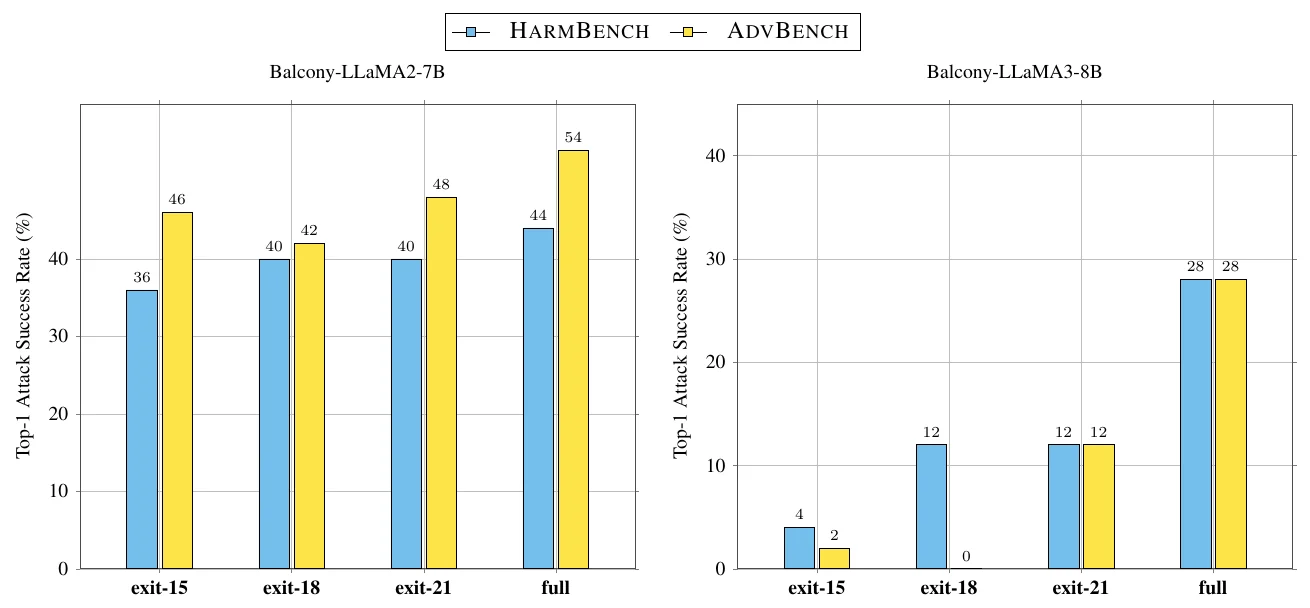 lassnajmuldeen/balcony-jailbreaking
Jailbreak vulnerability across early-exit depths LLMs. Published at NeurIPS 2026 in the FLMSec workshop
 crypto-unict/ghostfacempc
Reference implementation of privacy-preserving face recognition using replicated secret sharing in MP-SPDZ, with quantized GhostFaceNet inference,…